OT / SCADAImplementing IEC 62443-3-2: A Guide to Zones, Conduits and Purdue Boundaries
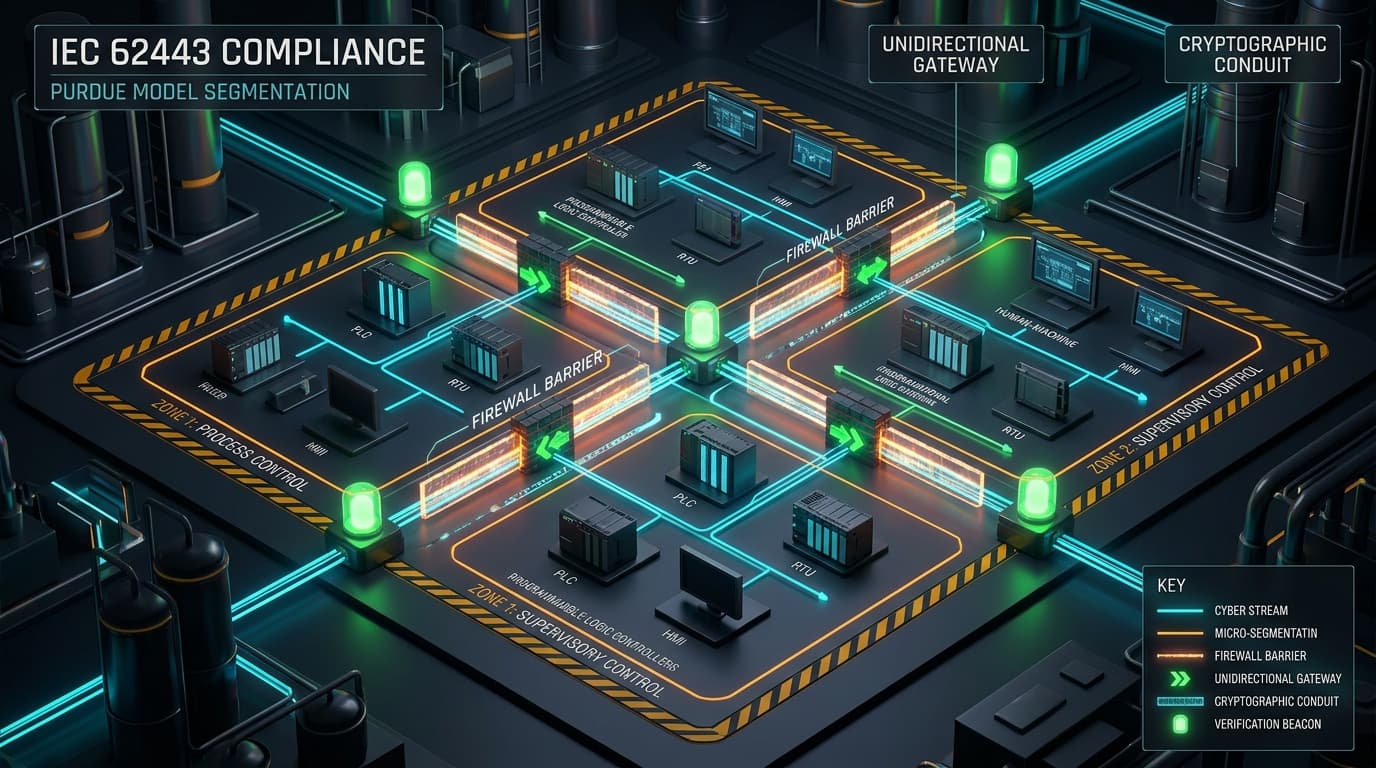
Engineering blueprint for implementing IEC 62443-3-2 zones, conduits, and Purdue Model boundaries across industrial automation and SCADA systems.
1,660 articles
OT / SCADAEngineering blueprint for implementing IEC 62443-3-2 zones, conduits, and Purdue Model boundaries across industrial automation and SCADA systems.
MicrosoftForensic examination of SEC Item 1.05 material cyber filings reveals how compromised IAM credentials and public S3/Blob storage enable rapid data exfiltration.
VMware ESXiCISA mandates urgent federal remediation as attackers weaponize CVE-2026-59310, an unauthenticated path traversal flaw granting root code execution on VMware vCenter appliances.
AppleCISA confirms active exploitation of CVE-2026-65400, an unauthenticated network authentication bypass in Apple macOS Screen Sharing enabling remote desktop seizure.
Active ExploitCISA issues an emergency directive on CVE-2025-62593, warning that unauthenticated code injection in Ray AI distributed computing clusters allows adversaries to seize GPU clusters and training models.
MicrosoftCISA confirms active in-the-wild exploitation of CVE-2026-33824, an unauthenticated double-free memory corruption flaw in Windows IKE enabling remote root code execution over UDP 500.
AWS CloudCISA issues urgent warning on CVE-2026-64849, a critical SSRF defect in open-source MLflow model registries allowing attackers to steal cloud IAM metadata and poison AI pipelines.
MicrosoftFederal agencies and enterprise operators face urgent deadlines as CISA confirms active exploitation of CVE-2021-23758, an unauthenticated deserialization RCE in Ajax.NET Professional.
Active ExploitCISA adds CVE-2026-21962 to its KEV catalog, warning of active remote exploitation bypassing Oracle HTTP Server reverse proxy rules to seize WebLogic clusters.
Active ExploitFederal agencies face strict remediation deadlines as CISA confirms active exploitation of CVE-2026-73570, allowing unauthenticated adversaries to execute root shell commands on Zimbra mail servers.
Threat IntelCISA warns of active exploitation targeting enterprise video conferencing systems via CVE-2026-72530, an unauthenticated remote code injection flaw on TrueConf port 4307.
CiscoCISA mandates urgent federal remediation after confirming active exploitation of CVE-2026-76461, an unauthenticated SQL injection flaw granting root shell access on Cisco SEG appliances.
KubernetesCISA adds CVE-2026-66384 to its KEV catalog, warning that path traversal in JFrog Artifactory allows remote adversaries to overwrite Docker layers and poison enterprise build pipelines.
Threat IntelCISA issues binding remediation directive on CVE-2026-60004, a critical code injection defect in Gitea's git diffpatch parser enabling remote command execution on self-hosted repositories.
Citrix NetScalerCISA issued a binding directive on CVE-2026-8452, a high-severity memory buffer vulnerability in Citrix NetScaler ADC and Gateway appliances triggering perimeter denial of service.
Threat IntelFederal agencies face urgent remediation deadlines as CISA confirms active exploitation of CVE-2023-49105, allowing attackers to access and delete cloud storage files without credentials.
LinuxCISA added CVE-2026-53362 to its KEV catalog, warning of active privilege escalation exploits targeting the Linux Kernel IPv6 networking subsystem across major enterprise distros.
OT / SCADACISA alerted industrial manufacturing operators to severe vulnerabilities in Rockwell Automation Logix controllers and 1756 communication modules allowing PLC tampering.
OT / SCADACISA issued an energy sector ICS advisory warning of memory corruption and authentication defects in AVEVA Pipeline Integrity Monitor supervising oil and gas transport.
OT / SCADACISA published an urgent medical ICS advisory detailing critical RCE vulnerabilities in NextGen Mirth Connect integration engines routing hospital clinical records.
Gov / DefenseCISA issued its landmark final rule under CIRCIA, legally mandating critical infrastructure operators report major cyber incidents within 72 hours and ransom payments within 24 hours.
Gov / DefenseA joint cybersecurity advisory from CISA, NSA, and FBI alerts defense contractors and cloud vendors to sophisticated state-sponsored AI model extraction campaigns.
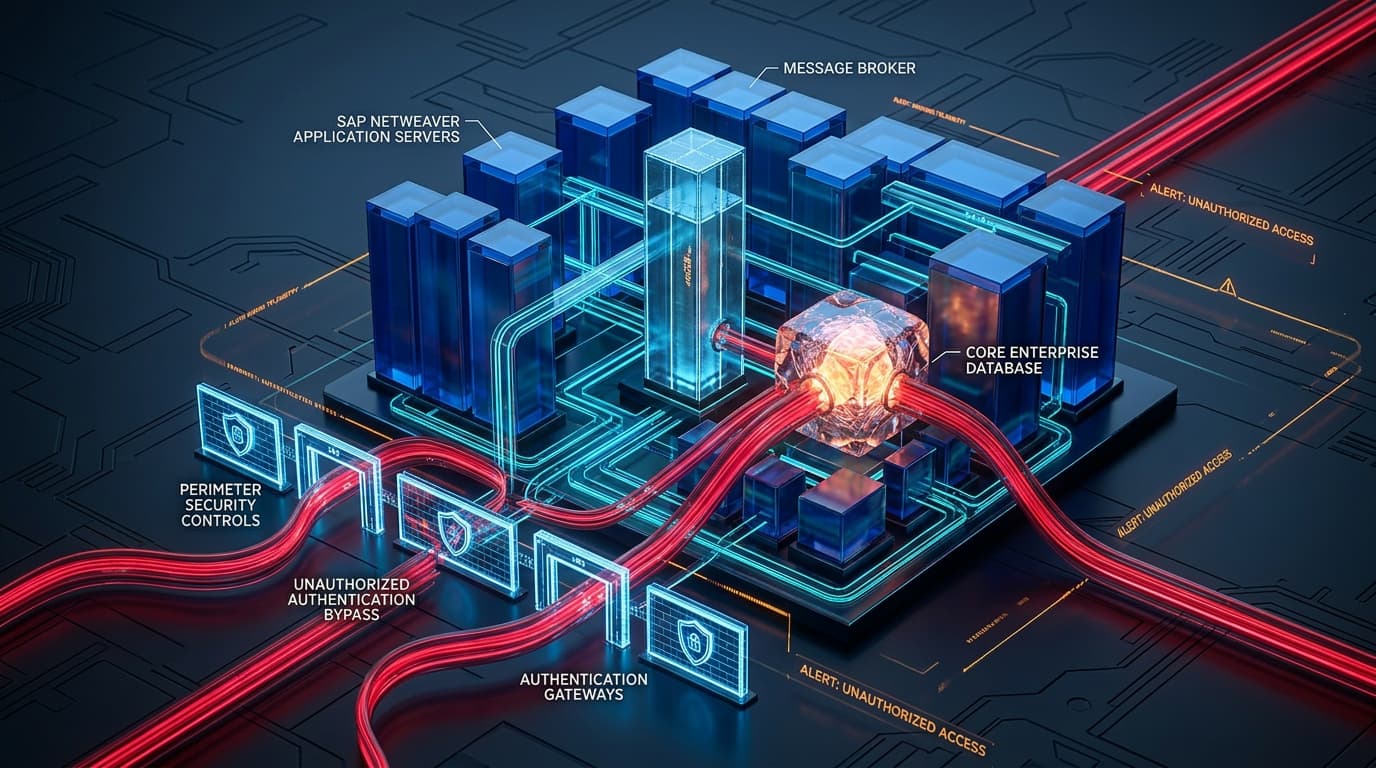
SAP EnterpriseSAP released security updates for CVE-2026-58240, a CVSS 9.6 authentication bypass in NetWeaver AS Java/ABAP Message Server that permits enterprise takeover.
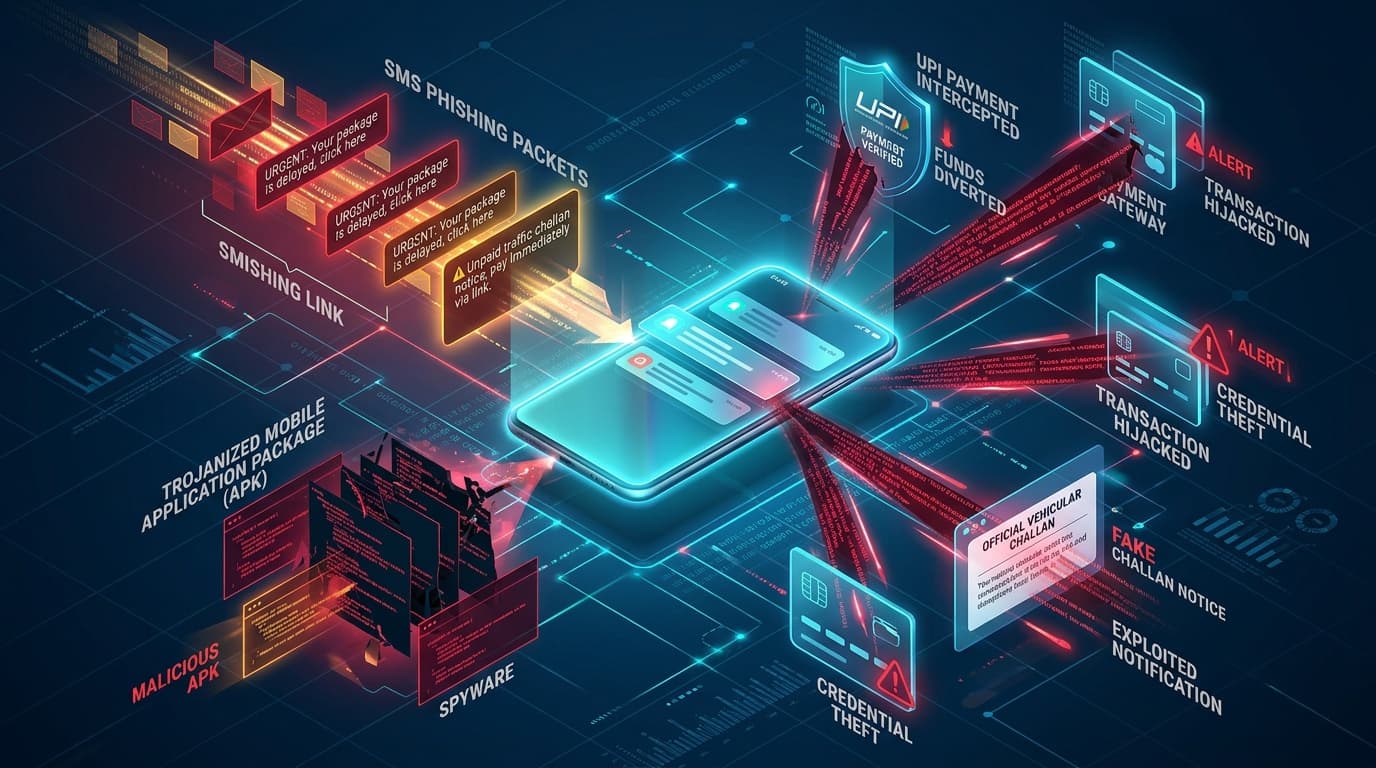
GoogleCERT-In issued advisory CIAD-2026-0038 warning against an aggressive smishing blitz delivering trojanized APKs disguised as official Parivahan traffic e-challan notices.