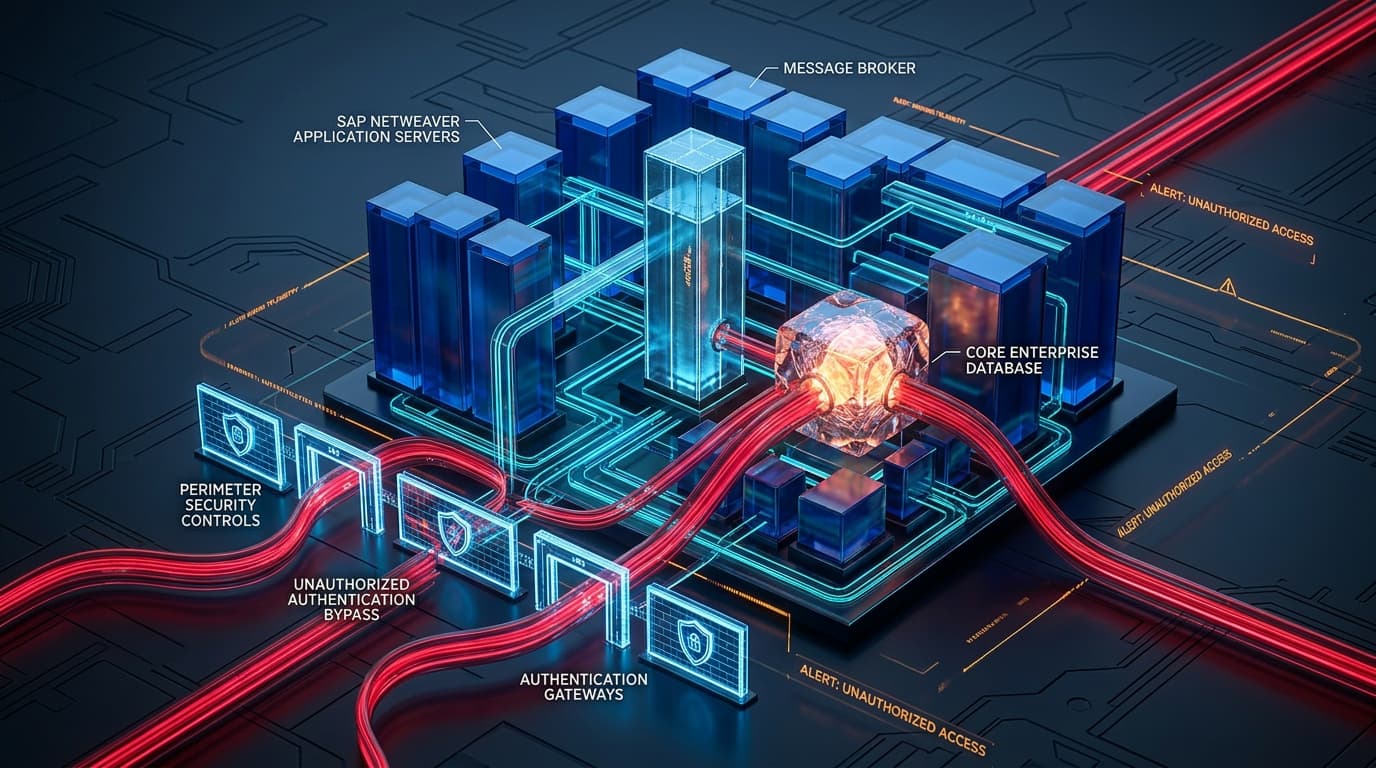
Enterprise resource planning (ERP) market leader SAP has published its monthly Security Patch Day bulletin, headlined by a critical vulnerability affecting the SAP NetWeaver Application Server (AS) architecture. The flaw allows unauthenticated remote attackers to bypass internal authentication controls and register rogue application servers within an organization’s core business systems.
Tracked as CVE-2026-58240, the vulnerability carries a Common Vulnerability Scoring System base score of 9.6 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:N). Classified under CWE-287: Improper Authentication, the defect is remediated through SAP Security Note 3492812.
Vulnerability Mechanics: The Rogue Application Server Register Vector
In a distributed SAP NetWeaver landscape, the Message Server (typically operating on TCP port 3900–3999 for internal communication and 3600–3699 for client connections) serves as the central coordination hub. It maintains the registry of active application servers, facilitates inter-instance load balancing, and routes remote function calls (RFCs) across the landscape.
Under CVE-2026-58240, an attacker with network reachability to the Message Server port can exploit an authentication state validation flaw during instance registration:
- Unauthenticated Registration: The attacker transmits a crafted registration packet to the Message Server internal communication port without presenting valid mutual authentication certificates or administrative tokens.
- Broker State Poisoning: The Message Server accepts the registration, adding the attacker’s rogue IP address and host identifier to the active application server dispatch table.
- Traffic Interception & Execution: Once registered, the Message Server routes user sessions, RFC calls, and business workflows to the rogue server. The attacker can harvest user session cookies, modify financial ledger postings in flight, or dispatch arbitrary administrative commands across the NetWeaver landscape.
SAP is the operational nervous system for multinational enterprises. An attacker controlling Message Server registration can siphon ERP business data, payroll records, and industrial supply chain communications without ever tripping endpoint alarms.
Affected NetWeaver Components & Security Notes
| Software Component | Affected Kernel Versions | Remediation Security Note | Severity Rating |
|---|---|---|---|
| SAP NetWeaver AS ABAP & Java (Kernel) | 7.22, 7.53, 7.54, 7.89, 7.93 | Security Note 3492812 | Critical (CVSS 9.6) |
| SAP S/4HANA (On-Premise & Cloud Private) | Releases 1809 through 2023 | Security Note 3492812 (Kernel Update) | Critical (CVSS 9.6) |
| SAP Web Dispatcher | Components linking to unpatched Message Server | Security Note 3491904 | High (CVSS 7.5) |
Remediation Checklist & Network Isolation Rules
SAP administrators must execute the following hardening protocol across all production, testing, and staging instances:
# Verify Message Server Access Control List configuration (ms/acl_info)
# File: /usr/sap//SYS/global/ms_acl_info

# Enforce strict IP whitelist for allowed application servers:
HOST=10.10.10.11, 10.10.10.12, 10.10.10.13

# Verify configuration parameter in SAP profile:
ms/acl_info = $(DIR_GLOBAL)/ms_acl_info
Recommended Administrative Safeguards
- Apply Kernel Patches: Immediately download and deploy the latest SAP Kernel patch associated with Security Note 3492812 via the SAP Support Portal.
- Enforce Message Server Access Control: Configure the
ms/acl_infoparameter to explicitly restrict which IP addresses are permitted to log on as application servers. Reject all wildcards (*). - Network Perimeter Segmentation: Ensure that Message Server ports (TCP 3900–3999 and 3600–3699) are strictly isolated within a dedicated SAP server VLAN and never exposed to general user subnets or internet-facing routing boundaries.
- Enable Secure Network Communications (SNC): Mandate SNC encryption and certificate validation for all internal SAP instance-to-instance communication channels.