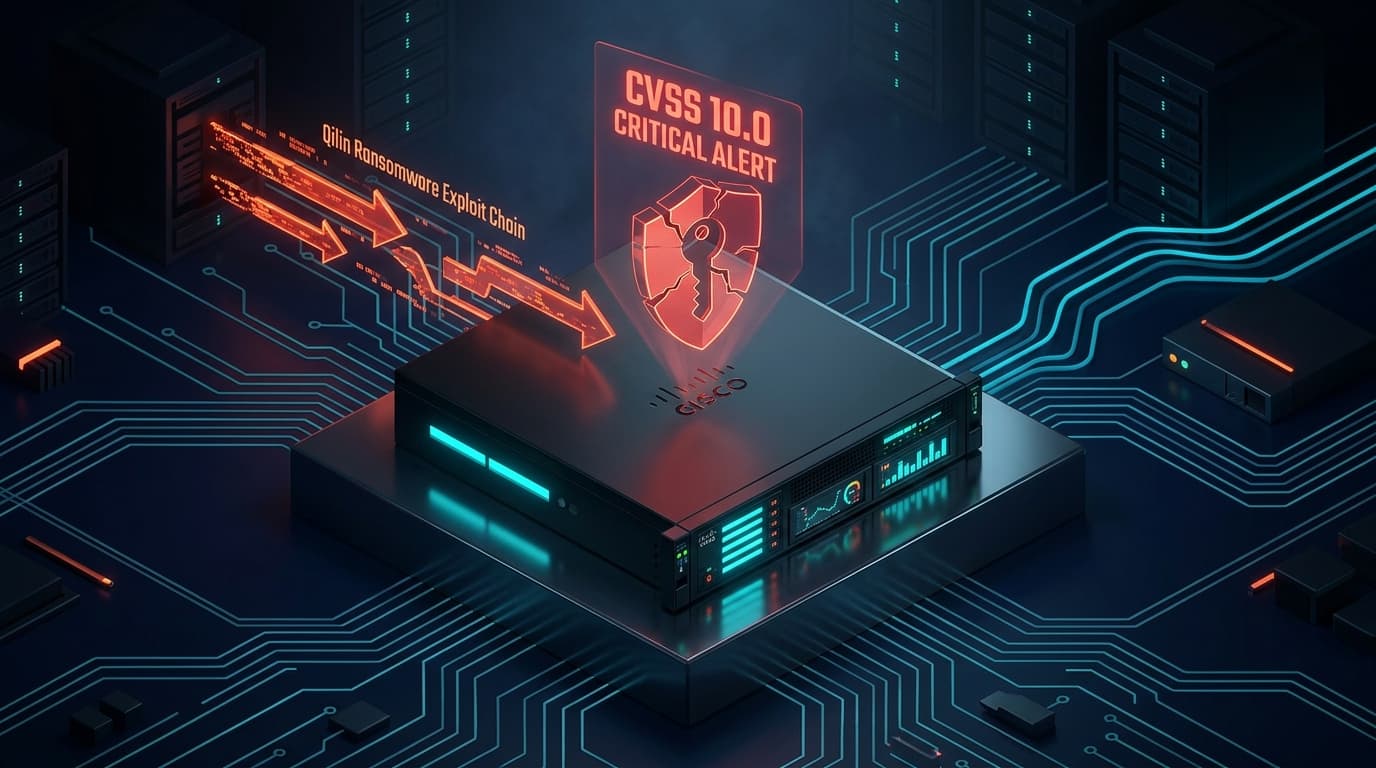
Cisco has confirmed that multiple threat actor clusters, including affiliates of the Qilin ransomware operation and state-aligned espionage groups, are actively exploiting a critical vulnerability in its Secure Firewall Management Center (FMC) software.
The primary flaw, tracked as CVE-2026-20079, carries a maximum Common Vulnerability Scoring System (CVSS) rating of 10.0. It resides in the HTTP/HTTPS web-based management interface of FMC and allows an unauthenticated, remote adversary to bypass authentication mechanisms and execute arbitrary scripts with root privileges on the underlying operating system.
The Attack Mechanics & Exploitation Chain
According to telemetry published by Cisco Talos, attackers are pairing CVE-2026-20079 with CVE-2026-20316 (CVSS 5.3), an authorization defect that enables authenticated low-privilege accounts to access sensitive system databases. Together, the bugs create a turnkey intrusion pipeline:
- Initial Unauthenticated Ingress: The remote attacker sends specially crafted HTTP POST requests to vulnerable FMC endpoints, circumventing session verification routines.
- Root Command Injection: Leveraging the flaw's script execution vector, the adversary spawns an interactive bash shell running as
root. - Credential Harvesting: Attackers extract stored administrative credentials, VPN authentication pre-shared keys, and Active Directory service account secrets managed by the central firewall cluster.
- Lateral Movement & Ransomware Deployment: In multiple observed intrusions, operators associated with Qilin ransomware used compromised FMC appliances as an internal pivot point to deploy file-encrypting payloads across enterprise VMware ESXi hosts and domain controllers.
Firewall management planes manage the entire network perimeter. When an attacker achieves unauthenticated root on an FMC appliance, perimeter filtering is effectively neutralized.
Defensive Guidance & Remediation Checklist
Cisco has issued hotfixes across affected FMC software releases and strongly urges immediate installation:
- Apply Emergency Hotfixes: Install vendor-supplied hotfixes for FMC releases 7.0, 7.2, 7.4, and 7.6 immediately.
- Isolate the FMC Web Interface: Ensure FMC management ports (HTTPS 443) are restricted to dedicated, isolated out-of-band management subnets. Under no circumstances should FMC interfaces be directly exposed to the public internet.
- Audit Administrative User Accounts: Review the FMC user directory for unauthorized local accounts created after recent maintenance windows.
- Inspect Firewall Telemetry: Check syslog streams for anomalous child processes spawned by web server daemons, particularly invocations of
/bin/shor unexpected python binaries.