Topic
CISA KEV: news, advisories and analysis
27 articles
CISA's Known Exploited Vulnerabilities (KEV) catalog lists flaws with reliable evidence of exploitation in the wild. Under Binding Operational Directive 22-01, US federal civilian agencies must remediate each entry by its due date, and most enterprise patch programmes now treat a KEV listing as the signal to move a fix to the front of the queue.
This page tracks every vulnerability we have covered that appears in the catalog: the affected product and versions, the fixed release, the remediation deadline and what is known about the campaigns using it. For a table view with severity and fix status side by side, see the CISA KEV advisory hub.
CISA KEV advisory hub: severity, KEV status and fixes in one table
Latest coverage
ThreatsCloud & SaaSBreakingCST Editorial Desk
ThreatsCloud & SaaSBreakingBroadcom VMware ESX Vulnerability Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalAdobe Commerce and Magento Unrestricted File Upload Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalCollabora Online – Built-in CODE Server OS Command Injection Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSSiemens Software Center Vulnerability Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSPlex Media Server Server-Side Request Forgery Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalPlex Media Server Input Validation Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSHighEG Secure Solutions SiteGuard Server Edition OS Command Injection Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSHighPalo Alto Networks PAN-OS Management Interface RCE Exploited in Attacks
CST Editorial Desk
ThreatsCloud & SaaSAhsayCBS Authentication Bypass Exploited Against Backup Servers
CST Editorial Desk
ThreatsCloud & SaaSCriticalAtlassian Data Center Flaw Spanning Jira, Confluence and Bitbucket Exploited
CST Editorial Desk
ThreatsCloud & SaaSCriticalCisco Secure Email Gateway AMP Flaw Exploited for Unauthenticated File Writes
CST Editorial Desk
ThreatsCloud & SaaSCriticalAhsayCBS Backup Server Command Injection Exploited in Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalProFTPD mod_copy Flaw Weaponized to Copy Server Files and Execute Code
CST Editorial Desk
ThreatsCloud & SaaSCriticalISC BIND 9 TKEY Flaw Exploited to Crash Authoritative DNS Servers
CST Editorial Desk
ThreatsCloud & SaaSCriticalApache Struts 2 Dynamic Method Invocation Flaw Weaponized for Remote Code Execution
CST Editorial Desk
ThreatsCloud & SaaSCriticalZammad Helpdesk Exploit Chain Pairs Session Fixation With Root Escalation for Takeover
Daniel Okafor
ThreatsCloud & SaaSCriticalCisco Catalyst SD-WAN Manager Hex Encoding Flaw Exploited to Hijack Enterprise Routing (CVE-2026-76504)
CST Editorial Desk
ThreatsCloud & SaaSMikroTik RouterOS SSH Rekey Flaw Weaponized in MikroTrick Chain to Hijack Routers
Daniel Okafor
ThreatsCloud & SaaSCriticalAdobe Commerce and Magento Authorization Flaw Exploited to Hijack Checkout Workflows
Daniel Okafor
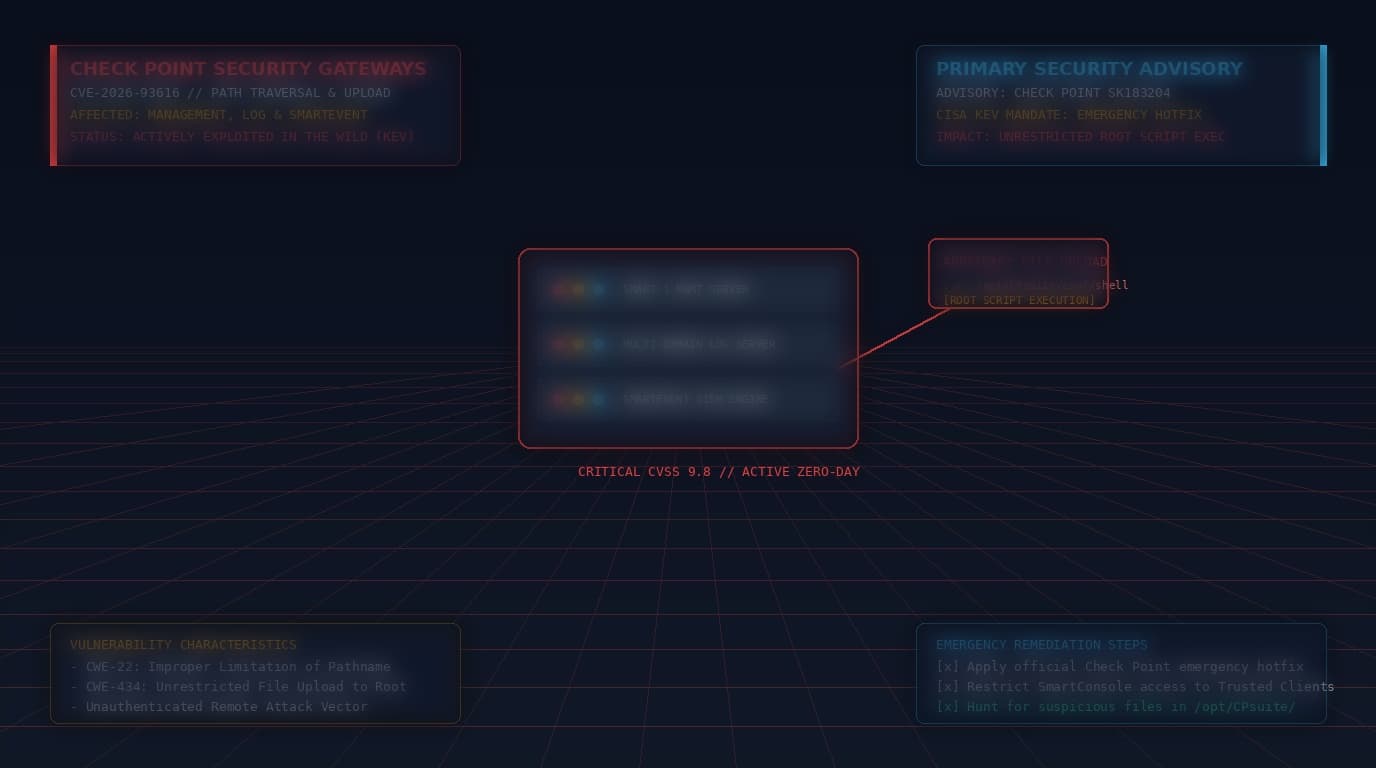
ThreatsCloud & SaaSCriticalCheck Point Security Management Server Path Traversal Exploited to Gain Root Access
CST Editorial Desk
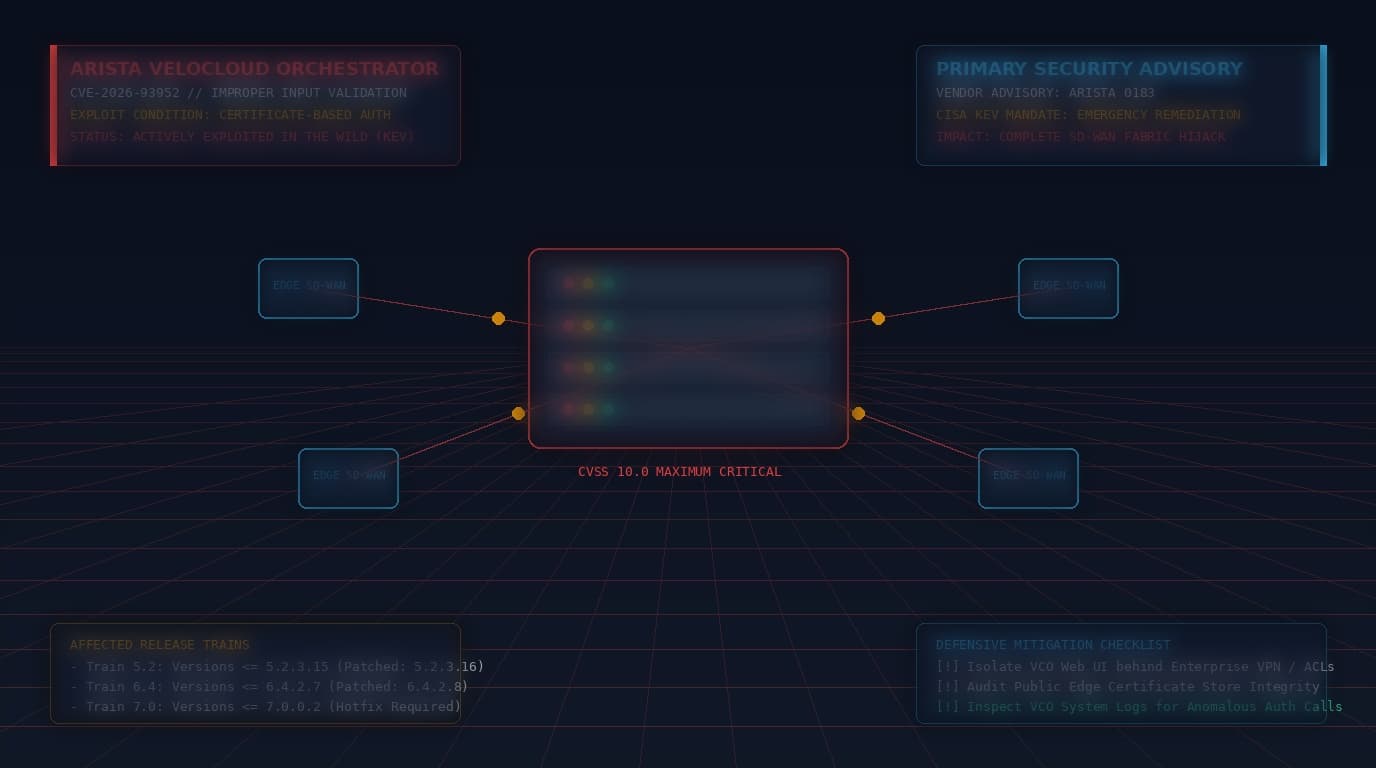
ThreatsCloud & SaaSCriticalArista VeloCloud Orchestrator Zero-Day Exploited to Hijack SD-WAN Edge Gateways
CST Editorial Desk