Topic
Zero-Day: news, advisories and analysis
27 articles
CyberSecureToday covers Zero-Day across 27 articles published between 9 Sep 2026 and 22 Oct 2026. The coverage includes 22 vulnerability advisories, 2 incident or breach reports and 3 analysis or guidance pieces. 21 advisories are rated critical or high severity, and 12 involve flaws listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on Zero-Day most often intersect with Active Exploitation, CVSS 9.8 and Remote Code Execution, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Critical 'PHP2Shell' Core Runtime Flaws Trigger Unauthenticated RCE Across Millions of Web Servers”, was published 22 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
CISA KEV advisory hub: severity, KEV status and fixes in one table
Latest coverage
ThreatsCloud & SaaSCST Editorial Desk
Cyber AttackCloud & SaaSOperation Cyber Guardian: CSA and IMDA Expose UNC3886 Stealth Espionage Campaign Targeting Singapore Telcos
Daniel Okafor
ResearchCloud & SaaSGoogle GTIG: AI-Found Bugs Skew Toward Code Execution as Exploited Vulnerabilities Outpace All of 2025
Priya Raman
ThreatsCloud & SaaSCriticalCitrix NetScaler ADC Memory Buffer Flaws Exploited to Breach Perimeter Gateways
Priya Raman
ThreatsCloud & SaaSCriticalFortinet FortiMail Path Traversal Flaw Exploited for Unauthenticated Remote Code Execution
Priya Raman
ThreatsCloud & SaaSCriticalApple Patches CoreGraphics In-The-Wild Zero-Day Memory Corruption Across iOS and macOS (CVE-2026-86950)
CST Editorial Desk
ThreatsCloud & SaaSCriticalWSO2 API Manager Path Traversal Flaw Weaponized to Extract Gateway Credentials
Daniel Okafor
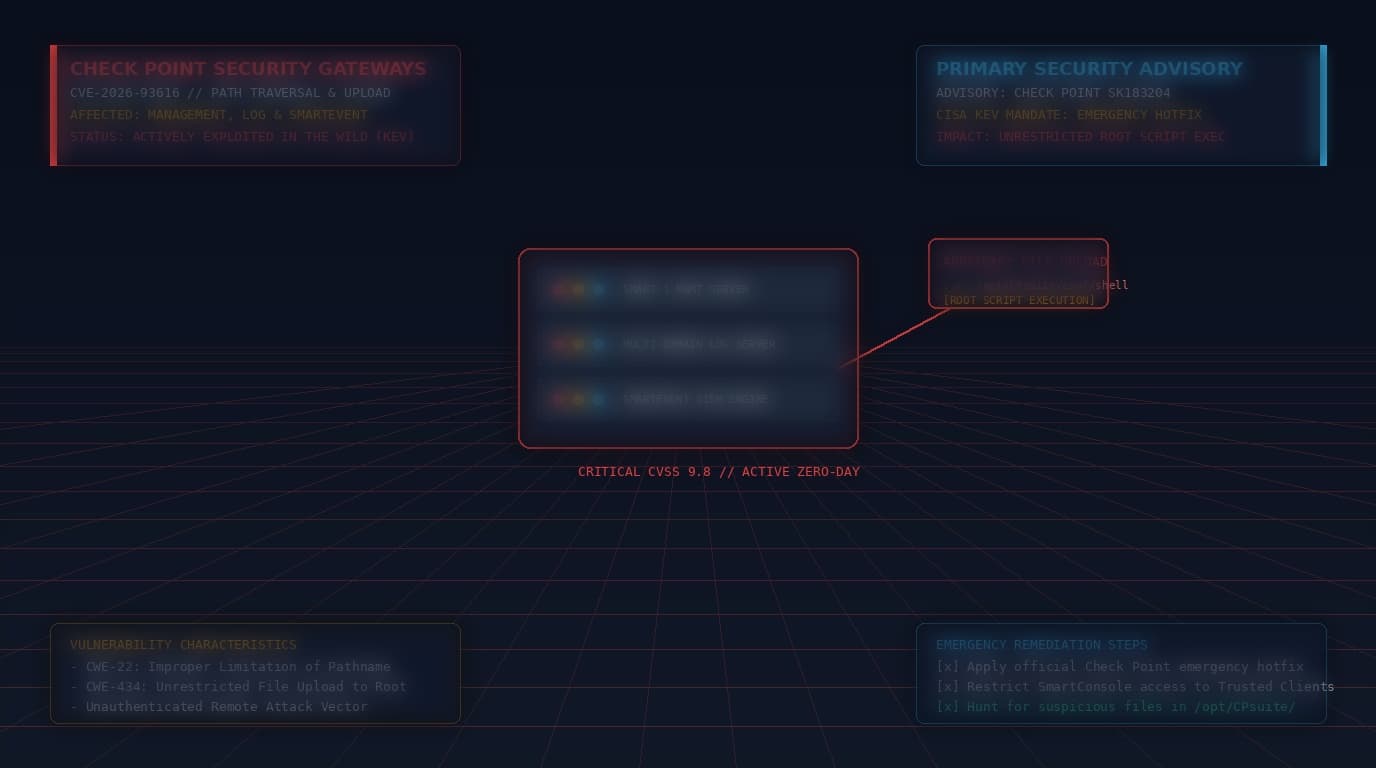
ThreatsCloud & SaaSCriticalCheck Point Security Management Server Path Traversal Exploited to Gain Root Access
CST Editorial Desk
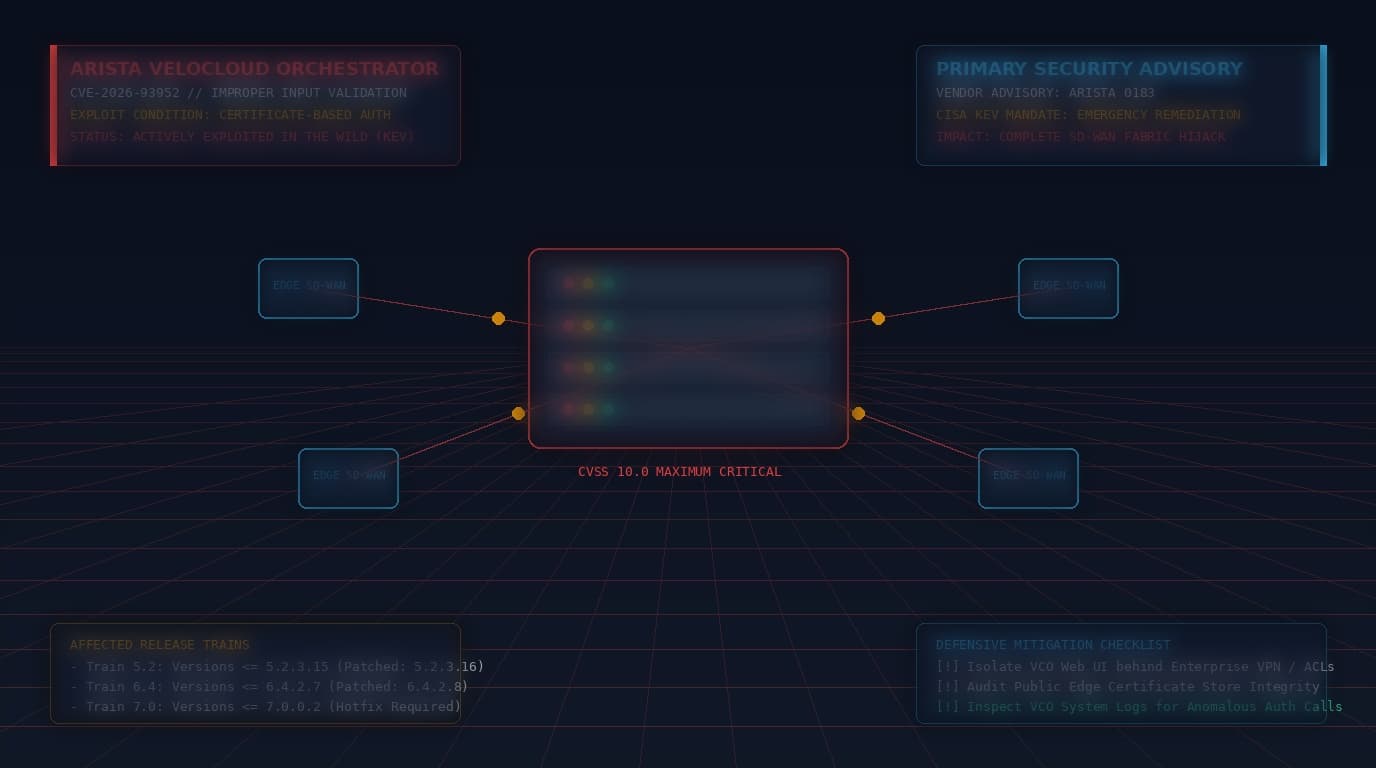
ThreatsCloud & SaaSCriticalArista VeloCloud Orchestrator Zero-Day Exploited to Hijack SD-WAN Edge Gateways
CST Editorial Desk
ThreatsCloud & SaaSCriticalF5 BIG-IP APM Heap Overflow Weaponized to Hijack Gateway Data Planes
CST Editorial Desk
ThreatsCloud & SaaSCriticalCisco Secure Firewall Flaw Weaponized to Compromise Perimeter Gateways
Priya Raman
ThreatsCloud & SaaSCriticalIvanti Sentry Critical OS Command Injection Flaw Exploited in Perimeter Infiltration Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalGoogle Pixel Cellular Modem Zero-Day Flaw Exploited in Targeted Mobile Attacks
Priya Raman
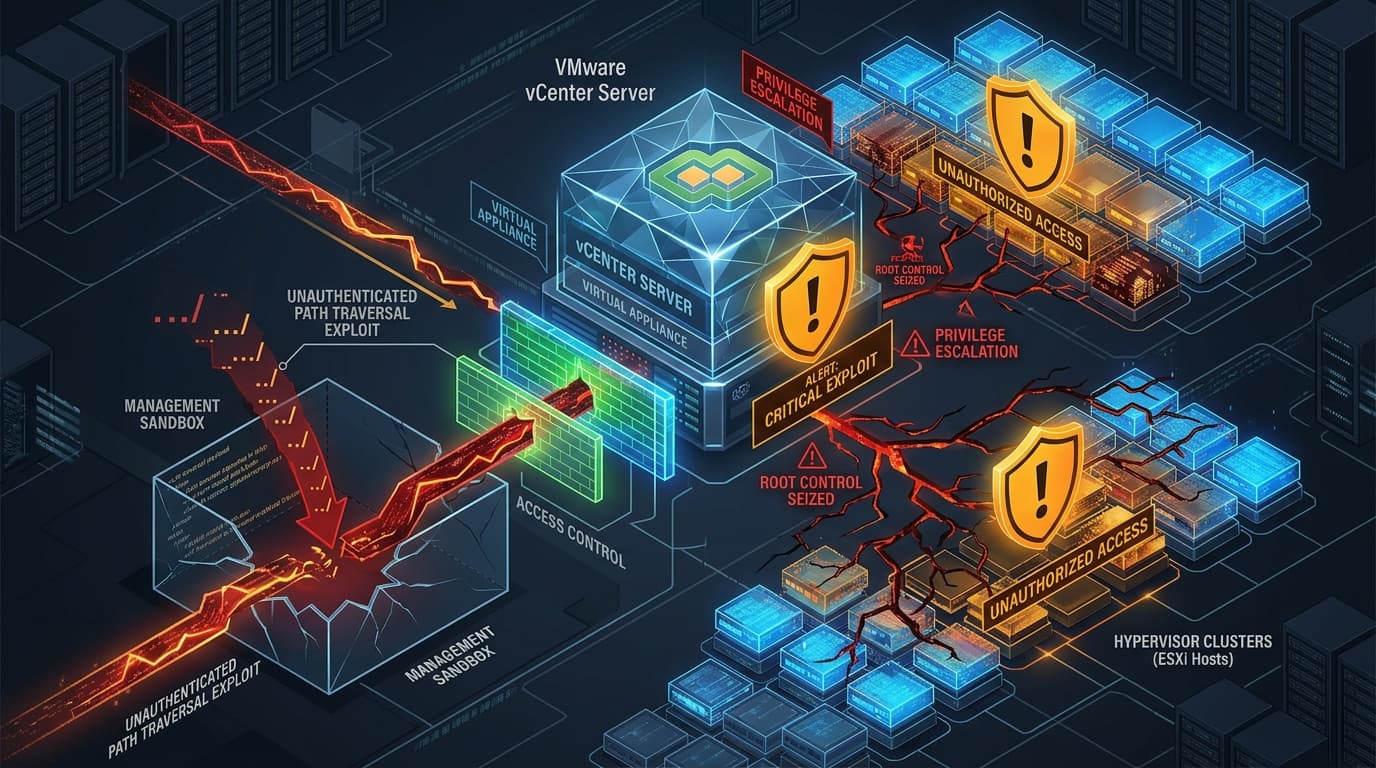
ThreatsCloud & SaaSCriticalVMware vCenter Server Critical Path Traversal Flaw Exploited in Virtualization Attacks
Priya Raman
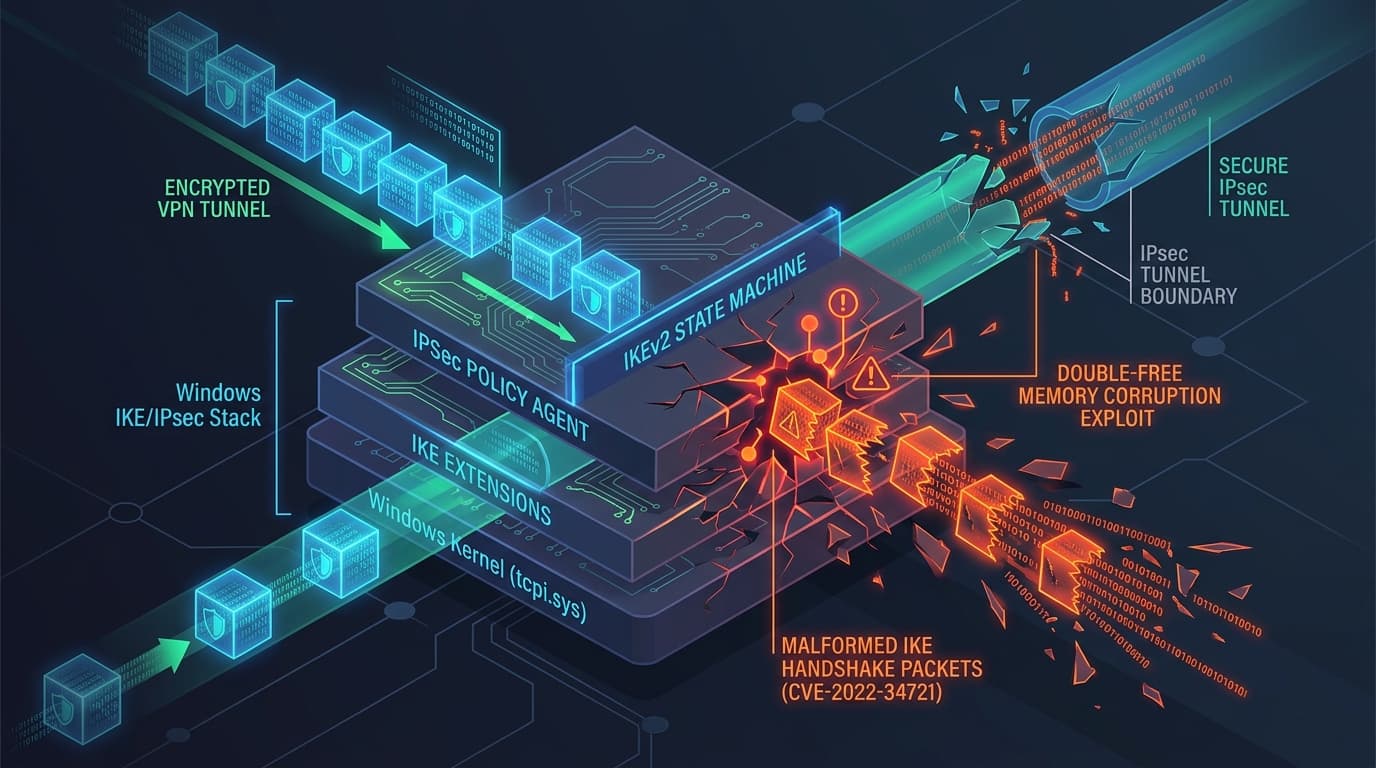
ThreatsCloud & SaaSCriticalMicrosoft Windows IKE Protocol Double-Free RCE Flaw Exploited in Active Network Attacks
Mei-Lin Chen
ThreatsCloud & SaaSCriticalOracle WebLogic Server & Proxy Plug-in Flaw Exploited to Bypass Access Controls
Aisha Noor
ThreatsCloud & SaaSCriticalZimbra Collaboration Suite Command Injection Flaw Exploited in the Wild
Priya Raman
ThreatsCloud & SaaSCriticalCisco Secure Email Gateway Critical SQL Injection Flaw Weaponized in Active Attacks
Mei-Lin Chen
ThreatsCloud & SaaSCriticalCitrix NetScaler CVSS 9.3 authentication bypass CVE-2026-19490 under active in-the-wild exploitation
Daniel Okafor
ResearchCloud & SaaS'ShieldCrash' exploit bypasses Microsoft Defender patch, enabling local SYSTEM file access
Mei-Lin Chen- ThreatsRetail & E-commerceCritical
Adobe warns of exploited Commerce and Magento RCE — patch CVE-2026-75650 now
Priya Raman
Cyber AttackCloud & SaaSCisco Secure FMC authentication bypass CVE-2026-20079 exploited by Qilin ransomware affiliates
Daniel Okafor
ThreatsTelecom & MediaCriticalChinese state-aligned group UNC3569 exploited zero-day flaw in Sogou Input Method to drop GRAYRABBIT backdoor
Mei-Lin Chen
ThreatsCloud & SaaSCriticalGitLab fixes maximum-severity CVSS 10.0 file-read flaw as in-the-wild exploitation begins
Priya Raman