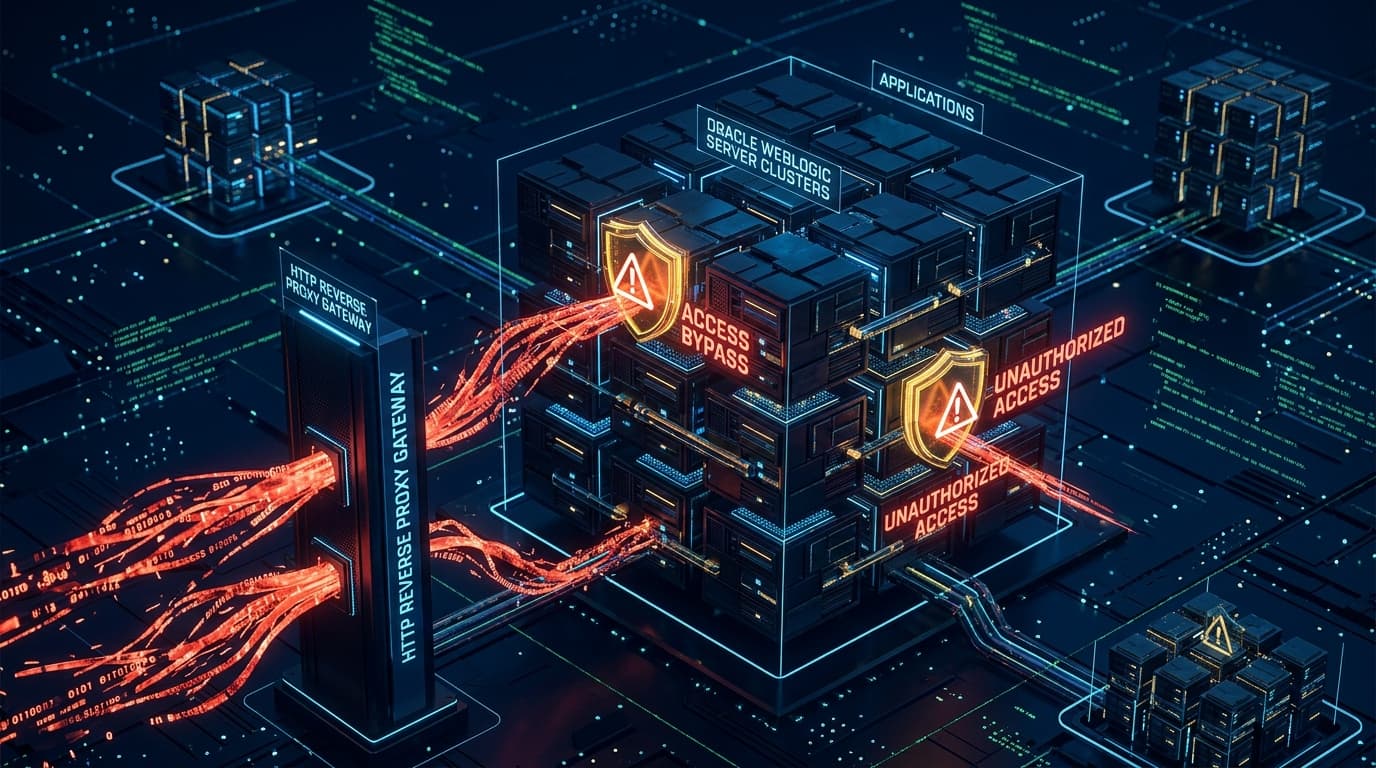
The Cybersecurity and Infrastructure Security Agency (CISA) has officially added CVE-2026-21962 to its Known Exploited Vulnerabilities (KEV) catalog. The flaw resides in the Oracle HTTP Server and Oracle WebLogic Server Proxy Plug-in components, commonly deployed by major financial institutions, government portals, and multinational enterprises to front multi-tier Java enterprise middleware environments.
Rated with a near-maximum CVSS v3.1 base score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H), the vulnerability enables unauthenticated remote adversaries to bypass reverse proxy access controls, reach internal WebLogic administration consoles (such as /console or internal management servlets), and execute administrative operations without providing valid credentials.
Vulnerability Deep Dive: HTTP Path Desynchronization & Reverse Proxy Confusion
According to technical advisories issued by Oracle Product Security, the flaw manifests when WebLogic Server sits behind edge reverse proxies—including Apache HTTP Server, Microsoft Internet Information Services (IIS), or Oracle HTTP Server (OHS)—using the WebLogic Proxy Plug-in (mod_wl):
- Perimeter Filter Bypass: Reverse proxies are typically configured with URL rewrite and access-list rules that block external requests to administrative endpoints such as
/console/*or/management/*. - Parser Inconsistency: By transmitting crafted HTTP requests featuring URL-encoded path traversal sequences, semicolon path parameters (e.g.,
/public;bypass=/console), or double URI encodings, the edge proxy treats the request as directed to a permitted public URI. - WebLogic Servlet Execution: When the Oracle WebLogic Proxy Plug-in forwards the raw URI to the backend managed WebLogic server, the backend Java Servlet engine normalizes the path differently, executing administrative servlets directly under unauthenticated caller contexts.
Reverse proxy confusion vulnerabilities are devastating because perimeter firewalls and WAFs report the incoming traffic as harmless static assets, while backend enterprise servers interpret the payload as high-privilege administrative instructions.
Affected Middleware & Component Matrix
| Oracle Component | Vulnerable Releases | Remediated Patch | CISA Remediation Deadline |
|---|---|---|---|
| Oracle WebLogic Server Proxy Plug-in | 12.2.1.4.0, 14.1.1.0.0 | Security Alert Patch Bundle | Emergency Remediation Order |
| Oracle HTTP Server (OHS) | 12.2.1.4.0 | OHS Critical Patch Update | Emergency Remediation Order |
| Oracle Fusion Middleware Infrastructure | 12.2.1.4.0, 14.1.1.0.0 | October Maintenance Stack | Apply Vendor Bundle |
Detection, Audit & Hardening Commands
Enterprise infrastructure engineers and incident response teams must audit their reverse proxy access logs and WebLogic domain access files immediately:
# Audit Apache / OHS access logs for URI delimiter bypass attempts
grep -E "(;|%3b|%252f|mod_wl)" /var/log/httpd/access_log | grep -E "(console|management)"

# Verify currently installed WebLogic Proxy Plug-in binary version
strings /opt/oracle/ohs/modules/mod_wl.so | grep -i "WebLogic Proxy"

# Audit WebLogic domain access log for direct servlet invocations
grep " 200 " /u01/oracle/user_projects/domains/base_domain/servers/AdminServer/logs/access.log | grep "/console"
Recommended Enterprise Mitigation Checklist
- Apply Emergency Oracle CPU Hotfix: Apply the interim patch for CVE-2026-21962 released via My Oracle Support (MOS) across all edge proxy servers and WebLogic managed instances.
- Normalize URI Paths at the Edge: Configure web application firewalls (WAFs) and edge load balancers to reject any incoming HTTP requests containing semicolons or unresolved relative directory components in the request line.
- Strict Network Segmentation: Ensure WebLogic Administration Ports (default TCP 7001/7002) are isolated strictly to out-of-band management subnets with zero route reachability from external internet gateways.