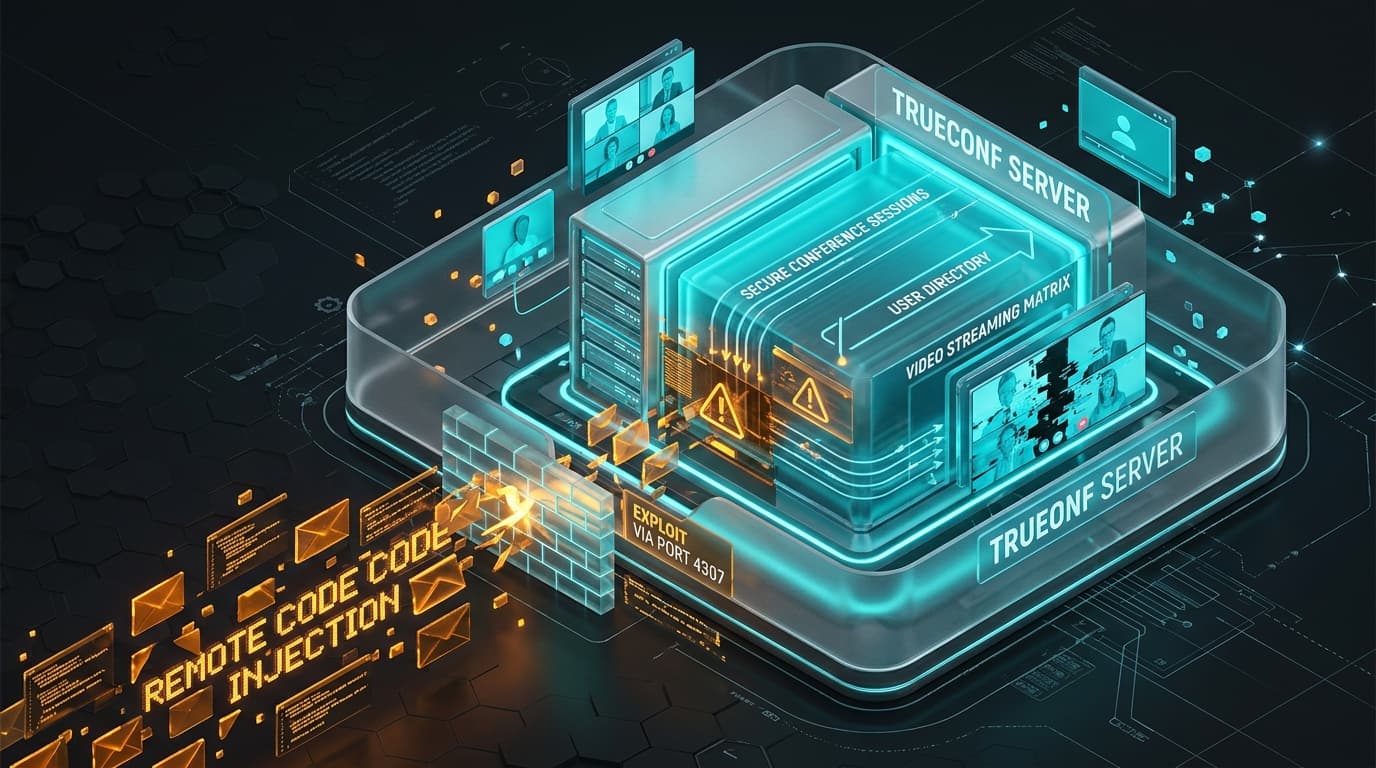
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities catalog to include CVE-2026-72530, an unauthenticated remote code injection flaw affecting TrueConf Server. The software is a self-hosted unified communications and video conferencing platform deployed extensively across enterprise networks, government agencies, and aerospace organizations seeking sovereign, on-premises collaboration infrastructure.
Carrying a CVSS v3.1 score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H), the vulnerability allows an unauthenticated remote adversary with network reachability to TrueConf Server's proprietary communication listener (typically TCP port 4307) to inject and execute arbitrary code within the host operating system context.
Vulnerability Analysis: Proprietary Protocol Packet Parsing Breakdown
TrueConf Server communicates with desktop clients, mobile applications, and room endpoints via a proprietary high-performance binary signaling protocol operating over TCP port 4307:
- Unauthenticated Network Access: TrueConf servers configured to facilitate remote work or external client connections frequently expose TCP port 4307 directly to corporate WANs or the public internet.
- Packet Boundary Desynchronization: During initial connection handshakes and user registration routines, the service fails to validate structure boundaries and length parameters embedded in incoming signaling packets.
- Code Injection & Memory Takeover: Crafted malformed binary payloads overwrite function pointers within the server process memory, redirecting execution to injected shellcode. The attacker gains execution privileges under
NT AUTHORITY\SYSTEMon Windows ortrueconfservice privileges on Linux.
Video conferencing servers process live audio, video feeds, screen sharing data, and internal organizational directories. A complete compromise of the conferencing infrastructure provides threat actors with eavesdropping access to confidential executive strategy sessions and intellectual property discussions.
Affected Releases & Security Updates
| TrueConf Component | Vulnerable Releases | Remediated Release | Remediation Status |
|---|---|---|---|
| TrueConf Server (Windows) | Versions prior to 5.4.5 | TrueConf Server 5.4.5.10222 | Emergency Directive Action Required |
| TrueConf Server (Linux / Debian) | Versions prior to 5.4.5 | TrueConf Server 5.4.5.10222 | Emergency Directive Action Required |
| TrueConf Enterprise Multi-Node | All cluster versions prior to 5.4.5 | Update Node Cluster to 5.4.5 | Immediate Action Required |
Forensic Audit & Mitigation Directive
Telecommunications engineers and SOC teams should execute the following forensic verification commands across TrueConf host servers:
# Check active TCP port 4307 listener status
netstat -ano | grep 4307

# Audit TrueConf Server event logs for anomalous connection termination
grep -iE "exception|memory corrupt|invalid packet" /opt/trueconf/server/var/log/server.log

# Block direct internet access to port 4307 via host firewall rules
sudo ufw deny 4307/tcp
Recommended Enterprise Safeguards
- Immediate Upgrade: Apply TrueConf Server release 5.4.5 or higher across all production host servers immediately.
- Enforce Perimeter VPN / Reverse Proxy Isolation: Restrict external access to port 4307 strictly through authenticated VPN tunnels or secure enterprise perimeter proxies.
- Endpoint Directory Integrity Verification: Audit active conference user directories and administrator accounts for unauthorized accounts provisioned prior to remediation.