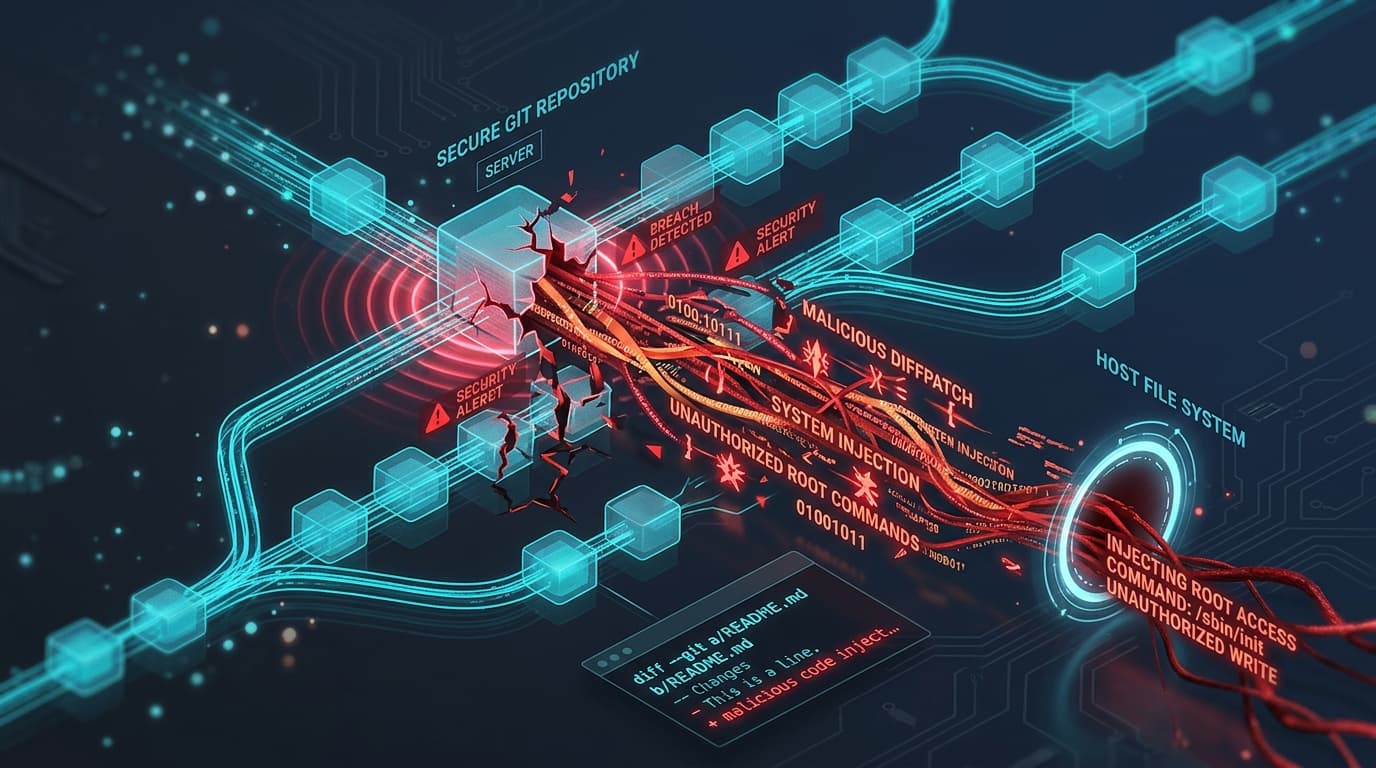
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency warning adding CVE-2026-60004 to its Known Exploited Vulnerabilities catalog. The vulnerability affects Gitea, the lightweight, self-hosted Git version control service deployed extensively across defense contractors, technology enterprises, and on-premises engineering teams.
Rated with a near-maximum CVSS v3.1 score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H), the vulnerability allows remote attackers with repository write or pull request submission capabilities to execute arbitrary operating system commands on the hosting server, compromise internal source code repositories, and pivot across internal development infrastructure.
Exploitation Mechanics: Malicious Diffpatch Sanitization Escape
The root cause lies in Gitea's internal patch preview and diff generation subsystem:
- Patch Submission: When a user opens a pull request or applies a unified diff patch through the web UI, Gitea invokes internal Git helper binaries and custom Go diff parsers to compute file changes and generate side-by-side diff previews.
- Git Command Argument Injection: Specially formatted diff headers containing malicious control characters, escaped newline delimiters, or shell metacommands are improperly sanitized before being passed to underlying
git applyorgit diffsystem executions. - Command Execution in Gitea Context: The attacker's embedded commands escape the command arguments and execute directly within the shell environment of the Gitea service account (typically
git), granting the adversary interactive shell access to server file systems, SSH private keys, and environment tokens.
Source code repositories are the epicenter of intellectual property. An uncontained code injection flaw in a Git server not only exposes confidential source code but gives adversaries the ability to plant backdoors directly into release branches.
Affected Releases & Upgrades
| Gitea Branch | Vulnerable Releases | Remediated Version | Remediation Action |
|---|---|---|---|
| Gitea 1.22.x | 1.22.0 through 1.22.3 | 1.22.4 | Emergency Upgrade Mandated |
| Gitea 1.21.x (Legacy) | All 1.21 releases | 1.21.11 Hotfix | Emergency Upgrade Mandated |
| Forgejo (Fork) | Prior to v7.0.5 | v7.0.5 or v8.0.0 | Apply Upstream Patch |
Incident Response & Hardening Playbook
Administrators managing on-premises Gitea or Forgejo servers should execute the following forensic triage steps immediately:
# Inspect Gitea application logs for malformed diffpatch executions
grep -iE "git apply|diffpatch|metacharacter" /var/lib/gitea/log/gitea.log

# Audit git user process tree for unexpected child shells
ps -ef | grep -E "^git.*(sh|bash|curl|nc|python)"

# Check SSH authorized_keys file on Gitea server for unauthorized keys
cat /home/git/.ssh/authorized_keys
Recommended Defensive Controls
- Immediate Upgrade: Upgrade to Gitea version 1.22.4 or higher immediately. The update replaces raw shell parameter passing with strictly isolated subprocess execution and rejects malformed diffpatch headers.
- Restrict Repository Permissions: Enforce mandatory branch protection rules and disable public repository creation on self-hosted instances exposed to external networks.
- Enforce Container Isolation: Run Gitea instances within rootless containers (e.g., Podman or unprivileged Docker) with read-only root filesystems and restricted capability sets (dropping
CAP_SYS_ADMIN).