Schneider Electric and CISA warn of improper authentication validation in PowerChute Serial Shutdown allowing unauthorized actors to disrupt critical infrastructure power.
CISA adds Linux kernel cryptographic socket race condition vulnerability CVE-2025-39964 to KEV catalog following active root privilege escalation attacks.
CISA orders federal agencies to patch Ubiquiti UniFi OS vulnerability CVE-2026-34909 enabling unauthenticated network configuration extraction and takeover.
Schneider Electric and CISA warn of improper authentication validation in PowerChute Serial Shutdown allowing unauthorized actors to disrupt critical infrastructure power.
India's six-hour CERT-In reporting clock has run since June 2022. From May 2027 a second DPDP clock starts on the same incident. Build one intake process now.
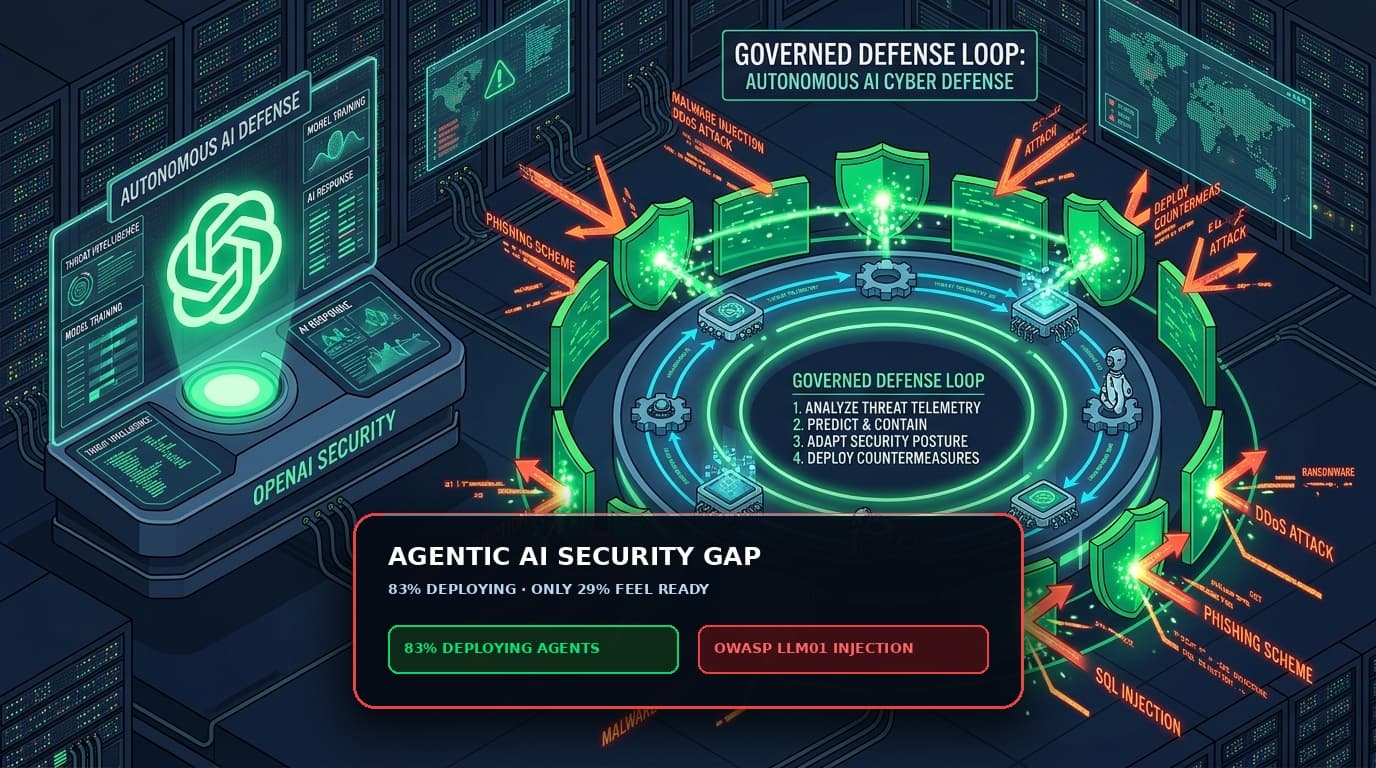
CISA adds critical Langflow AI vulnerabilities CVE-2026-0770 and CVE-2026-55255 to KEV catalog as threat actors weaponize agentic pipeline execution flaws.
A joint cybersecurity advisory from CISA, NSA, and FBI alerts defense contractors and cloud vendors to sophisticated state-sponsored AI model extraction campaigns.
Daniel Okafor··9 min read
News • Threats • Insights
Inform. Defend. Stay Ahead.
Join security leaders and practitioners who start their day with the exploited CVEs, live campaigns and analysis that actually change what they do next.
✓ Daily Briefing at 07:00 UTC✓ Zero Vendor Marketing Spam✓ 1-Click Instant Unsubscribe
You're on the list.
We'll email you when the next issue goes out.
The Daily Brief
Exploited CVEs, live campaigns and the analysis that matters — one email each weekday.