Topic
Cloud Security: news, advisories and analysis
101 articles
CyberSecureToday covers Cloud Security across 101 articles published between 8 Sep 2026 and 29 Oct 2026. The coverage includes 81 vulnerability advisories, 8 incident or breach reports and 9 analysis or guidance pieces. 77 advisories are rated critical or high severity, and 13 involve flaws listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on Cloud Security most often intersect with AWS, IAM and Privilege Escalation, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Broadcom VMware ESX Vulnerability Exploited in Wild Attacks”, was published 29 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsCloud & SaaSBreakingCST Editorial Desk
ThreatsCloud & SaaSBreakingAdobe Commerce and Magento Unrestricted File Upload Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalCollabora Online – Built-in CODE Server OS Command Injection Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSSiemens Software Center Vulnerability Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSHighSingCERT Issues Critical Alert as CARBONATO Botnet Exploits Exposed Docker Remote APIs Across Cloud Workloads
Aisha Noor
ThreatsCloud & SaaSPlex Media Server Server-Side Request Forgery Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSCriticalPlex Media Server Input Validation Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSHighEG Secure Solutions SiteGuard Server Edition OS Command Injection Flaw Exploited in Wild Attacks
CST Editorial Desk
ThreatsCloud & SaaSHighAWS Amplify CLI Prototype Pollution Flaw in Velocity Template Engine Enabled Local Code Execution
Aisha Noor
Cyber AttackCloud & SaaSConnectWise Cloud Backup Credential Leak Weaponized to Hijack Microsoft 365 Tenants
Aisha Noor
ThreatsCloud & SaaSCriticalMicrosoft Patches Maximum-Severity CVSS 10.0 Privilege Escalation Flaw CVE-2026-96207 in Partner Center Cloud Service
CST Editorial Desk
ThreatsCloud & SaaSCriticalMage OSS Critical Authentication Bypass Flaw CVE-2026-111823 Exposes Enterprise ETL Data Pipelines to Remote Takeover
CST Editorial Desk
InsightsBanking & FintechRBI Cyber Security Framework Mandates 6-Hour Breach Reporting and Cloud Audits
Priya Raman
ThreatsCloud & SaaSHighAWS Systems Manager (SSM) Agent OS Command Injection Flaw CVE-2026-87911 Patched
CST Editorial Desk
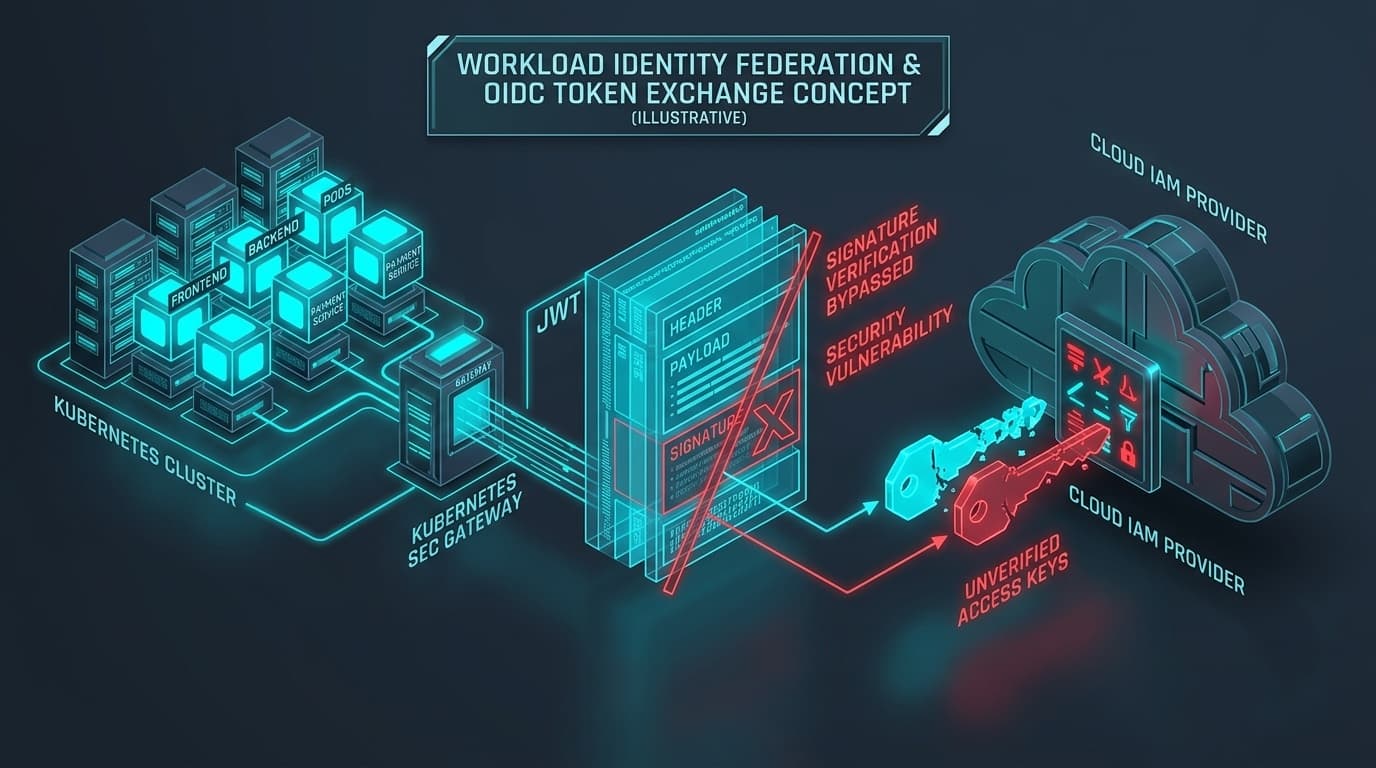
ThreatsCloud & SaaSHighGoogle Cloud Workload Identity Federation OIDC Token Bypass Flaw CVE-2026-19410 Remediated
Aisha Noor
ThreatsCloud & SaaSHighAWS IAM Identity Center Flaw Left Revoked Session Tokens Active
CST Editorial Desk
ThreatsCloud & SaaSHighAzure Arc Connected Machine Agent Local Privilege Escalation Flaw CVE-2026-83711 Enables Host Compromise
Aisha Noor
NewsCloud & SaaSCriticalAWS IAM Identity Center SAML Canonicalization Flaw Enables Cross-Account Administrative Role Assumption (CVE-2026-78520)
CST Editorial Desk
ThreatsCloud & SaaSCriticalAWS S3 Express One Zone Flaw Allowed Session Token Reuse Across Enclaves
CST Editorial Desk
Cyber AttackCloud & SaaSElectric Vehicle Maker Discloses Unauthorized Access to Global Fleet Telematics Platform
Priya Raman
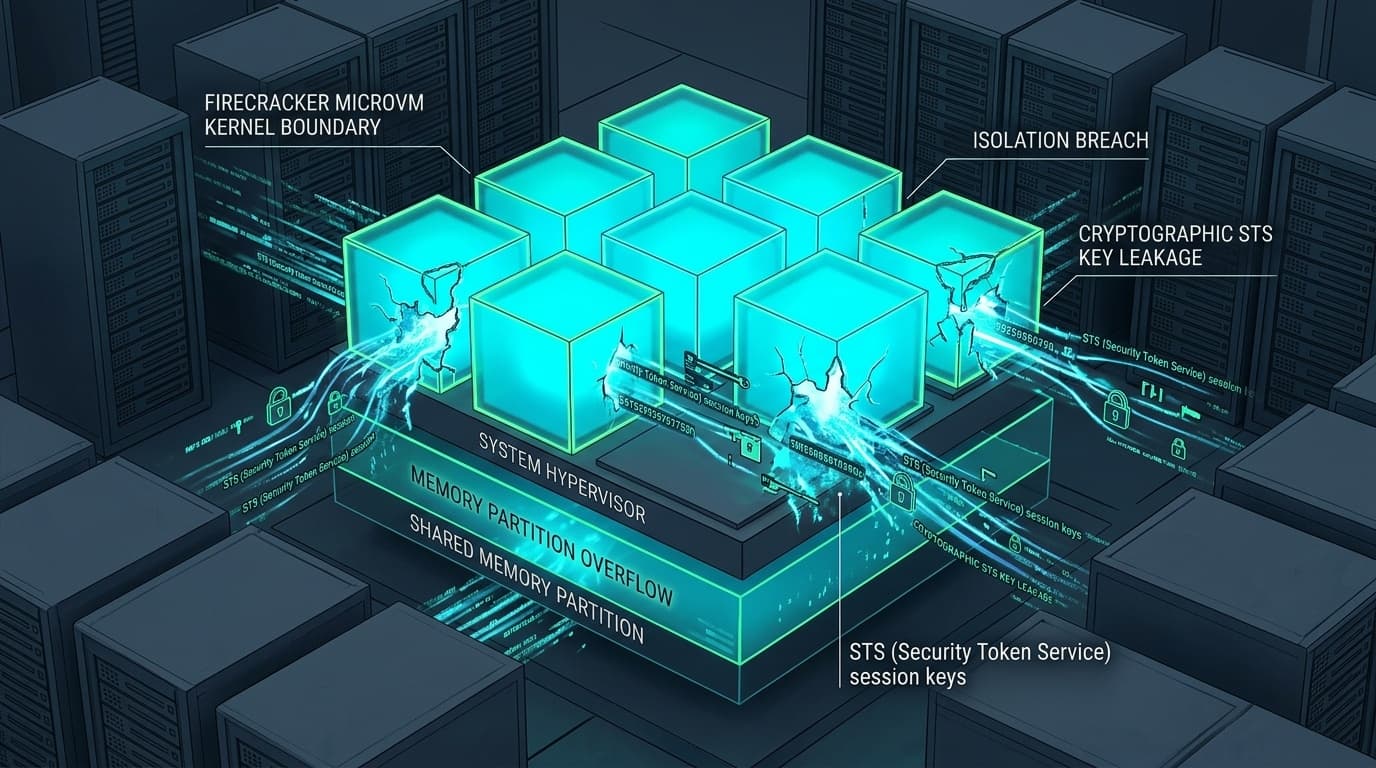
ThreatsCloud & SaaSCriticalAWS Lambda MicroVM Isolation Flaw Exposed STS Session Keys Across Invocations
CST Editorial Desk
ThreatsCloud & SaaSCriticalGoogle Cloud Workload Identity Flaw Enabled Cross-Organization Service Account Impersonation
CST Editorial Desk