The Cybersecurity and Infrastructure Security Agency (CISA) has issued a binding operational alert adding CVE-2023-49105 to its Known Exploited Vulnerabilities catalog. The advisory warns of widespread automated exploitation targeting enterprise deployments of ownCloud, the self-hosted open-source file synchronization and content collaboration platform.
The vulnerability carries a near-maximum CVSS v3.1 base score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). Categorized under CWE-287: Improper Authentication, the defect permits unauthenticated remote attackers to bypass access barriers, view confidential file repositories, modify documents, or wipe directory trees entirely.
Root Cause Analysis: Unsigned Pre-Signed URL Bypass
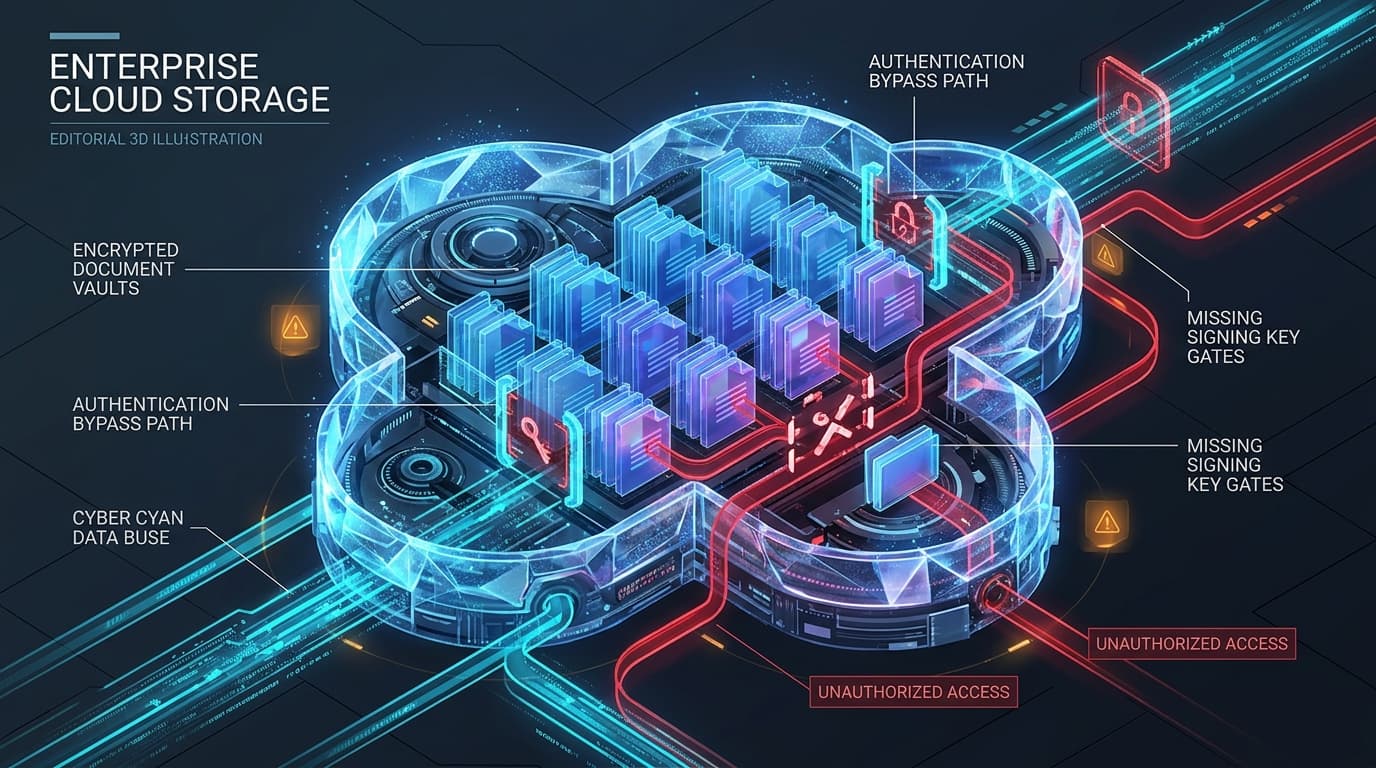
The vulnerability lies in the implementation of ownCloud’s WebDAV authentication filter and Graph API routing components. When users access files via WebDAV share links or third-party integrations, the application expects requests to contain a cryptographic HMAC signing key:
- Missing Default Key: If an administrator has not explicitly generated or configured a system-wide signing key (a common oversight in containerized or default installations), the validation check defaults to an insecure state.
- Arbitrary File Access: An attacker knowing or enumerating the username of a target employee can send crafted HTTP requests directly to the WebDAV endpoint. The server interprets the absence of a required signing key as a valid authorization bypass.
- Unauthenticated File Manipulation: The adversary inherits the file manipulation privileges of the target user, enabling the exfiltration of financial spreadsheets, intellectual property, or the injection of malicious ransomware binaries disguised as corporate documents.
Cloud file collaboration servers store the crown jewels of enterprise collaboration. An authentication bypass vulnerability on ownCloud exposes internal intellectual property to external extraction without leaving standard login log footprints.
Affected Software & Patch Requirements
| Software Package | Affected Versions | Remediated Version | Remediation Status |
|---|---|---|---|
| ownCloud Server Core | 10.6.0 through 10.13.0 | 10.13.4 or later | Mandatory Hotfix Required |
| ownCloud Infinite Scale (OCIS) | Independent Go Architecture | Not Affected | N/A (Memory Safe Core) |
Remediation & Forensic Verification Steps
Administrators responsible for ownCloud instances must take the following defensive actions immediately:
- Upgrade ownCloud Server: Apply ownCloud Server version 10.13.4 or higher, which enforces strict signature validation and eliminates the fallback condition.
- Generate Mandatory Signing Keys: If an immediate upgrade is scheduled during a maintenance window, manually generate and configure signing keys in the ownCloud configuration:
# Generate secure signing key occ config:system:set signing_key --value="$(openssl rand -base64 32)" - Audit Web Server Access Logs: Search web server access logs for anomalous requests targeting
/remote.php/davwithout accompanying authentication session cookies:grep -E "remote.php/dav/files" /var/log/nginx/access.log | grep " 200 " | grep -v "user=" - Restrict Network Perimeter Exposure: Place internal ownCloud collaboration servers behind authenticated Single Sign-On (SSO) reverse proxies or VPN boundaries.