The Cybersecurity and Infrastructure Security Agency (CISA) has officially designated CVE-2026-8452 as an actively exploited security vulnerability, ordering federal civilian executive branch agencies to patch affected Citrix NetScaler ADC and NetScaler Gateway appliances within strict operational deadlines.
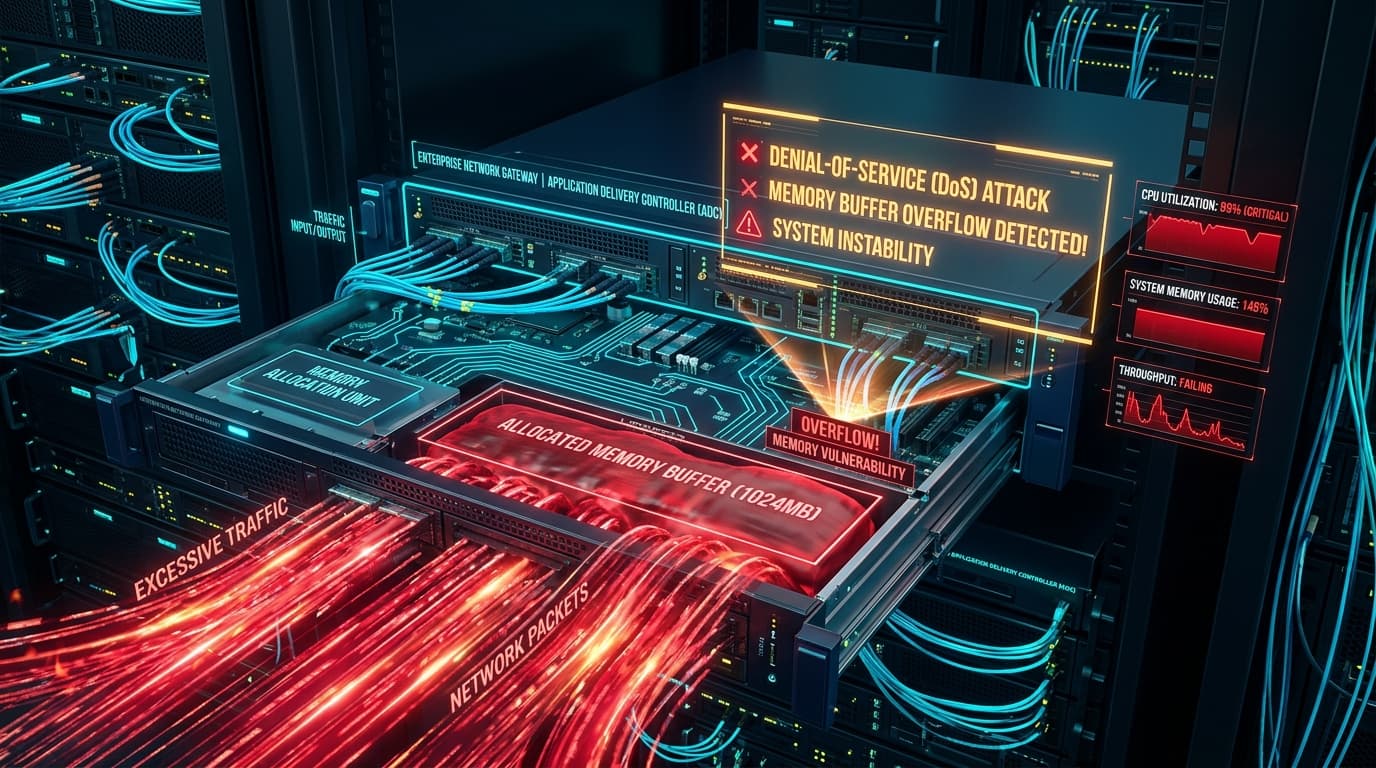
The vulnerability carries a Common Vulnerability Scoring System (CVSS v3.1) score of 8.6 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). Categorized under CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer, the flaw permits unauthenticated remote threat actors to trigger fatal buffer overruns in the core packet processing daemon (nsppe), crashing network gateways and severing remote access for entire enterprise workforces.
Technical Root Cause: Memory Boundary Flaw in HTTP Header Processing
NetScaler Application Delivery Controllers process inbound HTTP and SSL VPN transactions at multi-gigabit line rates using dedicated packet engines. The vulnerability exists within the memory boundary validation logic handling fragmented HTTP request headers and SSL handshake extension frames:
- Fragmented Packet Transmission: The attacker transmits a stream of crafted TCP packets containing fragmented HTTP headers with deliberate byte-boundary misalignments.
- Buffer Boundary Failure: The
nsppepacket engine fails to clamp the write pointer against the pre-allocated internal memory buffer, causing incoming bytes to overwrite adjacent operational structures in kernel memory. - Kernel Panic & Gateway Crash: The corrupted memory state triggers an immediate unhandled exception, causing the NetScaler operating system to panic and reboot. In environments configured with High Availability (HA) failover, repeating the exploit against the standby appliance completely knocks out enterprise remote connectivity.
Denial of service against enterprise identity gateways is a favored tactic for ransomware crews. By crashing perimeter SSL VPN appliances during active intrusions, adversaries disrupt defensive incident response teams from remotely accessing infected server environments.
Affected Product Versions & Patched Builds
| Product Line | Affected Builds | Remediated Build | Deployment Urgency |
|---|---|---|---|
| NetScaler ADC & Gateway 14.1 | Builds prior to 14.1-73.35 | 14.1-73.35 or later | Immediate |
| NetScaler ADC & Gateway 13.1 | Builds prior to 13.1-63.24 | 13.1-63.24 or later | Immediate |
| NetScaler ADC & Gateway FIPS / NDcPP | Legacy compliance builds | 13.1-37.280 | High |
Remediation Checklist & HA Gateway Best Practices
Network security engineers and infrastructure administrators should execute the following mitigation checklist:
- Deploy Firmware Hotfixes: Immediately upgrade all primary and secondary NetScaler nodes to the patched firmware builds released by Citrix.
- Audit NetScaler Crash Dumps: Inspect
/var/crash/and/var/log/ns.logon NetScaler appliances for recent core dump generation or unexpected kernel reboot records:# Check for crash dumps in NetScaler shell ls -la /var/crash/ tail -n 100 /var/log/ns.log | grep -i "panic|coredump|reboot" - Rate Limit Perimeter Ingress: Configure perimeter firewalls or upstream DDoS mitigation scrubbers to rate-limit incomplete TCP connection handshakes and fragmented HTTP packets directed at NetScaler virtual IP (VIP) addresses.
- Separate Out-of-Band Management: Ensure management interfaces (NSIP) are strictly confined to dedicated internal networks and never exposed to the public internet.