Executive Threat Advisory: Operational Technology Edge Exposure
Industrial automation leader ABB, in coordination with the Cybersecurity and Infrastructure Security Agency (CISA) ICS-CERT team, has issued a high-severity security advisory regarding an elevation of privilege vulnerability in the ABB Ability Edgenius operations data management platform.
Tracked as CVE-2026-31431, the vulnerability carries a CVSS v3.1 base score of 8.4 (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). The defect allows a locally authenticated operator or a compromised container application running on the Edgenius node to break out of container isolation, overwrite host kernel memory, and acquire unrestricted root administrative control over the industrial edge device.
Industrial OT Architecture & The Purdue Model Impact
ABB Ability Edgenius functions as an edge compute platform bridging Operational Technology (OT) shop-floor equipment with IT enterprise systems. It collects, standardizes, and processes real-time telemetry from programmable logic controllers (PLCs), distributed control systems (DCS), and intelligent electronic devices (IEDs).
Within the Purdue Enterprise Reference Architecture (PERA), Edgenius devices typically operate at Level 2 (Area Supervisory Control) or Level 3 (Site Operations):
- Boundary Breach: Obtaining root access on the Edgenius host bypasses PERA isolation, allowing an attacker to pivot from third-party analytics containers directly into industrial control network segments.
- Process Manipulation: Attackers can tamper with OPC Unified Architecture (OPC UA), Modbus TCP, and MQTT communication channels, injecting fraudulent telemetry into human-machine interfaces (HMIs) or masking unauthorized setpoint modifications on active production lines.
Root Cause: Kernel "Copy Fail" Memory Corruption (CWE-120)
The Edgenius appliance utilizes an optimized Linux kernel distribution with specialized real-time drivers for industrial serial and ethernet bus interfaces. A memory management defect occurs in the inter-process communication driver when handling nested container shared-memory descriptors:
- An attacker inside an edge analytics container allocates a malformed shared memory buffer via the driver interface.
- The driver fails to validate bounds during copy-on-write operations, resulting in a predictable buffer overflow into adjacent kernel memory structures.
- By overwriting the task credentials pointer (
struct cred), the container process elevates its effective UID from unprivileged (uid=1001) to root (uid=0) on the host operating system.
Remediation & IEC 62443 Defensive Measures
Asset owners in energy, manufacturing, chemicals, and water utility sectors must apply the following mitigations:
| Layer | Required Action | Standard Reference |
|---|---|---|
| Firmware Patching | Upgrade ABB Ability Edgenius to v2.2.4-patch1 or newer. | IEC 62443-4-2 Component Security |
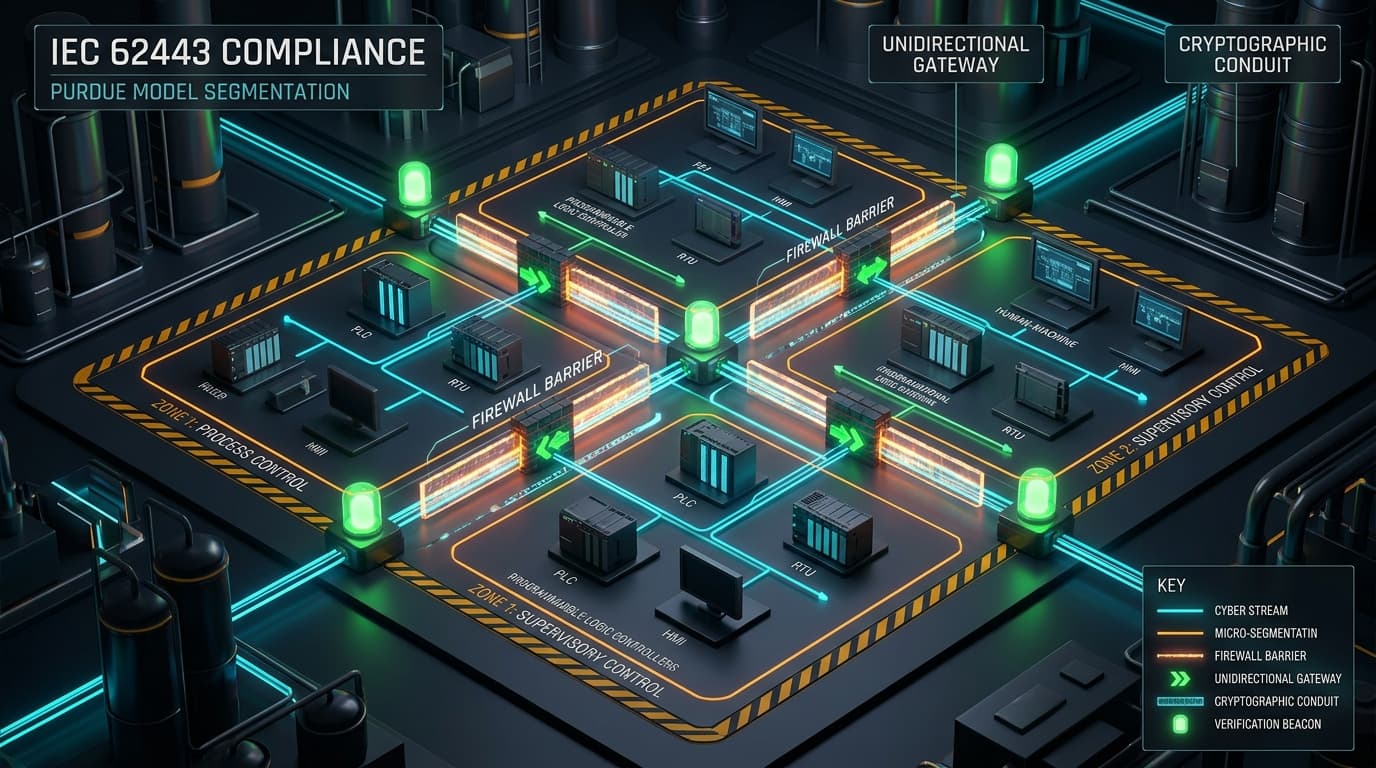
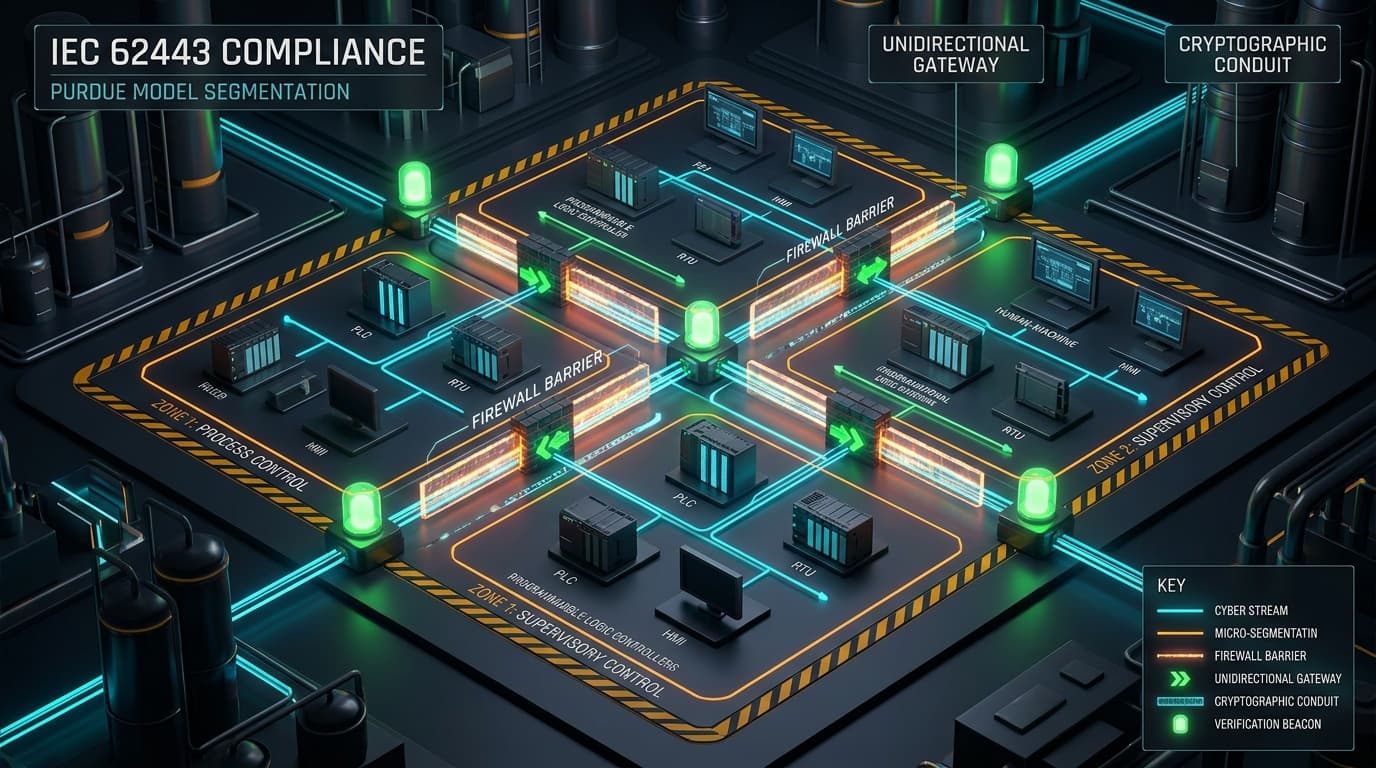
| Zone Segmentation | Enforce strict conduit boundary firewalls isolating Edgenius nodes from general corporate IT networks. | IEC 62443-3-2 Zones & Conduits |
| Container Sandboxing | Disable rootless container escape flags, drop CAP_SYS_ADMIN, and enforce read-only container root filesystems. |
CIS Docker & Linux Benchmark |
| Protocol Inspection | Deploy deep packet inspection (DPI) on OT firewalls to validate Modbus and OPC UA protocol commands. | IEC 62443-3-3 System Security |