Executive Industrial Threat Intelligence: Substation Protection Relays at Risk
The Cybersecurity and Infrastructure Security Agency (CISA) has released an urgent Industrial Control Systems (ICS) advisory, ICSA-26-258-05, highlighting critical vulnerabilities in Siemens Reyrolle 7SR5 numerical protection relays deployed across electrical transmission substations, power generation facilities, and industrial high-voltage distribution networks. Rated CVSS 8.6, the vulnerability enables unauthenticated network adversaries within the substation local area network (LAN) to send malformed supervisory packets that crash the device firmware, rendering overcurrent and earth fault protection inoperative.
Protection relays serve as the frontline safety mechanism in modern electrical substations. When short circuits, lightning strikes, or phase imbalances occur on transmission lines, relays detect anomalous current signatures within milliseconds and trip high-voltage circuit breakers to prevent catastrophic transformer explosions or wide-area blackouts. An unhandled denial of service condition in a protection relay leaves grid transformers unprotected or induces unintended breaker trips that destabilize the bulk electrical power grid.
Vulnerability Mechanics & Protocol Parsing Breakdown (CWE-400 / CWE-20)
The defect exists within the network protocol communications stack of the Reyrolle 7SR5 relay, specifically in the state machine handling incoming supervisory control commands via IEC 60870-5-103 and DNP3 over IP (TCP port 20000 and port 2404):
When an engineering workstation or Remote Terminal Unit (RTU) communicates with the relay, the Ethernet interface processes Application Layer Protocol Data Units (APDUs). A boundary parsing defect in the message length validation handler fails to handle fragmented frames containing unexpected Type Identification headers:
IEC 60870-5-103 Malformed Frame:
[ Start Byte: 0x68 ]
[ Length: 0xFF ]  <--- Inconsistent length parameter triggering buffer overflow
[ Length: 0xFF ]
[ Control Field: 0x43 ]
[ Type ID: 0x7E (Vendor Diagnostic Override) ]
[ Variable Structure Qualifier: 0x01 ]
[ Cause of Transmission: 0x09 ]
[ Payload Data: Obfuscated buffer overrun sequence ]
When the relay's micro-controller parses the malformed frame, an unhandled exception triggers a hardware watchdog timeout, forcing the relay into a continuous reboot loop (Defective Lockout Mode). During this period, the relay ceases real-time current sampling and drops supervisory communication with the substation SCADA Human-Machine Interface (HMI).
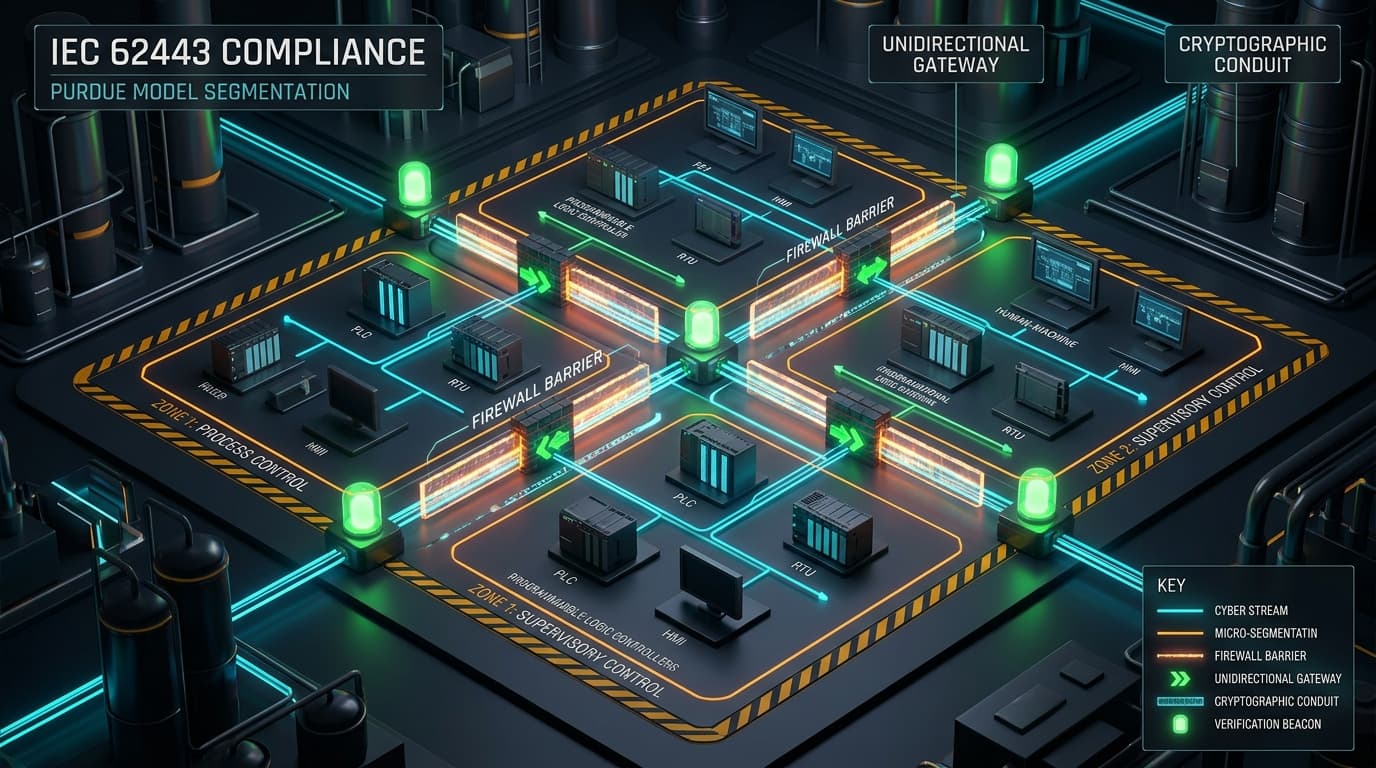
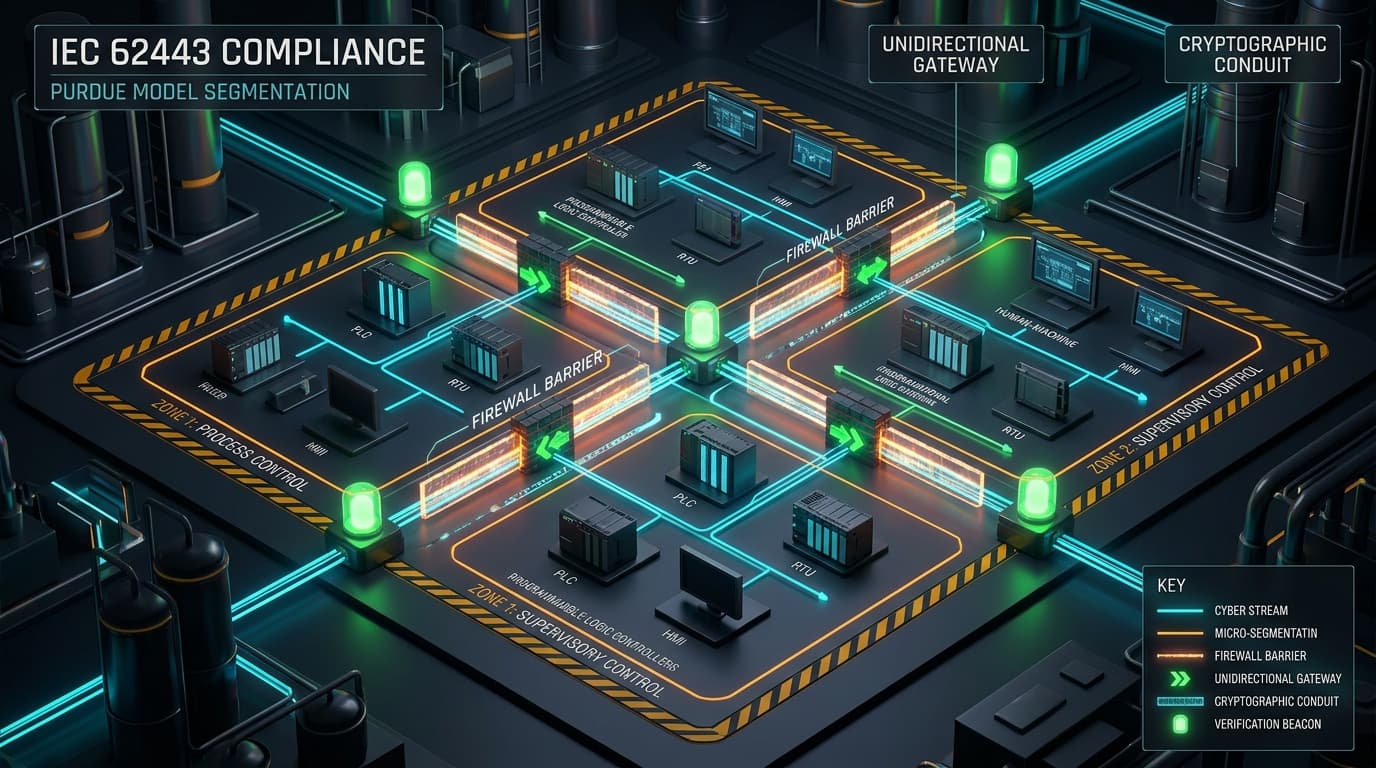
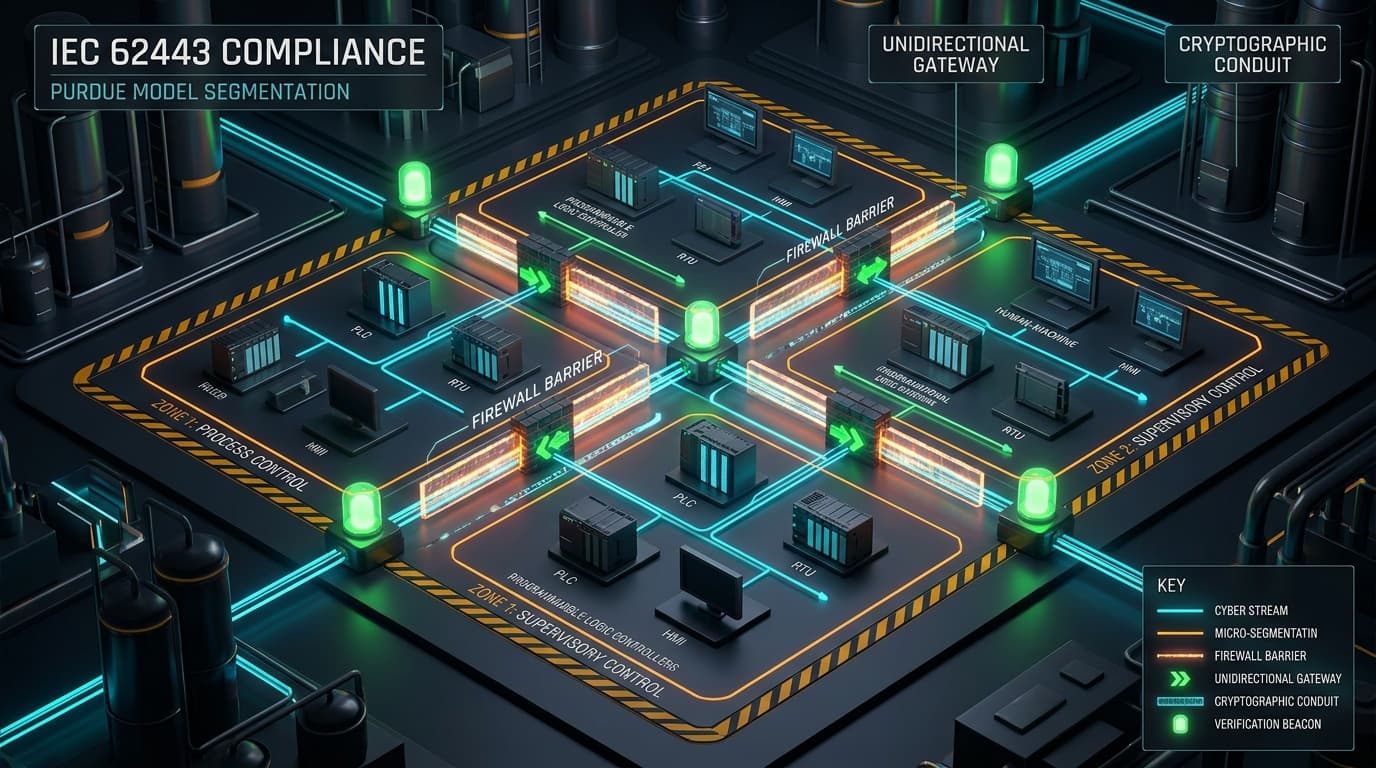
IEC 62443 Alignment & Substation Segmentation Strategy
Under the IEC 62443 industrial cybersecurity standard, protection relays reside in Purdue Model Level 1 (Basic Control / Safety Protection). Securing these assets requires strict adherence to IEC 62443-3-2 (Zones and Conduits):
| Purdue Level | Network Substation Role | IEC 62443 Security Level Target | Protective Conduit Controls |
|---|---|---|---|
| Level 3: Substation Operations | Substation Gateway, Engineering Workstation | SL-T 2 | Role-Based Access Control, MFA, Audit Logging |
| Level 2: Supervisory HMI | Local Substation HMI, Station Bus (IEC 61850) | SL-T 3 | Industrial Protocol Filtering, VLAN Isolation |
| Level 1: Protection & Control | Reyrolle 7SR5 Protection Relays, Merging Units | SL-T 4 | Isolated Process Bus, No Direct External IP Routing |
Remediation Blueprint & Defensive Playbook
Electric utilities and industrial plant electrical engineers must deploy the following remediation measures:
1. Upgrade Relay Firmware to Mitigated Release
Download and flash the official Siemens ProductCERT firmware update via the Reydisp Evolution engineering software:
# Firmware remediation matrix for Siemens Reyrolle 7SR5:
# - Reyrolle 7SR511 Overcurrent Relay: Upgrade to Firmware v2.10 or later
# - Reyrolle 7SR542 Transformer Differential Relay: Upgrade to Firmware v2.10 or later
# - Reyrolle 7SR571 Motor Protection Relay: Upgrade to Firmware v2.10 or later
2. Restrict Protocol Access at Substation Gateway
Ensure that substation firewalls block all incoming IEC 60870-5-103 (port 2404) and DNP3 (port 20000) packets originating outside the local substation Station Bus VLAN:
# Substation Firewall Access-List Rule
deny tcp any any eq 2404 log
deny tcp any any eq 20000 log
permit tcp 10.10.2.0/24 10.10.1.0/24 eq 2404
3. Implement Network Anomaly Detection for Substation Buses
Deploy passive OT network intrusion detection sensors (such as Zeek or Nozomi/Claroty) to monitor station bus traffic for malformed DNP3 or IEC 60870 APDUs before they reach relay interfaces.