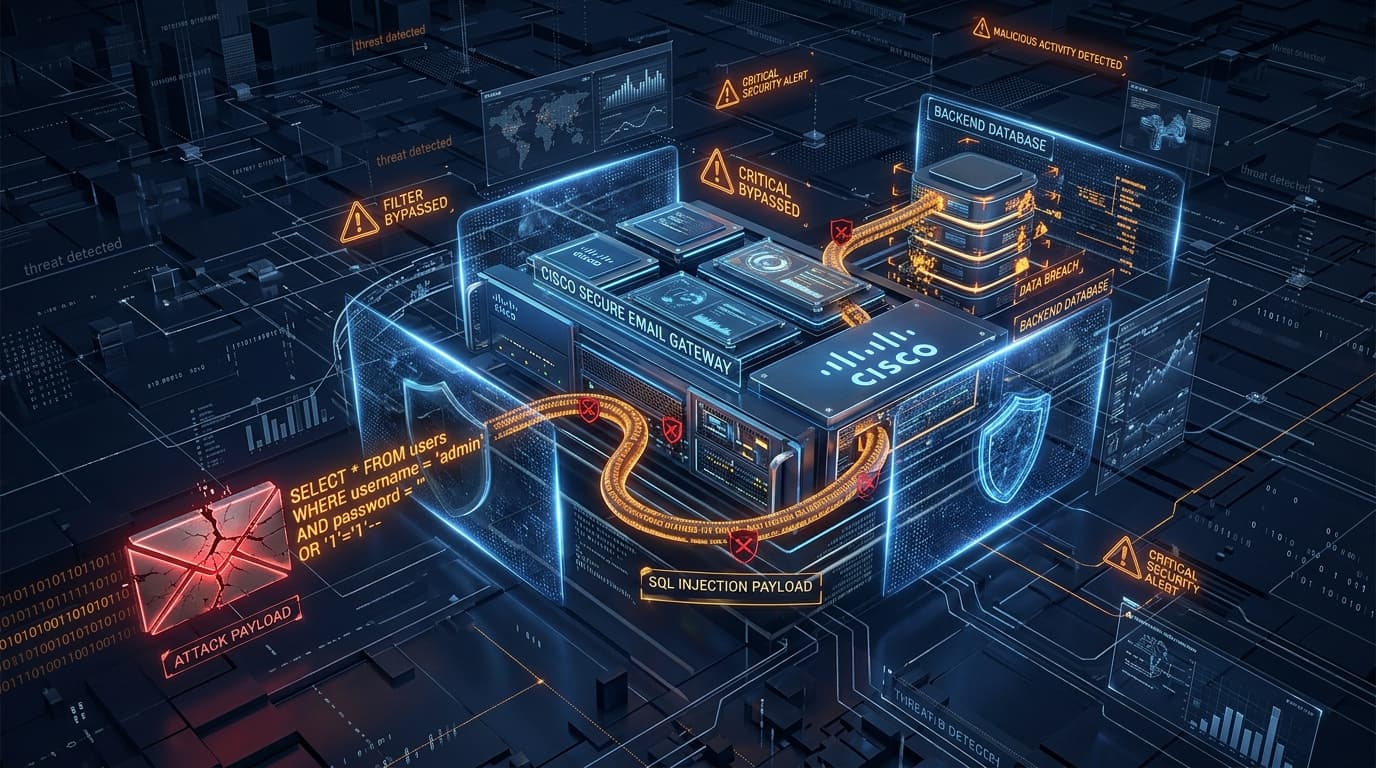
The Cybersecurity and Infrastructure Security Agency (CISA) has officially added CVE-2026-76461 to its Known Exploited Vulnerabilities (KEV) catalog. The critical security defect affects Cisco Secure Email Gateway (SEG) appliances—formerly marketed as Cisco Email Security Appliance (ESA)—running proprietary AsyncOS software.
With a maximum-severity CVSS v3.1 base score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H), the vulnerability allows unauthenticated, remote threat actors to execute arbitrary SQL commands on the backend database daemon, tamper with email quarantine databases, extract sensitive cryptographic keys, and break out into the underlying FreeBSD-based operating system with unrestricted root privileges.
Vulnerability Deep Dive: Input Sanitization Breakdown in AsyncOS Web Interface
According to vulnerability documentation published by Cisco Product Security Incident Response Team (PSIRT), the defect resides within the web-based administrative management console and reporting APIs of Cisco AsyncOS:
- Unauthenticated Parameter Submission: The appliance exposes an administrative web interface (typically running on TCP port 443 or custom management ports). An attacker transmits crafted HTTP requests with unescaped SQL escape sequences embedded within query parameters intended for quarantine search filters or message tracking lookups.
- Direct Query Concatenation: The backend AsyncOS daemon concatenates these unsanitized parameters directly into internal SQL queries executed by the appliance database engine without utilizing parameterized statements or rigorous type validation.
- Arbitrary File Write & System Execution: By leveraging SQL injection features (such as
ATTACH DATABASEor internal database stored procedures), an adversary writes arbitrary executable scripts to the web server root or triggers system commands under the context of the root management service.
Email security gateways sit at the perimeter of enterprise networks, decrypting and inspecting inbound and outbound communications. A root compromise of a perimeter email gateway grants adversaries the ability to inspect unencrypted email traffic, forge executive communications, and pivot into corporate Active Directory infrastructure.
Affected Hardware & AsyncOS Release Matrix
| Cisco Product / Platform | Vulnerable AsyncOS Releases | Remediated Maintenance Release | CISA Remediation Mandate |
|---|---|---|---|
| Cisco Secure Email Gateway (Physical C-Series) | AsyncOS 15.0, 15.5, and prior | AsyncOS 15.5.1-018 or later | Emergency Directive Action Required |
| Cisco Secure Email Virtual Gateway (vESA) | AsyncOS 15.0, 15.5, and prior | AsyncOS 15.5.1-018 or later | Emergency Directive Action Required |
| Cisco Secure Email Cloud Gateway (CES) | Cloud Infrastructure | Patched by Cisco Operations | Automated Cloud Rollout Complete |
Detection, Audit & Hardening Commands
Security operations centers and email engineering teams must immediately audit all on-premises and virtual Cisco SEG deployments using the following CLI procedures:
# Connect via SSH to the Cisco SEG appliance CLI
ssh admin@gateway.corp.internal

# Check currently installed AsyncOS version
version

# Inspect system logs for SQL syntax errors and unexpected statement termination
grep "syntax error" /data/logs/gui.log
grep -iE "UNION SELECT|ATTACH DATABASE|pg_exec" /data/logs/mail.log

# Verify that administrative web access is restricted to dedicated management VLANs
interfaceconfig
Recommended Enterprise Mitigation Checklist
- Apply AsyncOS Patch Immediately: Upgrade on-premises hardware and virtual appliances to AsyncOS 15.5.1-018 or higher directly through the Cisco Software Central portal.
- Disable Public Web Management Access: Under zero circumstances should the AsyncOS HTTP/HTTPS management portal (ports 80/443) be exposed to the public internet. Restrict management access strictly to dedicated out-of-band management subnets.
- Audit Quarantined Email Stores: Review mail quarantine release logs for unexpected modifications or bulk approvals that may indicate unauthorized tampering prior to patching.