Topic
Access Control: news, advisories and analysis
12 articles
CyberSecureToday covers Access Control across 12 articles published between 15 Sep 2026 and 24 Oct 2026. The coverage includes 12 vulnerability advisories. 12 advisories are rated critical or high severity, and 2 involve flaws listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on Access Control most often intersect with CWE-284, Privilege Escalation and Cloud Security, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Azure Enterprise Services Access Control Flaw Disclosed”, was published 24 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
 ThreatsBanking & FintechHigh
MariaDB DROP PACKAGE Defect Leaves Orphaned Grants in mysql.procs_priv Enabling Privilege Escalation
CST Editorial Desk ThreatsCloud & SaaSHigh
RubyGems Flaw in Gem Transfer Flow Allowed Organization Admins to Hijack Owner Rights and Evict Founders
Daniel Okafor ThreatsCloud & SaaSCritical
ProFTPD mod_copy Flaw Weaponized to Copy Server Files and Execute Code
CST Editorial Desk ThreatsCloud & SaaSHigh
AWS IAM Identity Center Flaw Left Revoked Session Tokens Active
CST Editorial Desk ThreatsCloud & SaaSCritical
AWS Identity and Access Management SCIM Endpoint Authentication Bypass Exposes Cloud Federation Roles
CST Editorial Desk ThreatsCloud & SaaSCritical
AWS IAM Identity Center Flaw Enables SCIM Bearer Token Bypass Across Enterprise Cloud Tenants
CST Editorial Desk ThreatsCloud & SaaSCritical
Internet2 Grouper Access Management Rule Engine Flaw Allows Unauthorized Privilege Escalation (CVE-2026-103470)
Priya Raman ThreatsCloud & SaaSHigh
Fortinet FortiSandbox Web Management Access Control Flaw Exposes Forensic Threat Telemetry (CVE-2026-26084)
Daniel Okafor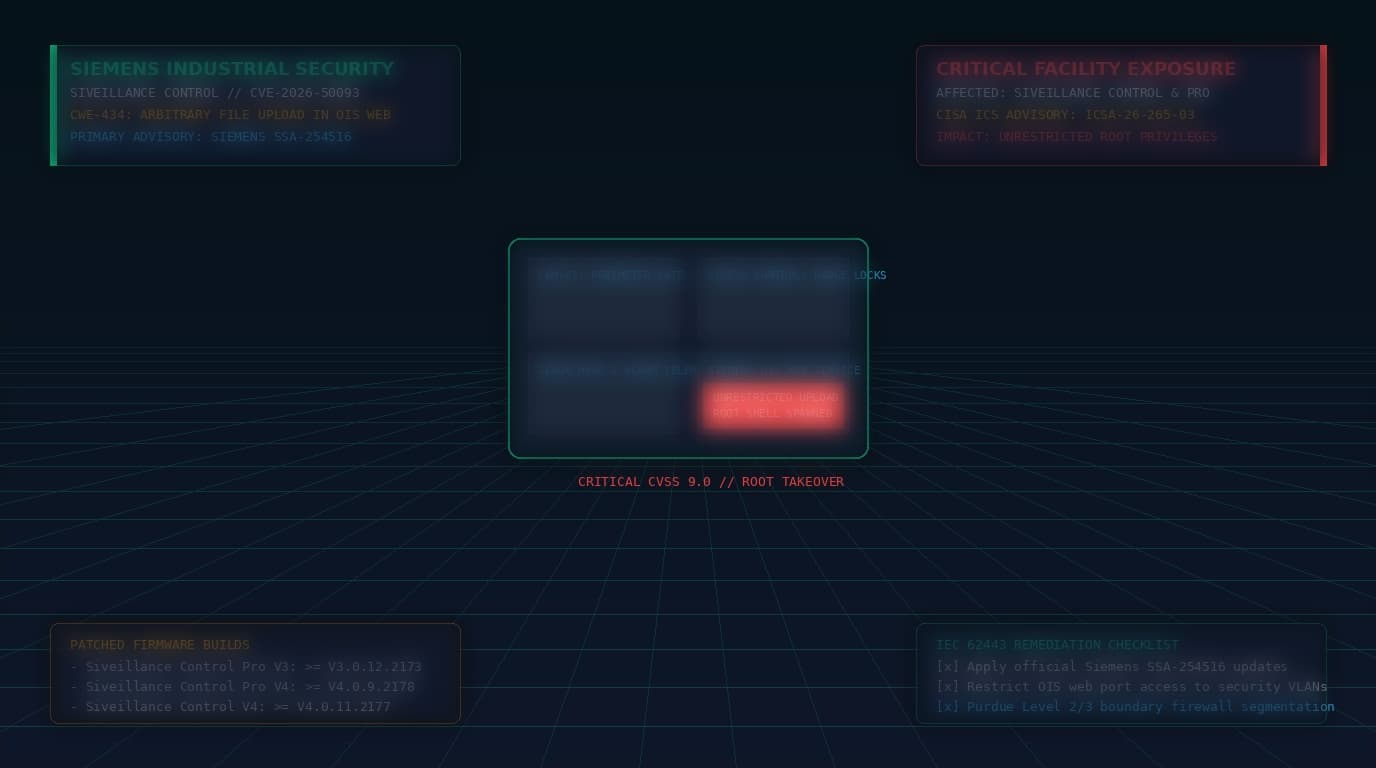 ThreatsIndustrial & OTCritical
Siemens Siveillance Control File Upload Flaw Grants Unauthenticated Root Access
CST Editorial Desk ThreatsIndustrial & OTCritical
Johnson Controls C-CURE 9000 Vulnerabilities Allow Attackers to Hijack Physical Facility Access Gateways
Mei-Lin Chen ThreatsCloud & SaaSCritical
Oracle WebLogic Server & Proxy Plug-in Flaw Exploited to Bypass Access Controls
Aisha Noor