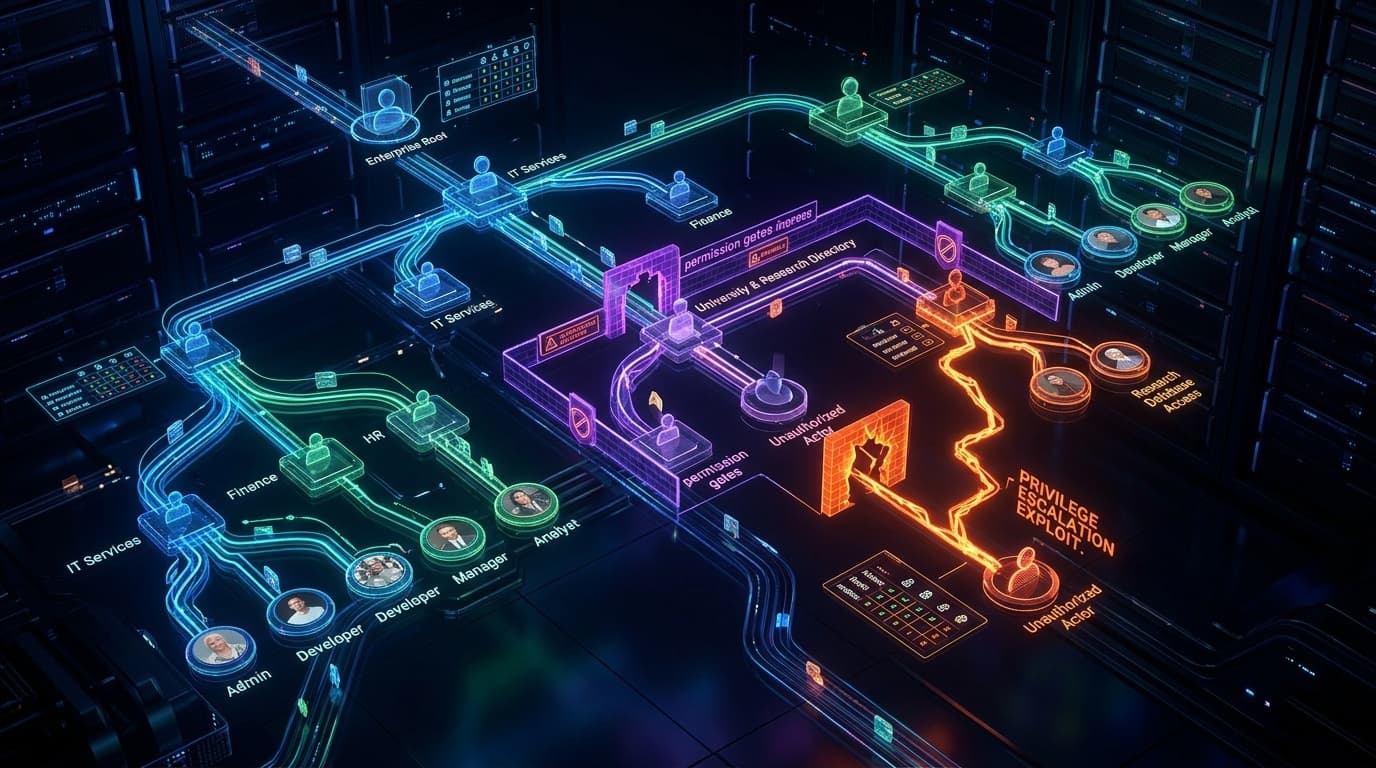
A critical privilege escalation vulnerability has been uncovered and patched in Internet2 Grouper, the enterprise identity management and access governance framework utilized extensively by national research institutions, higher education systems, and healthcare consortia worldwide. Assigned CVE-2026-103470 and published in GitHub Advisory GHSA-p48v-qg54-9c45, the security defect permits delegated users with localized rule-authoring permissions to escalate their privileges to root-level system administrators through Grouper's automated rule engine.
Grouper's Role in Federated Identity & Access Management (IAM)
Internet2 Grouper operates as the central source of truth for group access control, institutional entitlements, and attribute release in federated environments (such as InCommon and eduGAIN). By synchronizing directory groups with LDAP, Active Directory, Azure AD/Entra ID, and cloud service providers, Grouper automates access to high-performance computing (HPC) clusters, sensitive student/patient databases, and institutional financial portals.
To automate group lifecycle workflows, Grouper features a powerful declarative Rule Engine that executes actions (such as adding members or setting permissions) based on event triggers (such as folder events or attribute changes).
Vulnerability Mechanics: Defective Rule Scope Enforcement (CWE-269)
In Grouper configurations prior to version 7.5.1, departmental administrators or delegated group managers granted permissions to create rules within their own folder (stem) can configure rules whose action targets groups outside their authorized administrative scope:
// Vulnerable Rule Creation Workflow in Grouper UI
// Delegated User possesses rights only in: stem=colleges:engineering:cs

// Attacker creates a rule triggered by a harmless event in their own folder:
ruleDefinition: {
    ruleCheckType: "membershipAdd",
    ruleCheckOwnerStem: "colleges:engineering:cs:student_group",
    // FATAL FLAW: Rule Action was NOT bounded by the user's stem permissions!
    ruleActionType: "assignGroupMembership",
    ruleActionTargetGroup: "etc:sysadmin:grouperSysAdmin", // Target: Global Superadmin
    ruleActionTargetSubject: "attacker_subject_id"
}
When the rule condition fires (e.g., adding a test subject to the local group), the background Grouper Daemon (grouperLoader) processes the rule under the internal system security context (GrouperSystem). Because the rule engine assumes the rule definition was verified during creation, the background worker unhesitatingly grants the attacker membership in etc:sysadmin:grouperSysAdmin.
Privilege Escalation Blast Radius
| Permission State | Pre-Exploitation Scope | Post-Exploitation Capabilities |
|---|---|---|
| Delegated Group Admin | Restricted to departmental stem (e.g., cs:students) |
Inherited global grouperSysAdmin privileges |
| Federated Directory Sync | Read-only directory visibility | Push unauthorized memberships into Active Directory / Azure AD |
| Supercomputing & HPC Access | No shell access to national research clusters | Arbitrary entitlement assignment to Slurm / PBS HPC clusters |
Remediation & Defense Actions
- Upgrade to Grouper 7.5.1+: Deploy the latest maintenance release immediately. Version 7.5.1 introduces strict validation during rule submission, ensuring users can only target groups and attributes where they hold full administrative rights.
- Audit Existing Grouper Rules: Execute the administrative audit query to detect unauthorized rules targeting privileged system stems:
gsh -runscript -e "new RuleFinder().assignRuleCheckType(RuleCheckType.membershipAdd).findRules().each { println it.toString() }" - Restrict UI Rule Configuration: In
grouper.properties, limit rule editing privileges strictly to the central IAM security team:grouper.rules.enableUiRuleEditing = false