The Microsoft Security Response Center (MSRC) has published guidance on a critical identity platform vulnerability tracked as CVE-2026-50481 (CVSS score 9.9) in Microsoft Entra ID (formerly Azure Active Directory). The vulnerability allows authenticated network actors to modify directory attributes previously assumed immutable, enabling vertical privilege escalation to Global Administrator across cloud estates.
Executive Threat Overview: Cloud Identity Trust Boundary Compromise
Microsoft Entra ID is the central authentication and authorization plane for Microsoft 365, Azure, Intune, and thousands of federated enterprise SaaS integrations. Over 700 million daily active identity assertions depend on Entra ID directory claims to enforce Conditional Access policies, role-based access control (RBAC), and privileged role activations.
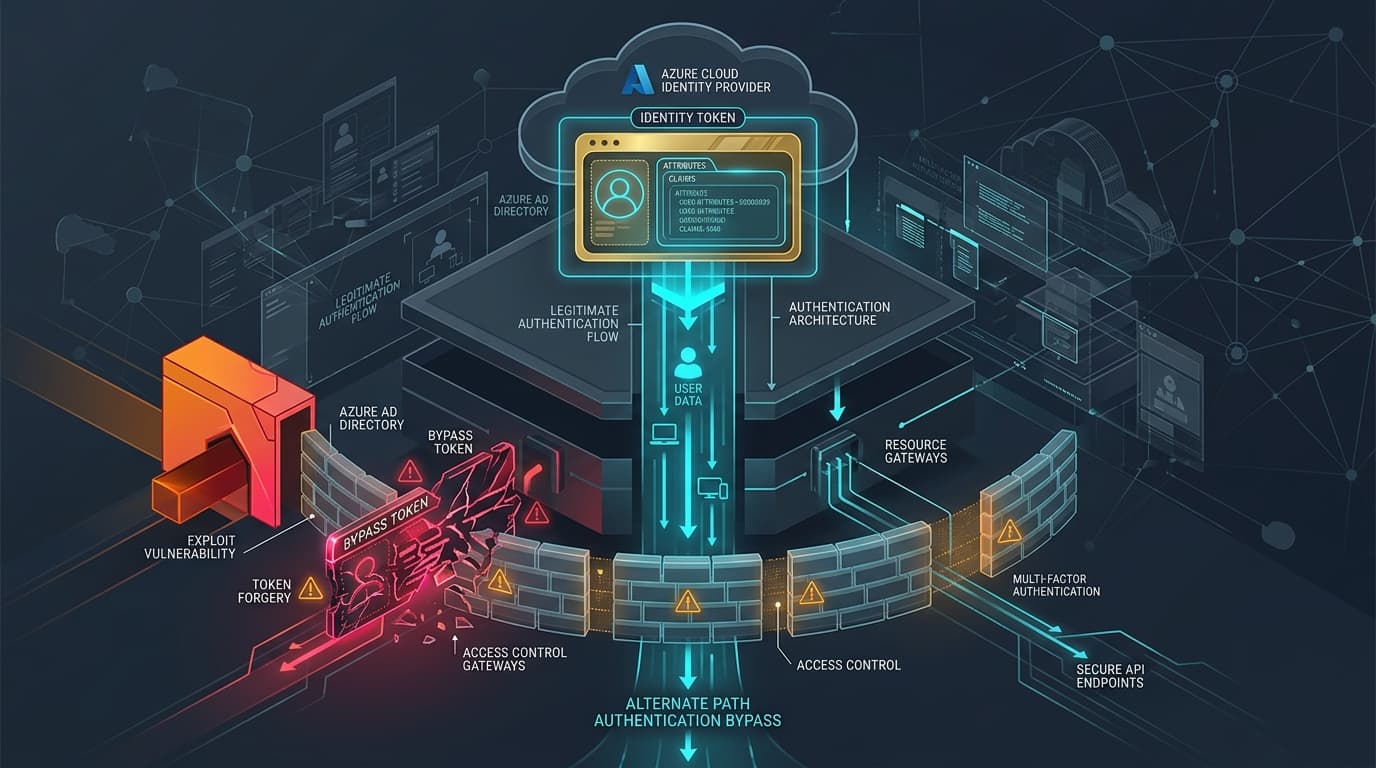
The defect, categorized under CWE-472 (Modification of Assumed-Immutable Data), represents an architectural breakdown in how Entra ID's internal microservices evaluated claim signatures during multi-tenant token exchanges. When standard users invoked specific graph manipulation subroutines, immutable tenant boundary claims could be forged or overwritten in memory, granting unconstrained directory control.
Technical Deep-Dive: The MAID Vulnerability Vector
In cloud identity architectures, directory objects contain both mutable properties (such as display names or job titles) and system-enforced immutable properties (such as tenantId, userPrincipalName, altSecId, and wids role identifier claims). Internal identity microservices rely on the assumption that client requests cannot alter immutable attributes once an identity is provisioned.
Security research revealed that during federated authentication flows involving multi-factor registration endpoints, a race condition and claim normalization flaw allowed an authenticated principal to supply override properties within nested JSON request envelopes:
# Architectural representation of immutable claim override
POST /v1.0/users/{user-id}/authentication/methods HTTP/1.1
Host: graph.microsoft.com
Authorization: Bearer eyJhbGciOiJSUzI1NiIs...

{
  "extensionAttribute": {
    "targetProperty": "wids",
    "overrideValue": ["62e90394-69f5-4237-9190-012177145e10"], # Global Administrator Role Template ID
    "enforceImmutable": false
  }
}
The backend parsing engine in affected revisions failed to sanitize the internal attribute dictionary before re-serializing the authentication artifact. When the user subsequently requested a refreshed OAuth token, the identity provider incorporated the forged wids claim into the signed JWT token, granting the actor instantaneous Global Administrator privileges over the entire Azure/Entra ID tenant.
Blast Radius & Post-Compromise Scenarios
An adversary exploiting CVE-2026-50481 could execute severe downstream intrusions:
- Full Cloud Estate Takeover: Generate new Global Admin credentials, modify Conditional Access rules to bypass MFA, and export BitLocker encryption keys from Intune.
- SaaS Supply Chain Hijacking: Grant administrative consent to rogue multi-tenant Entra applications, establishing persistent access to enterprise Exchange Online mailboxes and SharePoint sites.
- Azure Infrastructure Pivoting: Elevate access to Azure subscription root management groups, executing arbitrary commands across running virtual machines and serverless functions.
Vulnerability Profile & Impact Matrix
| Characteristic | Vulnerability Specification |
|---|---|
| Tracking Identifier | CVE-2026-50481 |
| Common Weakness | CWE-472: Modification of Assumed-Immutable Data (MAID) |
| CVSS v3.1 Vector | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H (Score: 9.9 Critical) |
| Affected Service | Microsoft Entra ID (Azure Active Directory) Directory Services |
| Remediation Method | Server-side patch deployed by Microsoft to global cloud identity clusters |
| Customer Action Required | Audit Entra ID audit logs for anomalous role assignments & service principals |
Defensive Playbook: Enterprise Identity Audit Roadmap
While Microsoft has neutralized the root attribute override vulnerability in the cloud control plane, enterprise security operations teams must perform retroactive forensics:
1. Audit Directory Role Assignments in Log Analytics
Query Entra ID Audit Logs for any role assignment additions, particularly Global Administrator or Privileged Role Administrator assignments originating from non-PIM workflows:
# KQL: Query Entra Audit Logs for suspicious role elevations
AuditLogs
| where TimeGenerated > ago(30d)
| where OperationName == "Add member to role"
| extend TargetRole = tostring(TargetResources[0].displayName)
| extend Initiator = tostring(InitiatedBy.user.userPrincipalName)
| where TargetRole in ("Global Administrator", "Privileged Role Administrator", "Security Administrator")
| project TimeGenerated, Initiator, TargetRole, ActivityDisplayName, Result
2. Inspect Third-Party OAuth App Consents
Review all enterprise applications granted high-privilege permissions (Directory.ReadWrite.All, RoleManagement.ReadWrite.Directory) to ensure no stealth backdoors were established:
# PowerShell: Audit high-risk service principals in Microsoft Graph
Get-MgServicePrincipal -Filter "appOwnerOrganizationId ne null" | Where-Object {
    $_.OAuth2PermissionGrants.Scope -match "Directory.ReadWrite.All"
} | Select-Object DisplayName, AppId, ServicePrincipalType
3. Enforce Strict Privileged Identity Management (PIM)
Ensure all administrative roles require just-in-time (JIT) activation with mandatory peer approval and FIDO2 hardware token step-up verification.