Topic
CWE-22: news, advisories and analysis
9 articles
CyberSecureToday covers CWE-22 across 9 articles published between 17 Sep 2026 and 14 Oct 2026. The coverage includes 9 vulnerability advisories. 9 advisories are rated critical or high severity, and 3 involve flaws listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on CWE-22 most often intersect with Path Traversal, Remote Code Execution and Zero-Day, with Technology, Cloud & SaaS the most affected sector. The most recent story, “ONLYOFFICE Document Server Path Traversal Flaw Enables Remote Code Execution”, was published 14 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsCloud & SaaSCriticalCST Editorial Desk
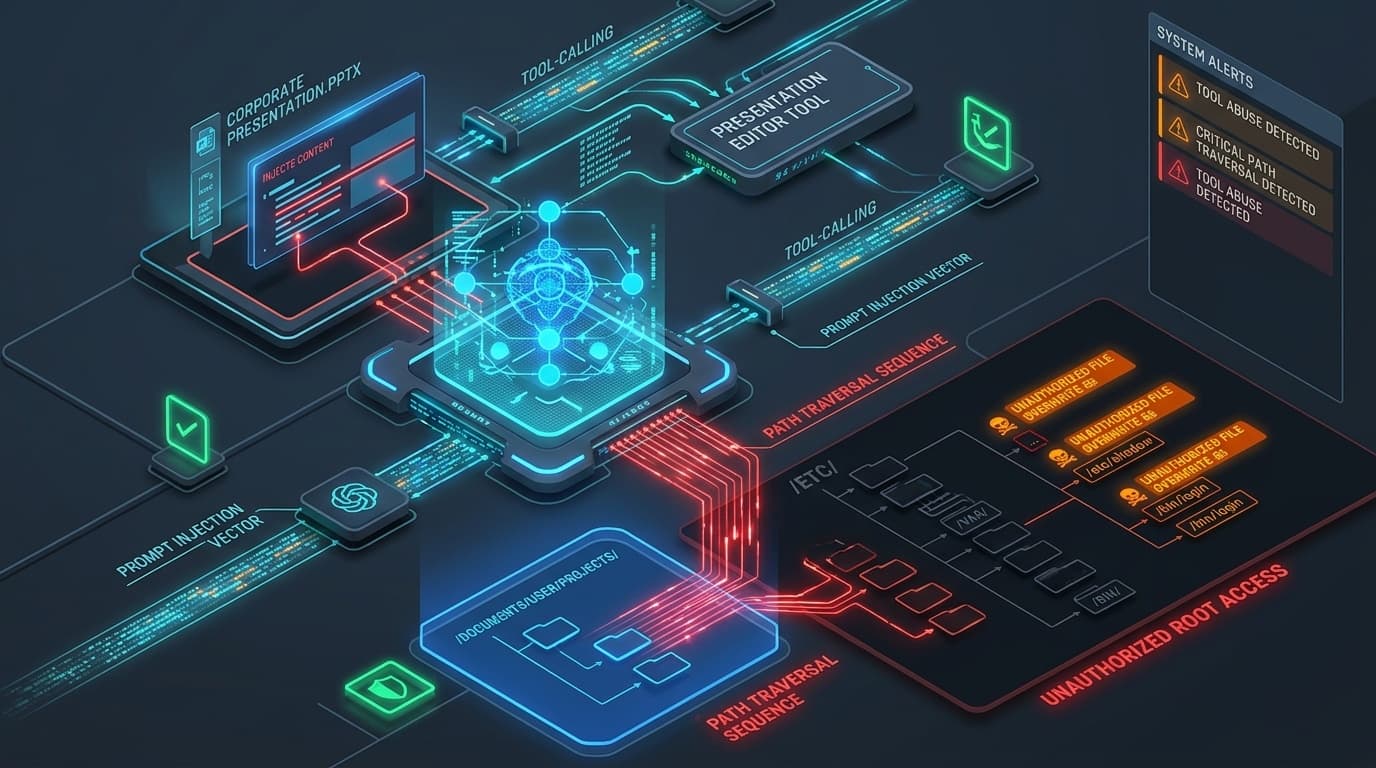
ThreatsCloud & SaaSHighOffice PowerPoint MCP Server Path Traversal Enables Indirect Prompt Injection File Overwrite (CVE-2025-71427)
Priya Raman
ThreatsCloud & SaaSCriticalFortinet FortiMail Path Traversal Flaw Exploited for Unauthenticated Remote Code Execution
Priya Raman
ThreatsCloud & SaaSHighLangChain Core Prompt Template Ingestion Flaw Exposes Host Systems to Path Traversal CVE-2026-34070
Daniel Okafor
ThreatsCloud & SaaSCriticalDify Cross-Tenant Path Traversal Flaw Exposes Internal Plugin APIs to Unauthorized Access
Priya Raman
ThreatsCloud & SaaSCriticalWSO2 API Manager Path Traversal Flaw Weaponized to Extract Gateway Credentials
Daniel Okafor
ThreatsCloud & SaaSCriticalCheck Point Security Management Server Path Traversal Exploited to Gain Root Access
CST Editorial Desk
ThreatsCloud & SaaSHighORAS-Go Symlink Path Traversal Flaw Opens OCI Artifact Supply Chain to Compromise
CST Editorial Desk
ThreatsCloud & SaaSCriticalAdobe ColdFusion Critical Path Traversal Flaw CVE-2026-48282 Exploited in Active Attacks
Mei-Lin Chen