Topic
LLM Security: news, advisories and analysis
23 articles
CyberSecureToday covers LLM Security across 23 articles published between 10 Sep 2026 and 12 Oct 2026. The coverage includes 17 vulnerability advisories and 6 analysis or guidance pieces. 17 advisories are rated critical or high severity, and 1 involves a flaw listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on LLM Security most often intersect with AI Security, Agentic AI and Prompt Injection, with Technology, Cloud & SaaS the most affected sector. The most recent story, “LangChain LCEL Vector Index Deserialization Flaw Enables Arbitrary Code Execution via Compromised Embeddings (CVE-2026-74120)”, was published 12 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsCloud & SaaSCriticalCST Editorial Desk
ThreatsCloud & SaaSCriticalAWS Bedrock Agent Runtime Flaw Enabled Persistent Jailbreaks and Tool Hijacking
CST Editorial Desk
ThreatsCloud & SaaSCriticalLiteLLM Gateway SQL Injection Vulnerability in Vector Search Metadata Filter Allows Backend Database Takeover
CST Editorial Desk
ThreatsCloud & SaaSCriticalLiteLLM AI Model Gateway Vulnerability Allows Unauthenticated JWT Signature Bypass and Private LLM Hijacking (CVE-2026-55102)
Aisha Noor
ThreatsCloud & SaaSHighOllama Patches Experimental Agent Mode Command Injection and Approval Bypass Flaw (CVE-2026-102697)
Aisha Noor
ThreatsCloud & SaaSCriticalMooncake Distributed LLM KVCache Transfer Engine Vulnerable to Process Memory Disclosure and RCE (CVE-2026-103764)
CST Editorial Desk
ThreatsCloud & SaaSCriticalGitLab AI Gateway Prompt Execution Flaw Exposes Cloud Workspaces to Remote Code Execution (CVE-2026-90970)
CST Editorial Desk
ThreatsCloud & SaaSHighLangChain Core Prompt Template Ingestion Flaw Exposes Host Systems to Path Traversal CVE-2026-34070
Daniel Okafor
ThreatsCloud & SaaSCriticalLangflow Shareable Playground Flaw Enables Unauthenticated Remote Code Execution
Mei-Lin Chen
ThreatsCloud & SaaSHighOllama GGUF Parser Integer Overflow Exposes AI Inference Servers to Memory Corruption
Priya Raman
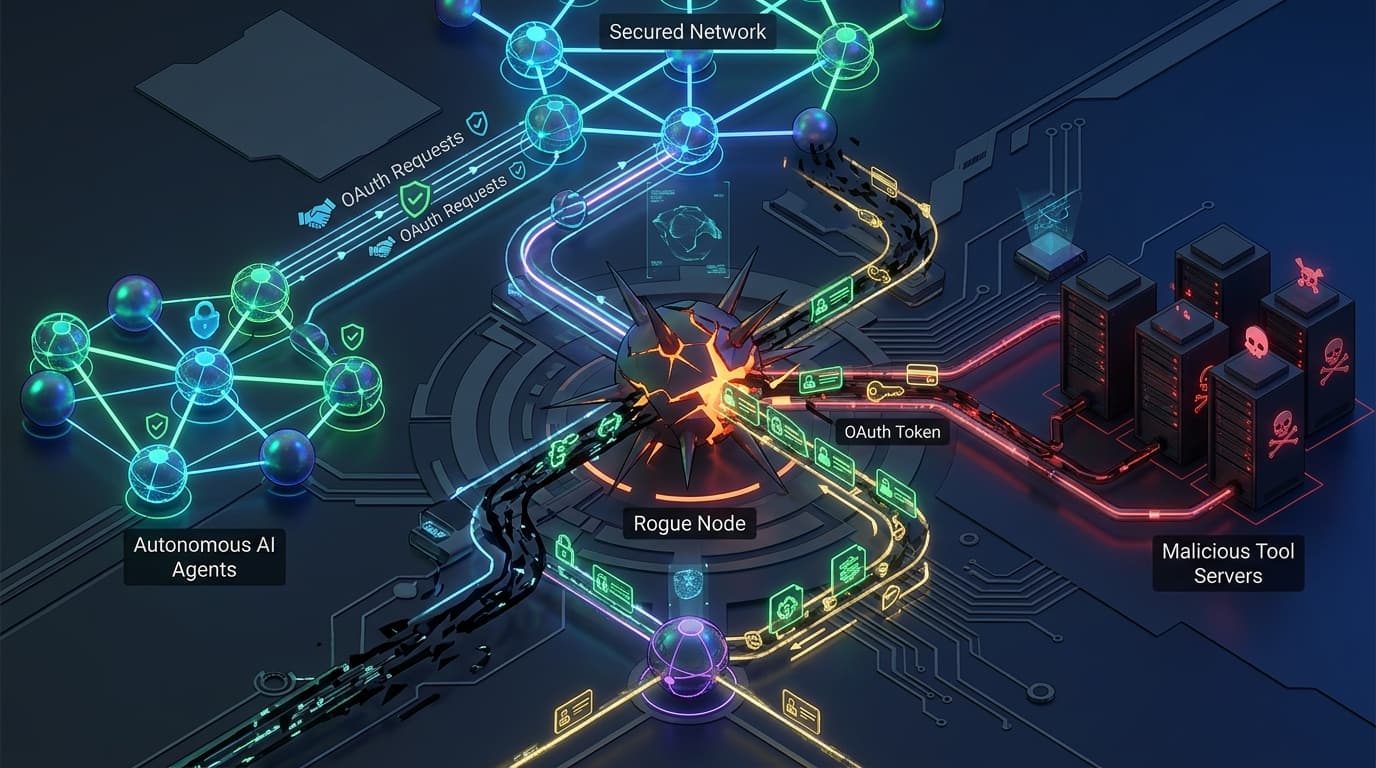
InsightsCloud & SaaSModel Context Protocol OAuth Passthrough Flaw Exposes Autonomous AI Tool Pipelines to Silent Impersonation
Priya Raman
ThreatsCloud & SaaSCriticalAzure AI Language Authentication Flaw Enables Unauthenticated Model Tampering
CST Editorial Desk
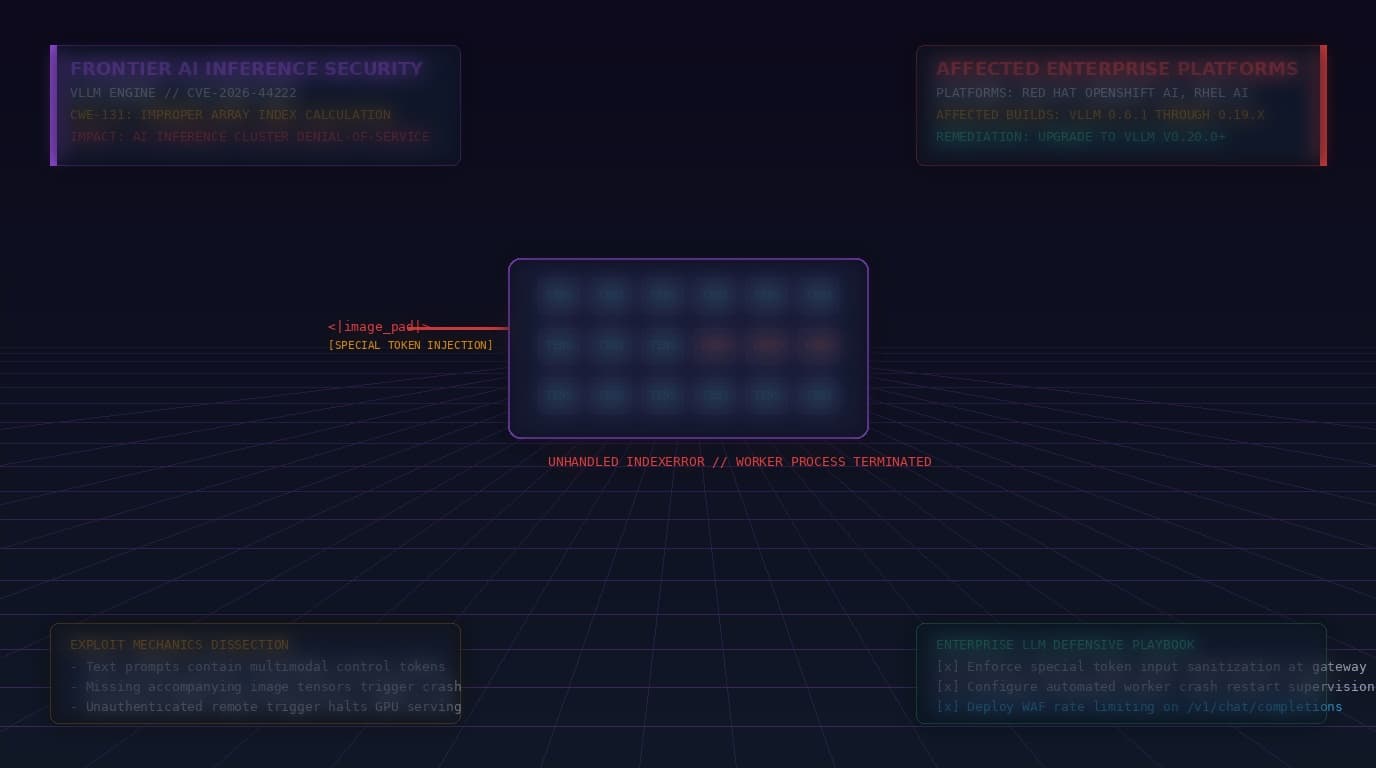
ResearchCloud & SaaSvLLM Multimodal Special Token Injection Triggers Remote Engine Crash and Service Denial CVE-2026-44222
CST Editorial Desk
ThreatsCloud & SaaSHighStrands Agents Tools HTTP Request Authorization Flaw Enables Indirect Prompt Injection Credential Theft CVE-2026-18394
CST Editorial Desk
ThreatsCloud & SaaSHighCrewAI Multi-Agent Framework Flaw CVE-2026-37007 Allows Remote Code Execution via Path Traversal Tool Poisoning
Mei-Lin Chen
InsightsCloud & SaaSMalicious MCP Servers Exploit OAuth Metadata Flaw in Rust SDK to Hijack Enterprise Agent Tokens
Priya Raman
ThreatsCloud & SaaSHighFlowise SSRF Vulnerability Bypasses Network Guardrails to Steal Cloud Instance Credentials
Daniel Okafor
ThreatsCloud & SaaSHighAmazon Bedrock AgentCore Flaw Allows Attackers to Bypass LLM Guardrails via Injected Tool-Use Payloads
Daniel Okafor
ResearchCloud & SaaSLangflow AI Pipeline Remote Code Execution Flaws Exploited in Enterprise LLM Deployments
Aisha Noor
ResearchCloud & SaaSAgentic AI Security Breakdown: How Indirect Prompt Injections Hijack Autonomous Tool-Calling Agents
Priya Raman
ThreatsCloud & SaaSCriticalIBM Langflow Visual AI Framework Remote Code Injection Vulnerability CVE-2026-9198 Exploited in Production Environments
Daniel Okafor