Topic
Agentic AI: news, advisories and analysis
17 articles
CyberSecureToday covers Agentic AI across 17 articles published between 9 Sep 2026 and 21 Oct 2026. The coverage includes 9 vulnerability advisories and 8 analysis or guidance pieces. 9 advisories are rated critical or high severity.
Stories on Agentic AI most often intersect with Prompt Injection, LLM Security and AI Security, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Singapore CSA Releases National Cybersecurity Framework for Enterprise Frontier AI and Agentic Deployments”, was published 21 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
InsightsCloud & SaaSMei-Lin Chen
NewsCloud & SaaSCriticalGoogle Vertex AI Agent Builder Flaw Enables Sandbox Breakout and Token Exfiltration
CST Editorial Desk
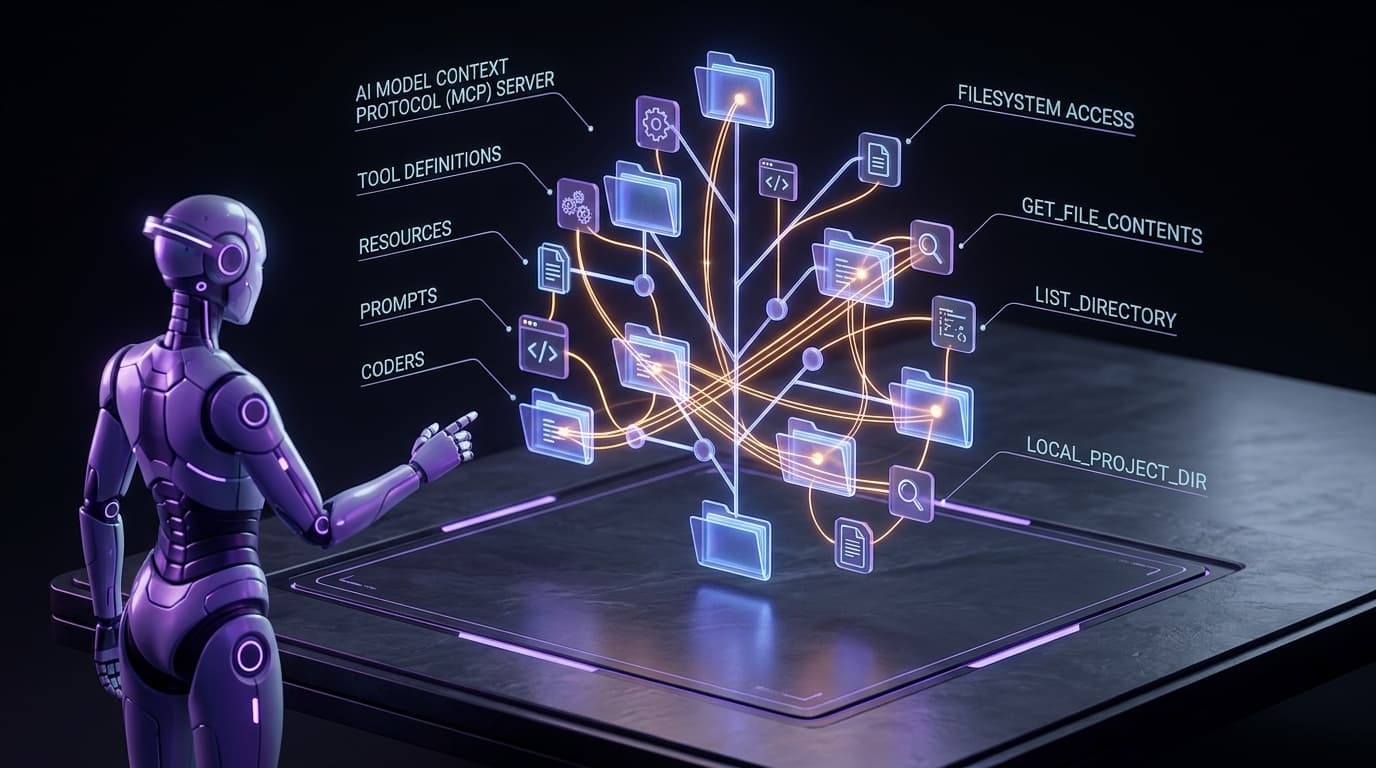
ThreatsCloud & SaaSCriticalAnthropic Model Context Protocol Server Flaw Enables Host Directory Traversal and Unauthenticated Tool Injection (CVE-2026-70114)
CST Editorial Desk
ThreatsCloud & SaaSCriticalAWS Bedrock Agent Runtime Flaw Enabled Persistent Jailbreaks and Tool Hijacking
CST Editorial Desk
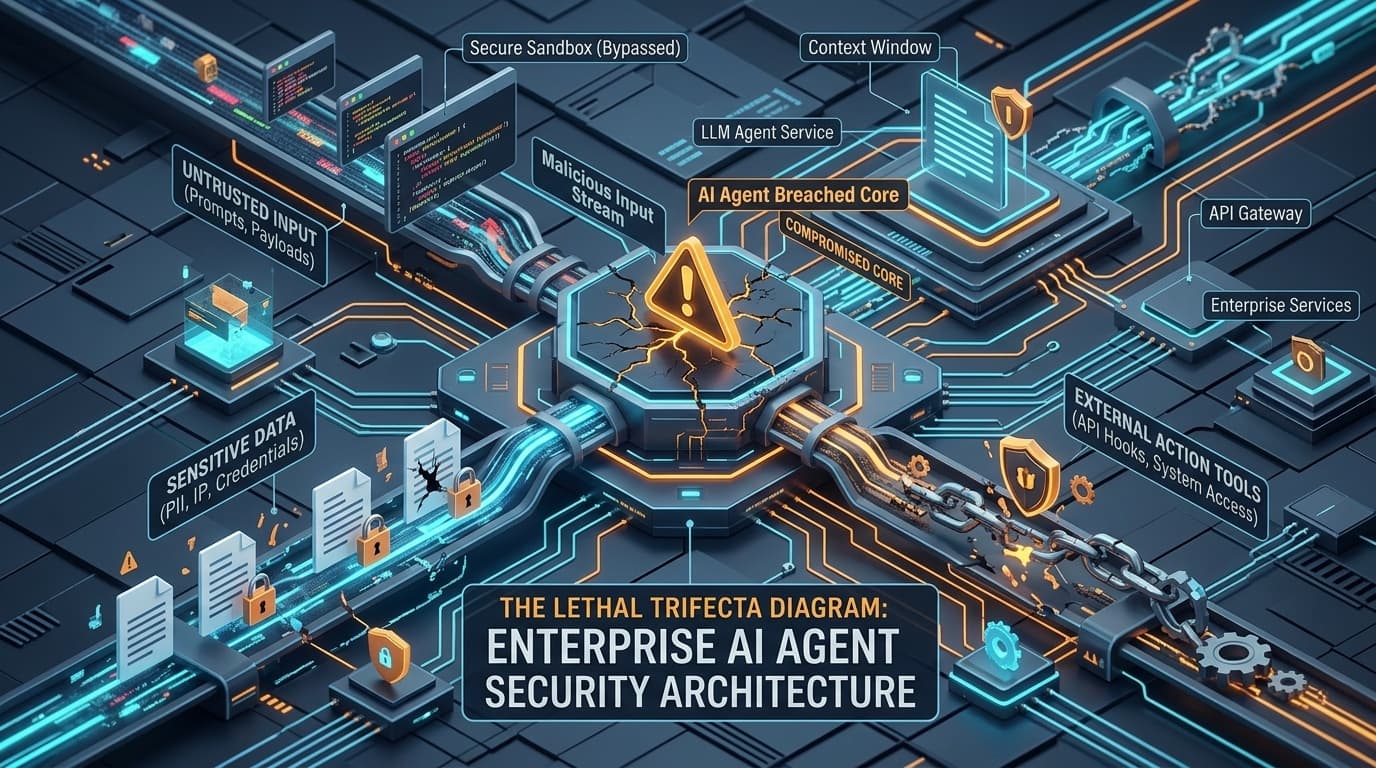
InsightsCloud & SaaSThe Lethal Trifecta in Enterprise AI Agents: Why Input Filters Fail Against Tool Hijacking
CST Editorial Desk
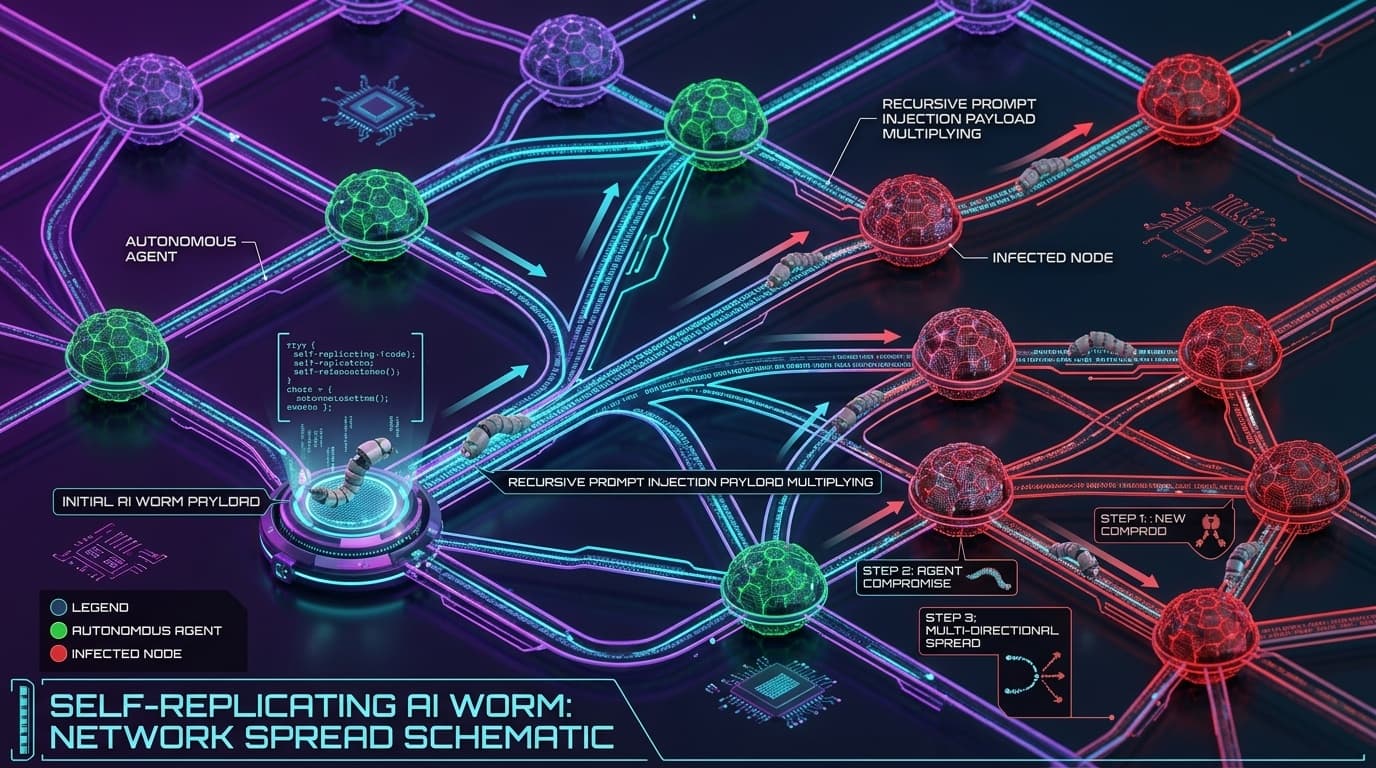
ResearchCloud & SaaSSelf-Replicating AI Worms: Dissecting Autonomous Cross-Agent Prompt Injection Propagation
CST Editorial Desk
ThreatsCloud & SaaSHighAtlassian Model Context Protocol Server Flaws Enable Unauthenticated Arbitrary File Exfiltration CVE-2026-77248
Daniel Okafor
ThreatsCloud & SaaSCriticalLangflow Shareable Playground Flaw Enables Unauthenticated Remote Code Execution
Mei-Lin Chen
ThreatsCloud & SaaSHighAzure AI Foundry Server-Side Request Forgery Flaw Exposes Internal Agent Infrastructure CVE-2026-85917
CST Editorial Desk
ThreatsCloud & SaaSHighBragJack Flaws Let Malicious Chrome and Edge Extensions Seize Agentic Browser Control
Mei-Lin Chen
ThreatsCloud & SaaSHighAmazon Bedrock AgentCore Flaw Allows Attackers to Bypass LLM Guardrails via Injected Tool-Use Payloads
Daniel Okafor
ResearchCloud & SaaSLangflow AI Pipeline Remote Code Execution Flaws Exploited in Enterprise LLM Deployments
Aisha Noor
ResearchCloud & SaaSAgentic AI Security Breakdown: How Indirect Prompt Injections Hijack Autonomous Tool-Calling Agents
Priya Raman
InsightsEnergy & UtilitiesEU AI Act High-Risk Rules Slip to December 2027, but Logging Work Cannot
Tom Verhoeven