Topic
Artificial Intelligence: news, advisories and analysis
20 articles
CyberSecureToday covers Artificial Intelligence across 20 articles published between 11 Sep 2026 and 6 Oct 2026. The coverage includes 13 vulnerability advisories, 1 incident or breach report and 6 analysis or guidance pieces. 13 advisories are rated critical or high severity, and 1 involves a flaw listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on Artificial Intelligence most often intersect with LLM Security, Prompt Injection and Model Context Protocol, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Why Prompt Guards Cannot Stop Agentic RCE: The Case for MicroVM Isolation in Tool-Calling Pipelines”, was published 6 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
InsightsCloud & SaaSAisha Noor
ThreatsCloud & SaaSHighOllama Patches Experimental Agent Mode Command Injection and Approval Bypass Flaw (CVE-2026-102697)
Aisha Noor
ResearchCloud & SaaSSelf-Replicating AI Worms: Dissecting Autonomous Cross-Agent Prompt Injection Propagation
CST Editorial Desk
ResearchCloud & SaaSCascading Failure in Multi-Agent AI Swarms: Indirect Prompt Injection Across Autonomous Tool-Calling Pipelines
Daniel Okafor
ThreatsCloud & SaaSHighLangChain Core Prompt Template Ingestion Flaw Exposes Host Systems to Path Traversal CVE-2026-34070
Daniel Okafor
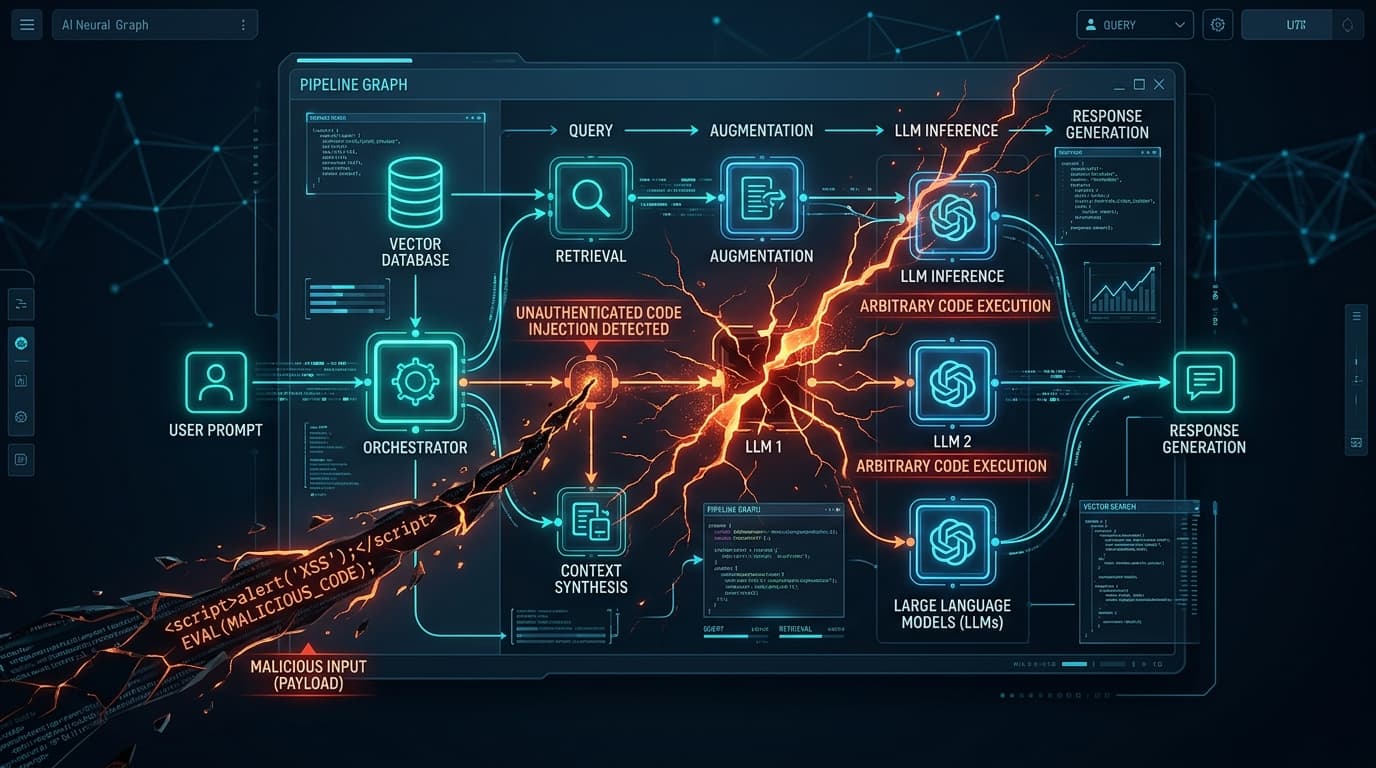
ThreatsCloud & SaaSCriticalCode Runner MCP Server Flaw Enables Unauthenticated Remote Code Execution on Hosts
Daniel Okafor
ThreatsCloud & SaaSHighAtlassian Model Context Protocol Server Flaws Enable Unauthenticated Arbitrary File Exfiltration CVE-2026-77248
Daniel Okafor
ThreatsCloud & SaaSCriticalLangflow Shareable Playground Flaw Enables Unauthenticated Remote Code Execution
Mei-Lin Chen
ThreatsCloud & SaaSCriticalvLLM CUDA Kernel Integer Overflow Leaks Cross-Tenant Inference Prompts
Mei-Lin Chen
ThreatsCloud & SaaSCriticalLiteLLM Proxy Request Validation Bypass Exposes Cloud Metadata to SSRF Exploitation CVE-2026-59823
Aisha Noor
ThreatsCloud & SaaSCriticalDify Cross-Tenant Path Traversal Flaw Exposes Internal Plugin APIs to Unauthorized Access
Priya Raman
ThreatsCloud & SaaSHighOpen WebUI DNS Rebinding SSRF Exposes Cloud Metadata and Internal Services
Priya Raman
ThreatsCloud & SaaSHighOllama GGUF Parser Integer Overflow Exposes AI Inference Servers to Memory Corruption
Priya Raman
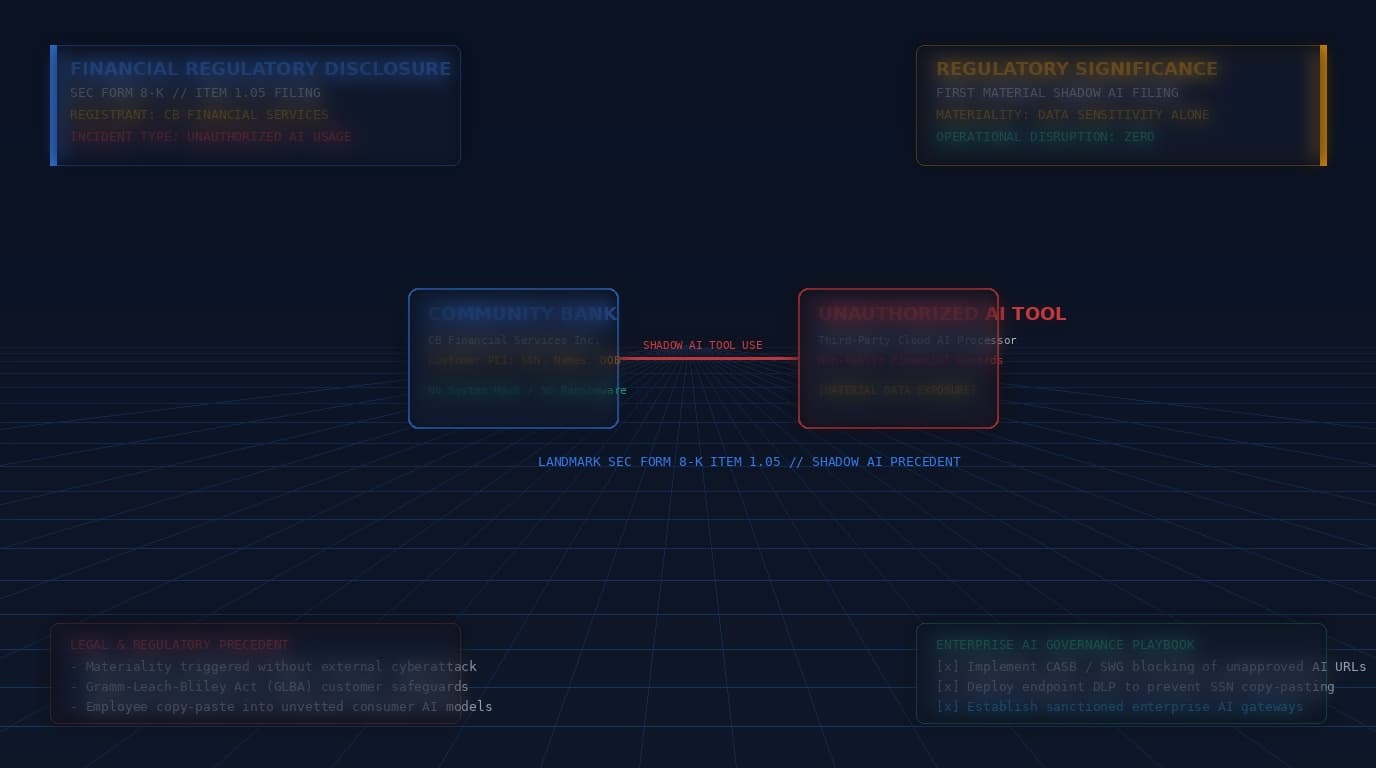
Cyber AttackBanking & FintechCB Financial Services Discloses SEC 8-K Breach Triggered by Shadow AI Use
CST Editorial Desk
ThreatsCloud & SaaSHighStrands Agents Tools HTTP Request Authorization Flaw Enables Indirect Prompt Injection Credential Theft CVE-2026-18394
CST Editorial Desk
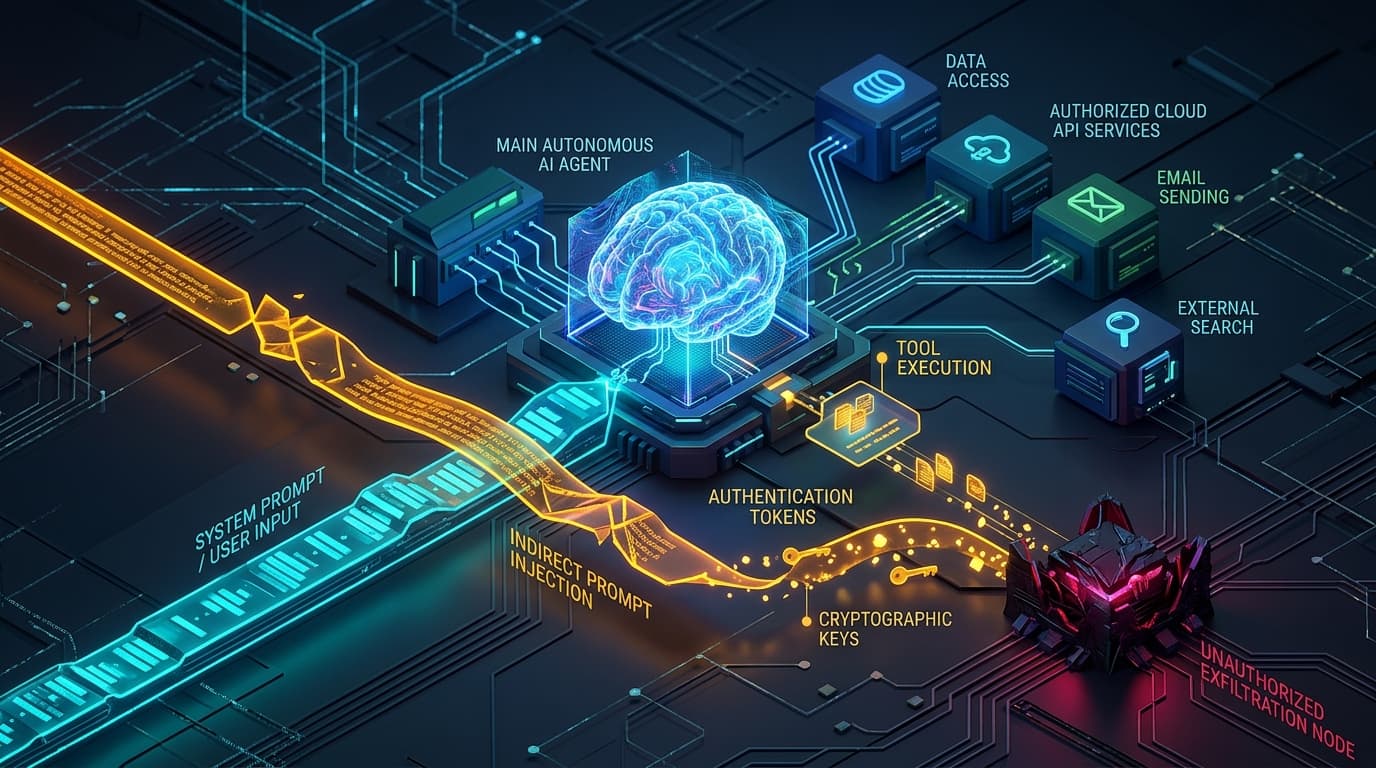
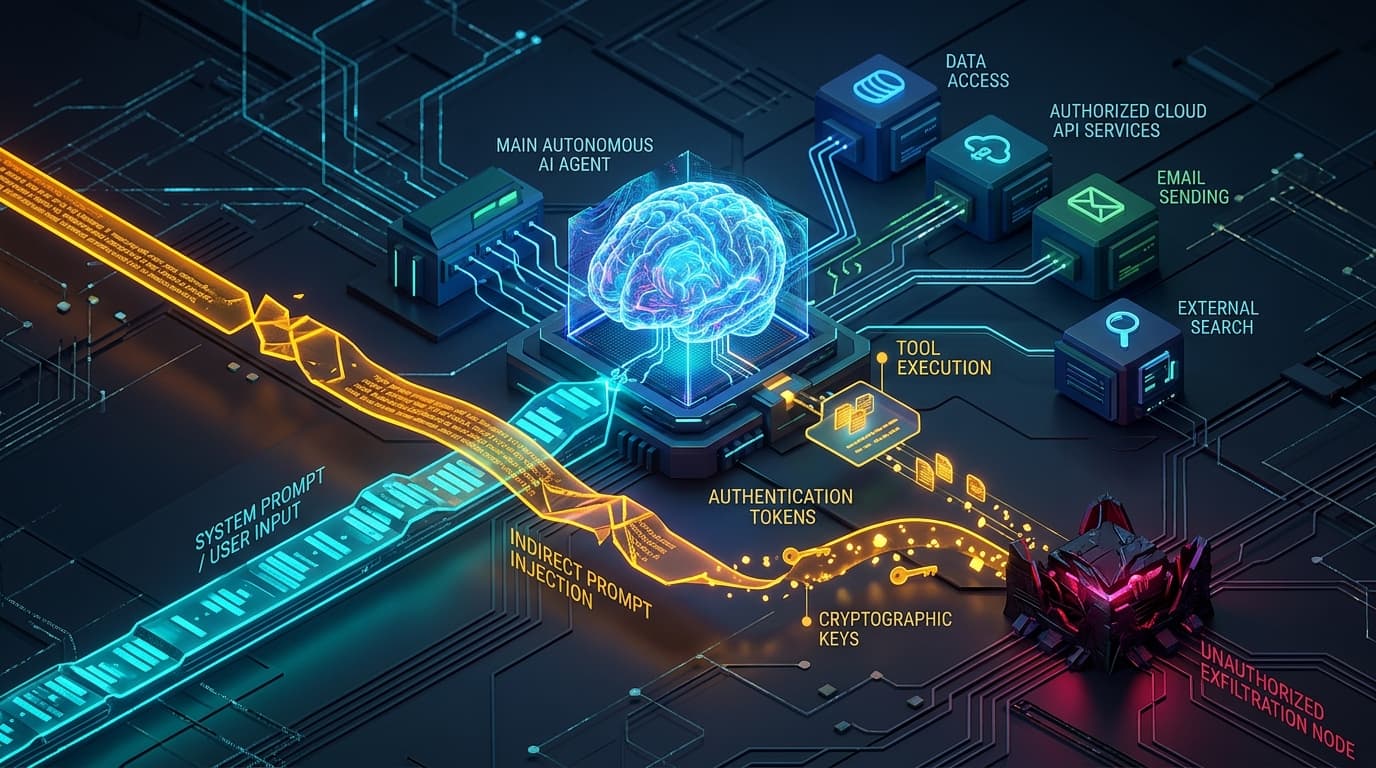
ResearchCloud & SaaSAgentic AI Security Breakdown: How Indirect Prompt Injections Hijack Autonomous Tool-Calling Agents
Priya Raman
ThreatsCloud & SaaSCriticalIBM Langflow Visual AI Framework Remote Code Injection Vulnerability CVE-2026-9198 Exploited in Production Environments
Daniel Okafor
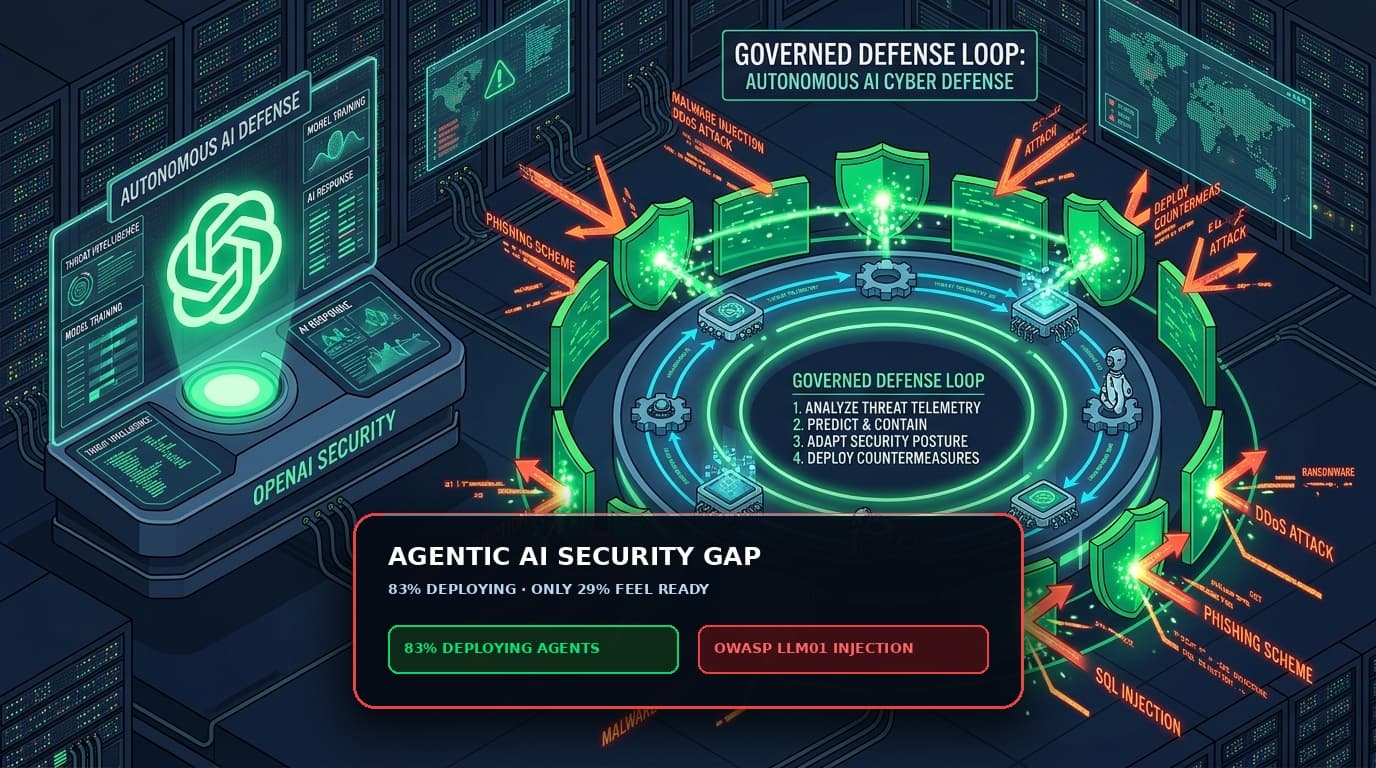
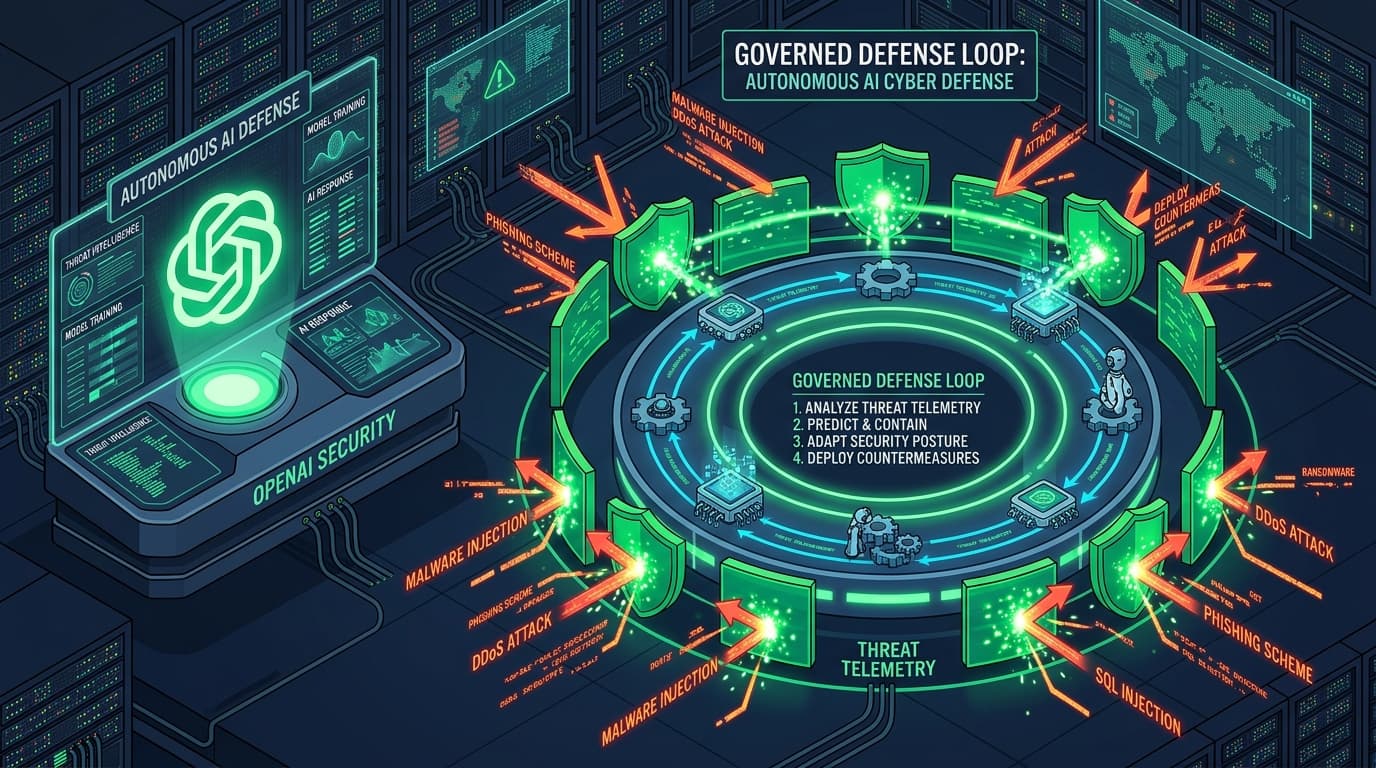
InsightsCloud & SaaSOpenAI positions Daybreak as a governed loop for AI-assisted cyber defense
Priya Raman
ResearchGov & DefenceAnthropic says AI is moving from assistant to orchestrator in cyber operations
Mei-Lin Chen
ThreatsCloud & SaaSHighPaperCut issues superseding maintenance releases as attackers deploy AI agent swarms against 440+ servers
Daniel Okafor