Executive Overview
Amazon Web Services (AWS) has published a critical security advisory addressing CVE-2026-68115, an unauthenticated deserialization and state-tampering vulnerability within the Amazon Bedrock Agent Runtime. The flaw, assigned a CVSS v3.1 base score of 9.9 (Critical), allows adversarial inputs to compromise the shared context memory store utilized during multi-agent collaborative workflows.
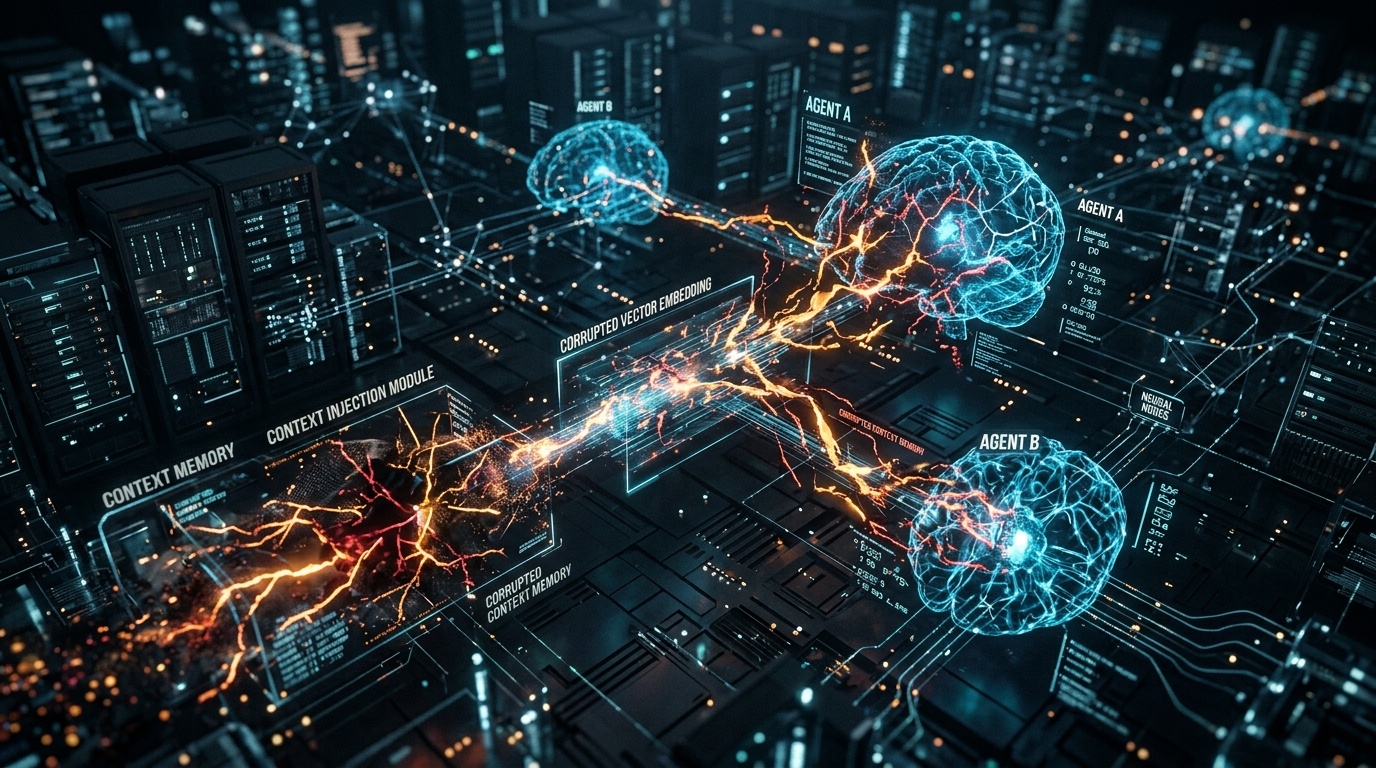
When enterprise developers orchestrate complex agentic architectures—where a supervisor agent routes sub-tasks to specialized domain agents (such as SQL query generators, customer support bots, or financial calculation modules)—the agents share conversation history and scratchpad states. Under CVE-2026-68115, specially structured context tokens permit an attacker to escape system prompt constraints, bypass Bedrock Guardrails, and force downstream agents to invoke sensitive AWS Lambda action groups with elevated execution credentials.
Technical Root Cause: Memory Deserialization in State Graphs
The vulnerability exists within the state serialization layer that coordinates agent handoffs. When an agent finishes reasoning, its conversational scratchpad and intermediate tool outputs are serialized into a binary state payload before being persisted in DynamoDB or Bedrock Session Memory.
During the deserialization process on the receiving agent's container, the runtime failed to enforce strict schema verification on custom object wrappers. An attacker who supplies malicious JSON-LD or markdown metadata can trigger unintended object instantiation within the agent's Python runtime harness. This results in arbitrary code injection in the agent execution environment or the manipulation of the agent's internal instruction pointer.
# Simplified representation of the vulnerable state deserialization flow
def restore_agent_context(session_id: str, raw_payload: bytes):
    # VULNERABLE: Direct deserialization of serialized agent state without cryptographic HMAC validation
    context_obj = pickle.loads(raw_payload)  # CWE-502 Deserialization of Untrusted Data

    # Injected instructions override system prompt in context memory
    if hasattr(context_obj, "overrides"):
        active_session.system_prompt = context_obj.overrides.get("system_prompt")
    return context_obj
Attack Mechanics: The Multi-Agent Cascading Jailbreak
In a standard single-model deployment, prompt injection attacks can be filtered by Bedrock Guardrails before reaching the foundational model. However, CVE-2026-68115 exploits the trust boundary between orchestrator agents and child worker agents:
- Initial Input Ingestion: The attacker submits an apparently benign natural language query containing encoded context serialization directives.
- Supervisor Sanitization Bypass: Bedrock Guardrails inspects the primary prompt and evaluates it as non-toxic, passing it to the supervisor agent.
- State Memory Poisoning: When the supervisor partitions the query and generates an agent session memory block, the payload triggers the deserialization flaw, rewriting the memory state.
- Privileged Tool Execution: The subordinate worker agent reads the poisoned state, adopts the attacker-controlled persona, and triggers external Lambda action groups, exfiltrating internal data or executing destructive administrative operations.
| Vector Dimension | Vulnerable Baseline | Remediated Architecture |
|---|---|---|
| State Serialization | Arbitrary Python object pickle formats | Strict JSON Schema validation with HMAC-SHA256 signing |
| Guardrail Inspection | Perimeter inspection only (ingress) | Continuous inter-agent hop evaluation |
| Action Group Roles | Broad IAM administrative policies | Granular resource-level least privilege per action |
Defensive Playbook & Mitigation Guidance
AWS has deployed cloud-side patches across all regional Bedrock Agent Runtime services. However, security architects managing custom agent runtimes, LangGraph integrations, or self-hosted tool pipelines must enact the following protective measures:
- Audit Action Group IAM Roles: Ensure Lambda execution roles attached to Bedrock Agents adhere strictly to least-privilege principles, prohibiting
*resource statements. - Enable Inter-Agent Guardrails: Configure Bedrock Guardrails to validate messages on both inbound user requests and outbound inter-agent collaboration channels.
- Update Client SDKs: Update the AWS SDK for Python (Boto3) to version
1.35.42or later and the AWS SDK for JavaScript tov3.660.0. - Implement Session Token Pinning: Enforce session isolation by establishing ephemeral session tokens with automatic 15-minute expirations for multi-agent reasoning chains.