Executive Summary: Perimeter Gateway Collapse
Enterprise networking and application security vendor F5 has issued an emergency security bulletin (Advisory K000162605) confirming that sophisticated threat actors are actively weaponizing a critical remote code execution (RCE) vulnerability tracked as CVE-2026-94127. Assigned a near-maximum CVSS v3.1 base score of 9.8, the vulnerability affects F5 BIG-IP appliances running the Access Policy Manager (APM) module.
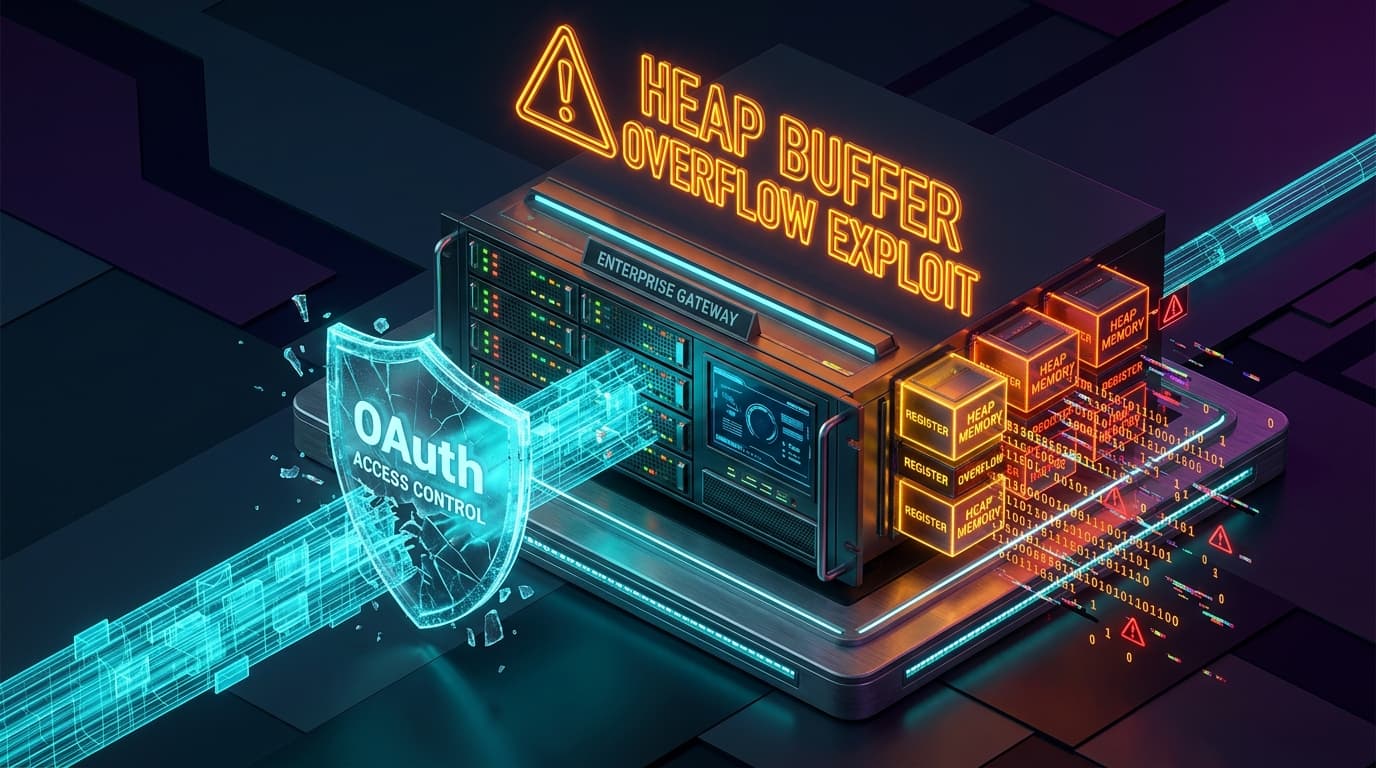
The defect operates within the high-performance data plane of F5's proprietary Traffic Management Microkernel (TMM). Specifically, when an enterprise virtual server is configured to evaluate incoming client traffic using both an active APM access policy and an OAuth client/resource server profile, improper memory boundary enforcement allows unauthenticated remote attackers to trigger a heap-based buffer overflow (CWE-122).
Because BIG-IP appliances frequently serve as the foundational authentication gateway, SSL/TLS termination edge, and single sign-on (SSO) reverse proxy for Fortune 500 corporations, government agencies, and financial institutions, successful exploitation grants adversaries complete control over perimeter network traffic. Attackers can decrypt in-flight TLS sessions, harvest enterprise Active Directory credentials, and pivot laterally into protected internal server enclaves.
Technical Dissection: TMM Data Plane Heap Corruption
Unlike administrative management plane vulnerabilities (such as earlier iControl REST flaws), CVE-2026-94127 is an unauthenticated data-plane bug. It executes directly within the fast-path packet processing routines of the tmm daemon listening on public-facing virtual server ports (typically 443/tcp).
OAuth Profile Token Parsing Mechanics
When F5 BIG-IP APM handles federated identity transactions (such as OpenID Connect or OAuth 2.0 bearer authorization), incoming client requests contain structured JSON Web Tokens (JWT) or base64-encoded URL parameters. During the token validation phase, TMM allocates a fixed-size buffer on the internal process heap to normalize and parse identity claims:
GET /oauth/v1/authorize?response_type=code&client_id=corp_app&redirect_uri=https://portal.enterprise.com/callback&state=[MALFORMED_STATE_TOKEN] HTTP/1.1
Host: vpn.enterprise.com
Authorization: Bearer eyJhbGciOiJSUzI1NiIsImtpZCI6Ij...[Oversized Encoded Claim Block]...
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64)
When parsing nested cryptographic parameters within malformed OAuth authorization header structures, the TMM state machine fails to verify the length of decompressed sub-claims against the pre-allocated chunk boundary. An arithmetic calculation error causes the copy loop to write past the boundary of the allocated heap chunk into adjacent memory structures:
- Heap Chunk Overwrite: Attacker-controlled byte sequences overwrite adjacent heap chunk metadata headers and internal pointer tables.
- Instruction Pointer Hijack: By grooming the TMM memory layout with repeated malformed requests, adversaries overwrite callback function pointers associated with subsequent SSL handshake decoders.
- Arbitrary Execution: The TMM process redirects control flow to injected shellcode or returns into internal shared library functions (
libtmm.so), executing commands under the context of the privilegedrootortmmservice accounts.
Active Threat Telemetry & Exploitation Footprint
Telemetric observations from global cybersecurity sensors indicate that threat groups are executing automated scans targeting external F5 endpoints presenting OAuth endpoints. Successful exploitation produces either core dumps of the tmm daemon (causing failover crashes in high-availability clusters) or silent persistence where attackers inject web shells into /var/tmp/ or modify PAM authentication modules.
Vulnerability Scope & Affected Matrix
| BIG-IP Product Branch | Vulnerable Versions | Remediated Hotfix Build | Exploitation Prerequisite |
|---|---|---|---|
| BIG-IP APM 17.x | 17.1.0 – 17.1.1.3 | 17.1.1.4 / 17.1.2 Hotfix | Virtual Server + APM Policy + OAuth Profile |
| BIG-IP APM 16.x | 16.1.2 – 16.1.4.2 | 16.1.4.3 Hotfix | Virtual Server + APM Policy + OAuth Profile |
| BIG-IP APM 15.x | 15.1.8 – 15.1.10.3 | 15.1.10.4 Hotfix | Virtual Server + APM Policy + OAuth Profile |
Defensive Playbook & Remediation Commands
System administrators and network security engineers managing BIG-IP infrastructure must immediately determine their exposure and execute mitigation actions.
1. Automated Vulnerability Verification via tmsh
Execute the following Traffic Management Shell (tmsh) query to identify whether any active virtual servers in your configuration possess both an APM access profile and an OAuth profile:
# Query BIG-IP tmsh for vulnerable virtual server configurations
tmsh -q -c 'list ltm virtual one-line' | grep -E 'profiles.*oauth' | grep -E 'access-policy'

# If any virtual servers are returned, your appliance is exposed to CVE-2026-94127
2. Emergency Temporary Workaround (If Immediate Patching is Delayed)
If engineering constraints prevent an immediate maintenance window for firmware upgrading, F5 recommends decoupling the OAuth profile or applying an emergency iRule to sanitize incoming Authorization headers and reject malformed token strings exceeding expected lengths:
# F5 iRule Mitigation for CVE-2026-94127 (Header Length Enforcement)
when HTTP_REQUEST {
    if { [HTTP::header exists "Authorization"] } {
        # Inspect length of bearer token claim
        if { [string length [HTTP::header "Authorization"]] > 4096 } {
            log local0.warn "CVE-2026-94127 Exploit Attempt Dropped: [IP::client_addr]"
            HTTP::drop
            return
        }
    }
}
3. Threat Hunting & Compromise Verification
Review BIG-IP internal log files for segmentation faults or unhandled exceptions originating from the Traffic Management Microkernel:
# Inspect /var/log/tmm and /var/log/ltm for daemon crashes
grep -i "SIGSEGV" /var/log/tmm*
grep -i "assertion failed" /var/log/tmm*
ls -lah /var/crash/

# Check for unexpected listening sockets or newly created binaries
netstat -tulpn | grep -vE 'tmm|httpd|sshd|snmpd'
find /var/tmp /tmp /shared/tmp -type f -mtime -3