Apple has deployed out-of-band security updates resolving an actively exploited zero-day vulnerability (CVE-2026-86950, CVSS 8.8) embedded within its core 2D graphics rendering framework, CoreGraphics. Security telemetry indicates that advanced threat actors weaponized the flaw in targeted, zero-click exploit chains against prominent enterprise executives and diplomatic personnel, allowing remote code execution on fully patched iPhones, iPads, and Mac workstations.
Root Cause Analysis: Heap Corruption in Vector Processing (CWE-787)
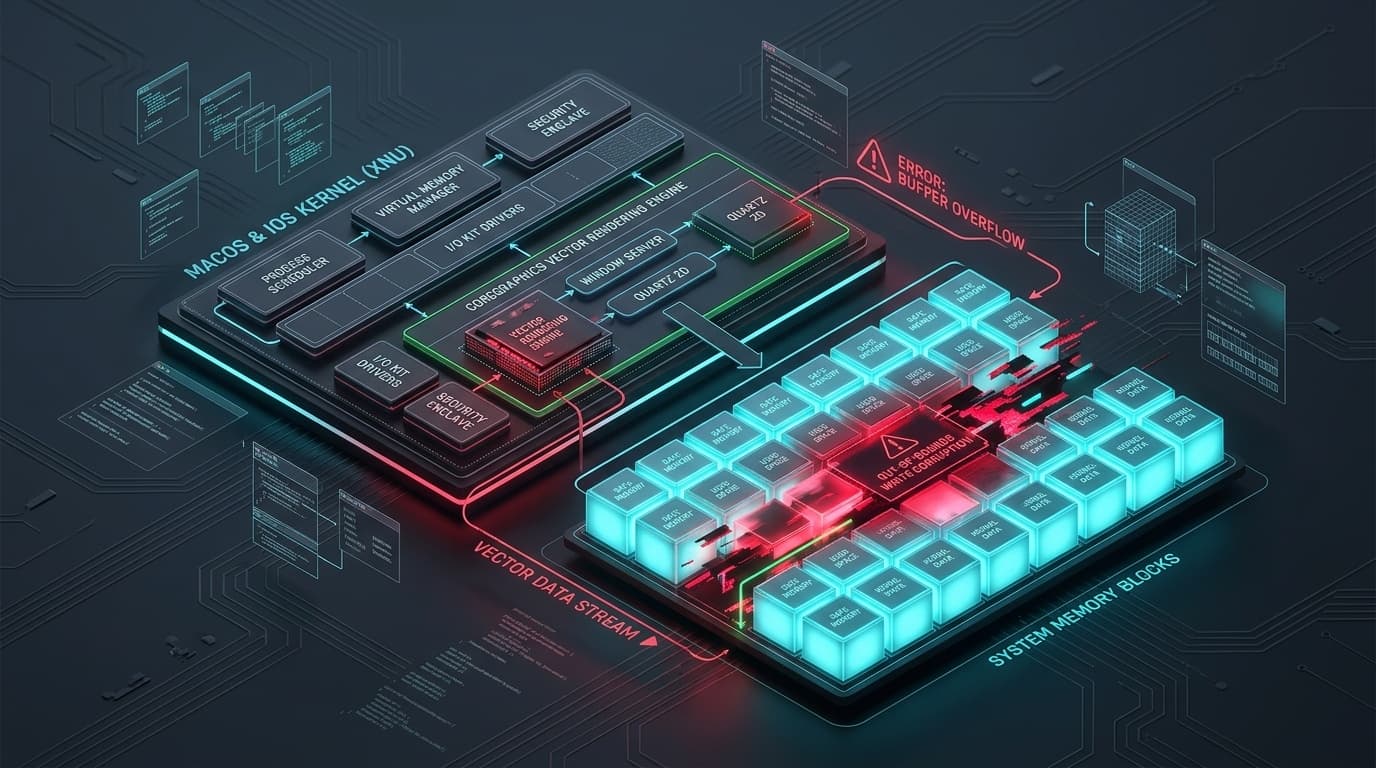
The CoreGraphics framework underpins the visual compositing pipeline across all Apple operating systems, responsible for rendering PDF structures, TrueType/OpenType font glyphs, and complex Bezier curves.
According to technical disclosures, the flaw is classified under CWE-787: Out-of-bounds Write. When CoreGraphics parses nested SVG or PDF vector path definition chunks, an integer calculation error in the path rasterization allocator results in an under-allocated memory buffer.
When the drawing engine renders stroke geometry for multi-segment Bezier spline curves, it writes coordinate points beyond the allocated heap boundary, overwriting adjacent memory structures:
// Pseudocode of vulnerable vector path rasterization logic in CoreGraphics
void CGPathRasterizeSpline(CGContextRef ctx, CGPathElement *element) {
    // Insecure: Integer multiplication truncation leads to undersized allocation
    size_t requiredSize = element->pointCount * sizeof(CGPoint);
    CGPoint *renderBuffer = (CGPoint *)malloc((uint16_t)requiredSize);

    // Out-of-bounds memory write occurs during point interpolation loop
    for (int i = 0; i < element->pointCount; i++) {
        renderBuffer[i] = InterpolateBezier(element->points, i); // Buffer overflow
    }
}
By corrupting objective-C object pointers located directly after the rendering buffer, attackers construct an initial arbitrary read/write primitive within the sandboxed render process, laying the foundation for a secondary kernel privilege escalation exploit.
Exploitation Vector & Zero-Click Delivery
Forensic telemetry reveals that attackers delivered crafted graphic assets via rich messaging protocols (such as iMessage and third-party collaboration platforms). Because the operating system automatically generates background thumbnails and rich link previews upon message receipt, the victim device triggers the vulnerable CGPathRasterizeSpline routine without requiring user interaction or file execution.
Affected Apple Platforms & Operating Systems
| Apple Platform | Vulnerable OS Version | Patched Release |
|---|---|---|
| iPhone / iPad | iOS & iPadOS 26.0 through 26.7.0 | iOS / iPadOS 26.7.1 |
| Mac (macOS Sequoia) | macOS 15.0 through 15.8.0 | macOS Sequoia 15.8.1 |
| Mac (macOS Tahoe) | macOS 26.0 through 26.7.0 | macOS Tahoe 26.7.1 |
| Apple Vision Pro | visionOS 2.0 through 2.5.0 | visionOS 2.5.1 |
Enterprise Remediation Directives
- Mandate Fleet-Wide MDM Push: Configure Jamf, Microsoft Intune, or Apple Business Manager to enforce rapid operating system installation across all corporate-enrolled endpoints.
- Enable Lockdown Mode for High-Risk Users: Executive leadership and legal personnel traveling abroad should activate Apple Lockdown Mode, which blocks complex vector fonts and message attachment preview processing by default.
- Audit Mobile Threat Defense (MTD) Telemetry: Monitor device management logs for abnormal process crashes originating from
imagent,SpringBoard, orQuickLookdaemons.