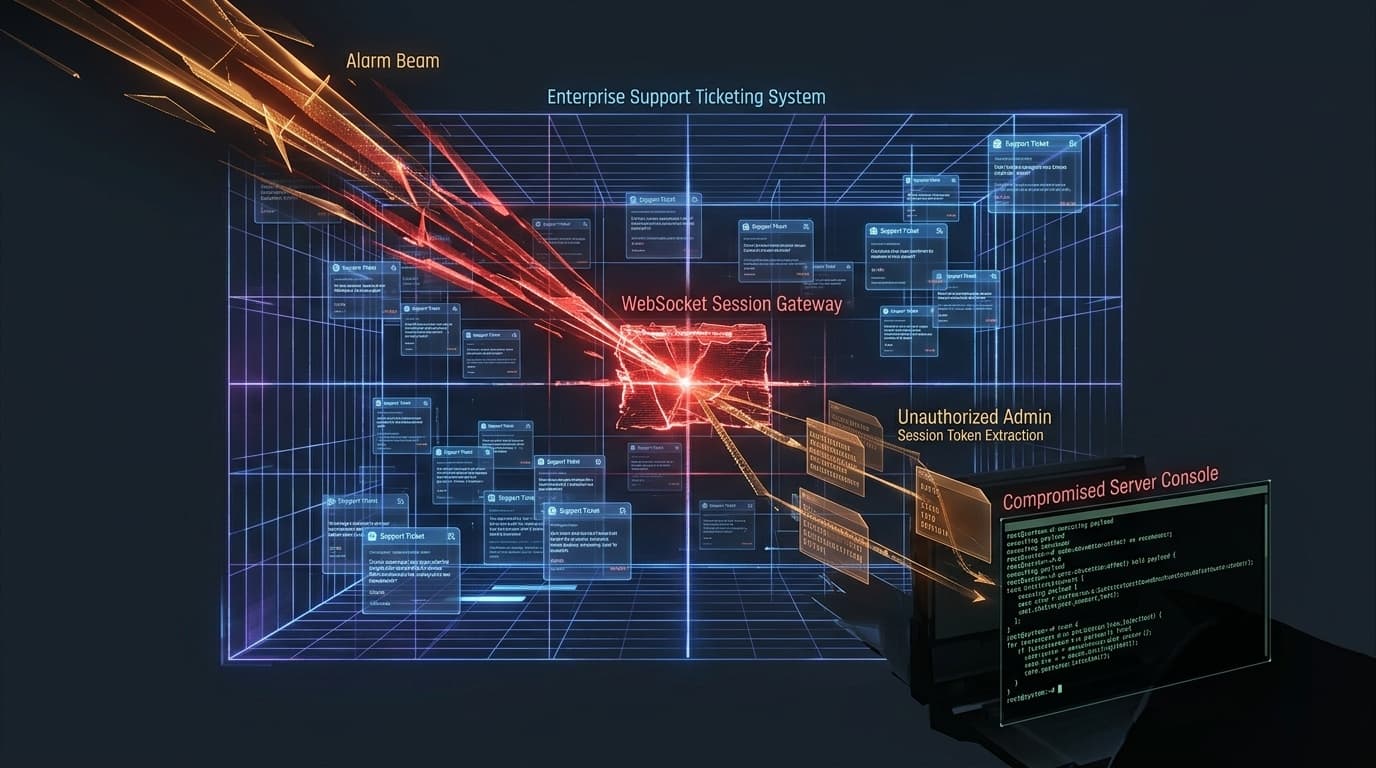
Threat actors have weaponized a devastating two-stage remote exploit chain targeting Zammad, the open-source web-based ticketing system relied upon by thousands of organizations worldwide. By chaining an unauthenticated session fixation defect (CVE-2026-102489) with an improper privilege management vulnerability (CVE-2026-102490), attackers achieve remote, unauthenticated code execution with full root privileges on host servers. CISA cataloged CVE-2026-102490 under emergency remediation directive BOD 26-04.
The Two-Stage Weaponization Chain
The threat campaign executes in two coordinated phases to transition from zero credentials to complete host takeover:
Phase 1: Session Fixation & Admin Account Hijacking (CVE-2026-102489)
In older releases of Zammad (notably 6.5 and earlier), the authentication controller failed to regenerate session tokens upon successful user logon. An attacker pre-seeds a valid session token in an unauthenticated HTTP request. When an administrator subsequently logs into the helpdesk, the backend accepts the attacker's token without issuing a fresh cookie. The attacker then assumes the administrative session, enabling access to system settings, custom hooks, and Ruby background job schedulers.
Phase 2: Local Privilege Escalation to Root (CVE-2026-102490)
Once initial script execution is established within the context of the service account (zammad), the attacker triggers CVE-2026-102490. Due to improper file permissions and misconfigured sudoer delegation scripts used for database backups and service maintenance, the zammad user can overwrite helper wrapper scripts executed by root cron tasks. Within seconds, the attacker spawns an interactive root shell.
Vulnerable Software Versions & Remediation Matrix
| Deployment Flavor | Vulnerable Releases | Fixed / Remediated Release | Required Remediation Action |
|---|---|---|---|
| Zammad Native Debian / Ubuntu Package | Versions 1.5.0 through 7.1.0-alpha | Zammad 7.1.0 | Execute apt-get package upgrade and restart rails workers |
| Zammad RHEL / CentOS Package | Versions 1.5.0 through 7.1.0-alpha | Zammad 7.1.0 | Execute dnf package upgrade and rotate database credentials |
| Zammad Docker Compose / Kubernetes | Image tags < 7.1.0 | zammad/zammad:7.1.0 | Pull updated container image and restart pod deployment |
Step-by-Step Remediation Playbook & Patch Commands
Security teams operating self-hosted or cloud-hosted Zammad instances must execute immediate containment and verification:
- Upgrade Zammad on Ubuntu / Debian Servers:
# Update repositories and install patched Zammad release sudo apt-get update sudo apt-get --only-upgrade install -y zammad # Verify package version dpkg -l | grep zammad - Upgrade Zammad Docker Deployments:
# Pull the patched container images docker pull zammad/zammad:7.1.0 docker-compose down && docker-compose up -d - Invalidate All Active Sessions: Terminate all active web sessions across the database:
zammad run rails r "Session.delete_all" - Inspect Sudoers & Cron Entries: Verify the integrity of
/etc/sudoers.d/zammadand ensure permissions on maintenance scripts are strictly owned byroot:rootwith mode0750:sudo chown -R root:root /opt/zammad/contrib/ sudo chmod 0750 /opt/zammad/contrib/backup/* - Rotate Credentials: Given that helpdesks store inbound/outbound SMTP credentials, IMAP passwords, and third-party webhook secrets, all integrated secrets must be rotated following server verification.
Threat Intelligence & Forensic Hunting Queries
Active intrusions demonstrate threat actors immediately dumping PostgreSQL database credentials and harvesting OAuth tokens integrated with Microsoft 365. Query server access logs for anomalous session pre-seeding:
# Search NGINX/Apache logs for session fixation attempts
grep -E "POST /api/v1/signin" /var/log/nginx/access.log | grep -E "Set-Cookie|Cookie:"

# Check for unauthorized processes spawned by user zammad
ps -u zammad -o pid,user,args | grep -E "bash|sh|nc|python|perl|curl|wget"