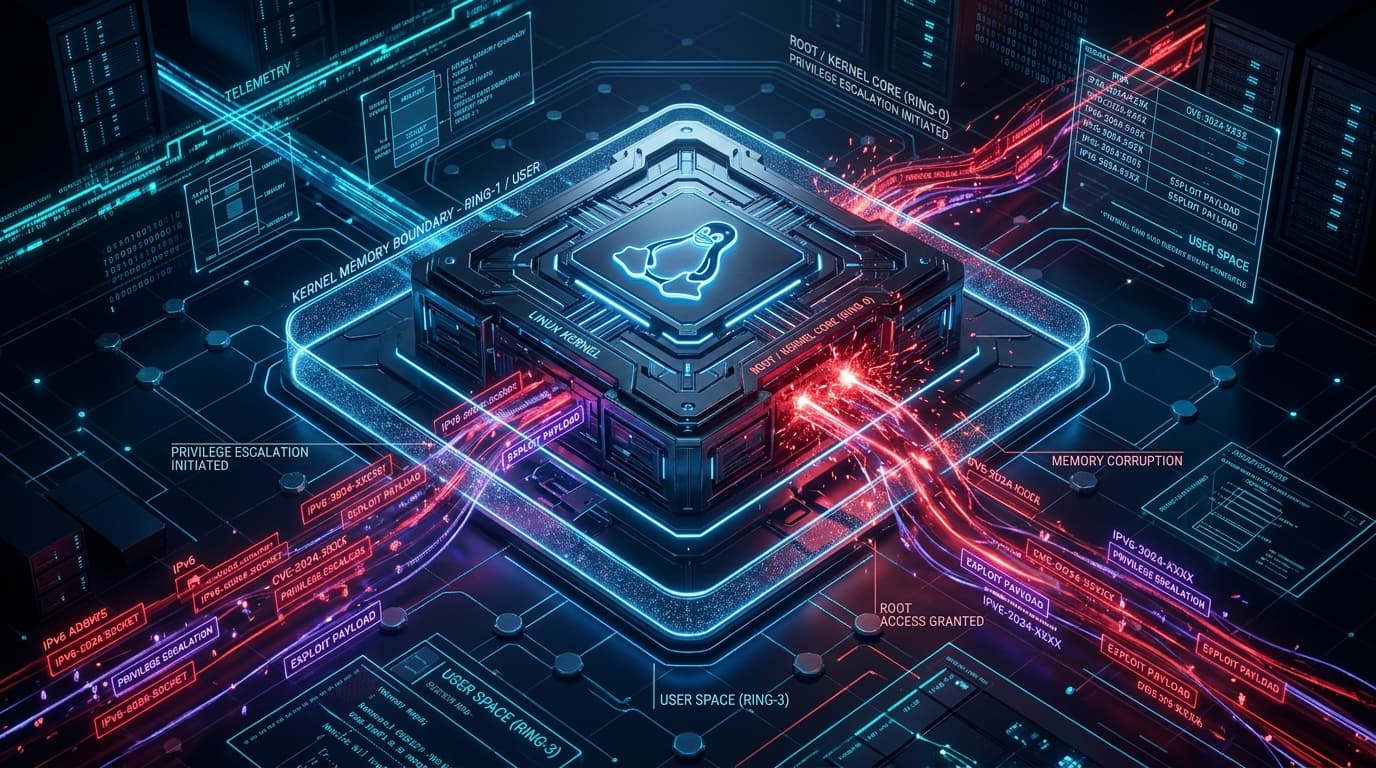
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities (KEV) catalog to include CVE-2026-53362, a critical privilege escalation defect in the Linux Kernel networking subsystem. Evidence indicates state-aligned actors and initial access brokers are actively weaponizing the defect to escalate from unprivileged shell access to unrestricted root (Ring-0) authority.
Carrying a CVSS v3.1 base score of 9.3, the vulnerability resides within the IPv6 networking stack—specifically how the kernel manages memory reallocation during raw socket option configurations and neighbor discovery table updates. Because the flaw can be triggered from unprivileged user namespaces, it poses an acute threat to containerized cloud architectures and multi-tenant virtualization clusters.
Kernel Mechanics: Race Condition & Socket State Confusion
According to vulnerability analyses published by kernel maintainers, the flaw stems from an asynchronous state desynchronization between the rawv6_setsockopt handler and the network device queue cleanup functions in net/ipv6/raw.c:
- Unprivileged Namespace Creation: An unprivileged local attacker initializes a new user and network namespace (
unshare(CLONE_NEWUSER | CLONE_NEWNET)), enabling full configuration privileges over virtual network interfaces. - Socket Option Manipulation: The attacker creates an IPv6 raw socket and repeatedly triggers concurrent socket option reconfiguration while simultaneously closing the underlying socket file descriptor.
- Use-After-Free (UAF) Trigger: The race condition results in a use-after-free scenario where kernel memory pointers to the network protocol block are accessed post-deallocation.
- Credential Structure Overwrite: By spraying the kernel heap with crafted payloads, the attacker overwrites the process's
struct credstructure, zeroing out the UID and GID fields to achieve instant root privilege.
Container isolation relies on namespaces and cgroups sharing a single host kernel. A local privilege escalation in the Linux networking subsystem enables unprivileged container payloads to escape container sandboxes and seize the entire physical host node.
Impacted Distributions & Kernel Branches
| Distribution / Platform | Vulnerable Kernel Versions | Patched Release | CISA Remediation Deadline |
|---|---|---|---|
| Red Hat Enterprise Linux (RHEL 8 & 9) | 5.14.0-x through 5.14.0-427 | kernel-5.14.0-427.18.1 | Immediate Action Required |
| Ubuntu Server (22.04 LTS / 24.04 LTS) | 5.15.0-x, 6.5.0-x, 6.8.0-x | 6.8.0-45-generic | Immediate Action Required |
| SUSE Linux Enterprise Server (SLES 15) | 5.14.21-150500.55.x | 5.14.21-150500.55.73.1 | Immediate Action Required |
Detection & Hardening Playbook
System administrators and security operations engineers must audit their Linux infrastructure using the following verification and mitigation procedures:
# Check currently running kernel version
uname -r

# Verify if unprivileged user namespaces are enabled
sysctl kernel.unprivileged_userns_clone

# Interim Mitigation: Disable unprivileged user namespaces (if feasible)
sudo sysctl -w kernel.unprivileged_userns_clone=0
echo "kernel.unprivileged_userns_clone=0" | sudo tee -a /etc/sysctl.d/99-disable-userns.conf

# Audit system logs for abnormal IPv6 raw socket allocations
journalctl -k | grep -E "kernel BUG at|general protection fault|rawv6"
Recommended Enterprise Countermeasures
- Deploy Kernel Updates Immediately: Reboot target machines into updated kernel packages supplied by your distribution vendor.
- Restrict Unprivileged User Namespaces: In environments where rootless containers are not mandatory, disabling unprivileged user namespaces blocks the initial namespace creation step required to trigger the exploit chain.
- Kubernetes Pod Security Admission: Mandate the
BaselineorRestrictedPod Security standard, explicitly disallowing pods from running withCAP_NET_RAWorCAP_NET_ADMINprivileges.