OT / SCADASiemens Building Energy Gateway Flaw Enables Denial of Service in Smart Facilities
CISA issues advisory ICSA-26-265-08 for Siemens WTV676 and WTV776 M-Bus gateways, warning of a web interface flaw that terminates building SCADA telemetry.
1,437 articles
OT / SCADACISA issues advisory ICSA-26-265-08 for Siemens WTV676 and WTV776 M-Bus gateways, warning of a web interface flaw that terminates building SCADA telemetry.
RansomwareRiver Financial discloses unauthorized ransomware intrusion and customer data exfiltration in SEC Form 8-K filings following network extortion demands.
OT / SCADACISA releases advisory ICSA-26-265-01 for critical CVSS 9.8 flaw CVE-2026-87121 in lwIP MQTT client, allowing unauthenticated attackers to execute arbitrary code.
AWS CloudAWS publishes Bulletin 2026-094-AWS for high-severity flaw CVE-2026-84851 in Amazon Ion-C library, allowing attackers to exhaust stack memory and crash services.
Data BreachCB Financial Services files historic SEC Form 8-K Item 1.05 after an employee used an unauthorized AI tool to process non-public customer PII and SSNs.
AWS CloudAWS and OpenSearch release bulletin 2026-092-AWS for high-severity flaw CVE-2026-83497 in the SQL plugin allowing authenticated users to execute code via cursors.
Data BreachAstrana Health files SEC Form 8-K Item 1.05 after threat actors spoofed corporate phone numbers to socially engineer IT support and compromise patient systems.
MicrosoftMicrosoft discloses high-severity flaw CVE-2026-85917 in Azure AI Foundry allowing unauthenticated attackers to execute SSRF and elevate privileges over the network.
OT / SCADACISA and lwIP maintainers warn of high-severity flaw CVE-2026-91018 in the lwIP TCP/IP stack allowing unauthenticated remote memory corruption across IoT and PLCs.
MicrosoftMicrosoft addresses CVSS 9.6 vulnerability CVE-2026-87701 in Azure Cosmos DB allowing authenticated attackers to execute downstream injection and elevate privileges.
Deep DiveThe Reserve Bank of India overhauls bank cyber regulations with the 2026 Directions, mandating Board-level accountability, assurance audits, and 6-hour reporting.
Check PointCheck Point and CISA confirm active in-the-wild exploitation of CVSS 9.8 flaw CVE-2026-93616 allowing unauthenticated attackers to write arbitrary files as root.
RansomwareNavient files SEC Form 8-K Item 1.05 after a ransomware attack on an external law firm exposed sensitive student loan borrower PII and Social Security numbers.
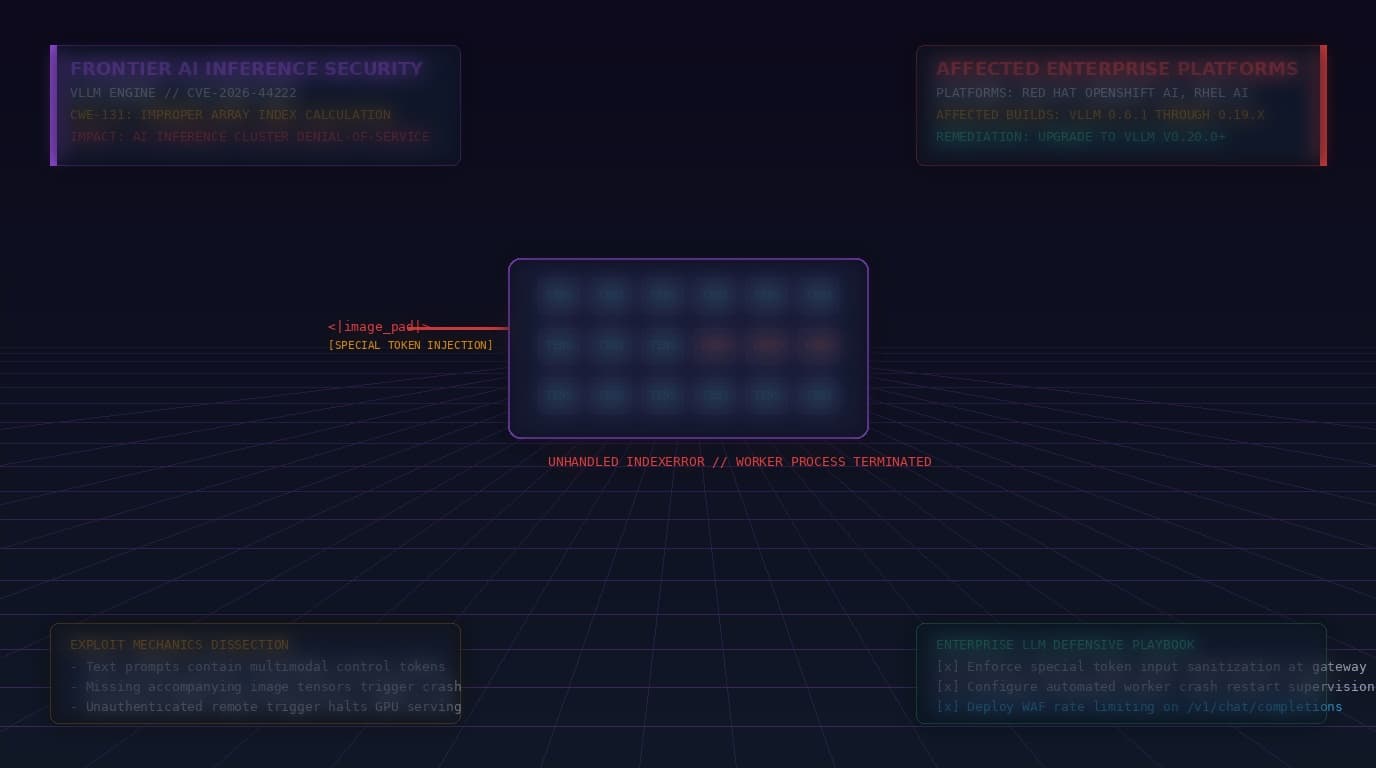
LinuxHigh-severity flaw CVE-2026-44222 in vLLM allows remote unauthenticated users to crash distributed GPU inference clusters via crafted multimodal tokens.
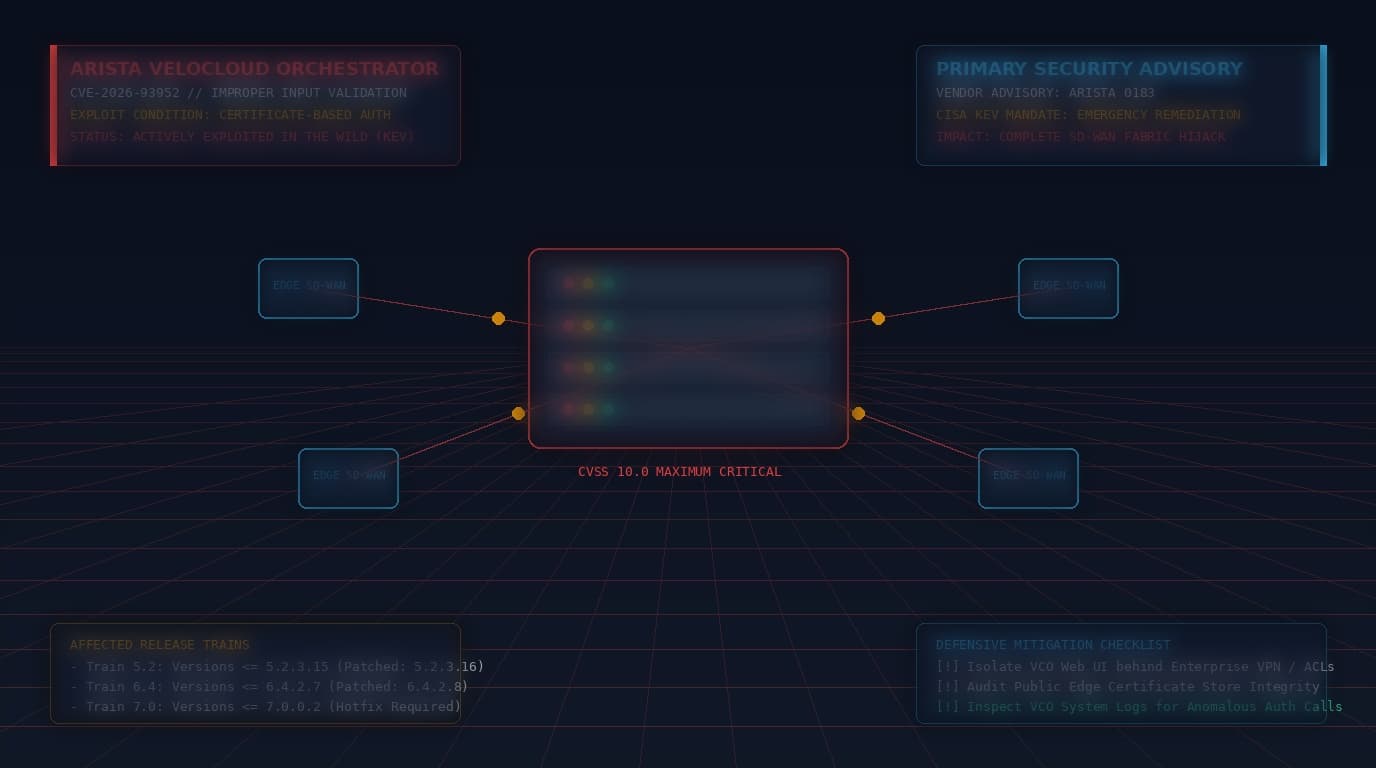
Active ExploitArista confirms active in-the-wild exploitation of CVSS 10.0 CVE-2026-93952, allowing unauthenticated attackers to hijack on-prem VeloCloud Orchestrators.
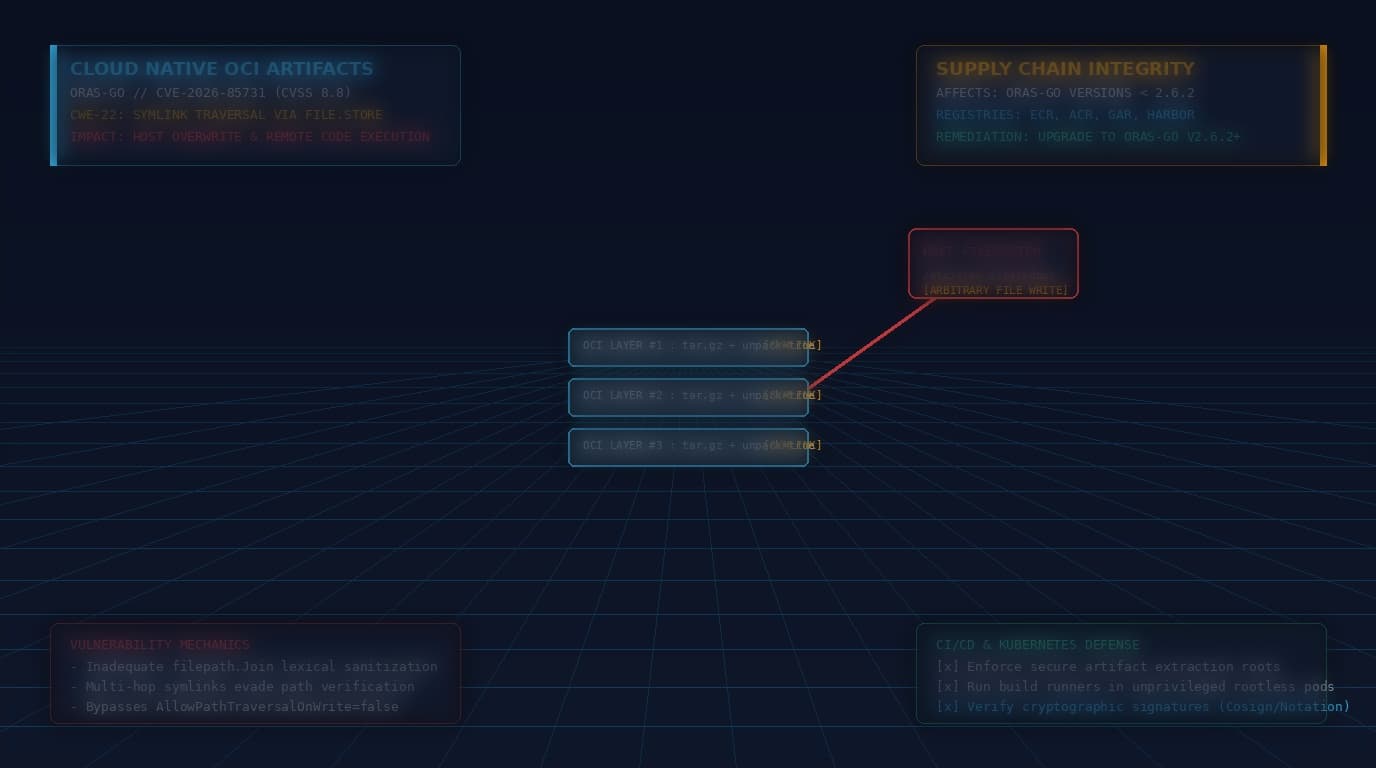
KubernetesA high-severity CVSS 8.8 path traversal vulnerability in oras-go allows malicious OCI container artifacts to escape extraction roots and execute arbitrary code.
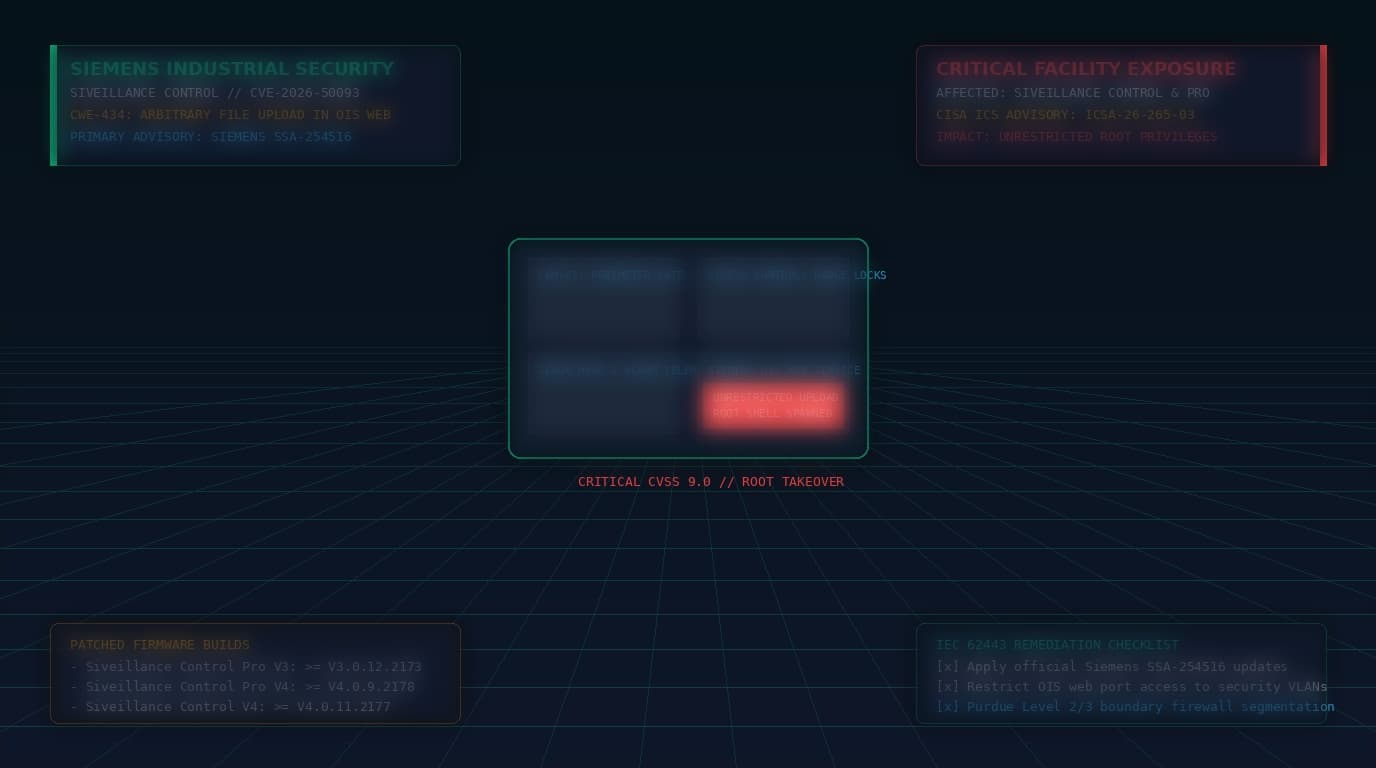
OT / SCADASiemens patches critical CVSS 9.0 flaw CVE-2026-50093 in Siveillance Control OIS web service, enabling unauthenticated remote attackers to obtain root privileges.
Threat IntelF5 confirms active zero-day exploitation of CVE-2026-94127, a critical heap buffer overflow in BIG-IP APM OAuth gateways allowing unauthenticated remote code execution.
RansomwareNutex Health files amended SEC Form 8-K Item 1.05 confirming patient PHI and provider records exfiltrated and published following ransomware double extortion.
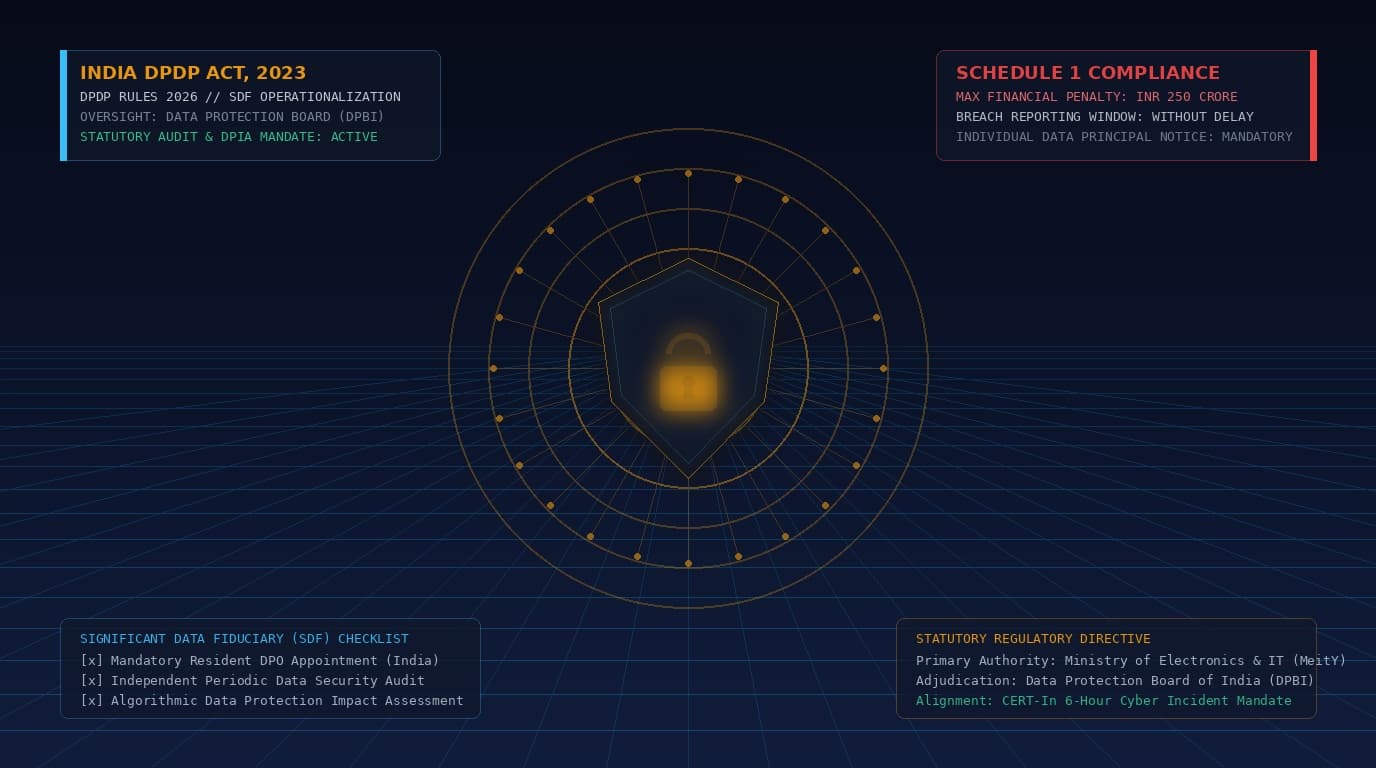
Data BreachIndia operationalizes DPDP Rules 2026, establishing Data Protection Board inquiries, mandatory resident DPOs, independent audits, and ₹250 Crore breach fines.
MicrosoftGoogle Cloud remediates critical GCP-2026-058 flaw in GKE Multi-Cloud APIs where missing project checks enabled unauthorized cluster registration and IAM impersonation.
MicrosoftSecurity researchers demonstrate BragJack prompt forcing attacks against Chrome and Edge, hijacking agentic AI control planes to exfiltrate files and spy via camera.
OT / SCADACISA warns of CVE-2026-88020 in OpenPLC Runtime v3 web interface, allowing attackers to hijack operator sessions and manipulate physical industrial processes.
Threat IntelCISA issues advisory for CareCam CM2507 IP cameras detailing unauthenticated video streaming, empty ONVIF passwords, and hardcoded root hashes risking facility surveillance.