Executive Lead: Perimeter Surveillance Systems Compromised by Zero-Auth Flaws
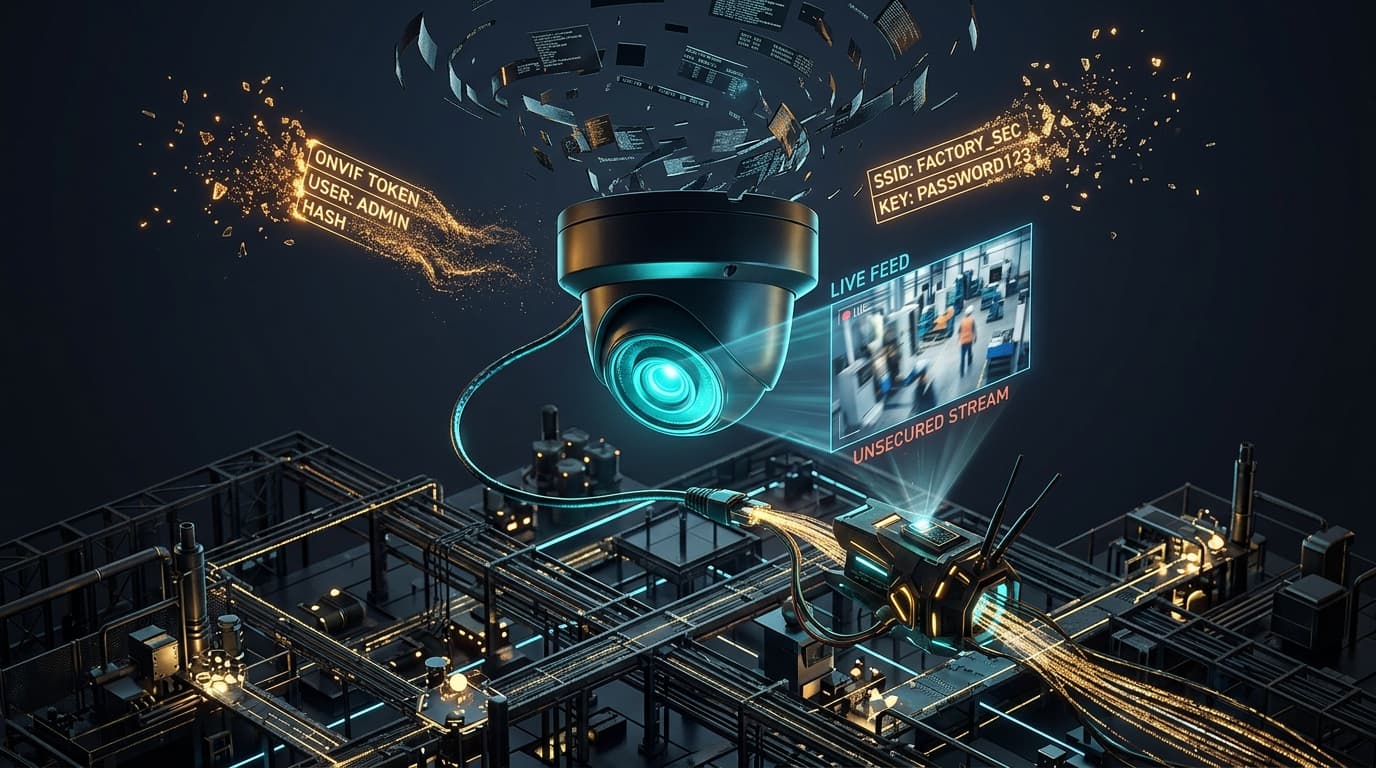
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an Industrial Control Systems (ICS) security advisory warning enterprise facilities directors, physical security administrators, and critical infrastructure operators of multiple severe vulnerabilities in CareCam CM2507 IP surveillance cameras. Identified across firmware release HMT.CM2507 v251211.1507, the flaws allow remote, unauthenticated adversaries on adjacent or routable networks to intercept live video feeds, extract wireless credentials, and gain unrestricted root administrative control over the camera hardware.
CareCam CM2507 dome and bullet cameras are widely deployed across manufacturing plants, warehousing logistics hubs, smart building perimeters, and municipal facilities. The primary vulnerability, cataloged as CVE-2026-88259 with a CVSS v3.1 base score of 7.5 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N), exposes Real-Time Streaming Protocol (RTSP) and HTTP video endpoints to unauthenticated capture.
Exacerbating the video leak is CVE-2026-84398, where the standardized Open Network Video Interface Forum (ONVIF) management account ships with an empty administrative password. Compounding these issues, CVE-2026-85497 and CVE-2026-81321 reveal hardcoded root password hashes and unencrypted Wi-Fi credentials stored in local flash memory. Crucially, CISA reported that the hardware manufacturer has remained unresponsive to coordinated vulnerability disclosure attempts, leaving organizations solely dependent on network-level architectural mitigations.
Technical Root Cause: Missing Authentication & Insecure Credential Storage
The vulnerabilities illustrate a systemic collapse of foundational embedded security practices across four discrete Common Weakness Enumeration (CWE) categories:
1. Unauthenticated Video Endpoint (CVE-2026-88259 / CWE-306)
Under CWE-306 (Missing Authentication for Critical Function), the embedded streaming daemon binds to TCP port 554 (RTSP) and TCP port 8080 (HTTP MJPEG). While the camera's web configuration interface requires basic authentication, the underlying streaming handler executes no credential verification when receiving standard RTSP DESCRIBE or SETUP requests:
# Unauthenticated RTSP stream interrogation via FFmpeg / VLC:
ffplay rtsp://camera-ip:554/live/ch0

# Packet inspection reveals immediate H.264 video NAL units transmitted
# without any HTTP 401 Unauthorized challenge-response negotiation!
2. Empty Password on Privileged ONVIF Service (CVE-2026-84398 / CWE-258)
ONVIF is the global open industry standard for IP-based physical security products. Under CWE-258 (Empty Password in Configuration File), the SOAP XML service listening on TCP port 8899 evaluates incoming GetSystemDateAndTime and SetUser requests. The privileged admin user is configured with a null password string (""). An attacker can submit an unauthenticated XML envelope to overwrite administrative users or reconfigure PTZ (Pan-Tilt-Zoom) sweeps:
POST /onvif/device_service HTTP/1.1
Host: 192.168.10.45:8899
Content-Type: application/soap+xml; charset=utf-8

<s:Envelope xmlns:s="http://www.w3.org/2003/05/soap-envelope">
  <s:Body xmlns:d="http://www.onvif.org/ver10/device/wsdl">
    <d:SetUser>
      <d:User>
        <d:Username>attacker_root</d:Username>
        <d:Password>InjectedPassword2026!</d:Password>
        <d:UserLevel>Administrator</d:UserLevel>
      </d:User>
    </d:SetUser>
  </s:Body>
</s:Envelope>
3. Static Root Hash & Plaintext Wi-Fi Keys (CVE-2026-85497 & CVE-2026-81321)
Firmware extraction of HMT.CM2507 v251211.1507 reveals that /etc/shadow contains a fixed, highly vulnerable MD5-based crypt hash for the root account (CWE-326). Simultaneously, when the camera is joined to a corporate Wi-Fi network, the WPA2/WPA3 Pre-Shared Key (PSK) is written directly into /etc/wpa_supplicant.conf in plain text without filesystem encryption (CWE-312).
+------------------------------------------------------------------------------------------+
|                  CARECAM CM2507 MULTI-VULNERABILITY INTRUSION FLOW                       |
+------------------------------------------------------------------------------------------+
| Attacker on Enterprise LAN / Adjacent Wi-Fi                                              |
|                                       |                                                  |
|       +-------------------------------+-------------------------------+                  |
|       |                               |                               |                  |
|       v                               v                               v                  |
| [Port 554: RTSP Stream]       [Port 8899: ONVIF Service]      [Port 23 / 80: Flash Memory]   |
| Missing Authentication        Empty Admin Password            Plaintext /etc/wpa_supplicant |
| (CVE-2026-88259)              (CVE-2026-84398)                (CVE-2026-81321)              |
|       |                               |                               |                  |
|       v                               v                               v                  |
| Real-Time Facility Video      PTZ Hijack, Camera Re-pointing, Corporate Wi-Fi PSK Stolen,   |
| Live Reconnaissance           Firmware Backdoor Uploaded      Pivots into Corporate LAN  |
+------------------------------------------------------------------------------------------+
Operational Threat Context: Physical Espionage and Lateral Pivoting
In industrial control and defense environments, compromised video surveillance appliances represent dual-threat vectors:
- Physical Security Reconnaissance: Threat actors observe guard patrol schedules, badge-swipe entry points, safe combinations, and sensitive manufacturing operations in high-definition video.
- Internal Network Pivoting: Because security cameras are frequently connected to enterprise switches with PoE (Power over Ethernet), an adversary gaining root access on the camera's Linux operating system can convert the device into an internal network proxy (using tools like
chiselorsocat) to bypass perimeter firewalls and attack Purdue Model Level 2/3 industrial controllers. - Botnet Recruitment: Unpatched IoT camera fleets remain prime targets for Mirai and its variants, weaponizing compromised hardware into massive DDoS botnets.
Vulnerability Matrix for CareCam CM2507
| Identifier | Vulnerability Type | CWE ID | CVSS v3.1 | Technical Impact |
|---|---|---|---|---|
| CVE-2026-88259 | Missing Authentication on RTSP/HTTP | CWE-306 | 7.5 | Unauthenticated capture of live video streams |
| CVE-2026-84398 | Empty Password in ONVIF Service | CWE-258 | 7.5 | Full administrative device management takeover |
| CVE-2026-85497 | Hardcoded Weak Root Hash | CWE-326 | 6.8 | Local privilege escalation via SSH/Telnet |
| CVE-2026-81321 | Cleartext Wi-Fi Credential Storage | CWE-312 | 6.5 | Exfiltration of corporate WPA2 Pre-Shared Keys |
Compensatory Mitigation Playbook & Network Isolation
Because the vendor has not released patched firmware, facilities engineers must immediately enforce compensatory architectural controls aligned with IEC 62443-3-2:
1. Immediate Physical Security VLAN Isolation
Isolate all CareCam cameras into a dedicated, non-routable Surveillance Management VLAN. Prohibit all direct communication between the camera VLAN and general corporate networks or the internet:
# Cisco IOS Switch Configuration: Hardened CCTV VLAN
vlan 400
  name INDUSTRIAL-SURVEILLANCE-CAMERAS

interface range GigabitEthernet1/0/1 - 24
  switchport mode access
  switchport access vlan 400
  spanning-tree portfast
  storm-control broadcast level 5.00

# Access Control List: Block Internet Egress and Inter-VLAN Traversal
ip access-list extended ISOLATE_CCTV_VLAN
  # Allow cameras to stream ONLY to authorized Network Video Recorder (NVR)
  permit tcp 10.40.0.0 0.0.255.255 host 10.40.0.10 eq 554
  permit tcp 10.40.0.0 0.0.255.255 host 10.40.0.10 eq 8899
  # Deny all other outbound traffic (Internet and Internal LAN)
  deny ip 10.40.0.0 0.0.255.255 any log-input
2. Disable Unused Management Ports at Firewall Boundary
Configure network firewalls to drop all traffic targeting TCP ports 23 (Telnet), 8080 (HTTP Alt), and 8899 (ONVIF) originating from unauthorized subnets. Restrict NVR access strictly through dedicated jump hosts with multi-factor authentication.
3. Rotate Wi-Fi Pre-Shared Keys
If any CareCam cameras were previously connected to a corporate or operational Wi-Fi SSID, assume the WPA2/WPA3 passphrase has been compromised. Rotate the network pre-shared key across all access points immediately.
4. Plan Hardware Decommissioning
In accordance with CISA Binding Operational Directives and enterprise risk management standards, organizations should establish a timeline to replace non-responsive vendor IoT hardware with NDAA-compliant (National Defense Authorization Act) camera systems that support signed firmware updates, secure boot, and mandatory password enforcement.