Topic
Amazon Web Services: news, advisories and analysis
18 articles
CyberSecureToday covers Amazon Web Services across 18 articles published between 17 Sep 2026 and 14 Oct 2026. The coverage includes 18 vulnerability advisories. 17 advisories are rated critical or high severity.
Stories on Amazon Web Services most often intersect with Cloud Security, AWS and IAM, with Technology, Cloud & SaaS the most affected sector. The most recent story, “AWS Systems Manager (SSM) Agent OS Command Injection Flaw CVE-2026-87911 Patched”, was published 14 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsCloud & SaaSHighCST Editorial Desk
ThreatsCloud & SaaSHighAWS IAM Identity Center Flaw Left Revoked Session Tokens Active
CST Editorial Desk
ThreatsCloud & SaaSHighAWS Bedrock Guardrails Vulnerability Enables Adversarial Safety Filter Evasion via Unicode Homoglyph Normalization (CVE-2026-80210)
CST Editorial Desk
ThreatsCloud & SaaSCriticalAWS S3 Multi-Region Access Point Flaw Enables IAM Signature Version 4 Authorization Bypass CVE-2026-79787
Daniel Okafor
ThreatsCloud & SaaSHighAWS Systems Manager Agent SSRF Vulnerability Allows Link-Local IMDS Credential Theft CVE-2026-89049
Aisha Noor
ThreatsCloud & SaaSHighAWS Bedrock Agent Runtime Vulnerability Exposes Temporary IAM Credentials CVE-2026-62181
Aisha Noor
ThreatsCloud & SaaSHighAWS Athena ClickHouse Connector Flaw Enables Cross-Account Secrets Manager Extraction
Daniel Okafor
ThreatsCloud & SaaSHighAWS Transform MCP Server Flaw Enables Arbitrary File Overwrites in Agent Workflows
Daniel Okafor
ThreatsCloud & SaaSHighAWS pgcollection Type Confusion Flaw Enables Remote Code Execution in PostgreSQL
CST Editorial Desk
ThreatsCloud & SaaSHighAWS Amazon Connect Salesforce Integration Flaw Enables IAM Privilege Escalation via Lambda
CST Editorial Desk
ThreatsCloud & SaaSHighAmazon ECS Container Agent Flaw Enables Task Boundary Breakout and IAM Role Credential Hijacking
Aisha Noor
ThreatsCloud & SaaSHighAmazon Ion-C Library Recursion Flaw Triggers Cloud Service Stack Exhaustion Crashes CVE-2026-84851
CST Editorial Desk
ThreatsCloud & SaaSHighAmazon OpenSearch SQL Plugin Cursor Deserialization Flaw Enables Remote Code Execution CVE-2026-83497
CST Editorial Desk
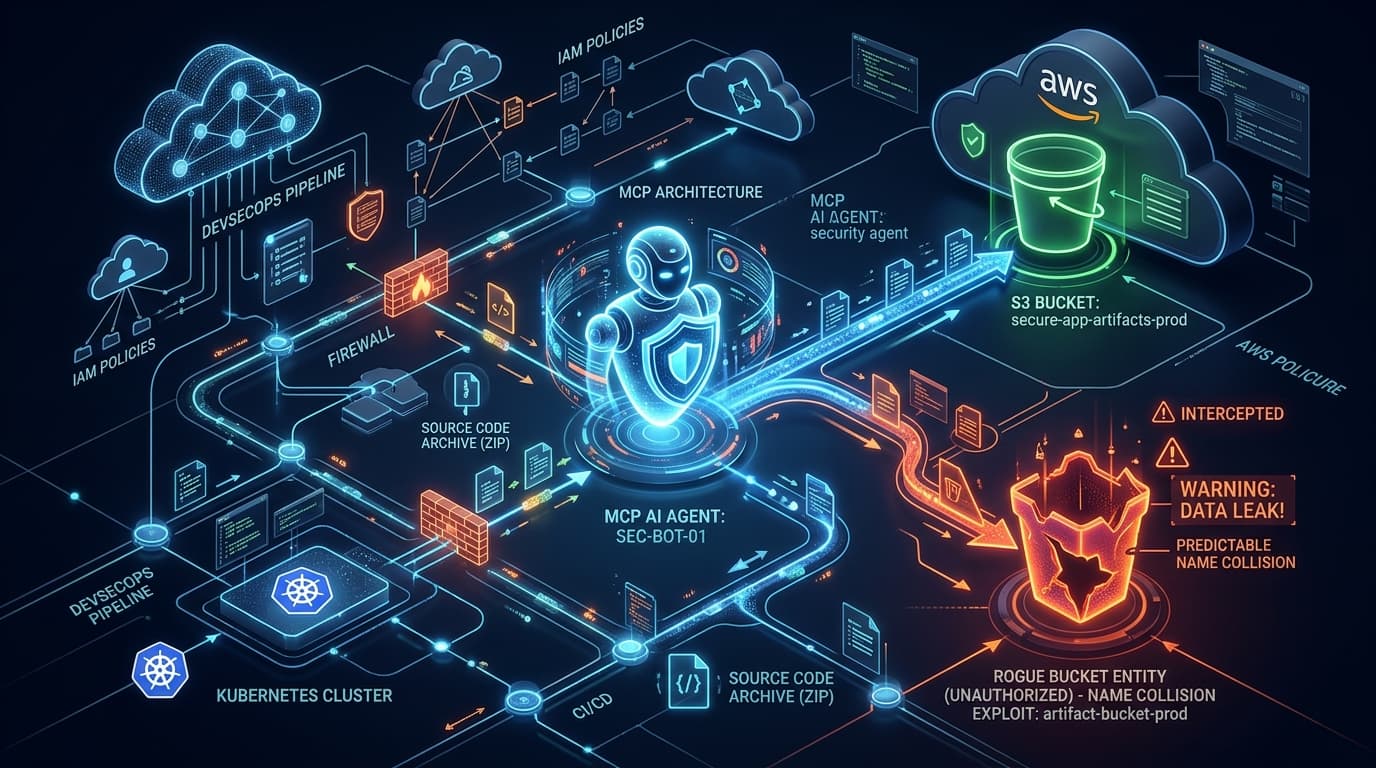
ThreatsCloud & SaaSHighAWS Security Agent, MCP Server Flaws Let S3 Squatters Intercept Source Code
Aisha Noor
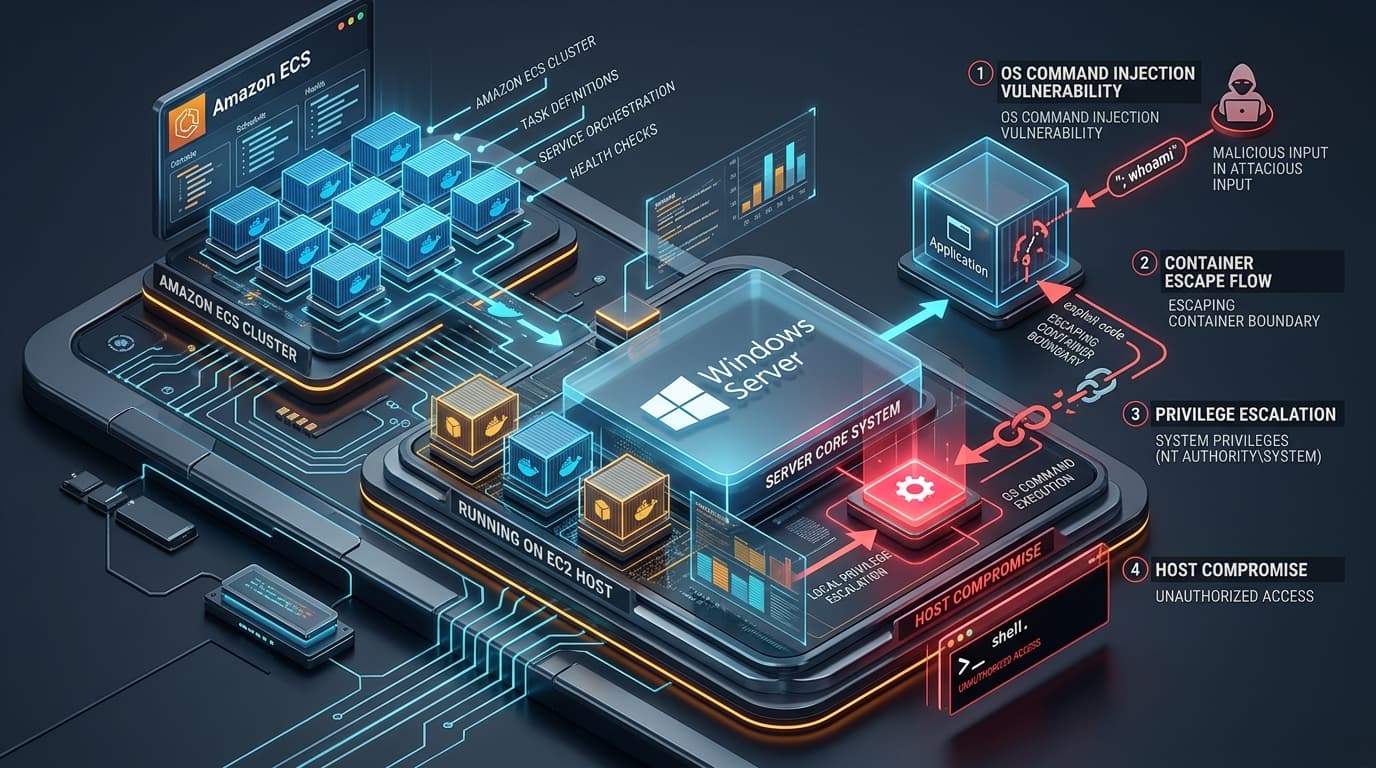
ThreatsCloud & SaaSHighAmazon ECS Agent Flaw CVE-2026-7461 Permits Command Injection and Host Takeover on Windows Clusters
Mei-Lin Chen
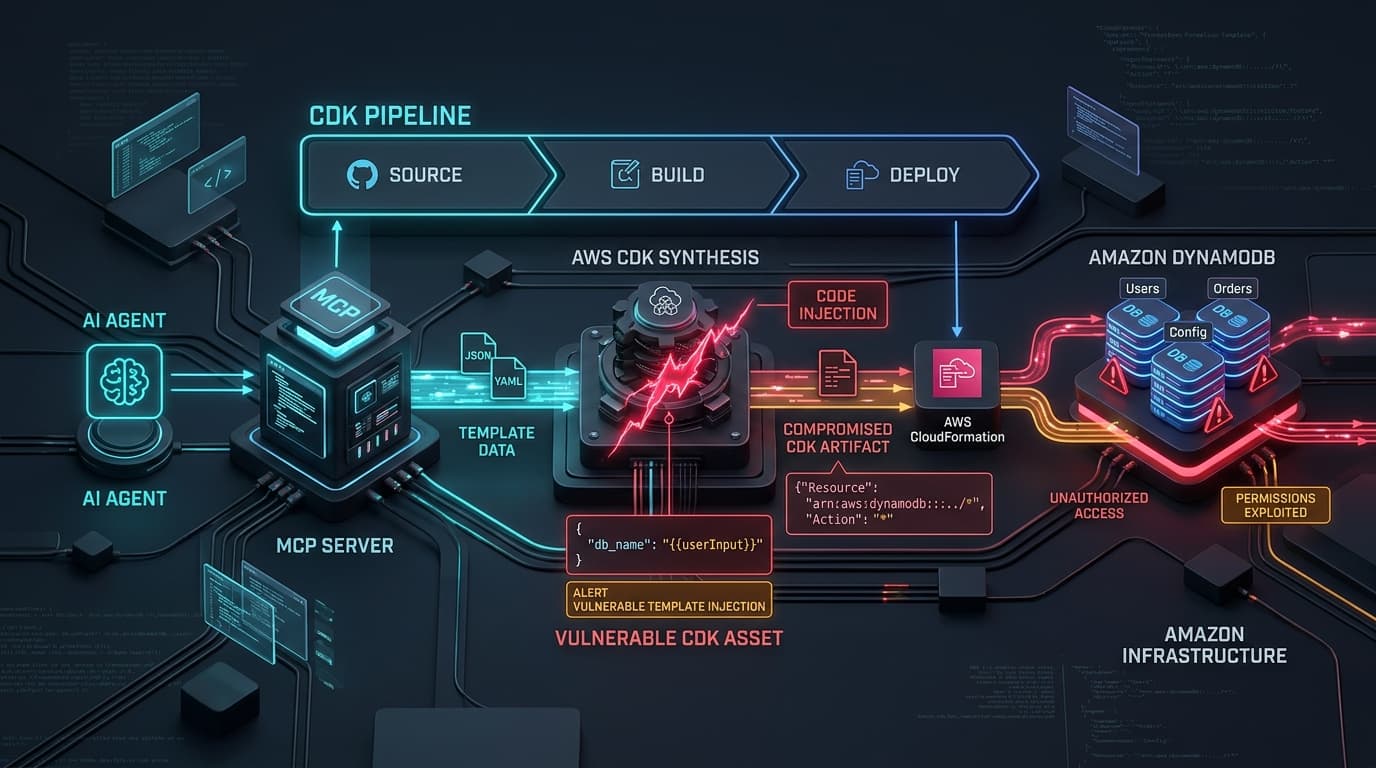
ThreatsCloud & SaaSHighAmazon DynamoDB Model Context Protocol Server Code Injection Flaw Enables Arbitrary Host Execution
CST Editorial Desk
ThreatsCloud & SaaSHighAWS Security Advisory: Linux Kernel vhost vring Cache Corruption Flaw CVE-2026-74580 Patched via Livepatch
Daniel Okafor