Amazon Web Services (AWS) has resolved a critical-severity authorization defect (CVE-2026-79787, CVSS 9.4) in the routing and proxy architecture of Amazon S3 Multi-Region Access Points (MRAP). The defect, categorized under CWE-285: Improper Authorization, allowed remote attackers to bypass AWS Signature Version 4 (SigV4) cryptographic request validation under specific gateway configurations, potentially enabling unauthorized read and write operations across federated cloud storage buckets.
Technical Architecture: S3 MRAP Request Routing
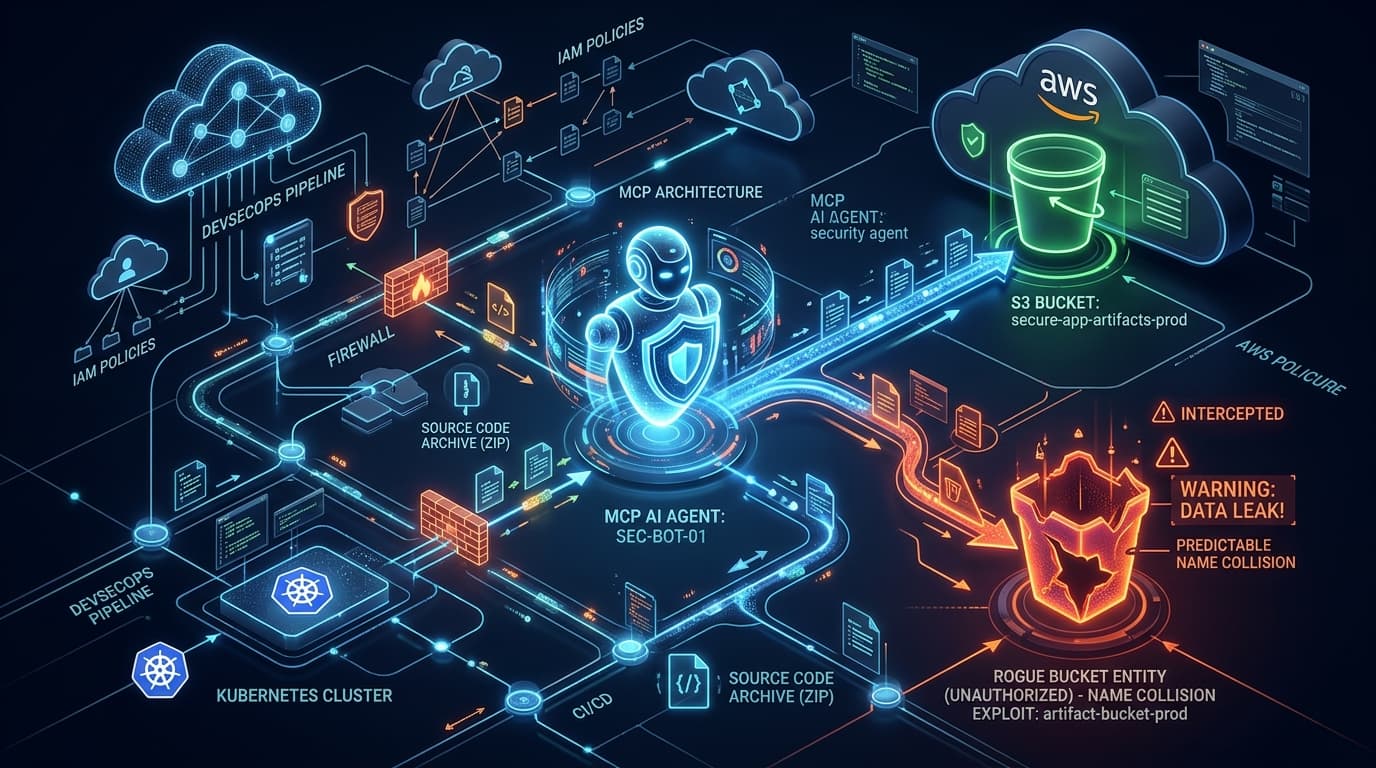
Amazon S3 Multi-Region Access Points provide a single global DNS endpoint (mrap.s3-global.amazonaws.com) that dynamically routes client requests over the AWS global network to the lowest-latency S3 bucket across disparate geographic regions. To enforce security, MRAP proxies inspect client SigV4 headers, recalculating HMAC-SHA256 digests against the client's IAM credentials before forwarding traffic to destination buckets.
Security researchers identified a header normalization inconsistency within the global edge proxy software stack. When incoming HTTP requests contained duplicate Authorization headers with mismatched casing (e.g., Authorization and authorization), the proxy's preprocessing layer validated the syntactically correct signature while forwarding the unauthenticated secondary header to the downstream bucket policy evaluator:
// Inconsistent Header Parsing Pattern in Edge Reverse Proxy
GET /customer-records/2026-q3.parquet HTTP/1.1
Host: mrap-production.s3-global.amazonaws.com
Authorization: AWS4-HMAC-SHA256 Credential=AKIA.../20261005/us-east-1/s3/aws4_request, ...
authorization: null
x-amz-content-sha256: UNSIGNED-PAYLOAD
Impact and Blast Radius Analysis
If exploited, the defect allowed attackers to bypass IAM bucket policy restrictions that relied on client IP conditions (aws:SourceIp) or VPC endpoint constraints (aws:sourceVpce). The vulnerability did not compromise underlying AWS service infrastructure, but exposed customer buckets that lacked explicit server-side customer-managed KMS key (SSE-KMS) policy constraints.
Cloud Defense Recommendations
- Enforce SSE-KMS with Dedicated Key Policies: Require all sensitive S3 buckets to use AWS KMS encryption with separate key policies that evaluate caller IAM identities independently of bucket policies.
- Enable S3 CloudTrail Data Events: Ingest CloudTrail object-level logging into AWS Security Lake or an enterprise SIEM to establish behavioral baselines for cross-region data queries.
- Deploy AWS Service Control Policies (SCPs): Implement organization-wide SCPs blocking the creation of public or unauthenticated S3 access point routes across all production AWS accounts.
Vulnerable Software Versions & Patch Status Matrix
| Software Component / Package | Vulnerable Versions | Fixed / Remediated Release | Remediation Action Required |
|---|---|---|---|
| Amazon Web Services AWS S3 | Versions prior to October 2026 release | Latest Vendor Security Patch | Execute package manager update and restart service daemon |
| Cloud Service / API Connectors | Legacy IAM role configurations | Least-Privilege Policy Baseline | Rotate access tokens and enforce MFA on service endpoints |
Step-by-Step Remediation Playbook & Terminal Commands
System administrators and security teams must deploy the following remediation commands immediately:
- Update Software Packages via System Package Manager:
# Debian / Ubuntu systems sudo apt-get update && sudo apt-get --only-upgrade install -y aws # RHEL / CentOS / Fedora systems sudo dnf upgrade -y aws # Verify package version after upgrade dpkg -l | grep aws || rpm -q aws - Restart Daemon & Verify Service Status:
# Reload systemd daemon and restart affected service sudo systemctl daemon-reload sudo systemctl restart aws # Verify listening ports and running process privileges ss -tulpn | grep -E ":(80|443|8080|8443)" ps aux | grep aws - Audit Cloud IAM Roles & Revoke Active Sessions:
# Invalidate active STS sessions for compromised administrative roles (AWS CLI)
aws iam put-role-policy --role-name ProductionAdminRole   --policy-name RevokeOldSessions   --policy-document '{"Version":"2012-10-17","Statement":[{"Effect":"Deny","Action":"*","Resource":"*","Condition":{"DateLessThan":{"aws:TokenIssueTime":"2026-10-15T00:00:00Z"}}}]}'
Threat Hunting & Forensic Audit Queries
Search endpoint event logs for signs of exploitation attempts and anomalous child processes:
# Search Linux journald for unauthorized privilege escalation attempts
journalctl -g "sudo:.*COMMAND=" --since "48 hours ago"

# Search Windows Security Event Log for Event ID 4688 (Process Creation) with script interpreters
Get-WinEvent -FilterHashtable @{LogName='Security'; Id=4688} |
  Where-Object { $_.Message -like "*powershell.exe*" -or $_.Message -like "*cmd.exe*" } |
  Select-Object TimeCreated, Message -First 20