AWS Cloud
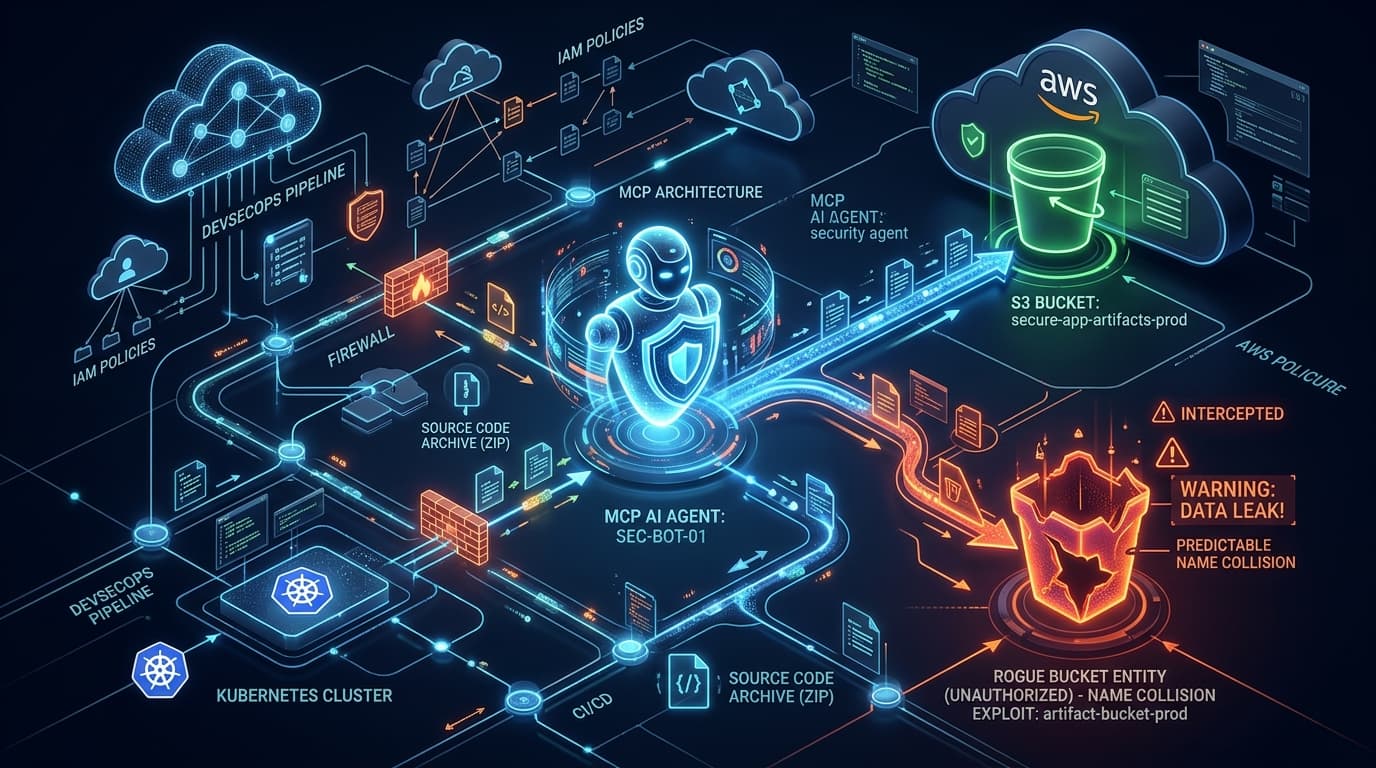
AWS S3 Multi-Region Access Point Flaw Enables IAM Signature Version 4 Authorization Bypass CVE-2026-79787
ThreatsCloud & SaaSCVE-2026-79787Critical
AWS Security Bulletin details an authorization validation defect in S3 Multi-Region Access Point endpoints permitting IAM privilege escalation.
Daniel Okafor8 min read