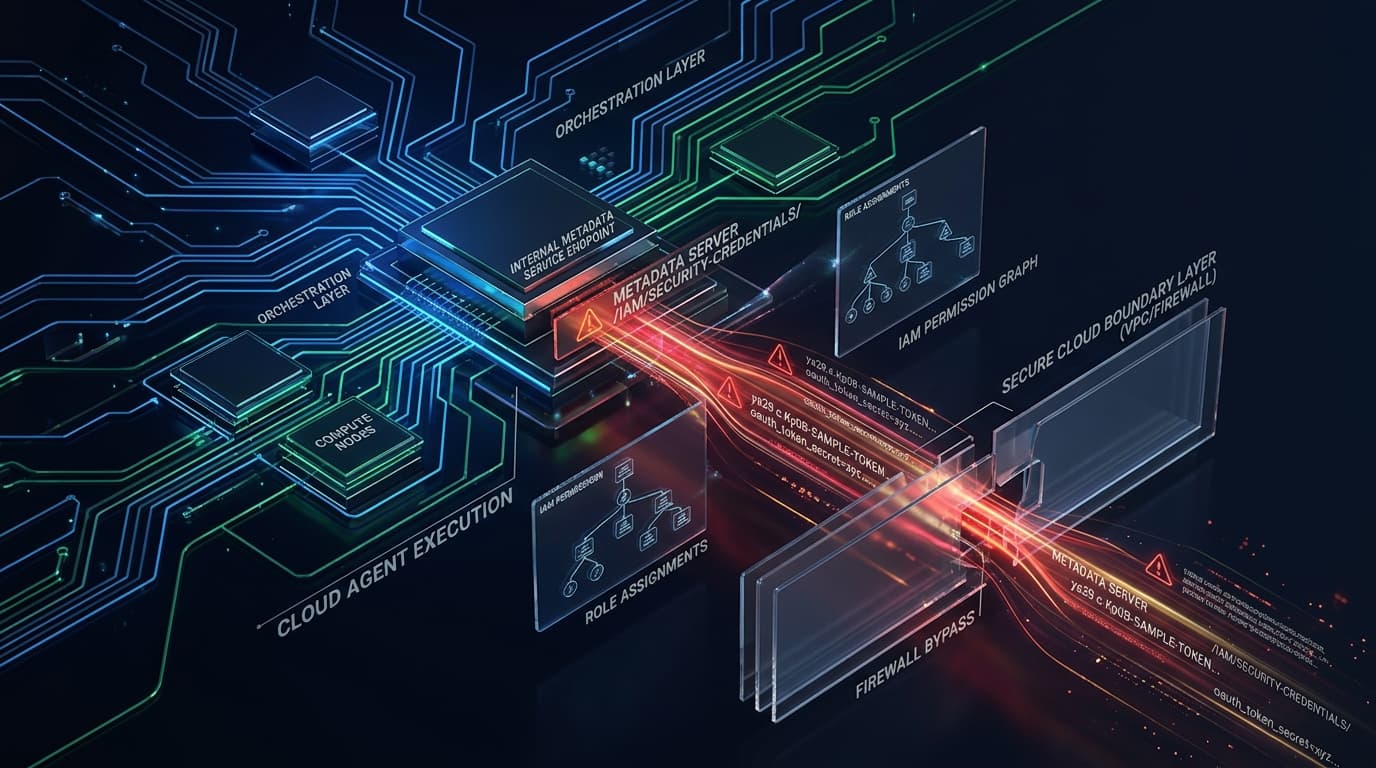
Amazon Web Services (AWS) has released a critical security bulletin resolving a high-severity Server-Side Request Forgery (SSRF) vulnerability (CVE-2026-89049, CVSS 8.5) affecting the open-source amazon-ssm-agent. The flaw allows authenticated IAM principals possessing constrained session permissions to bypass destination denylists and proxy connections directly to the link-local EC2 Instance Metadata Service (IMDS), extracting temporary IAM credentials assigned to the managed node.
Architectural Breakdown: Remote-Host Port Forwarding in SSM Agent
The AWS Systems Manager Agent executes as a root or system-level daemon across EC2 instances, on-premises virtual machines, and hybrid nodes. Through the AWS-StartPortForwardingSessionToRemoteHost SSM document, administrators can establish multiplexed TLS tunnels through the Systems Manager gateway to access internal corporate databases, administration panels, and auxiliary microservices located within isolated Virtual Private Clouds (VPCs).
To prevent operators from turning the port-forwarding tunnel into an arbitrary intranet proxy or accessing sensitive local interfaces, the agent enforces a destination validation routine designed to drop connections targeting loopback addresses (127.0.0.1) and cloud link-local subnets (169.254.0.0/16).
Root Cause Analysis: Equivalent IP Encoding Bypass (CWE-918)
According to AWS engineering documentation, the vulnerability is classified under CWE-918: Server-Side Request Forgery (SSRF). Prior to version 3.3.4851.0, the validation parser performed canonical string comparisons against dotted-quad IPv4 strings rather than normalizing destination addresses into raw binary socket primitives.
Adversaries supplied alternate integer representations, hex-encoded values, or decimal integer encodings of the link-local metadata address (e.g., 2852039166 or 0xA9.0xFE.0xA9.0xFE). The denylist evaluator failed to identify the payload as 169.254.169.254, allowing the socket connection to proceed:
# Vulnerable IP comparison logic in amazon-ssm-agent port forwarding module
func isDestinationDenied(host string) bool {
    // INSECURE: Simple string matching failed on alternative numeric encodings
    deniedHosts := []string{"169.254.169.254", "127.0.0.1", "localhost"}
    for _, d := range deniedHosts {
        if host == d {
            return true
        }
    }
    return false
}
Once the tunnel established connectivity with port 80 on the metadata service, the attacker could query /latest/meta-data/iam/security-credentials/<role-name>, exfiltrating the instance's active AccessKeyId, SecretAccessKey, and Token to achieve persistent cloud persistence outside the virtual machine.
Vulnerability Assessment & CVSS Vector
| Security Parameter | Vulnerability Specification |
|---|---|
| Vulnerability Identifier | CVE-2026-89049 |
| CVSS v3.1 Base Score | 8.5 (High) - CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:L/A:N |
| Common Weakness Enumeration | CWE-918 (Server-Side Request Forgery) |
| Affected Software | amazon-ssm-agent < v3.3.4851.0 |
| Impact Scope | Link-Local IMDS Credential Theft, Cross-Account Workload Impersonation |
Defensive Playbook & Mitigation Directives
Cloud security operations and infrastructure teams should immediately execute the following defensive measures:
1. Automated Fleet Upgrade via Systems Manager
Deploy the updated SSM agent across all EC2 managed instances using the AWS-UpdateSSMAgent automation document:
# AWS CLI: Execute SSM Agent update across all Linux and Windows managed instances
aws ssm send-command   --document-name "AWS-UpdateSSMAgent"   --targets '[{"Key":"InstanceIds","Values":["*"]}]'   --parameters '{"allowDowngrade":["false"]}'   --region us-east-1
2. Enforce IMDSv2 Hop Limit Restrictions
Enforce IMDSv2 and configure the metadata HTTP hop limit to 1. This prevents requests from traversing network bridges or tunnel interfaces:
# AWS CLI: Enforce IMDSv2 and restrict HTTP hop limit to 1
aws ec2 modify-instance-metadata-options   --instance-id i-0123456789abcdef0   --http-tokens required   --http-put-response-hop-limit 1   --http-endpoint enabled
3. Restrict Port Forwarding Document Permissions
Audit IAM policies and attach condition keys restricting which users can invoke the AWS-StartPortForwardingSessionToRemoteHost document.