Executive Lead: IAM Service Account Token Exposure in Enterprise Cloud Agents
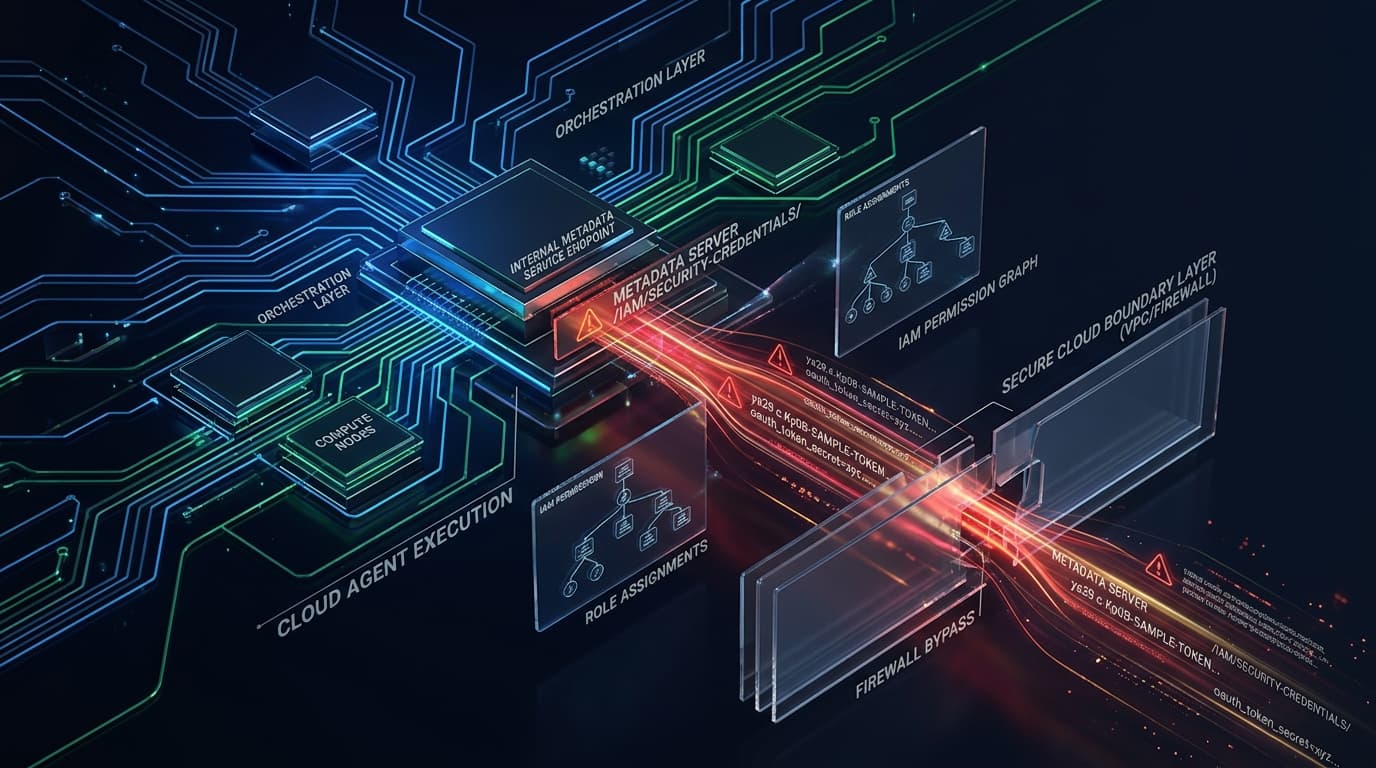
Google Cloud has published a security bulletin disclosing a high-severity vulnerability, cataloged as CVE-2026-19486, in the Gemini Enterprise Agent Platform App Builder (formerly Vertex AI Search and Conversation / Generative AI App Builder). Rated with a Common Vulnerability Scoring System (CVSS v4.0) base score of 8.7 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:L/VA:N/SC:H/SI:L/SA:N), the defect enables remote, unauthenticated attackers to induce enterprise AI agent applications to execute Server-Side Request Forgery (SSRF) requests against Google Cloud's internal instance metadata services.
By exploiting this flaw, threat actors could extract active OAuth 2.0 access tokens assigned to the Compute Engine default service account (or custom attached service accounts) backing the agent runtime. Because default Compute Engine service accounts frequently inherit the overly permissive roles/editor IAM role across legacy Google Cloud projects, successful token harvesting enables adversaries to list Cloud Storage buckets, query BigQuery data warehouses, manipulate Cloud Run deployments, and pivot laterally throughout the organization's cloud environment.
Technical Root Cause & CWE-918 Dissection: Flawed Connector URL Validation
Under CWE-918: Server-Side Request Forgery (SSRF), the defect occurred within the tool integration and retrieval connector subsystem of the Gemini Enterprise Agent Platform App Builder.
When developers configure conversational agents or multi-agent workflows in App Builder, the platform allows agents to call external enterprise tools, webhooks, and REST endpoints to retrieve live business data (e.g., querying CRM APIs, knowledge bases, or internal inventory endpoints). During agent runtime execution, dynamic parameters generated by LLM reasoning or direct user inputs are formatted into outbound HTTP requests.
In container runtime templates deployed between October 11, 2025, and June 1, 2026, the webhook dispatch proxy failed to properly sanitize destination URLs when processing redirected requests or custom schema endpoints. Specifically, the proxy failed to enforce the mandatory Metadata-Flavor: Google request header boundary when handling client-influenced redirection chains:
// Conceptual Flaw in App Builder Outbound Request Proxy
func DispatchAgentToolRequest(toolConfig *ToolEndpoint, userParams map[string]string) (*HTTPResponse, error) {
    targetURL := toolConfig.BaseURL + ConstructQuery(userParams)

    // SECURITY DEFECT: HTTP client follows redirects automatically without
    // stripping headers or re-evaluating whether the redirected target resolves
    // to the internal metadata IP (169.254.169.254 / metadata.google.internal)
    client := &http.Client{
        CheckRedirect: func(req *http.Request, via []*http.Request) error {
            // Fails to validate target host against internal link-local IP
            return nil // Follows redirect blindly
        },
    }

    req, _ := http.NewRequest("GET", targetURL, nil)
    // Custom headers injected by tool integration proxy leaked to redirected host
    return client.Do(req)
}
An attacker could designate an external webhook endpoint under their control that returned an HTTP 302 redirect pointing to:
http://metadata.google.internal/computeMetadata/v1/instance/service-accounts/default/token
Because the initial request generated by App Builder already included legitimate internal Google headers, the redirected request traversed the local virtual machine network bridge to the Google Cloud metadata server. The metadata server returned the active OAuth token, which the agent runtime swallowed and reflected in downstream conversational outputs or execution logs.
Architecture & Attack Trajectory Diagram
The diagram below illustrates how an external adversary leverages tool execution redirects to harvest Google Cloud IAM credentials:
+-----------------------------------------------------------------------------------+
|                        CVE-2026-19486 GOOGLE CLOUD SSRF ATTACK                    |
+-----------------------------------------------------------------------------------+
|                                                                                   |
|  [ Remote Attacker ]                                                              |
|          |                                                                        |
|          |  1. Invokes Gemini Agent with input triggering webhook call            |
|          v                                                                        |
|  +-----------------------------------------------------------------------------+  |
|  | Gemini Enterprise Agent Platform App Builder (Customer GCP Project)        |  |
|  |                                                                             |  |
|  |   [ Agent Runtime Container ]                                               |  |
|  |          |                                                                  |  |
|  |          |  2. Sends outbound HTTP GET to attacker-controlled server        |  |
|  |          v                                                                  |  |
|  |  +-----------------------------------------------------------------------+  |  |
|  |  | Attacker Webhook Server (https://attacker-c2.example/redirect)        |  |  |
|  |  |   - Responds: HTTP 302 Found                                          |  |  |
|  |  |   - Location: http://metadata.google.internal/.../default/token       |  |  |
|  |  +-----------------------------------------------------------------------+  |  |
|  |          |                                                                  |  |
|  |          |  3. Client follows redirect internally inside compute host       |  |
|  |          v                                                                  |  |
|  |   [ Google Compute Engine Metadata Service (169.254.169.254) ]              |  |
|  |          |                                                                  |  |
|  |          |  4. Validates Metadata-Flavor header and issues OAuth 2.0 token  |  |
|  |          v                                                                  |  |
|  |   [ Access Token Returned: ya29.c.Kp0B... (Default Compute Engine SA) ]     |  |
|  +----------|------------------------------------------------------------------+  |
|             |                                                                     |
|             |  5. Token reflected in Agent Response or Log Telemetry              |
|             v                                                                     |
|  [ Attacker Authenticates directly against Google Cloud Resource Manager APIs ]   |
|                                                                                   |
+-----------------------------------------------------------------------------------+
Blast Radius: GCP IAM Compromise & Cloud Lateral Movement
The blast radius of a compromised Compute Engine service account token depends heavily on the project's IAM posture:
- Default Compute Engine Service Account Exposure: By default, Google Cloud creates a service account formatted as
PROJECT_NUMBER-compute@developer.gserviceaccount.com. In many production environments where least-privilege principles are not strictly enforced, this account retains the broadEditorrole, granting write access to storage, compute instances, and networking. - Sensitive Data Exfiltration: With a valid Bearer token, the attacker uses the Google Cloud CLI or REST APIs from an external workstation to download confidential assets stored in Cloud Storage (GCS) buckets, dump BigQuery tables, or access Secret Manager payloads.
- Persistence & Privilege Escalation: Attackers can create new service account keys, grant additional IAM permissions, or deploy rogue Cloud Functions to establish persistent out-of-band access.
Remediation Guidance & Mandatory Customer Actions
Google patched the underlying App Builder container runtime template on June 1, 2026. However, because deployed agent instances run immutable container images locked to the build timestamp, customers must perform manual application redeployments.
1. Mandatory Redeployment Workflow
Organizations with Gemini Enterprise Agent Platform App Builder instances created or updated between October 11, 2025, and June 1, 2026, must redeploy their applications immediately:
- Navigate to the Google Cloud Console -> Agent Builder -> Apps.
- Select each active application and review the deployment history.
- Trigger a Redeploy to ensure the container runtime pulls the patched base image containing the redirect validation fix.
- Alternatively, execute the redeployment via the Google Cloud CLI or Terraform pipeline.
# Google Cloud CLI: Trigger app rebuild and deployment update
gcloud alpha discoveryengine apps update YOUR_APP_ID   --location=global   --display-name="Production Support Agent"   --project=enterprise-cloud-prod-1029
2. Enforce Service Account Least-Privilege & Disable Default Accounts
Eliminate reliance on the default Compute Engine service account across your Google Cloud projects. Bind dedicated, least-privilege service accounts with minimal roles:
# Create dedicated, constrained service account for AI agents
gcloud iam service-accounts create sa-gemini-agent-prod   --description="Constrained service account for Gemini App Builder"   --display-name="Gemini Agent Service Account"

# Grant strictly necessary role (e.g., Discovery Engine User)
gcloud projects add-iam-policy-binding enterprise-cloud-prod-1029   --member="serviceAccount:sa-gemini-agent-prod@enterprise-cloud-prod-1029.iam.gserviceaccount.com"   --role="roles/discoveryengine.user"
3. Organization Policy Constraints for Metadata Protection
Deploy Google Cloud Organization Policies to disable default service account creation and restrict access scopes:
# Enforce Org Policy: Disable automatic role grants for default service accounts
gcloud resource-manager org-policies enable-enforce   iam.automaticIamGrantsForDefaultServiceAccounts   --project=enterprise-cloud-prod-1029

# Require Shielded VM / Secure Boot to prevent runtime metadata tampering
gcloud compute instances update INSTANCE_NAME   --shielded-secure-boot   --shielded-vtpm
4. Cloud Audit Logs Hunting Query
Security teams should inspect Google Cloud Audit Logs in Cloud Logging or BigQuery to identify token usage originating from unexpected non-cloud IP addresses:
-- Google Cloud Logging Query: Detect Service Account API Calls from External IPs
protoPayload.authenticationInfo.principalEmail=~".*compute@developer.gserviceaccount.com"
AND protoPayload.requestMetadata.callerIp!~"^35."
AND protoPayload.requestMetadata.callerIp!~"^10."
AND protoPayload.requestMetadata.callerIp!~"^172."
AND protoPayload.requestMetadata.callerIp!~"^192.168."
AND severity>=NOTICE