Advisory Overview
Amazon Web Services (AWS) has remediated CVE-2026-80210 (CVSS score 7.4), a high-severity security filter evasion vulnerability in Amazon Bedrock Guardrails. The managed service provides configurable safety guardrails—enforcing topical filters, toxic language thresholds, and PII anonymization—across foundation models including Claude, Llama 3, and Amazon Titan.
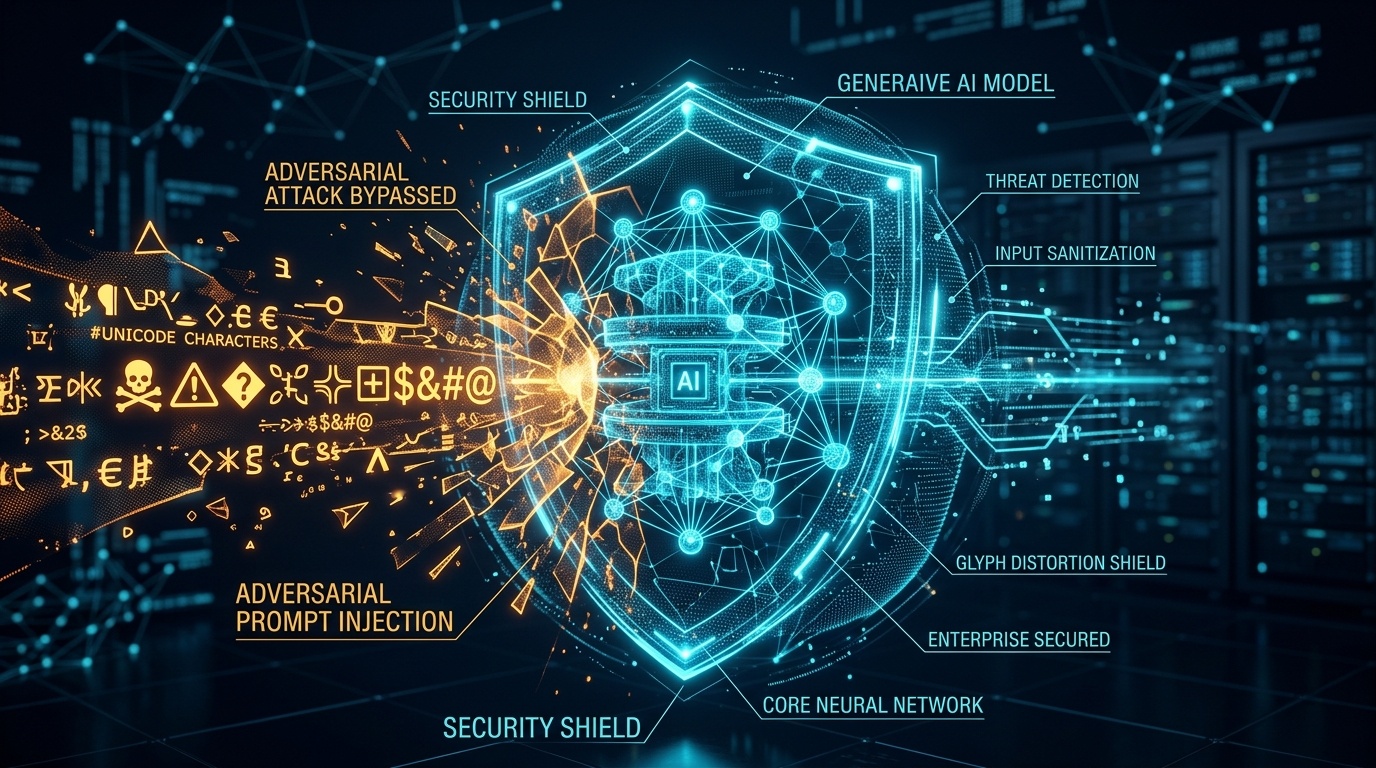
The vulnerability permitted attackers to execute indirect prompt injection or bypass content restrictions by embedding visually identical Unicode homoglyphs (such as Cyrillic and Cherokee characters substituting Latin glyphs) within model input prompts, evading the regex and embedding similarity classifiers.
Root Cause: Discrepancy Between Guardrail Parser & Model Tokenizer
The flaw resulted from asymmetric normalization between the Guardrails pre-processing engine and the downstream foundation model tokenizer:
| Vulnerability Attribute | Technical Parameter |
|---|---|
| Vulnerability ID | CVE-2026-80210 |
| CWE Classification | CWE-172 (Encoding Error) / CWE-693 (Protection Mechanism Failure) |
| CVSS v3.1 Base Score | 7.4 (High) - CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:N |
| Affected Service | Amazon Bedrock Guardrails (all API endpoints prior to October 2026 patch) |
| Remediation Scope | Global cloud-side rollout across all AWS commercial and GovCloud partitions |
The Guardrails engine performed standard NFC (Normalization Form Canonical Composition) parsing, which leaves visually indistinguishable homoglyphs intact. However, the downstream Byte-Pair Encoding (BPE) tokenizers used by foundation models decomposed these characters into subword representations that retained full semantic context, causing the LLM to follow the instructions while Guardrails judged the prompt compliant.
Adversarial Exploitation Scenarios
Researchers demonstrated two high-impact bypass paths in enterprise production deployments:
- Sensitive Data Filter Evasion: Replacing ASCII letters with Cyrillic equivalents allowed prompts soliciting proprietary source code, credentials, and API keys to traverse Guardrails without triggering PII redacting masks.
- System Prompt Overrides: Combining invisible zero-width spaces with homoglyphic instruction keywords (such as
ІgnоrеorSystеm) bypassed topical boundaries, permitting model jailbreaks in customer-facing support agents.
Remediation & LLM Security Playbook
While AWS has deployed automated NFKC (Normalization Form Compatibility Composition) and confusable-string detection on the managed infrastructure, enterprise AI engineering teams should adopt the following controls:
- Client-Side Input Canonicalization: Pre-process all user inputs using strict NFKC normalization libraries (e.g., Python's
unicodedata.normalize('NFKC', text)) prior to passing payloads to cloud APIs. - Implement Multi-Tiered Guardrail Checks: Layer prompt inspection across both input pre-flight and model output post-flight checks to catch anomalous responses before they reach end users.
- Red Team Evaluation for Confusables: Incorporate Unicode confusable fuzzing into continuous automated red-teaming pipelines for production LLM deployments.