Active ExploitArista VeloCloud Orchestrator Zero-Day Exploited to Hijack SD-WAN Edge Gateways
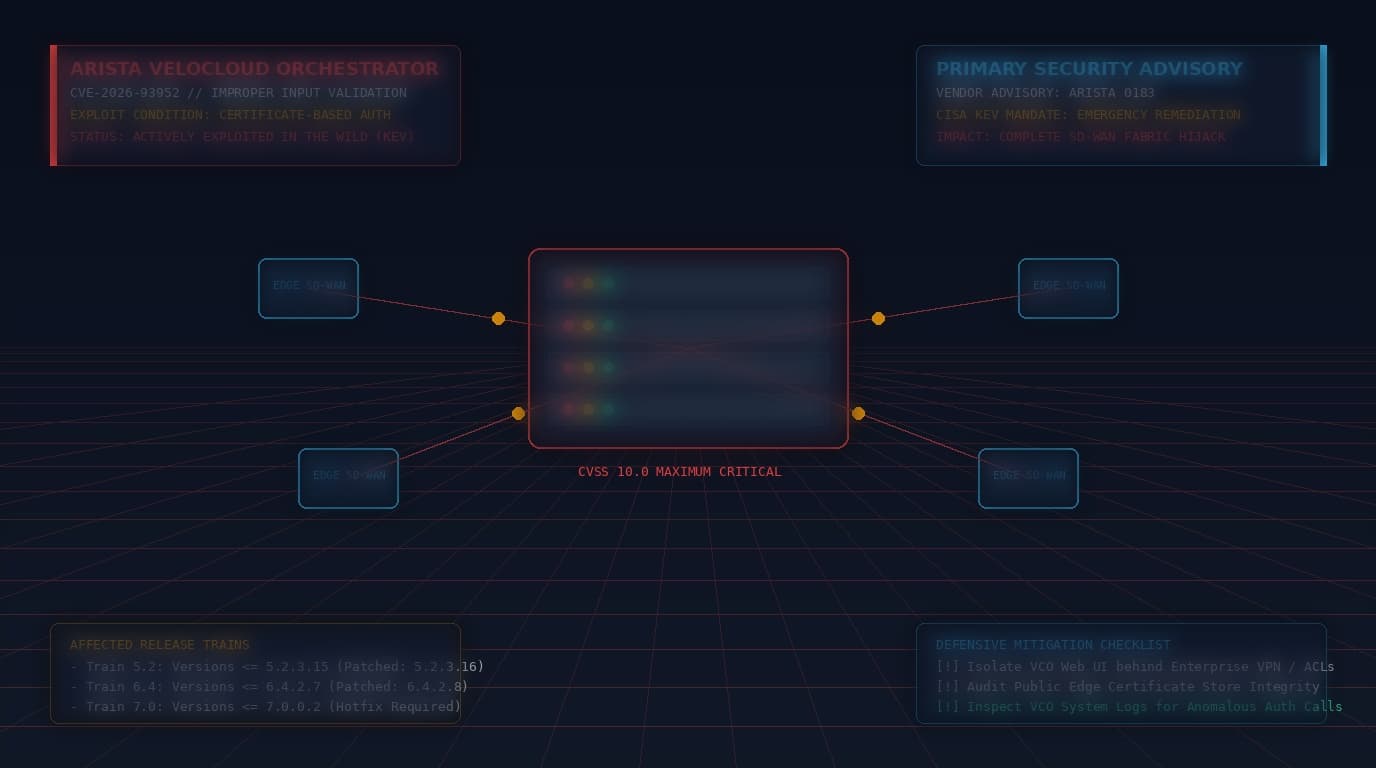
Arista confirms active in-the-wild exploitation of CVSS 10.0 CVE-2026-93952, allowing unauthenticated attackers to hijack on-prem VeloCloud Orchestrators.
1,062 articles
Active ExploitArista confirms active in-the-wild exploitation of CVSS 10.0 CVE-2026-93952, allowing unauthenticated attackers to hijack on-prem VeloCloud Orchestrators.
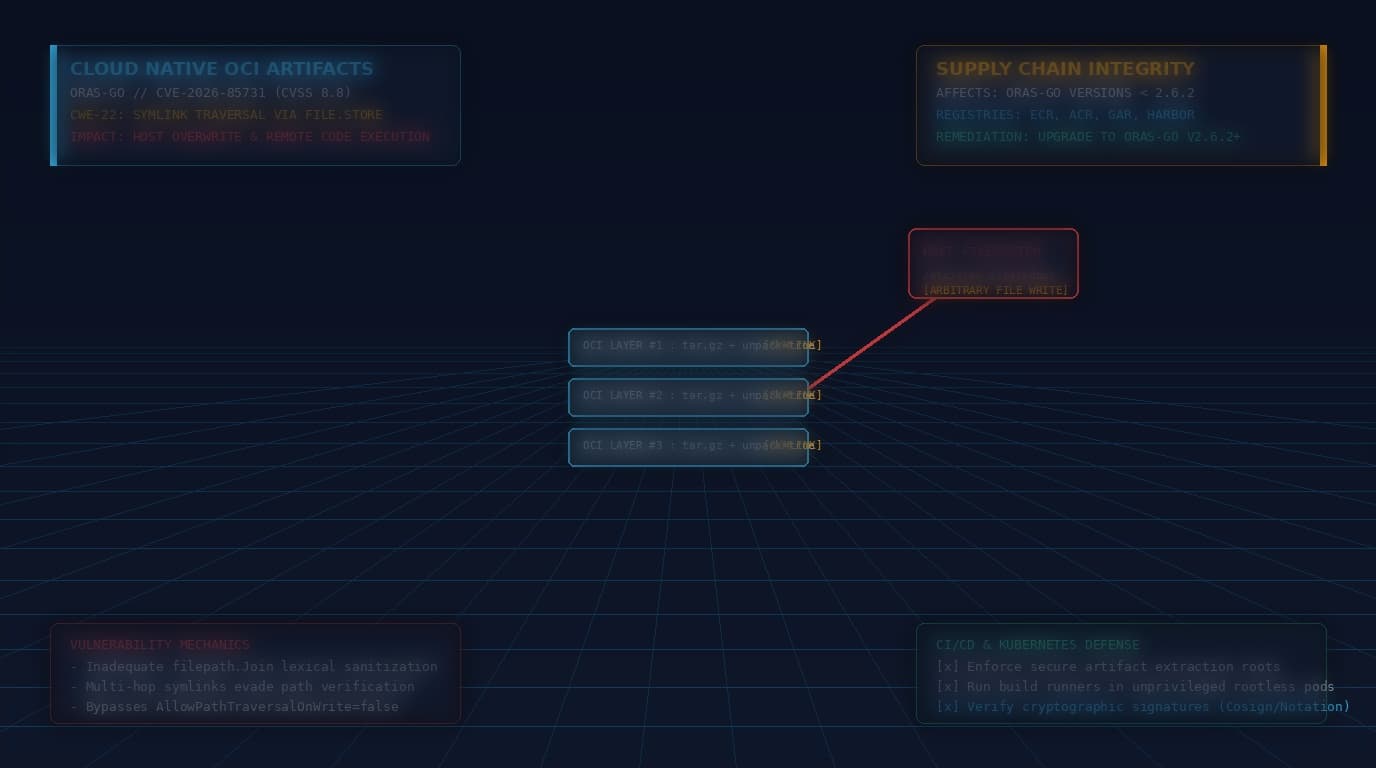
KubernetesA high-severity CVSS 8.8 path traversal vulnerability in oras-go allows malicious OCI container artifacts to escape extraction roots and execute arbitrary code.
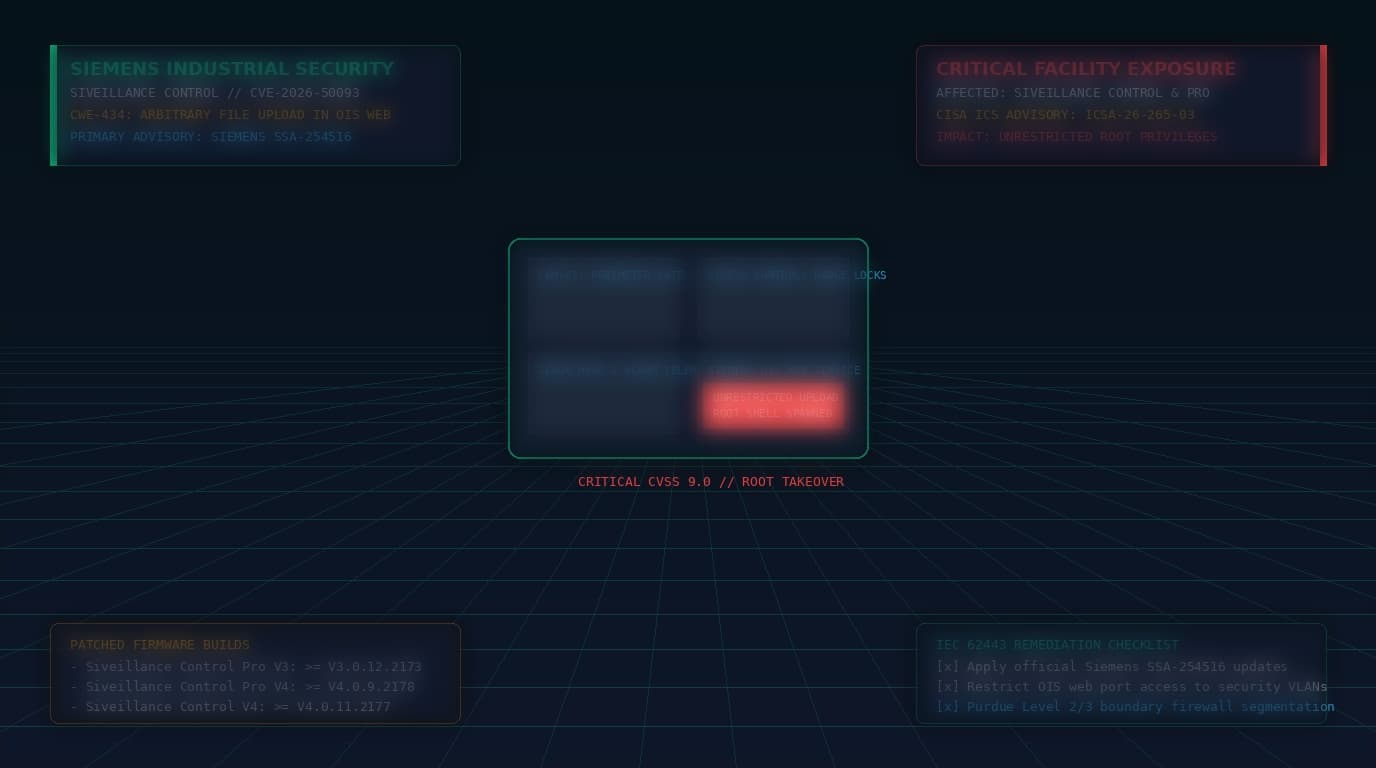
OT / SCADASiemens patches critical CVSS 9.0 flaw CVE-2026-50093 in Siveillance Control OIS web service, enabling unauthenticated remote attackers to obtain root privileges.
Threat IntelF5 confirms active zero-day exploitation of CVE-2026-94127, a critical heap buffer overflow in BIG-IP APM OAuth gateways allowing unauthenticated remote code execution.
MicrosoftGoogle Cloud remediates critical GCP-2026-058 flaw in GKE Multi-Cloud APIs where missing project checks enabled unauthorized cluster registration and IAM impersonation.
MicrosoftSecurity researchers demonstrate BragJack prompt forcing attacks against Chrome and Edge, hijacking agentic AI control planes to exfiltrate files and spy via camera.
OT / SCADACISA warns of CVE-2026-88020 in OpenPLC Runtime v3 web interface, allowing attackers to hijack operator sessions and manipulate physical industrial processes.
Threat IntelCISA issues advisory for CareCam CM2507 IP cameras detailing unauthenticated video streaming, empty ONVIF passwords, and hardcoded root hashes risking facility surveillance.
Threat IntelCloudflare and OpenNext patch high-severity flaw CVE-2026-3125, where path normalization bypasses allow attackers to trigger SSRF and extract private Next.js cache assets.
OT / SCADASiemens and CISA issue advisory ICSA-26-258-07 for CVE-2026-58113 in Teamcenter PLM, where reflected XSS in authentication redirects allows remote attackers to hijack CAD sessions.
AWS CloudAWS resolves high-severity vulnerability CVE-2026-18394 in Strands Agents Tools, where indirect prompt injection forces AI agents to exfiltrate bearer credentials via malicious proxy parameters.
AWS CloudAWS patches medium-severity flaw CVE-2026-89090 in AWS SDK for Go v2, where malformed event stream response frames trigger unrecovered runtime panics and service crashes.
Threat IntelCISA advisory ICSA-26-260-01 details hardcoded MQTT credentials across Bransys ELD telematics units, allowing remote adversaries to eavesdrop on live freight telemetry.
Active ExploitZyxel patches actively exploited stack buffer overflow flaw CVE-2026-7273 in GS1900 smart switches, enabling unauthenticated LAN attackers to execute arbitrary code.
Threat IntelCritical path traversal vulnerability CVE-2026-37007 in CrewAI FileWriterTool allows autonomous agents to be manipulated into executing arbitrary code on host systems.
Threat IntelOracle's Critical Security Patch Update fixes maximum-severity CVSS 10.0 flaw CVE-2026-83021 in WebLogic Server Core enabling unauthenticated remote takeover.
MicrosoftMicrosoft patches important command injection flaw CVE-2026-83948 in Azure CLI, requiring customer updates to prevent remote code execution in CI/CD pipelines.
OT / SCADACISA and Rockwell Automation issue advisory ICSA-26-244-03 for ControlLogix and CompactLogix PLCs where CIP message parsing flaws trigger fatal controller crashes.
Threat IntelSecuronix uncovers TASK#STOMP campaign leveraging Living-off-the-Land VBScript stagers, masqueraded Scheduled Tasks, and resilient dual-PowerShell backdoors.
Threat IntelCritical code validation bypass flaw CVE-2026-0768 in Langflow AI orchestration platform allows unauthenticated remote attackers to execute arbitrary system commands.
Check PointHigh-severity vulnerability CVE-2026-50195 in containerd allows privileged containers to poison the host image cache via CRI Checkpoint API tar archive injection.
OT / SCADASiemens issues advisory SSA-330084 for Desigo CC building management systems where improper input validation in graphics files allows arbitrary script execution.
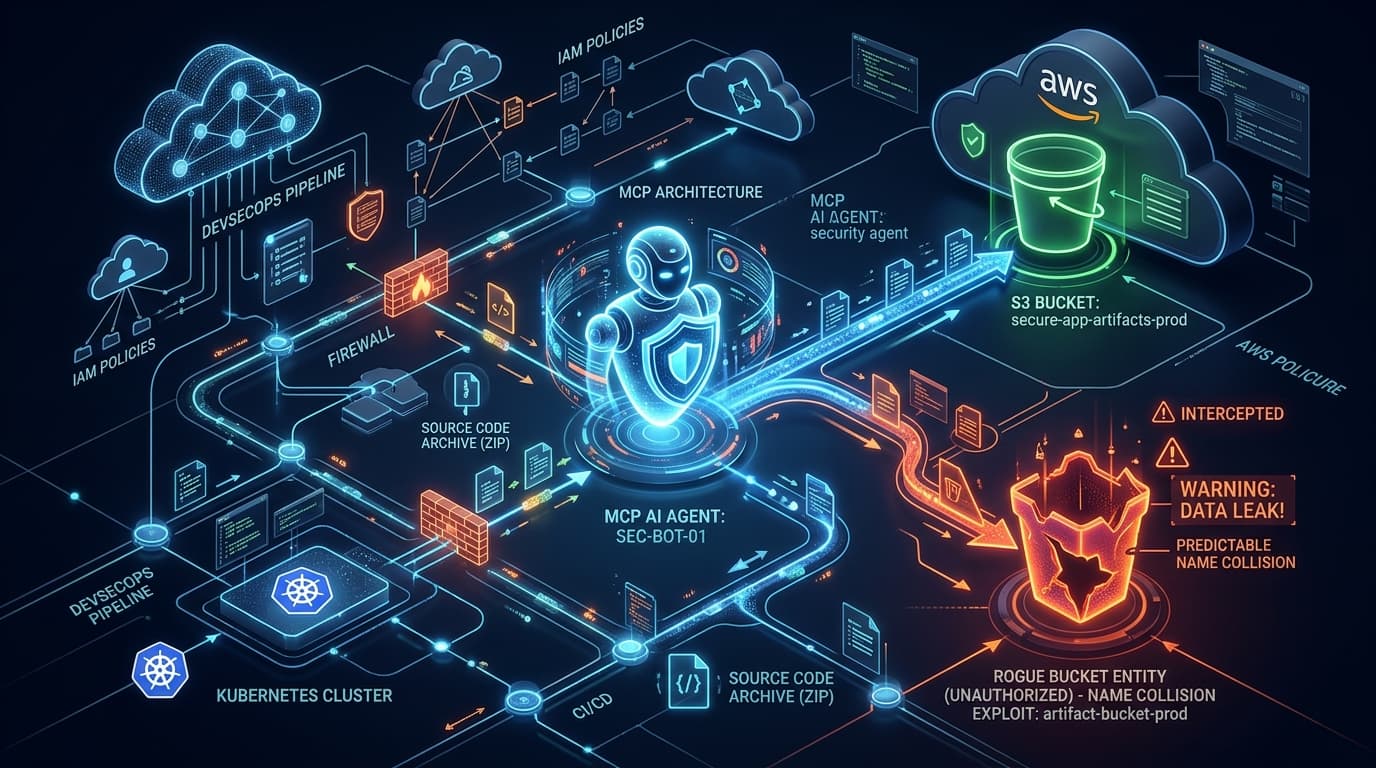
AWS CloudAWS patches vulnerabilities CVE-2026-87912 and CVE-2026-87913 in DevSecOps security agents and Model Context Protocol servers where predictable bucket names permit source code theft.
Threat IntelCritical CVSS 9.1 flaw CVE-2026-48746 in vLLM allows unauthenticated remote attackers to bypass API key verification and access model completions due to URL normalization defects.