Executive Lead: Perimeter Edge Switches Weaponized in Active Intrusions
The Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity vulnerability tracked as CVE-2026-7273 to its Known Exploited Vulnerabilities (KEV) catalog. The defect affects the widely deployed Zyxel GS1900 series of smart managed switches, standard networking infrastructure utilized across small-to-medium enterprises, corporate branch offices, and distributed operational technology (OT) facilities.
Assigned a CVSS v3.1 base score of 8.8 High (CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H), the vulnerability is a stack-based buffer overflow located within the switch's embedded web management Common Gateway Interface (CGI) program. Incident response telemetry confirms that threat actors, initial access brokers, and automated Mirai-derived botnet variants are actively weaponizing the defect. By transmitting specially crafted HTTP/HTTPS requests to the switch's web administration service, unauthenticated network-adjacent attackers can execute arbitrary system commands with root privileges, achieving complete control over local network routing, VLAN isolation perimeters, and traffic mirroring.
Technical Root Cause: Stack Memory Corruption in Web CGI Handler
The Zyxel GS1900 switch family runs a customized Linux-based embedded operating system featuring a lightweight HTTP web daemon for device configuration. When processing administrative sessions or status queries, incoming HTTP requests are dispatched to native compiled C binaries in the /cgi-bin/ path.
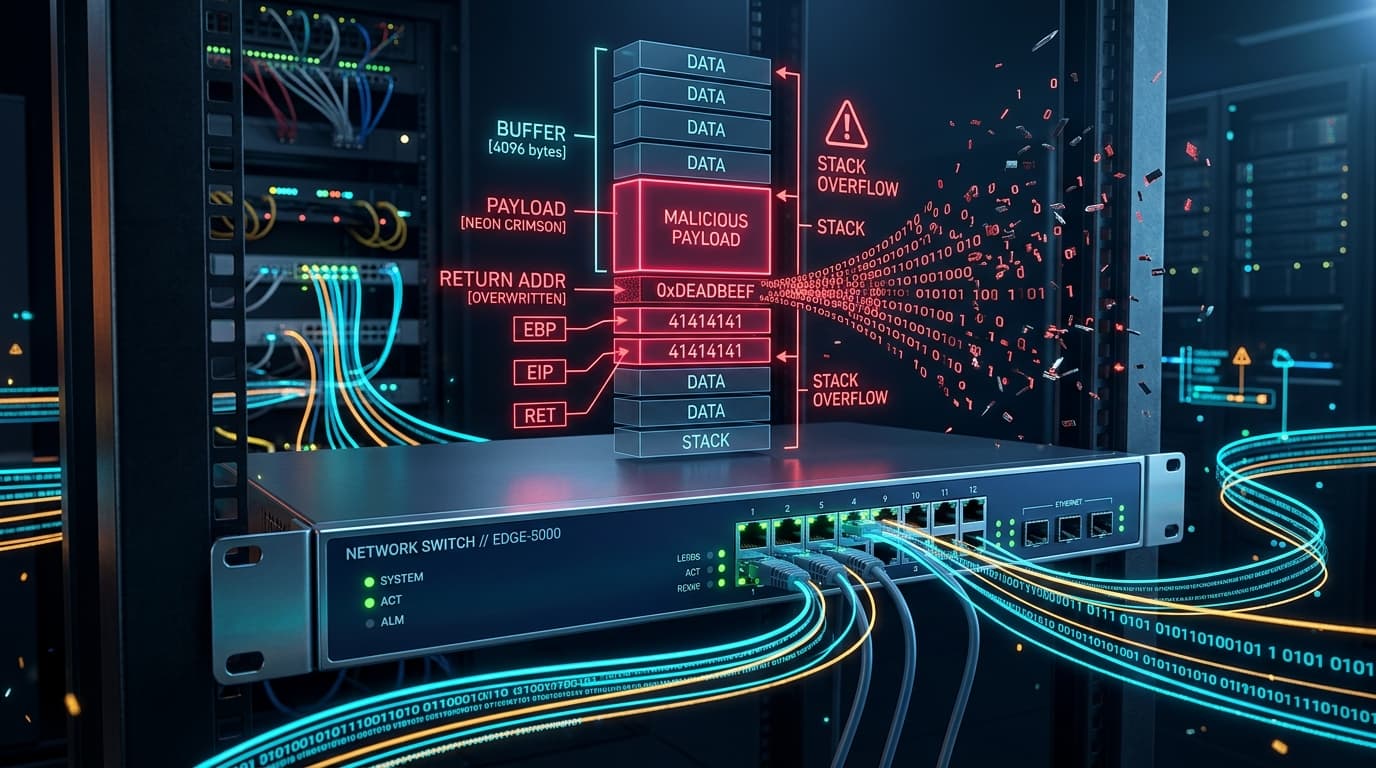
The vulnerability manifests in the request parsing routine responsible for unpacking incoming HTTP request headers and form-data parameters. The program copies user-supplied string data into a fixed-length local stack buffer using an unsafe strcpy() or unconstrained sprintf() function without validating whether the input string exceeds the designated memory boundary:
// Decompiled representation of vulnerable CGI parsing routine
void handle_http_request(char *query_string) {
    char local_buffer[512]; // Fixed-size stack buffer
    char *param_val;

    param_val = parse_cgi_param(query_string, "session_token");
    if (param_val != NULL) {
        // Unsafe string copy without bounds checking
        strcpy(local_buffer, param_val); // Overwrites return pointer when > 512 bytes
    }
    process_switch_telemetry(local_buffer);
}
Because embedded MIPS/ARM architectures in legacy switch firmware often lack modern memory mitigations—such as stack canaries (-fstack-protector) or Address Space Layout Randomization (ASLR)—submitting an overly long parameter payload allows an attacker to overwrite the stored function return address ($ra on MIPS or LR on ARM). The control flow is hijacked directly into an executable buffer or shellcode payload, granting interactive shell access on the switch's embedded busybox environment.
Vulnerability Impact & Lateral Pivoting Vectors
Compromising an enterprise smart switch yields immense strategic advantages for an adversary:
| Stage | Attacker Action | Vulnerable Layer | Tactical Advantage |
|---|---|---|---|
| 1. Network Ingress | Scans local subnet or bridged Wi-Fi VLAN for switch web portal on port 80/443. | Web GUI Daemon | Discovers unauthenticated Zyxel GS1900 management interfaces. |
| 2. Exploitation | Transmits malformed HTTP POST request with overflow string in CGI parameters. | CGI Program Stack | Overwrites return address; executes root shellcode. |
| 3. Persistence | Installs reverse shell or modifies /etc/init.d/ startup scripts in flash storage. |
Embedded Linux OS | Establishes persistent foothold surviving switch reboots. |
| 4. Network Pivoting | Reconfigures switch port mirroring (SPAN) or modifies 802.1Q VLAN trunking. | Switch Hardware ASIC | Sniffs corporate traffic, bypasses network segmentation, and targets internal servers. |
Affected Models & Firmware Matrix
The vulnerability impacts the following Zyxel GS1900 series smart managed switch models running firmware releases prior to v2.90(XXXX.2)C0:
| Model Family | Affected Hardware Models | Remediation Firmware |
|---|---|---|
| GS1900 8-Port Series | GS1900-8, GS1900-8HP | Upgrade to v2.90(AAEE.2)C0 or later |
| GS1900 10-Port Series | GS1900-10HP | Upgrade to v2.90(AAEH.2)C0 or later |
| GS1900 16-Port Series | GS1900-16 | Upgrade to v2.90(AAEI.2)C0 or later |
| GS1900 24-Port Series | GS1900-24, GS1900-24E, GS1900-24EP, GS1900-24HPv2 | Upgrade to v2.90(AAEJ.2)C0 or later |
| GS1900 48-Port Series | GS1900-48, GS1900-48HPv2 | Upgrade to v2.90(AAEK.2)C0 or later |
Defensive Playbook & Mitigation Guidance
1. Immediate Firmware Flashing
Download the corresponding model firmware from the official Zyxel Download Library and apply updates via the web configurator or centralized network management station:
# Verify current firmware version via switch web CLI or SNMP
snmpwalk -v2c -c public  sysDescr.0
2. Management Interface Isolation
Under no circumstances should the switch management interface be accessible from general user subnets, guest Wi-Fi networks, or public IP addresses:
- Assign the switch management IP to a dedicated, out-of-band management VLAN (e.g., VLAN 999).
- Configure Access Control Lists (ACLs) on upstream routers to restrict traffic to ports 80/TCP and 443/TCP exclusively from authorized administrative workstations.
- Disable HTTP and enforce HTTPS with modern TLS cipher suites for administrative sessions.
3. Network Traffic Inspection & Suricata Signature
Deploy network intrusion detection signatures to identify oversized HTTP requests targeting the CGI binary:
alert http $LAN_NET any -> $SWITCH_NET [80,443] ( msg:"CST THREAT DESK - Zyxel GS1900 Stack Buffer Overflow Exploit Attempt (CVE-2026-7273)"; flow:established,to_server; content:"/cgi-bin/"; http_uri; pcre:"/(?:session_token|action|cmd)=[A-Za-z0-9%]{512,}/"; classtype:attempted-admin; sid:20267273; rev:1; )