Deep DiveData Protection Board of India Opens First Inquiries Into Data Fiduciaries
The Data Protection Board of India issues regulatory show-cause notices to major enterprise data fiduciaries over non-compliant algorithmic impact assessments.
114 articles
Deep DiveThe Data Protection Board of India issues regulatory show-cause notices to major enterprise data fiduciaries over non-compliant algorithmic impact assessments.
Deep DiveThe Reserve Bank of India mandates migration to Post-Quantum Cryptography across hardware security modules and financial switches to counter Q-day risks.
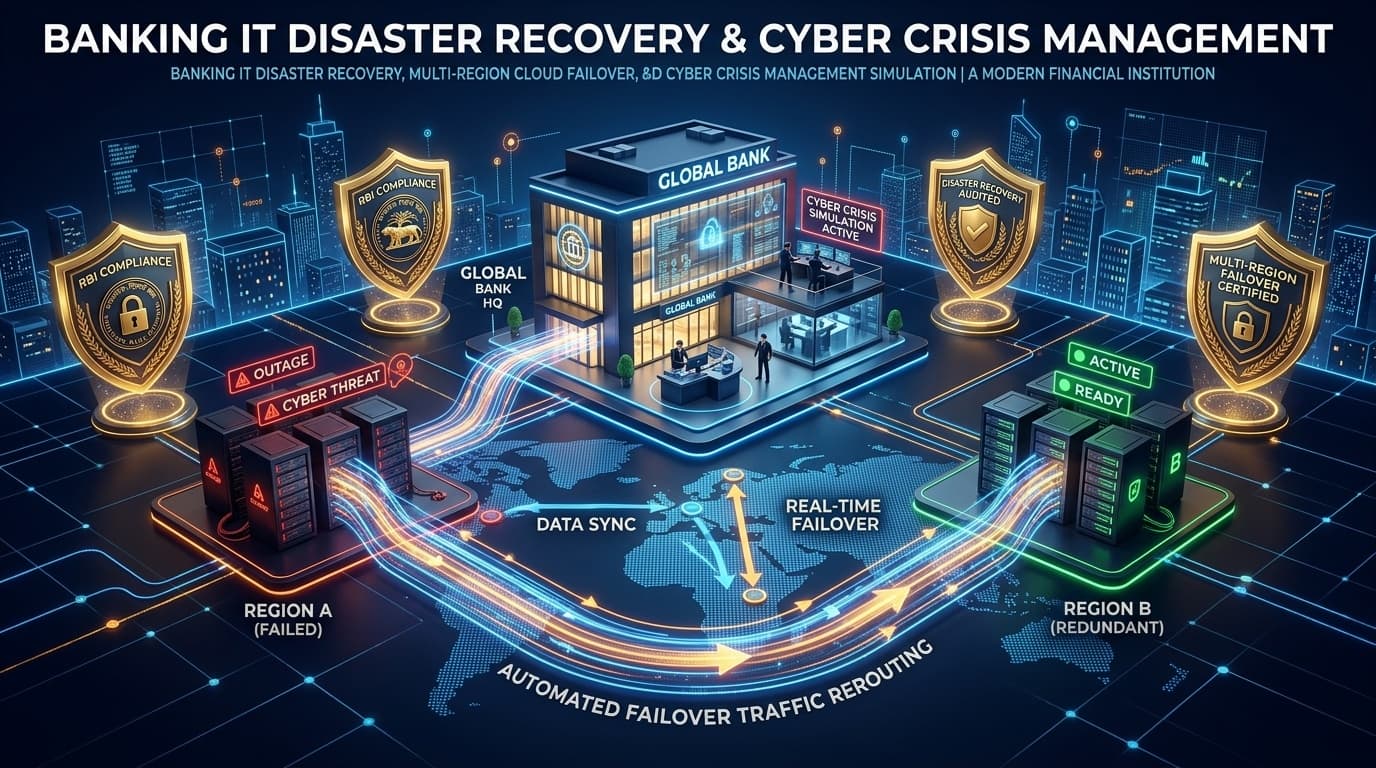
Deep DiveReserve Bank of India issues binding directions requiring all regulated banks to execute annual live cyber crisis simulations and automated multi-region cloud failover.
Deep DiveEuropean Supervisory Authorities notify binding DORA technical standards requiring mandatory Threat-Led Penetration Testing (TLPT) and strict third-party ICT audits.
Deep DiveReserve Bank of India issues binding directions requiring automated HSM cryptographic key rotation and token decryption logging across all payment systems.
Deep DiveMeitY and Data Protection Board of India issue binding DPDP Rules 2026 requiring annual algorithmic audits, biometric tokenization, and strict 6-hour breach reports.
Deep DiveThe Reserve Bank of India mandates continuous automated compliance monitoring and sovereign data localization for all banking cloud workloads.
Deep DiveThe European Commission publishes harmonized technical standards for the Cyber Resilience Act, requiring hardware-based secure boot and 24-hour vulnerability notification.
Deep DiveThe Reserve Bank of India mandates strict 15-minute RTO failover benchmarks and WORM immutable backup architectures for all scheduled commercial banks.
Deep DiveThe PCI Security Standards Council enforces mandatory Requirement 6.4.3 and 11.6.1 compliance, requiring automated inventory and cryptographic hashing of all payment scripts.
Deep DiveEuropean Supervisory Authorities finalize binding technical standards under the Digital Operational Resilience Act (DORA), requiring 4-hour intermediate incident disclosures.
Deep DiveThe Reserve Bank of India mandates strict Hardware Security Module (HSM) key management, post-quantum readiness, and 6-hour incident disclosure across all digital payment entities.
Deep DiveThe Ministry of Electronics and Information Technology (MeitY) has finalized DPDP Rules 2026, establishing strict audit deadlines and algorithmic assessments for Significant Data Fiduciaries.
Deep DiveThe European Union Cyber Resilience Act enters critical enforcement phases, requiring hardware OEMs and software vendors to maintain machine-readable SBOMs and report actively exploited flaws within 24 hours.
Deep DiveReserve Bank of India issues Master Direction mandating scheduled banks and payment operators to deploy automated mule account detection and 2-hour fraud holds.
Deep DiveThe European Union's NIS2 Directive enforces strict 24-hour early warning notifications and executive liability for critical entities facing major cyber incidents.
Deep DivePCI DSS v4.0.1 Requirement 6.4.3 and 11.6.1 enforcement mandates strict browser script inventory and tamper detection on all payment checkout pages.
Gov / DefenseCERT-In security advisory mandates multi-cloud redundancy, immutable backup vaults, and 6-hour incident disclosure across Indian financial institutions.
Deep DiveEuropean Supervisory Authorities operationalize DORA TLPT frameworks, requiring banks and critical ICT providers to undergo advanced red-team audits.
Deep DiveContinuous zero-days in Citrix, Fortinet, and enterprise gateways demonstrate that reactive patching is failing. Only hardware MTE and Rust re-architectures offer an exit.
Deep DiveIndia activates Phase 2 of the Digital Personal Data Protection Act, introducing DPBI enforcement inquiries and penalties up to ₹250 Crore.
Deep DiveDisparate incident reporting windows across the SEC, EU DORA, and India's RBI create a legal hazard for CISOs. Here is how enterprise response playbooks must adapt.
Agentic AIRecent CVEs in Ollama and AWS MCP reveal that semantic prompt filters cannot prevent tool injection. Engineering teams must isolate agent tools in ephemeral microVMs.
Deep DiveReserve Bank of India mandates strict IT governance, cloud outsourcing oversight, and 6-hour cyber incident disclosures across financial institutions.