Regulatory Framework Overview
The Ministry of Electronics and Information Technology (MeitY), in consultation with the Data Protection Board of India (DPBI), has officially notified the Digital Personal Data Protection (DPDP) Rules, 2026. Following the enactment of the parent DPDP Act in 2023, the 2026 operational rules establish the precise technical parameters, governance structures, and enforcement timelines required for all entities processing personal digital data within the Republic of India.
Chief Information Security Officers (CISOs) and enterprise compliance officers must urgently adjust data management pipelines to meet the rigorous obligations imposed on entities classified as Significant Data Fiduciaries (SDFs).
Core Compliance Mandates for Significant Data Fiduciaries
Under Section 10 of the Act and Rule 12 of the 2026 Rules, the Central Government designates data fiduciaries as "Significant" based on the volume of data processed, sensitivity of personal identifiers, risk of harm to Data Principals, and potential impact on national security and public order. Entities handling large volumes of financial, healthcare, or AI training data must satisfy four non-negotiable pillars:
| Mandate Area | Statutory Requirement | Audit & Validation Frequency |
|---|---|---|
| Data Protection Officer (DPO) | Indian resident, reporting directly to the Board of Directors | Continuous governance oversight |
| Algorithmic Impact Assessment | Independent technical audit of automated processing & AI models | Annual statutory audit + pre-deployment reviews |
| Biometric Data Tokenization | Irreversible cryptographic salt-hashing; no plaintext storage | Real-time architecture enforcement |
| Breach Notification | Mandatory notification to DPBI & CERT-In within 6 hours | Incident-triggered (24/7 SLA) |
Rule 18: Mandatory Biometric Tokenization Standard
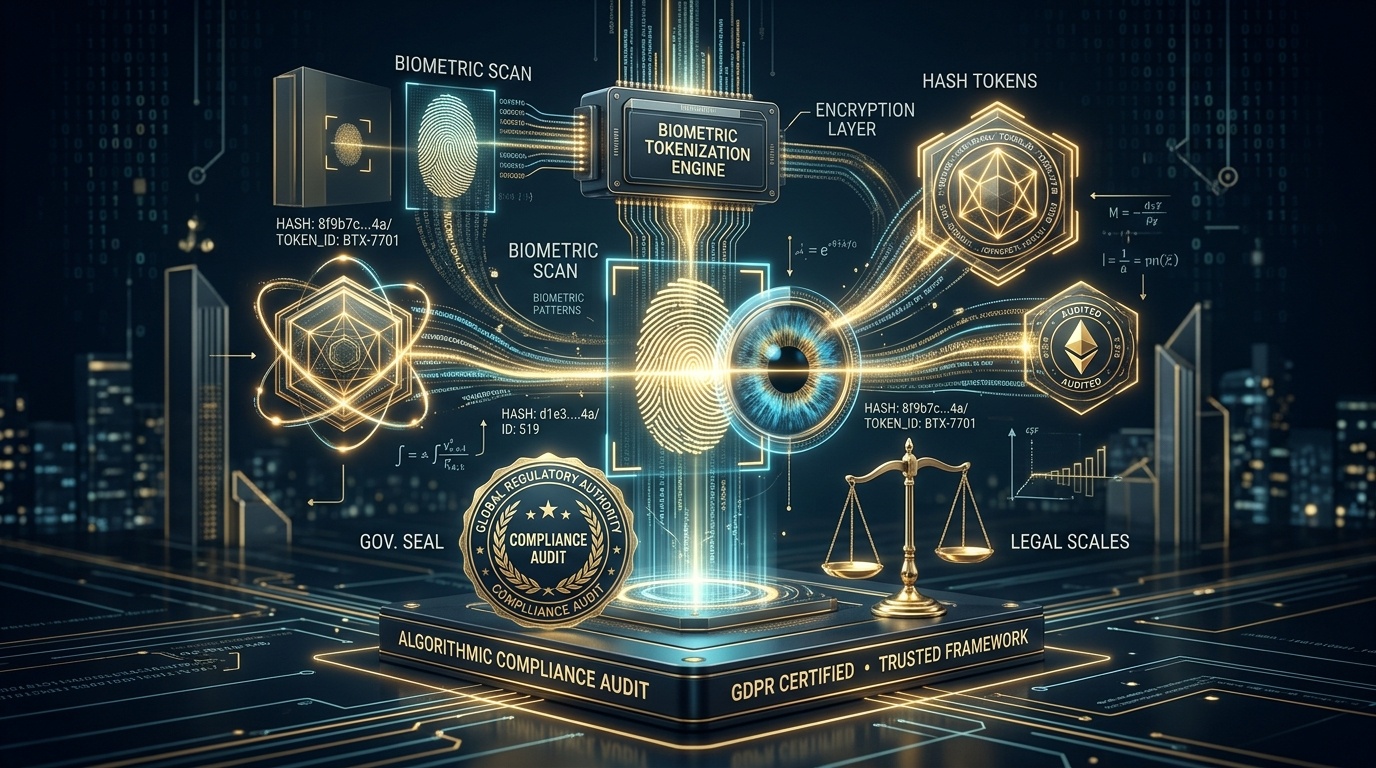
One of the most consequential technological additions in the 2026 Rules is Rule 18, which governs biometric data processing. Any organization processing fingerprints, facial recognition scans, iris templates, or voice biometric markers is strictly prohibited from storing raw biometric images or reversible feature vectors in public or private cloud environments.
Instead, fiduciaries must implement irreversible cryptographic tokenization utilizing FIPS 140-3 validated Hardware Security Modules (HSMs). Biometric vectors must be transformed into format-preserving pseudorandom tokens salted with enterprise-held root keys that cannot be reconstructed even in the event of database exfiltration.
Harmonization with RBI and CERT-In Reporting SLAs
The DPDP Rules 2026 explicitly synchronize with the Reserve Bank of India (RBI) Cyber Security Framework and CERT-In directions. In the event of a personal data breach:
- T+6 Hours: The fiduciary must submit an initial notification to the DPBI portal and CERT-In detailing the affected data categories, estimated number of Data Principals, and immediate containment actions.
- T+72 Hours: A comprehensive forensic investigation report must be filed, incorporating endpoint telemetry, root cause vulnerability analysis, and mitigation efficacy.
- Communication to Data Principals: Fiduciaries must directly notify affected individuals without undue delay using plain, unambiguous language across SMS, registered email, or mobile app notices.
Failure to implement reasonable security safeguards to prevent a personal data breach attracts maximum statutory penalties of up to ₹250 Crore (~$30 Million USD) per violation under Schedule 1 of the Act.