Executive Overview
The landmark Cyber Resilience Act (CRA), formally adopted by the European Parliament and the Council of the European Union, has established comprehensive mandatory cybersecurity requirements for all products with digital elements placed on the EU single market. Covering everything from connected IoT consumer electronics to enterprise routers, industrial controllers, and software applications, the regulation introduces legally enforceable cybersecurity obligations spanning product design, supply chain tracking, and lifetime maintenance.
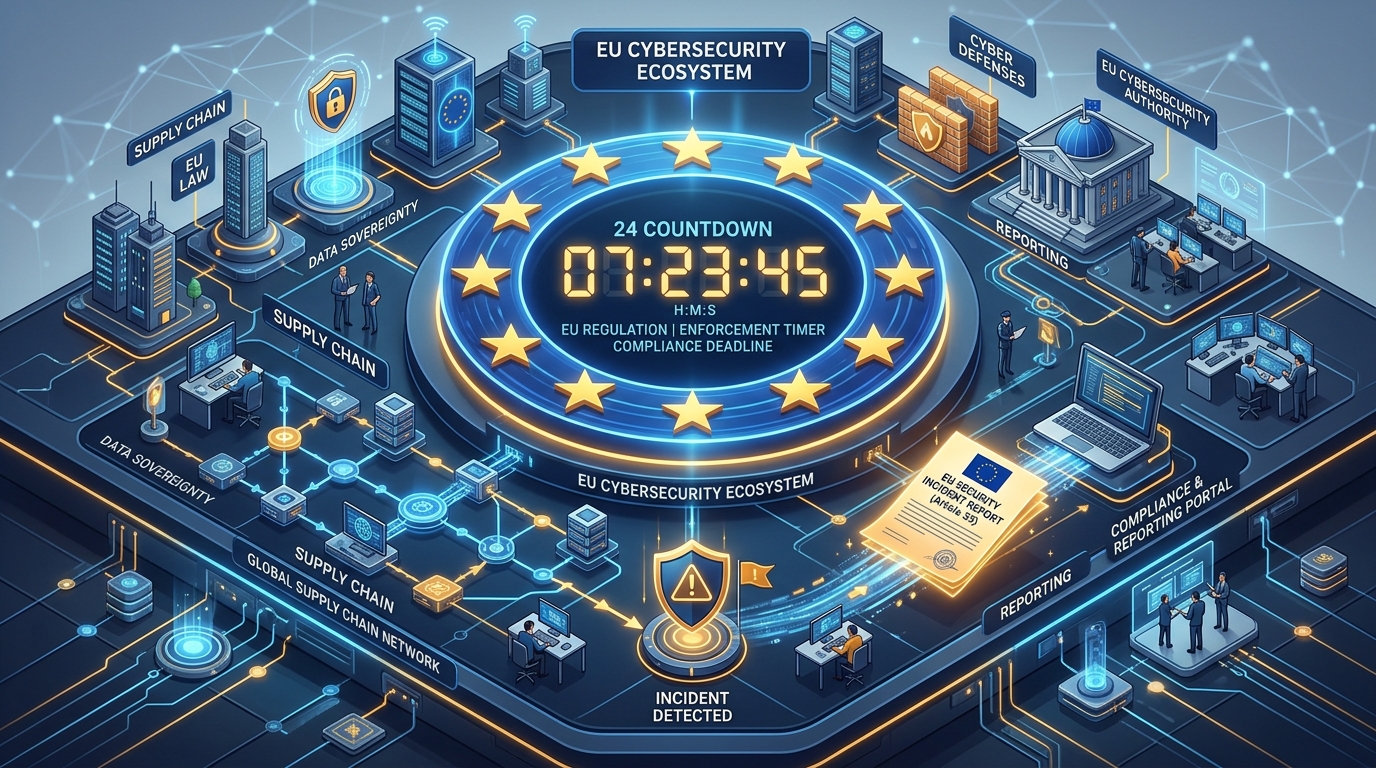
Chief among the CRA's strict mandates is the universal requirement for manufacturers to produce and continuously maintain a machine-readable Software Bill of Materials (SBOM), alongside a legally binding obligation to report actively exploited vulnerabilities to the European Union Agency for Cybersecurity (ENISA) and designated national Computer Security Incident Response Teams (CSIRTs) within 24 hours of awareness.
The Technical Architecture of Mandatory SBOMs
Under Article 10 of the regulation, manufacturers are required to systematically identify and document all software components, third-party libraries, open-source dependencies, and firmware modules integrated into their products. Unlike voluntary guidelines, the CRA specifies strict technical criteria for compliance:
- Standardized Machine-Readable Formats: SBOMs must conform to established open standards, specifically CycloneDX (v1.5+) or SPDX (Software Package Data Exchange v2.3+).
- Cryptographic Provenance: Dependency trees must feature cryptographic hashes (SHA-256) for every library binary, accompanied by verifiable author and license metadata.
- Vulnerability Traceability: Manufacturers must maintain continuous mapping between their SBOM repository and authoritative vulnerability databases (NVD, GitHub Advisory Database) to detect upstream flaws automatically.
{
  "bomFormat": "CycloneDX",
  "specVersion": "1.5",
  "serialNumber": "urn:uuid:3e671687-395b-41f5-a30f-a58921a69b79",
  "version": 1,
  "metadata": {
    "timestamp": "2026-10-08T00:00:00Z",
    "component": {
      "type": "device",
      "name": "Industrial-IoT-Gateway-Pro",
      "version": "2.4.0",
      "cpe": "cpe:2.3:h:oem_corp:gateway_pro:2.4.0:*:*:*:*:*:*:*"
    }
  }
}
24-Hour Incident Reporting & Regulatory Penalties
The CRA establishes a two-tiered incident disclosure timeline designed to eliminate undisclosed zero-day exploitation across European infrastructure:
- Early Warning (24 Hours): The manufacturer must submit an initial notification to ENISA and the competent national CSIRT within 24 hours of becoming aware of any actively exploited vulnerability or severe cyber incident affecting their product.
- Comprehensive Report (72 Hours): A comprehensive technical analysis detailing root cause, severity, affected firmware builds, and available mitigations must follow within 72 hours.
Non-compliance carries severe financial sanctions: regulatory authorities may impose administrative fines of up to €15,000,000 or 2.5% of total worldwide annual turnover for the preceding financial year, whichever is higher, alongside potential product recall orders across all 27 EU member states.
Enterprise Readiness Checklist
Organizations developing hardware or software marketed in Europe must immediately execute the following readiness steps:
- Integrate automated SBOM generation into CI/CD build pipelines using tools such as Syft or Trivy.
- Establish dedicated PSIRT (Product Security Incident Response Team) operations equipped to triage and notify ENISA within the mandatory 24-hour window.
- Define and publish clear security support lifetime timelines for all connected products, ensuring over-the-air (OTA) cryptographic firmware updates remain supported for at least five years.