In a watershed milestone for international software security governance, the mandatory reporting requirements of the European Union Cyber Resilience Act (CRA) have officially come into force as of September 11, 2026.
While the full suite of cybersecurity requirements—including CE marking conformity and secure-by-design architectural mandates—will apply in late 2027, the European Commission structured the legislation so that vulnerability and severe incident reporting obligations took effect early. From this week onward, any hardware manufacturer or software publisher distributing products with digital elements in the European Union must operate under a strict, legally binding disclosure clock.
The Three-Stage Reporting Timeline
The CRA replaces informal, discretionary vendor disclosure timelines with an aggressive tripartite notification schedule:
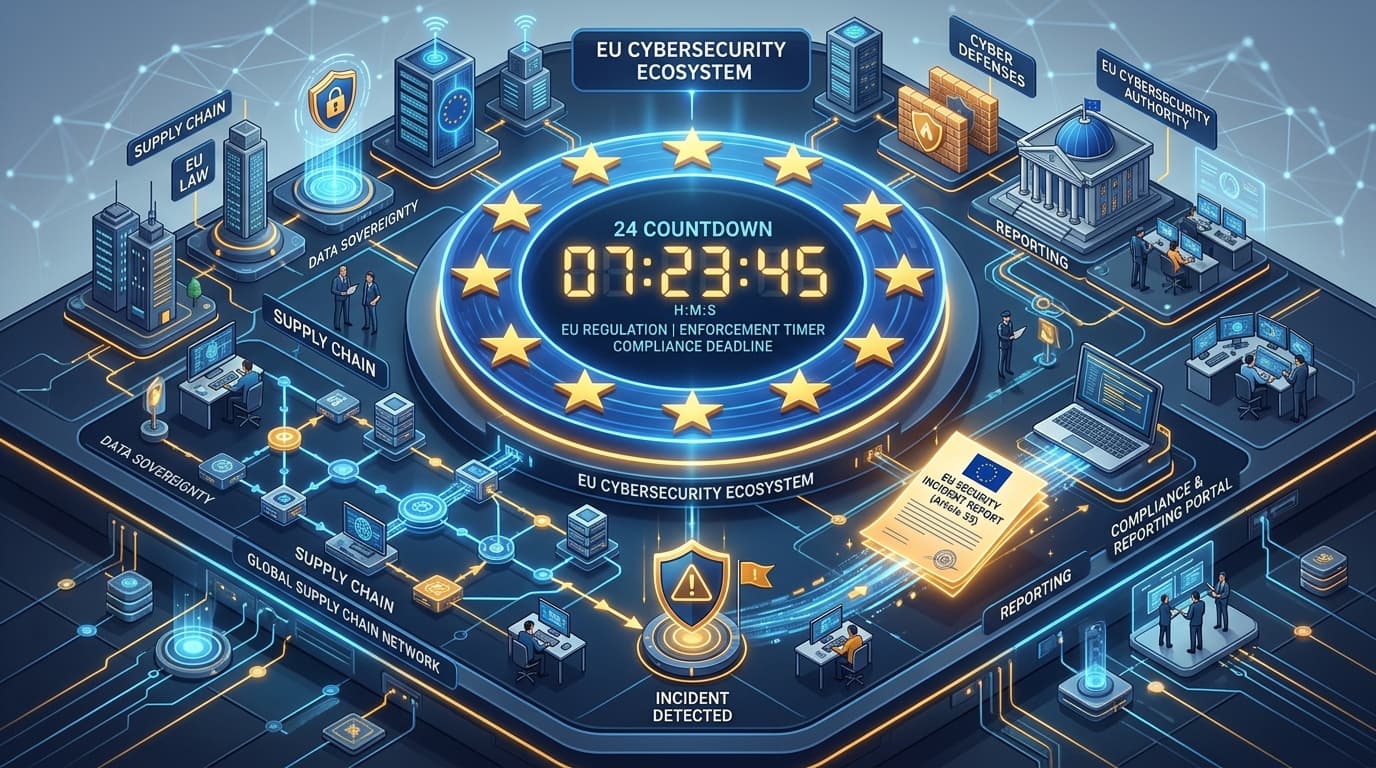
- 24-Hour Early Warning: Within 24 hours of becoming aware of an actively exploited vulnerability or severe cybersecurity incident, the manufacturer must file an initial alert indicating whether the issue is suspected of being caused by unlawful or malicious acts.
- 72-Hour Full Notification: Within 72 hours of initial awareness, the manufacturer must provide a comprehensive assessment detailing general technical indicators, estimated severity, potential cross-border impacts, and any mitigations implemented.
- Final Report (14 Days Post-Remediation): For actively exploited vulnerabilities, a formal final report must be submitted no later than 14 days after a corrective measure or patch is released to the public, documenting root causes and corrective actions taken.
The days of vendors quietly sitting on exploited zero-days for weeks while coordinating marketing releases are over in the European market. A 24-hour statutory timer requires incident response teams to be directly wired into regulatory reporting desks.
The Single Reporting Platform (SRP) Architecture
To prevent companies from having to duplicate submissions across 27 national authorities, the European Union Agency for Cybersecurity (ENISA) deployed the CRA Single Reporting Platform (SRP) at portal.cra-srp.enisa.europa.eu.
The portal uses a "report once" model: manufacturers authenticate using EU Login with mandatory multi-factor authentication and submit notifications to the designated national Computer Security Incident Response Team (CSIRT) where their EU headquarters is located. The platform automatically mirrors the notification to ENISA and relevant member-state CSIRTs simultaneously.
Critical Scope: Legacy Products Are Not Exempt
A crucial detail catching many enterprise legal and engineering departments off guard is the scope of products covered by the September 2026 milestone. Unlike standard design requirements that apply only to newly manufactured items post-2027, the reporting obligations apply to all products with digital elements currently active on the EU market, including legacy software and supported hardware.
Failing to submit notifications within the prescribed statutory timeframes exposes organizations to administrative fines of up to €15,000,000 or 2.5% of total worldwide annual turnover from the preceding financial year, establishing financial liabilities comparable to the GDPR.
Action Items for Product Security & Engineering Teams
- Establish EU Login Credentials: Ensure your corporate security organization has verified accounts and delegated administrators configured on ENISA's Single Reporting Platform today.
- Define the 24-Hour Triage Playbook: Update Product Security Incident Response Team (PSIRT) runbooks so that the moment a flaw is confirmed to have in-the-wild exploitation, regulatory counsel and designated submitters are engaged immediately.
- Coordinate with Upstream Open-Source Dependencies: While open-source software stewards have until December 2027 before facing direct obligations under Article 24(3), commercial vendors packaging open-source libraries into commercial offerings remain directly liable for vulnerabilities actively exploited in those bundled components.