Executive Lead: The European Union Enacts Comprehensive Cybersecurity Overhaul
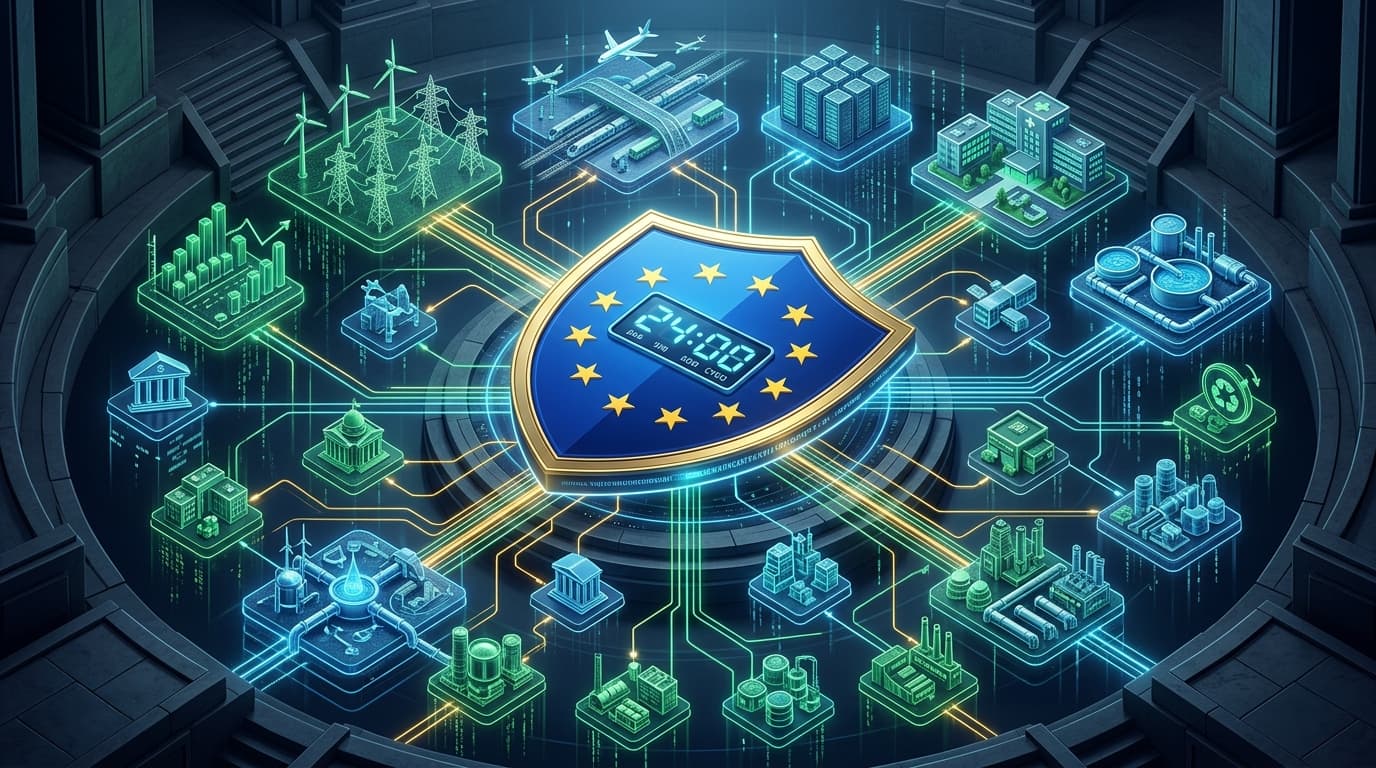
The regulatory grace period for Directive (EU) 2022/2555—widely known as the NIS2 Directive—has formally transitioned into full statutory enforcement across the European Union. Superseding the original 2016 NIS Directive, NIS2 dramatically broadens the scope of mandatory cybersecurity requirements, expanding legal oversight to encompass more than 160,000 public and private organizations across 18 critical and important economic sectors.
Administered by national competent authorities in coordination with the European Union Agency for Cybersecurity (ENISA), the NIS2 regime transforms enterprise cybersecurity from an optional IT discipline into a board-governed fiduciary obligation. Central to the directive is a rigid, multi-stage incident notification clock that requires organizations to submit an Early Warning within 24 hours of detecting any significant cybersecurity incident.
Crucially, NIS2 introduces unprecedented governance enforcement: corporate board members and executive directors face direct personal liability for cybersecurity non-compliance, including potential temporary bans from exercising managerial functions. Backed by maximum administrative fines reaching up to €10 Million or 2% of total worldwide annual turnover, the directive establishes the most comprehensive regulatory cybersecurity standard in the Western hemisphere.
Expanded Sectoral Taxonomy: Essential vs. Important Entities
NIS2 eliminates the ambiguity of the previous "Operators of Essential Services" classification by establishing an objective size-cap rule (generally applying to all medium and large enterprises with over 50 employees or €10 million turnover) divided into two regulatory categories:
+-----------------------------------------------------------------------------------------+
|                              NIS2 SECTORAL TAXONOMY                                     |
+-----------------------------------------------------------------------------------------+
| ESSENTIAL ENTITIES (Annex I)                | IMPORTANT ENTITIES (Annex II)             |
| Higher supervision, ex-ante enforcement    | Ex-post supervision, triggered by incident|
| - Energy (Electricity, Oil, Gas, Hydrogen)  | - Postal and courier services             |
| - Transport (Air, Rail, Water, Road)        | - Waste management                        |
| - Banking & Financial Market Infrastructure| - Manufacture & distribution of chemicals|
| - Health (Hospitals, Pharma, Labs)          | - Food production, processing & retail  |
| - Drinking water & Wastewater systems     | - Manufacturing (Medical, Electronics,    |
| - Digital Infrastructure (DNS, TLDs, Cloud, |   Machinery, Motor vehicles)              |
|   Data Centers, CDNs, Trust Services)       | - Digital Providers (Search engines,      |
| - ICT Service Management (MSPs, MSSPs)      |   Online marketplaces, Social platforms)  |
| - Public Administration & Space           | - Research organizations                  |
+-----------------------------------------------------------------------------------------+
The inclusion of Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs) within Annex I is a direct regulatory response to supply chain compromises, ensuring that outsourced IT providers cannot serve as unmonitored backdoors into critical infrastructure.
The NIS2 Incident Reporting Lifecycle: The 24-Hour Clock
Under Article 23 of NIS2, any incident that has a "significant impact"—defined as causing severe operational disruption, financial loss, or affecting other natural or legal persons by causing considerable material or non-material damage—triggers a structured, three-tiered notification obligation to the national Computer Security Incident Response Team (CSIRT) or competent authority:
+-----------------------------------------------------------------------------------------+
|                       THE NIS2 MANDATORY INCIDENT REPORTING TIMELINE                    |
+-----------------------------------------------------------------------------------------+
| T+0:00      Significant Incident Detected by Enterprise Security Operations             |
|               |                                                                         |
|               v                                                                         |
| T+24:00     EARLY WARNING NOTIFICATION (Within 24 Hours)                                |
|             - State whether the incident was caused by unlawful or malicious acts       |
|             - Indicate whether the incident has cross-border impact across EU states    |
|               |                                                                         |
|               v                                                                         |
| T+72:00     INCIDENT NOTIFICATION (Within 72 Hours)                                     |
|             - Provide comprehensive initial assessment: severity, impact, IOCs         |
|             - Outline technical mitigation measures deployed                            |
|               |                                                                         |
|               v                                                                         |
| T+1 Month   FINAL COMPREHENSIVE REPORT (Within 30 Days of Incident)                     |
|             - Detailed post-mortem analysis: root cause, threat actor attribution       |
|             - Forensic telemetry, long-term corrective action plans, audit findings     |
+-----------------------------------------------------------------------------------------+
C-Suite Personal Liability & The Penalty Matrix
Unlike conventional compliance frameworks that penalize only corporate legal entities, NIS2 explicitly pierces the corporate veil under Article 20, holding executive management bodies accountable:
- Mandatory Board Cybersecurity Training: Members of the management body must follow specific training to gain sufficient cybersecurity risk-management knowledge and must offer similar training to corporate employees on a regular basis.
- Approval of Risk Measures: The management body must formally approve all enterprise cybersecurity risk-management measures and actively oversee their operational implementation.
- Temporary Managerial Bans: In cases of severe non-compliance following an incident, judicial authorities may temporarily suspend individuals exercising chief executive officer (CEO) or legal representative functions until deficiencies are rectified.
- Severe Financial Fines: Essential Entities face fines up to €10 million or 2% of total worldwide turnover; Important Entities face up to €7 million or 1.4% of turnover.
Technical Implementation Matrix: Article 21 Security Baseline
| Security Domain | Article 21 Statutory Requirement | Engineering Implementation Standard |
|---|---|---|
| Access Control & Authentication | Multi-factor authentication (MFA) or continuous auth | FIDO2 / WebAuthn hardware keys, Zero Trust conditional access |
| Supply Chain Security | Security aspects concerning relationships with suppliers | Automated Software Bill of Materials (SBOM), vendor SOC 2 audits |
| Vulnerability Handling | Vulnerability handling and disclosure processes | Coordinated Vulnerability Disclosure (CVD), automated SCA scanning |
| Incident Handling | Incident detection, analysis, containment, and response | 24/7 Managed Detection and Response (MDR), automated SOAR workflows |
| Business Continuity | Backup management, disaster recovery, and crisis governance | 3-2-1-1-0 immutable backups, air-gapped recovery, annual DR drills |
| Cryptography | Policies on the use of cryptography and encryption | TLS 1.3, AES-256-GCM data-at-rest encryption, HSM key management |
Enterprise NIS2 Readiness Playbook: Strategic Engineering Steps
To ensure full compliance and insulate executive leadership from statutory liability, CISOs and corporate technology leaders should execute the following four-tier roadmap:
1. Establish Automated Incident Triage & 24-Hour CSIRT Dispatch
Configure your Security Orchestration, Automation, and Response (SOAR) platform to automate the drafting of national CSIRT Early Warning filings immediately upon P1 alert triage:
# SOAR Playbook: NIS2 24-Hour Early Warning Workflow
- Trigger: SIEM Critical Incident (Ransomware / Critical Data Exfiltration)
- Automated Actions:
    1. Check if affected entity falls within NIS2 Essential/Important Annex.
    2. Populate NIS2 Early Warning Form:
       - Incident Detection Timestamp (UTC)
       - Suspected Malicious Origin: [YES / NO]
       - Cross-Border European Impact: [List Member States]
    3. Generate high-priority notification to Legal Counsel and CISO for digital dispatch.
2. Institute Formal Supply Chain & SBOM Validation
Audit all third-party software components and IT service providers. Mandate CycloneDX or SPDX Software Bill of Materials (SBOM) generation across all continuous integration pipelines to identify upstream vulnerabilities before deployment:
# Generate CycloneDX SBOM via Syft in CI/CD pipeline:
syft packages dir:/app --output cyclonedx-json > sbom.json

# Scan SBOM against vulnerability databases using Grype:
grype sbom:sbom.json --fail-on high
3. Executive Management Cybersecurity Governance
Conduct bi-annual board-level cybersecurity immersion briefings covering current threat landscape telemetry, ransomware extortion dynamics, and NIS2 personal liability frameworks. Document board minutes demonstrating active risk-appetite reviews and IT security budget allocations.
4. Deploy Zero Trust & Phishing-Resistant MFA
Decommission password-only and SMS-based multi-factor authentication across all corporate access gateways, administrative portals, and cloud consoles. Mandate cryptographic, hardware-rooted authenticators (FIDO2/WebAuthn) for all internal personnel and third-party contractors.