Regulatory Framework Overview
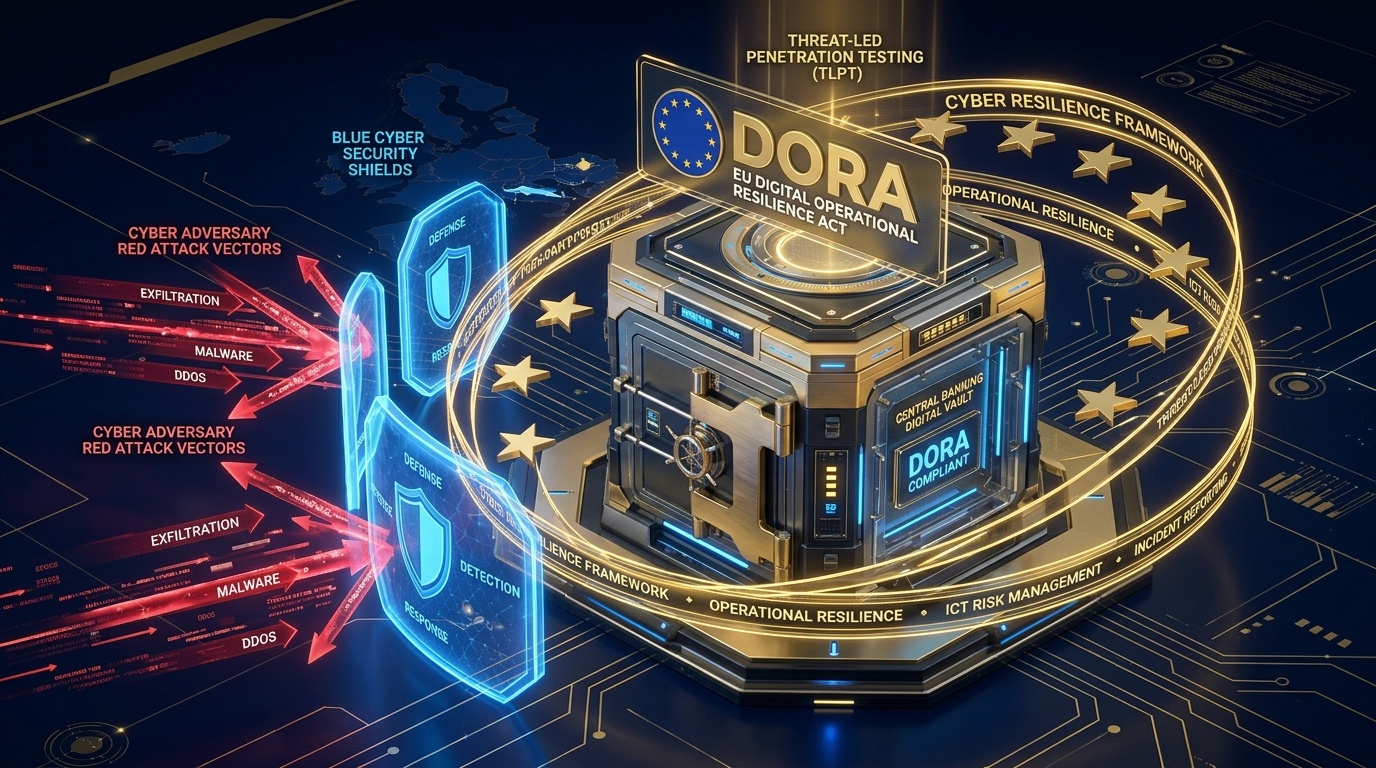
The European Supervisory Authorities (ESAs)—comprising the European Banking Authority (EBA), European Insurance and Occupational Pensions Authority (EIOPA), and European Securities and Markets Authority (ESMA)—have published the finalized Regulatory Technical Standards (RTS) on Threat-Led Penetration Testing (TLPT) under the Digital Operational Resilience Act (DORA, Regulation EU 2022/2554).
The RTS operationalizes Chapter IV of DORA, establishing the precise methodological criteria, tester qualifications, testing scope, and supervisory oversight mechanisms governing live ethical hacking exercises across Europe's financial architecture.
Core Statutory Requirements of the DORA TLPT Standard
Unlike standard penetration tests or synthetic tabletop exercises, TLPT mandates controlled, intelligence-led red teaming against live production systems supporting critical or important financial functions:
| Governance Dimension | DORA RTS Requirement | Operational SLA |
|---|---|---|
| Testing Frequency | Mandatory full-scope TLPT cycle for identified critical institutions | At least once every 3 years |
| Testing Environment | Strictly live production ICT systems supporting critical services | Continuous risk management with operational kill-switches |
| Third-Party Cloud Inclusion | Mandatory inclusion of critical third-party ICT service providers (CTPPs) | Pooled or individual multi-client testing frameworks |
| Tester Accreditation | Certified external red team providers with verified professional indemnity | Strict supervisory vetting |
The TIBER-EU Harmonization & Pooled Cloud Testing
The DORA TLPT framework explicitly builds upon the European Central Bank’s TIBER-EU (Threat Intelligence-based Ethical Red Teaming) methodology. Testing must proceed through three coordinated phases: Scope Specification, Threat Intelligence Gathering (Targeted Threat Modeling), and Red Team Execution followed by Purple Teaming remediation workshops.
One of the most complex challenges resolved by the RTS is testing third-party cloud hyperscalers (such as AWS, Azure, and Google Cloud). Under Article 26 of DORA, where a financial entity relies on a shared cloud service provider, the RTS allows the provider to participate in pooled testing—allowing a certified red team to test the shared infrastructure once on behalf of multiple financial clients simultaneously.
Remediation & Supervisory Compliance Roadmap
Financial entities designated for TLPT must adhere to strict reporting workflows with national competent authorities (such as BaFin, ACPR, or the Central Bank of Ireland):
- Pre-Test Authorization: Submit the proposed testing scope, threat scenarios, and external tester credentials to the supervisory authority at least 6 months prior to test launch.
- Remediation Planning: Following completion of the red team phase, submit a joint test summary report and comprehensive remediation plan endorsed by the institution’s Management Board within 3 months.
- Contractual Re-Negotiation: Update ICT vendor agreements to include mandatory clauses requiring vendor cooperation in DORA TLPT pooled testing and access rights for external auditors.