 Kubernetes
Addressing protocol security gaps in multi-tenant Kubernetes
InsightsCloud & SaaS
Technical architectural analysis of Addressing cloud workload protection, IAM integrity controls, and enterprise boundary defense.
Aisha Noor11 min read
95 articles
KubernetesTechnical architectural analysis of Addressing cloud workload protection, IAM integrity controls, and enterprise boundary defense.
 Deep Dive
Cloudflare's Q3 threat report details an unprecedented 38% surge in network-layer DDoS attacks, recording 18.2 million volumetric and carpet-bombing floods.
 Agentic AI
CSA Singapore issues technical guidelines for securing frontier and autonomous agentic AI models, mandating rigorous defenses against indirect prompt injection and tool-calling escapes.
 Data Breach
The Reserve Bank of India enforces updated CSFB directives mandating 6-hour breach disclosure to CERT-In, third-party cloud audits, and zero-trust banking security.
 Ransomware
Forensic analysis of SEC Form 8-K Item 1.05 material cybersecurity incident disclosures: 4-day reporting timelines, root causes, and board oversight standards.
 Deep Dive
The Data Protection Board of India issues regulatory show-cause notices to major enterprise data fiduciaries over non-compliant algorithmic impact assessments.
 Deep Dive
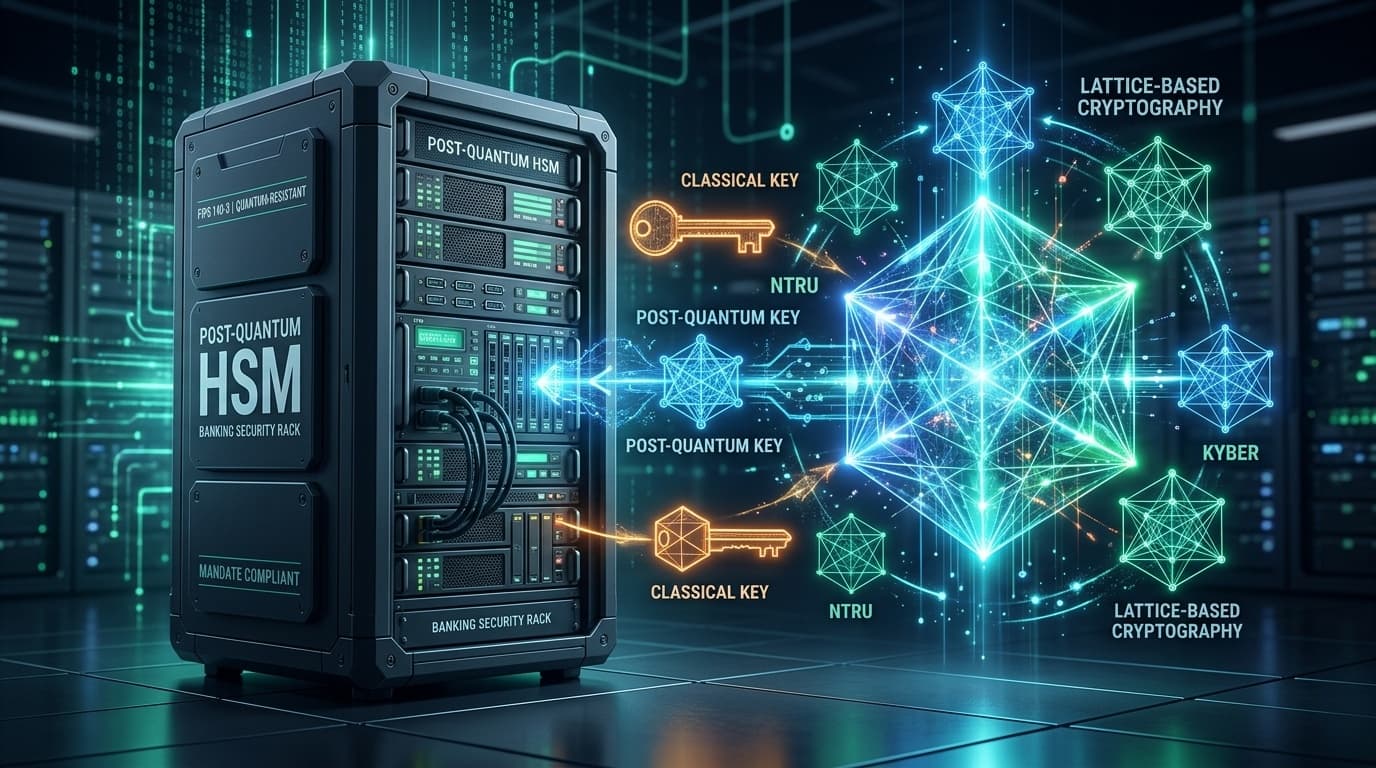
The Reserve Bank of India mandates migration to Post-Quantum Cryptography across hardware security modules and financial switches to counter Q-day risks.
 Deep Dive
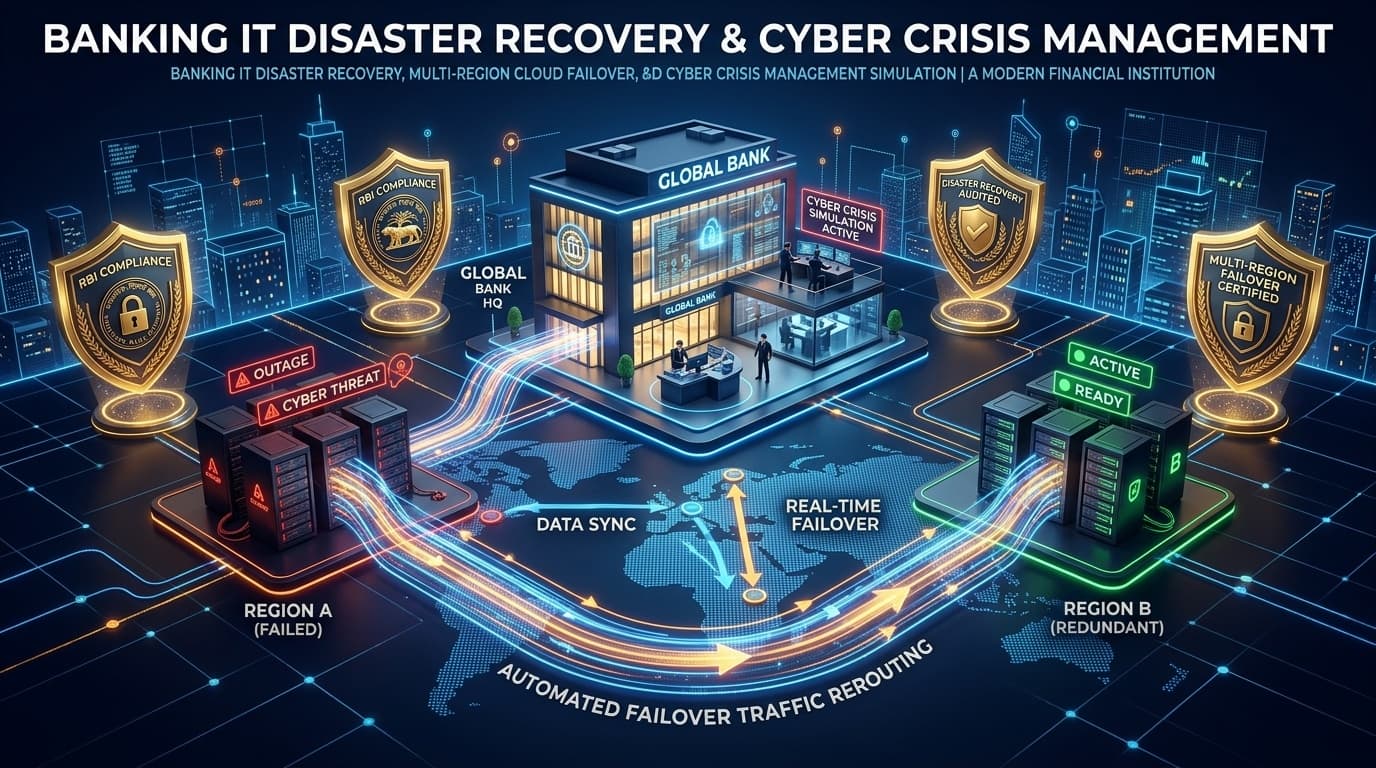
Reserve Bank of India issues binding directions requiring all regulated banks to execute annual live cyber crisis simulations and automated multi-region cloud failover.
 Deep Dive
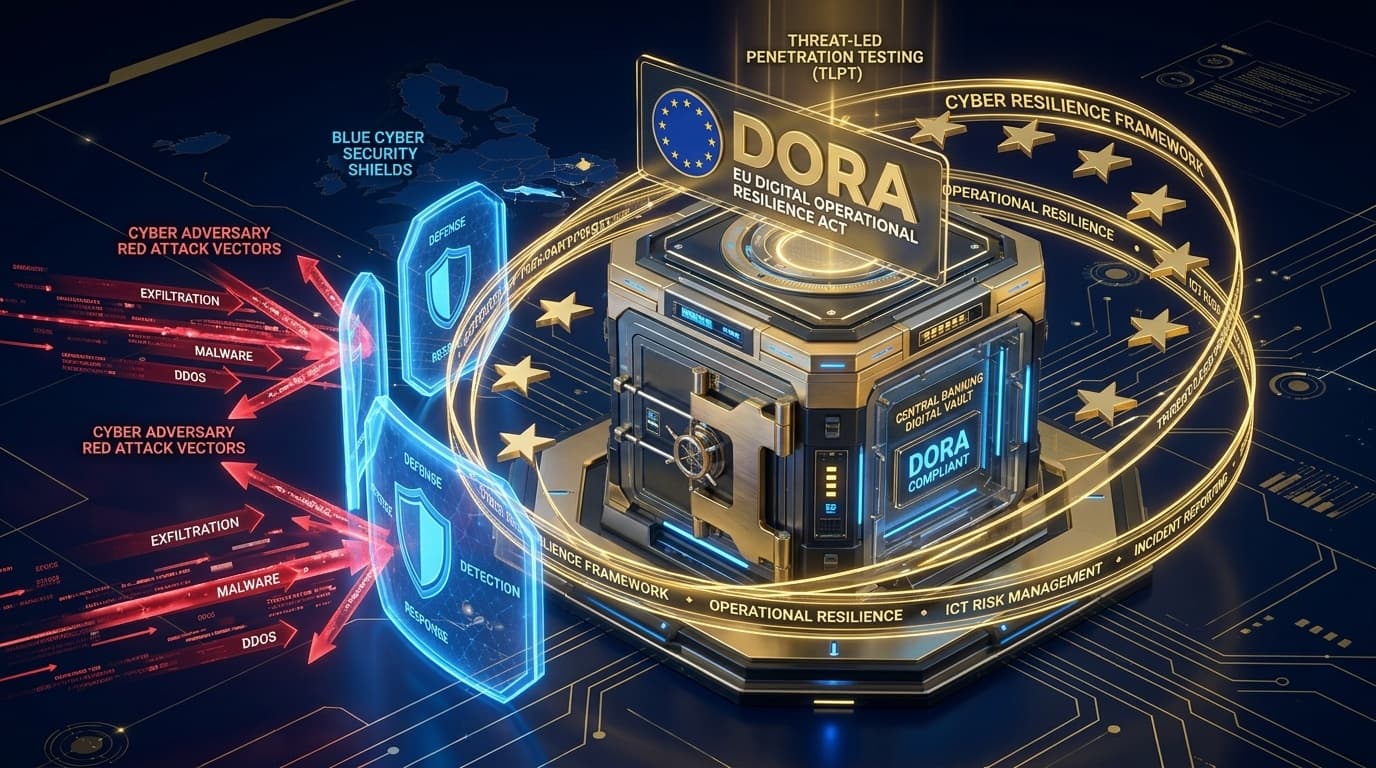
European Supervisory Authorities notify binding DORA technical standards requiring mandatory Threat-Led Penetration Testing (TLPT) and strict third-party ICT audits.
 Deep Dive
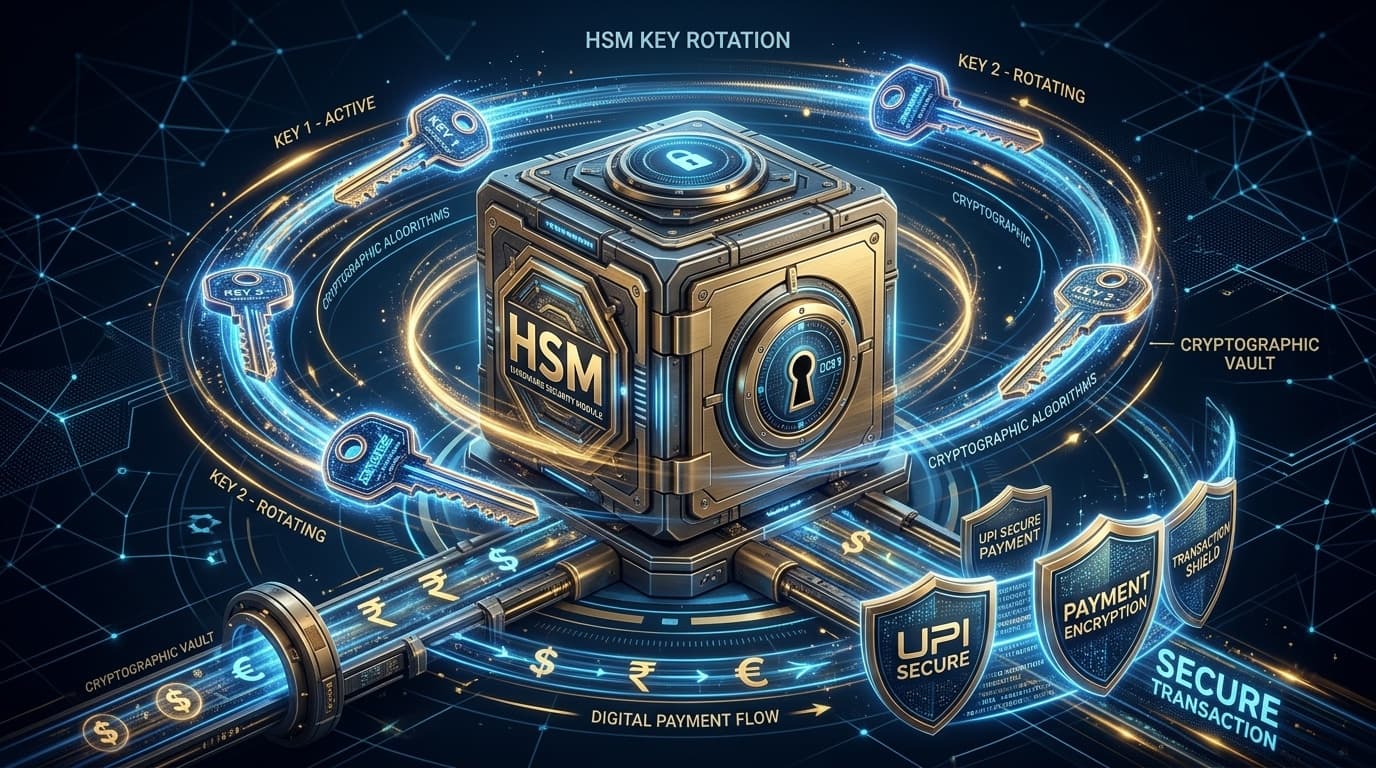
Reserve Bank of India issues binding directions requiring automated HSM cryptographic key rotation and token decryption logging across all payment systems.
 Deep Dive
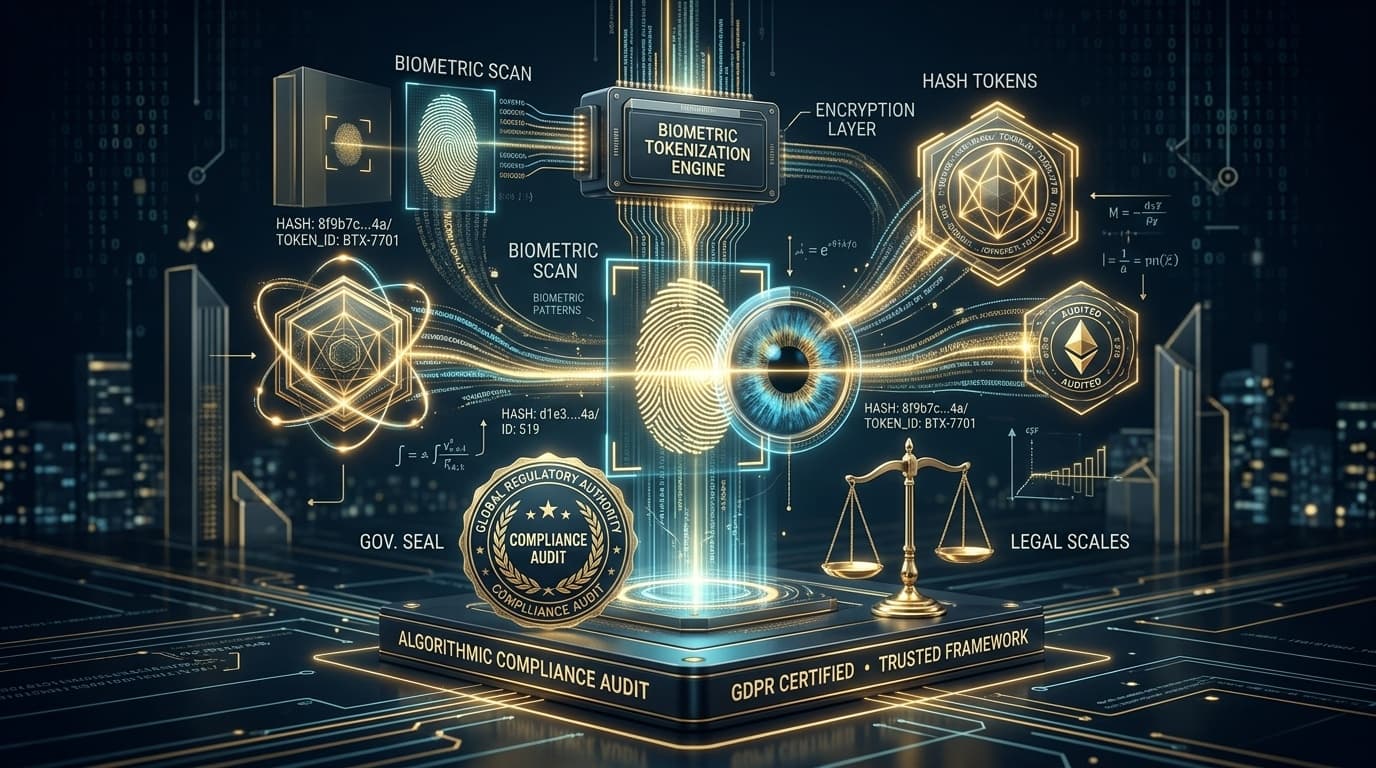
MeitY and Data Protection Board of India issue binding DPDP Rules 2026 requiring annual algorithmic audits, biometric tokenization, and strict 6-hour breach reports.
 Deep Dive
The Reserve Bank of India mandates continuous automated compliance monitoring and sovereign data localization for all banking cloud workloads.
 Deep Dive
The European Commission publishes harmonized technical standards for the Cyber Resilience Act, requiring hardware-based secure boot and 24-hour vulnerability notification.
 Deep Dive
The Reserve Bank of India mandates strict 15-minute RTO failover benchmarks and WORM immutable backup architectures for all scheduled commercial banks.
 Deep Dive
The PCI Security Standards Council enforces mandatory Requirement 6.4.3 and 11.6.1 compliance, requiring automated inventory and cryptographic hashing of all payment scripts.
 Deep Dive
European Supervisory Authorities finalize binding technical standards under the Digital Operational Resilience Act (DORA), requiring 4-hour intermediate incident disclosures.
 Deep Dive
The Reserve Bank of India mandates strict Hardware Security Module (HSM) key management, post-quantum readiness, and 6-hour incident disclosure across all digital payment entities.
 Deep Dive
The Ministry of Electronics and Information Technology (MeitY) has finalized DPDP Rules 2026, establishing strict audit deadlines and algorithmic assessments for Significant Data Fiduciaries.
 Deep Dive
The European Union Cyber Resilience Act enters critical enforcement phases, requiring hardware OEMs and software vendors to maintain machine-readable SBOMs and report actively exploited flaws within 24 hours.
 Deep Dive
Reserve Bank of India issues Master Direction mandating scheduled banks and payment operators to deploy automated mule account detection and 2-hour fraud holds.
 Deep Dive
The European Union's NIS2 Directive enforces strict 24-hour early warning notifications and executive liability for critical entities facing major cyber incidents.
 Deep Dive
PCI DSS v4.0.1 Requirement 6.4.3 and 11.6.1 enforcement mandates strict browser script inventory and tamper detection on all payment checkout pages.
 Gov / Defense
CERT-In security advisory mandates multi-cloud redundancy, immutable backup vaults, and 6-hour incident disclosure across Indian financial institutions.
 Deep Dive
European Supervisory Authorities operationalize DORA TLPT frameworks, requiring banks and critical ICT providers to undergo advanced red-team audits.