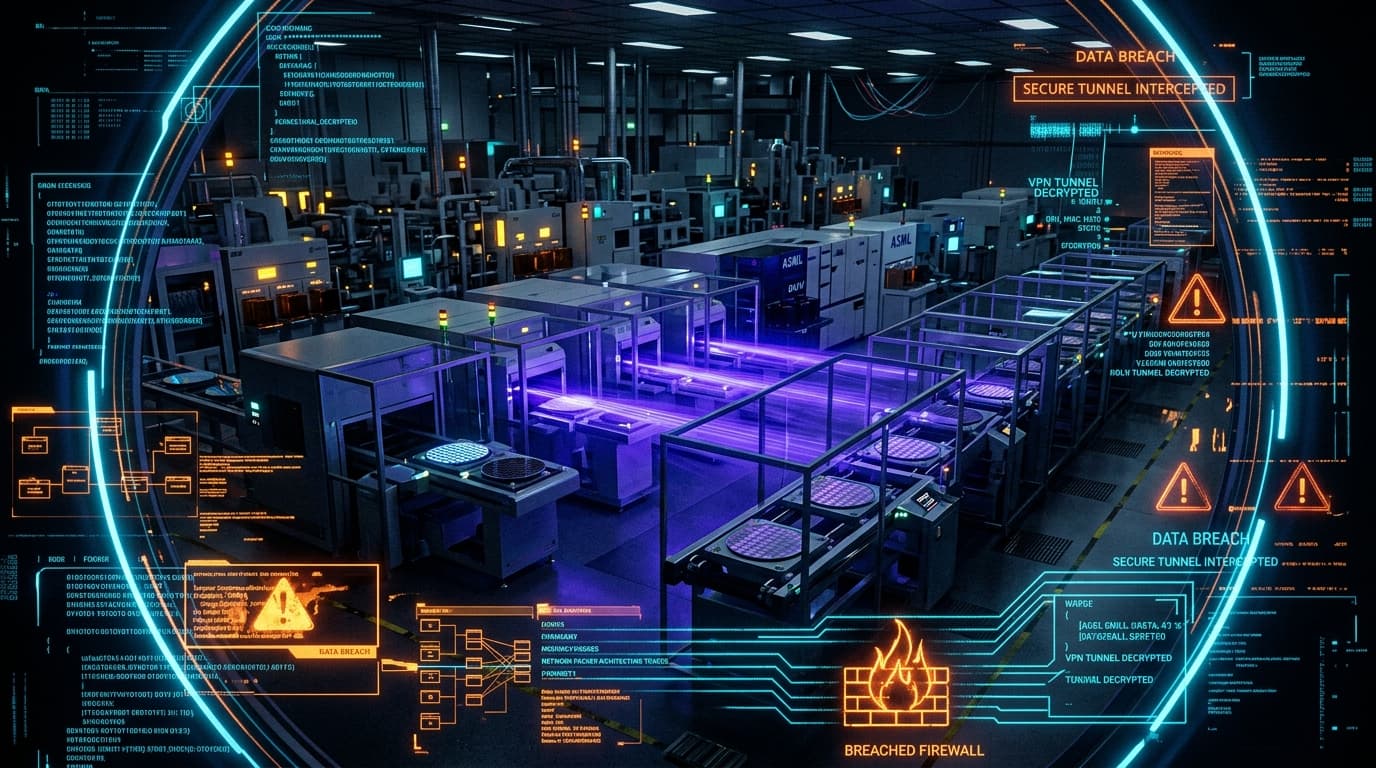
Semiconductor Foundry Discloses Exfiltration of EUV Lithography Mask Designs
A premier semiconductor foundry submits SEC Form 8-K Item 1.05 after nation-state actors compromise CAD vaults and exfiltrate sub-2nm EUV lithography mask IP.
Editor-in-Chief
Priya has covered enterprise security for over a decade, with a focus on vulnerability disclosure, incident response and the gap between vendor advisories and what defenders can actually action.
636 articles
A premier semiconductor foundry submits SEC Form 8-K Item 1.05 after nation-state actors compromise CAD vaults and exfiltrate sub-2nm EUV lithography mask IP.
Deep DiveReserve Bank of India issues binding directions requiring automated HSM cryptographic key rotation and token decryption logging across all payment systems.
RansomwareA premier defense aerospace supplier files SEC Form 8-K Item 1.05 after ransomware actors compromise unclassified R&D enclaves and exfiltrate sensor avionics telemetry.
Deep DiveMeitY and Data Protection Board of India issue binding DPDP Rules 2026 requiring annual algorithmic audits, biometric tokenization, and strict 6-hour breach reports.
Cyber AttackA commercial aviation satellite communications provider files SEC Form 8-K Item 1.05 after nation-state actors breach in-flight telemetry and passenger Wi-Fi systems.
Deep DiveThe Reserve Bank of India mandates continuous automated compliance monitoring and sovereign data localization for all banking cloud workloads.
OT / SCADAA major North American energy utility discloses an SEC Form 8-K cyber incident involving extortion over exfiltrated regional transmission telemetry.
Deep DiveThe European Commission publishes harmonized technical standards for the Cyber Resilience Act, requiring hardware-based secure boot and 24-hour vulnerability notification.
KubernetesA major international container logistics carrier files SEC Form 8-K Item 1.05 after threat actors exfiltrate intermodal shipping manifests and customs manifests.
Deep DiveThe Reserve Bank of India mandates strict 15-minute RTO failover benchmarks and WORM immutable backup architectures for all scheduled commercial banks.
Cyber AttackSEC Form 8-K filing reveals an advanced persistent threat breached the corporate IT network of a major commercial airline, accessing flight dispatch and crew scheduling platforms.
Deep DiveThe PCI Security Standards Council enforces mandatory Requirement 6.4.3 and 11.6.1 compliance, requiring automated inventory and cryptographic hashing of all payment scripts.
RansomwareSEC Form 8-K filing reveals an extortion syndicate encrypted corporate cloud servers hosting diagnostic telemetry and proprietary firmware repositories for hospital medical devices.
Cyber AttackSEC Form 8-K filing reveals an advanced persistent threat exfiltrated sensitive aerospace engineering CAD designs and satellite propulsion telemetry.
Deep DiveThe Reserve Bank of India mandates strict Hardware Security Module (HSM) key management, post-quantum readiness, and 6-hour incident disclosure across all digital payment entities.
OT / SCADASEC 8-K filing reveals an advanced extortion group infiltrated the corporate network of a major energy pipeline operator, accessing historical SCADA telemetry archives.
Deep DiveThe Ministry of Electronics and Information Technology (MeitY) has finalized DPDP Rules 2026, establishing strict audit deadlines and algorithmic assessments for Significant Data Fiduciaries.
Material SEC 8-K disclosure reveals advanced nation-state threat actors pivoted through a third-party equipment vendor SSL VPN to exfiltrate proprietary lithography recipes.
Gov / DefenseCERT-In security advisory mandates multi-cloud redundancy, immutable backup vaults, and 6-hour incident disclosure across Indian financial institutions.
Deep DiveEuropean Supervisory Authorities operationalize DORA TLPT frameworks, requiring banks and critical ICT providers to undergo advanced red-team audits.
Deep DiveIndia activates Phase 2 of the Digital Personal Data Protection Act, introducing DPBI enforcement inquiries and penalties up to ₹250 Crore.
Deep DiveReserve Bank of India mandates strict IT governance, cloud outsourcing oversight, and 6-hour cyber incident disclosures across financial institutions.
Data BreachThe exfiltration of 8.8M Danish CPR records exposes the systemic risk of partner API queries. Security leaders must replace static trust with verifiable credentials.
GoogleGoogle released Chrome 154.0.8037.97 resolving a critical out-of-bounds write flaw in WebGL (CVE-2026-103628) that exposes memory to arbitrary code execution.