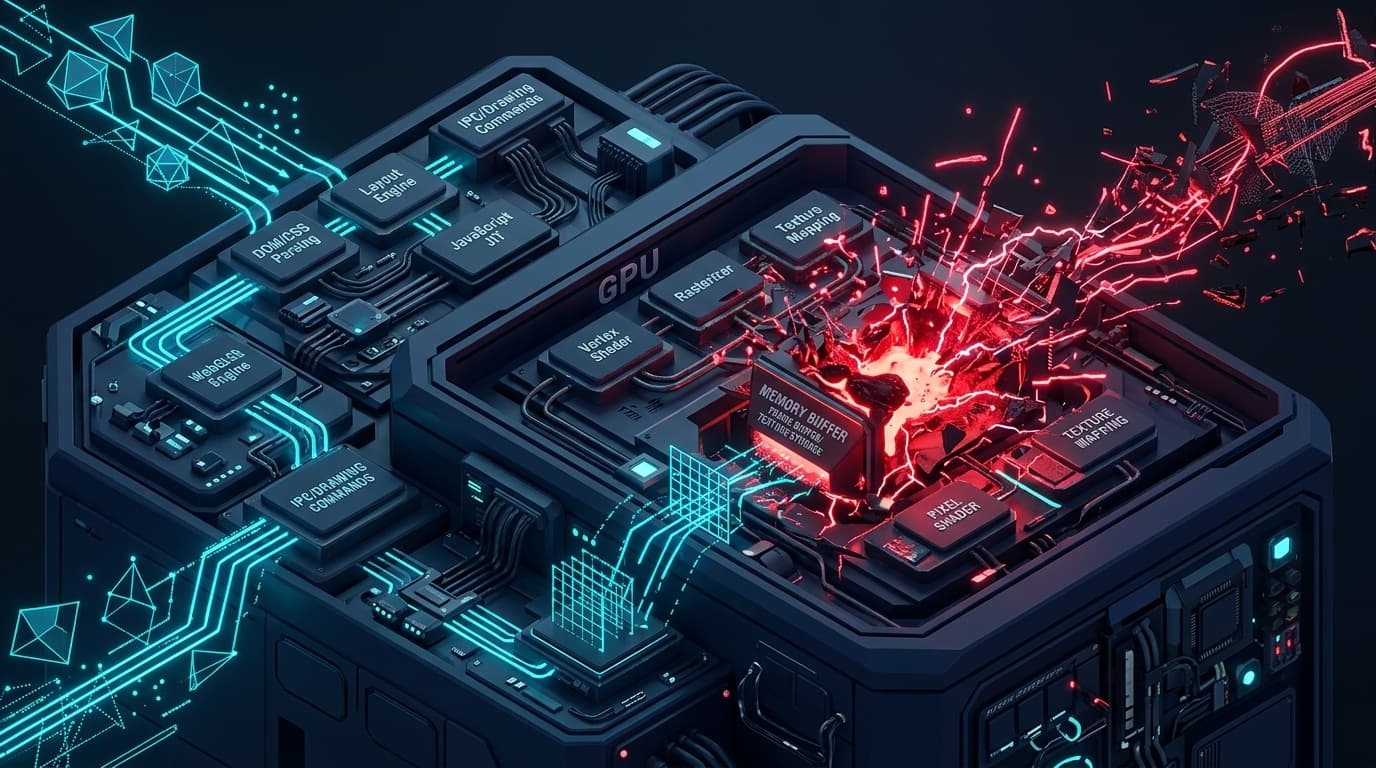
Google has issued an urgent Stable Channel security update for Google Chrome Desktop, resolving 11 security vulnerabilities across core rendering, JavaScript execution, and graphics subsystems. The most severe issue in the batch is CVE-2026-103628, an externally reported Critical-severity out-of-bounds write flaw in WebGL. Exploitation allows specially crafted HTML5 canvas and 3D graphics rendering instructions to corrupt GPU process memory buffers, creating a viable path for remote code execution and escape from the Chromium sandbox.
Anatomy of CVE-2026-103628: WebGL Out-of-Bounds Memory Corruption
WebGL (Web Graphics Library) provides hardware-accelerated 3D graphics inside Chromium by communicating between the untrusted renderer process and the privileged GPU process. To preserve boundary separation, Chromium employs rigorous validation layers within its GPU command buffer parser.
Under CVE-2026-103628, a boundary check breakdown occurs during the compilation and allocation of dynamic vertex attribute arrays. When a web page supplies non-standard buffer stride parameters combined with compressed texture coordinates, the GPU process incorrectly computes memory offsets. Instead of clamping writes to the allocated backing memory segment, the WebGL pipeline writes raw data past the designated boundary (CWE-787: Out-of-bounds Write).
Because this memory corruption occurs directly within the GPU process context, an attacker possessing an initial low-privilege renderer exploit can chain this flaw to corrupt GPU control flow, hijack execution pointers, and break out of the operating system sandbox.
// Conceptual reproduction trigger of vertex stride miscalculation
const canvas = document.createElement("canvas");
const gl = canvas.getContext("webgl2");
const buffer = gl.createBuffer();
gl.bindBuffer(gl.ARRAY_BUFFER, buffer);

// Large stride parameter causing 32-bit integer overflow during offset calculation
const malformedStride = 0x7FFFFFFF;
gl.bufferData(gl.ARRAY_BUFFER, 1024, gl.STATIC_DRAW);
gl.vertexAttribPointer(0, 4, gl.FLOAT, false, malformedStride, 0);
gl.drawArrays(gl.TRIANGLES, 0, 3); // Triggers out-of-bounds write in GPU worker
Vulnerable Software Versions & Patch Status Matrix
Google maintains separate build numbers across desktop operating system platforms. Fleet managers should verify that installed binaries match or exceed the patched milestones:
| Operating System Platform | Vulnerable Versions | Fixed / Remediated Release | Remediation Action Required |
|---|---|---|---|
| Linux (Debian, Ubuntu, Fedora, RHEL) | Versions < 154.0.8037.97 | 154.0.8037.97 | Package manager upgrade and browser restart |
| Microsoft Windows (x64 / ARM64) | Versions < 154.0.8037.97 | 154.0.8037.97 or 154.0.8037.98 | Enterprise MSI rollout or Winget auto-update |
| Apple macOS (Intel / Apple Silicon) | Versions < 154.0.8037.97 | 154.0.8037.97 or 154.0.8037.98 | MDM Jamf profile push or Homebrew upgrade |
Step-by-Step Remediation Playbook & Patch Commands
Enterprise IT and security operations teams should enforce immediate automated rollout across managed browser fleets:
- Linux Workstations (Debian/Ubuntu/APT):
# Update local repositories and upgrade Google Chrome Stable sudo apt-get update && sudo apt-get --only-upgrade install -y google-chrome-stable # Verify current installed version google-chrome --version # Output must report: Google Chrome 154.0.8037.97 or higher - Linux Workstations (RHEL/CentOS/Fedora/DNF):
# Upgrade via DNF package manager sudo dnf upgrade -y google-chrome-stable # Verify package manifest rpm -q google-chrome-stable - Windows Fleet Update via Winget or PowerShell:
# Query and upgrade Google Chrome silently across enterprise workstations winget upgrade --id Google.Chrome --silent --accept-source-agreements --accept-package-agreements # Verify active executable file version (Get-Item "C:Program FilesGoogleChromeApplicationchrome.exe").VersionInfo.FileVersion - macOS Workstation Rollout via Homebrew or Terminal:
# Upgrade Chrome via Homebrew Cask brew upgrade --cask google-chrome # Verify binary build string /Applications/Google Chrome.app/Contents/MacOS/Google Chrome --version - Temporary WebGL Hardening Policy: For high-assurance isolation zones or PAM jump boxes where 3D graphics are unnecessary, WebGL can be disabled globally via policy:
// Chrome Enterprise Policy: Disable WebGL across managed devices
{
  "Disable3DAPIs": true,
  "RelaunchNotification": 2,
  "RelaunchNotificationPeriod": 86400000
}
Threat Hunting & GPU Crash Telemetry Queries
Security operations centers (SOC) should monitor endpoint detection and response (EDR) telemetry for unusual GPU process terminations or unexpected child process spawning from chrome.exe:
# Audit system logs for repeated Chromium GPU process segment violations (Linux)
journalctl -u systemd-coredump --since "24 hours ago" | grep -i "chrome.*gpu-process"

# Audit Windows Event Log for Event ID 1000 (Application Crash) targeting chrome.exe
Get-WinEvent -FilterHashtable @{LogName='Application'; ProviderName='Application Error'; Id=1000} |
  Where-Object { $_.Message -like "*chrome.exe*" -and $_.Message -like "*gpu*" }