Regulatory Incident Filing Overview
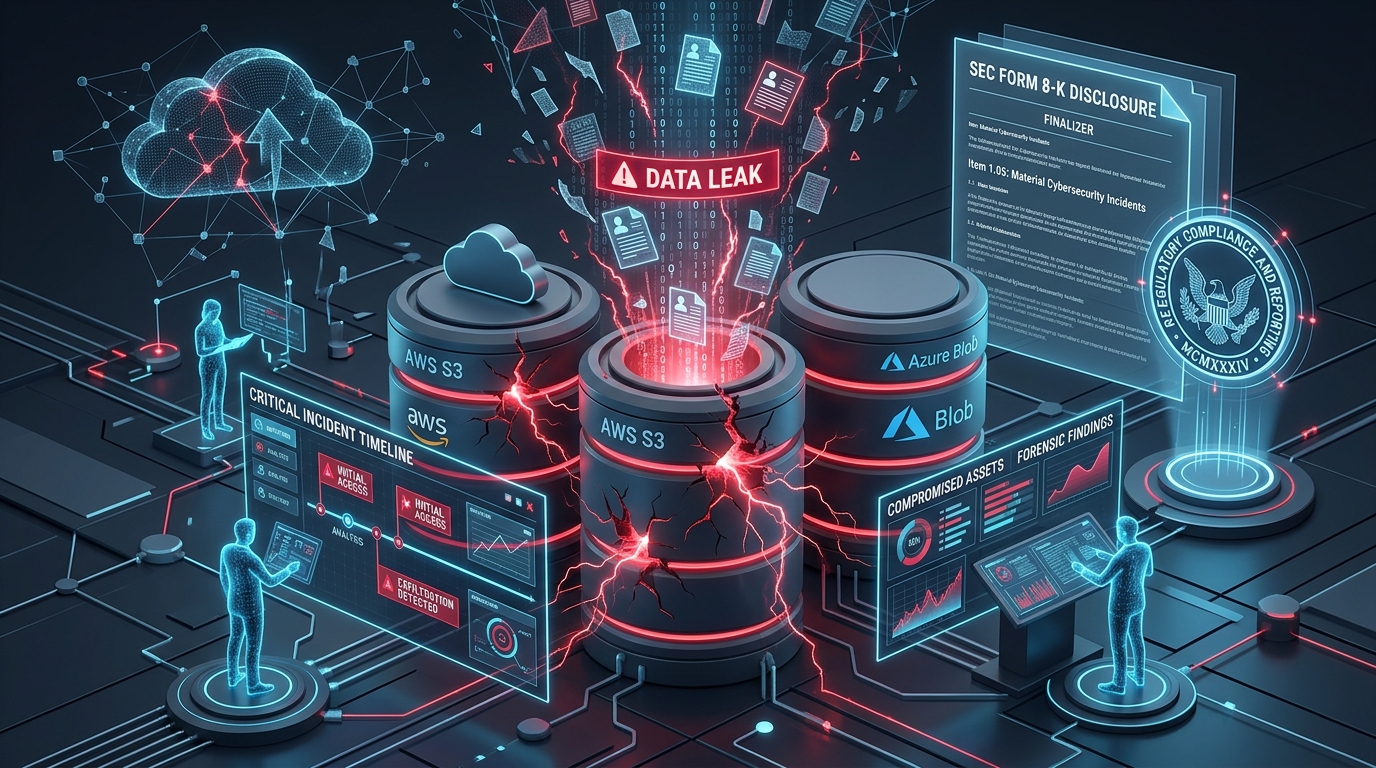
In a mandatory Form 8-K Item 1.05 disclosure filed with the U.S. Securities and Exchange Commission (SEC), an international semiconductor foundry operator has formally confirmed a material cybersecurity incident involving unauthorized access to its internal engineering and manufacturing networks. According to the regulatory disclosure, sophisticated nation-state threat actors infiltrated the enterprise's digital boundary and exfiltrated proprietary chip design assets and manufacturing process documentation.
The disclosure underscores the escalating targeting of the global semiconductor supply chain, where advanced manufacturing intellectual property—specifically Process Design Kits (PDKs), extreme ultraviolet (EUV) photolithography recipe files, and chemical vapor deposition telemetry—represents critical strategic and economic assets.
Forensic Timeline & Initial Access Vector
Forensic telemetry documented by the company's internal Incident Response team and federal cyber defense agencies revealed that the breach originated not through a direct perimeter flaw, but via a compromised external third-party maintenance contractor:
- Initial Infiltration (T-minus 14 Days): Threat actors acquired valid enterprise credentials belonging to an overseas field service engineer employed by an industrial lithography equipment supplier. The credentials lacked mandatory FIDO2 hardware token enforcement and relied on legacy SMS-based MFA.
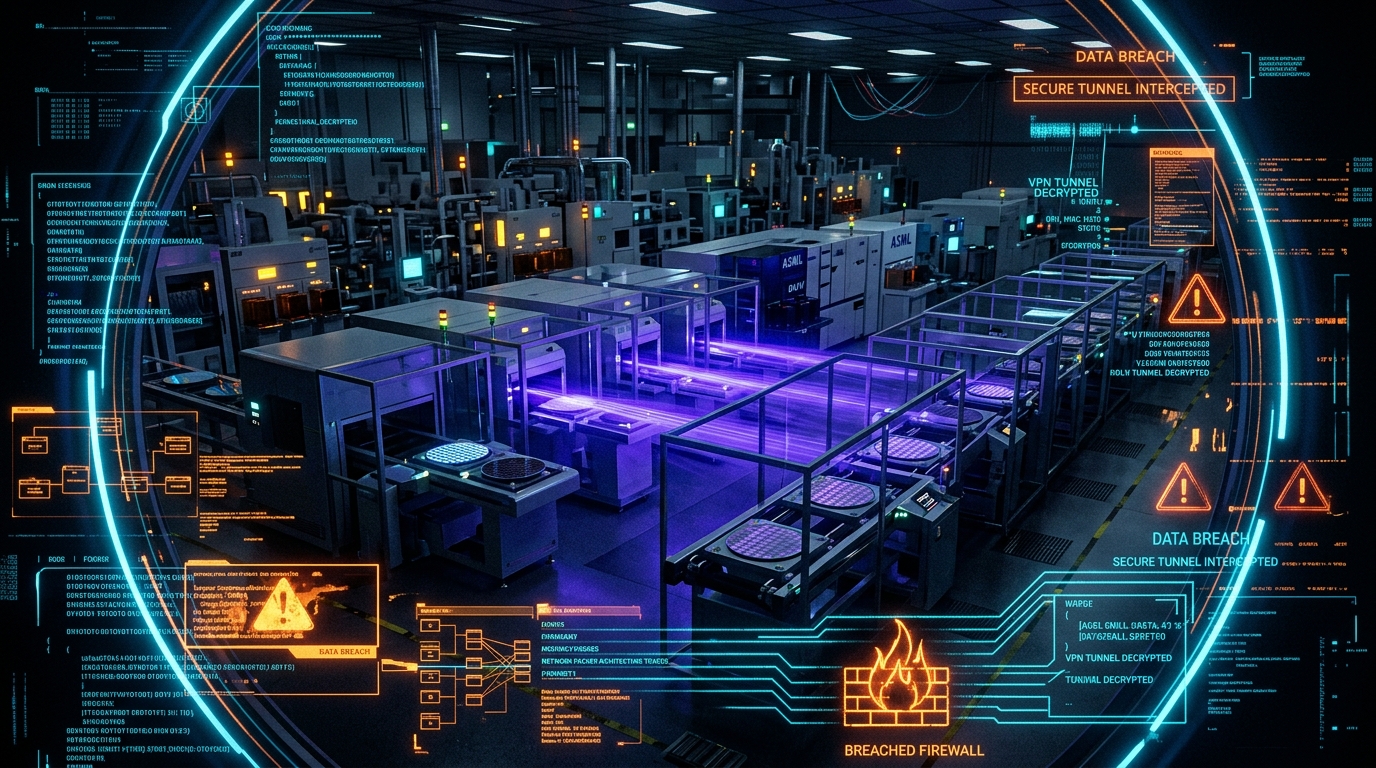
- Perimeter Ingress: The adversary authenticated through a legacy SSL VPN gateway maintained specifically for remote vendor equipment diagnostics.
- Privilege Escalation & Lateral Movement: Leveraging credential dumping tools (Mimikatz and internal Kerberoasting attacks), the actors extracted domain administrator credentials from an unpatched engineering jump server.
- Data Staging & Exfiltration: Over 1.8 terabytes of compressed archives—comprising proprietary 2-nanometer gate-all-around (GAA) layout blueprints and cleanroom operational telemetry—were staged on internal SMB shares and exfiltrated over encrypted HTTPS sessions masquerading as routine telemetry to reputable public cloud storage endpoints.
Attack Progression Forensic Matrix:
[Compromised Vendor Credential]
      │ (SSL VPN Authentication)
      ▼
[Engineering Jump Host (DMZ)]
      │ (Pass-the-Hash / Kerberoasting)
      ▼
[Domain Controller Compromise]
      │ (SMB Lateral Movement)
      ▼
[Cleanroom File Server] ──(Encrypted Exfiltration)──> [External Cloud Storage]
Material Business & Regulatory Implications
Under SEC Rule 33-11216, public companies are required to disclose material cybersecurity incidents within four business days of determining materiality. In the filing, the enterprise stated that while primary manufacturing fabrication lines remained operationally intact without physical sabotage, the theft of core semiconductor IP constitutes a material event affecting competitive positioning and customer confidence.
The company also notified the Department of Commerce and CISA, as the stolen files included technology subject to strict Export Administration Regulations (EAR) and International Traffic in Arms Regulations (ITAR).
Third-Party Vendor Risk Remediation Playbook
To eliminate the attack vectors exploited in this campaign, enterprise security architectures must immediately implement stringent third-party supply chain controls:
- Decommission Legacy SSL VPNs: Replace all persistent vendor VPN access with Zero Trust Network Access (ZTNA) solutions enforcing just-in-time (JIT) access and full session recording.
- Mandate Phishing-Resistant MFA: Require all third-party contractors and service engineers to authenticate using hardware security keys (FIDO2 / WebAuthn). Eliminate SMS and push-based notifications entirely.
- Data Loss Prevention (DLP) on High-Value IP: Apply cryptographic digital rights management (DRM) and watermark tracking to all proprietary CAD files, PDKs, and manufacturing recipe scripts.