Topic
Third-Party Risk: news, advisories and analysis
10 articles
CyberSecureToday covers Third-Party Risk across 10 articles published between 20 Sep 2026 and 23 Oct 2026. The coverage includes 4 incident or breach reports and 6 analysis or guidance pieces.
Stories on Third-Party Risk most often intersect with Data Breach, Banking Security and Compliance, with Banking, Financial Services & Fintech the most affected sector. The most recent story, “RBI IT Governance & Cybersecurity Master Direction for NBFCs: Implementation Playbook”, was published 23 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
GuidesBanking & FintechPriya Raman
InsightsBanking & FintechEU DORA Standards Set Major ICT Incident Classification and Third-Party Oversight Rules
CST Editorial Desk
Cyber AttackCloud & SaaSSEC Form 8-K Forensics: Advanced Semiconductor Foundry Discloses Intellectual Property Theft via Compromised Supplier VPN
Priya Raman
InsightsGov & DefenceDenmark's 8.8 Million CPR Breach Exposes Trusted Partner API Blind Spot
Priya Raman
Cyber AttackGov & DefenceCompromised Partner Integration Exposes 8.8 Million Citizen Records in Denmark National Registry Breach
Tom Verhoeven
InsightsBanking & FintechEU DORA Mandates 4-Hour ICT Incident Disclosure and Threat-Led Penetration Testing
Mei-Lin Chen
InsightsBanking & FintechRBI Enforces 6-Hour Breach Notification and Cloud Outsourcing Audits Across Financial Sector
Tom Verhoeven
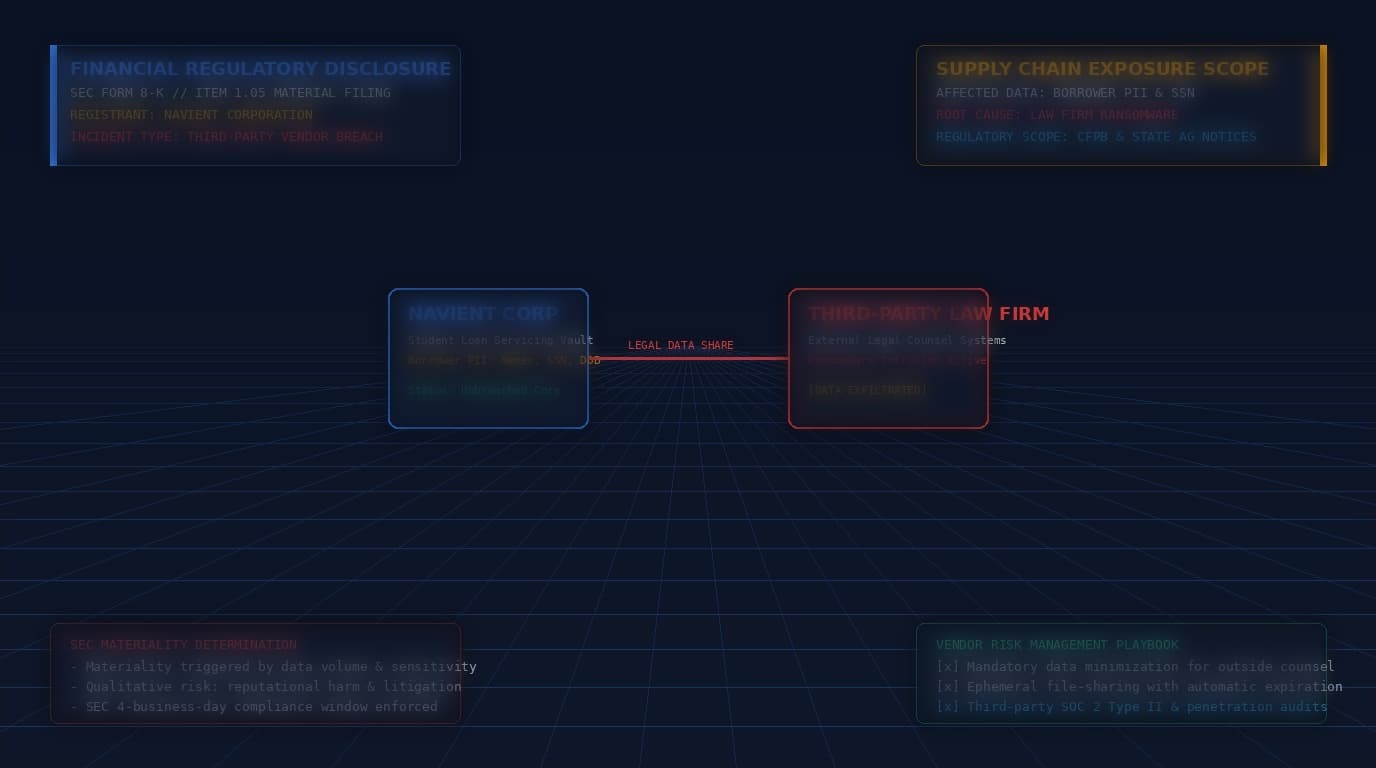
Cyber AttackBanking & FintechNavient Corporation Files SEC Form 8-K After Third-Party Law Firm Ransomware Exfiltrates Borrower Records
CST Editorial Desk
Cyber AttackHealthcare & PharmaAmgen Discloses Unauthorized Cloud Data Exfiltration and Patient PHI Theft in SEC Form 8-K Filing
CST Editorial Desk
InsightsBanking & FintechEU DORA Enforcement Shifts to Live Production Penetration Testing and Third-Party Oversight
Priya Raman