Regulatory Disclosure Summary
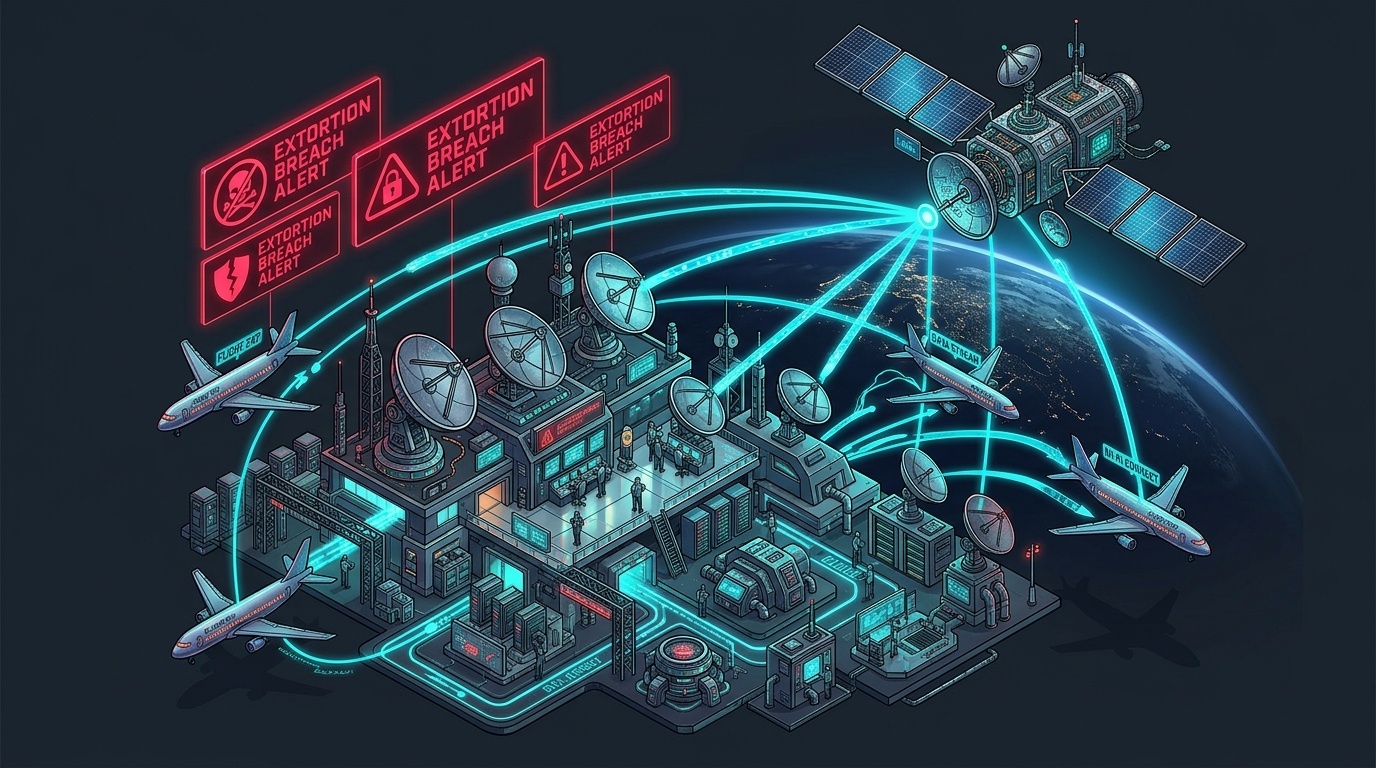
A leading international satellite communications and in-flight connectivity (IFC) provider has submitted a formal Form 8-K Item 1.05 disclosure to the U.S. Securities and Exchange Commission (SEC), notifying markets of a material cybersecurity incident that compromised ground teleport networks, satellite earth station routing platforms, and customer airline portal systems.
Forensic Timeline & Attack Progression
The forensic investigation revealed that sophisticated threat actors leveraged stolen credentials belonging to an engineering contractor, bypassing legacy single-factor VPN gateways. The adversaries progressed through the following attack chain:
| Attack Phase | Observed Activity | Target Assets |
|---|---|---|
| Initial Infiltration | VPN authentication bypass using compromised contractor account | Ground Earth Station Operations LAN |
| Lateral Movement | Exploitation of internal virtualization management consoles | Satellite Hub Modulation Gateways |
| Data Access | Exfiltration of flight passenger connectivity logs and satellite transponder routing | In-Flight Wi-Fi Billing & Telemetry DB |
| Incident Containment | Severing of ground station management links and credential invalidation | Global Satellite Teleport Network |
The exfiltrated records included commercial aircraft tail number positional tracking logs, transponder beam allocation schedules, and passenger Wi-Fi authentication session tokens across commercial airline partners. Crucially, the provider emphasized that aircraft flight control systems, Fly-By-Wire avionics, and cockpit voice communications are governed by independent, hardware-isolated SATCOM channels and were never exposed to the compromised passenger network.
Regulatory & Aviation Safety Coordination
The satellite provider coordinated with the Federal Aviation Administration (FAA), the European Union Aviation Safety Agency (EASA), and the Cybersecurity and Infrastructure Security Agency (CISA) to verify that flight safety remained uncompromised. The carrier is actively providing technical support to customer airlines to revoke and refresh in-flight connectivity tokens.
Enterprise Remediation Protocols
To eliminate attacker footholds across the satellite infrastructure, the provider has deployed the following measures:
- Mandatory enterprise-wide rollout of FIDO2 hardware security keys for all ground station access.
- Complete isolation of satellite teleport management networks behind unidirectional security diodes.
- Zero Trust microsegmentation separating in-flight passenger internet services from ground telemetry routing backbones.